WEAPONIZING-CVE-2024-4367

CVE-2024-4367 is a critical vulnerability (CVSS 9.8) in PDF.js, allowing arbitrary JavaScript code execution due to insufficient type checks on the…

CVE-2024-4367 is a critical vulnerability (CVSS 9.8) in PDF.js, allowing arbitrary JavaScript code execution due to insufficient type checks on the…

CVE-2024-3094 XZ Utils backdoor research - attack surface visualiser, system vulnerability checker, and general Linux CVE assessment tool

Proof-of-concept for a reflected XSS vulnerability (CVE-2025-69606) in GSVoIP Web Panel v2.0.90, demonstrating unauthenticated arbitrary JavaScript…

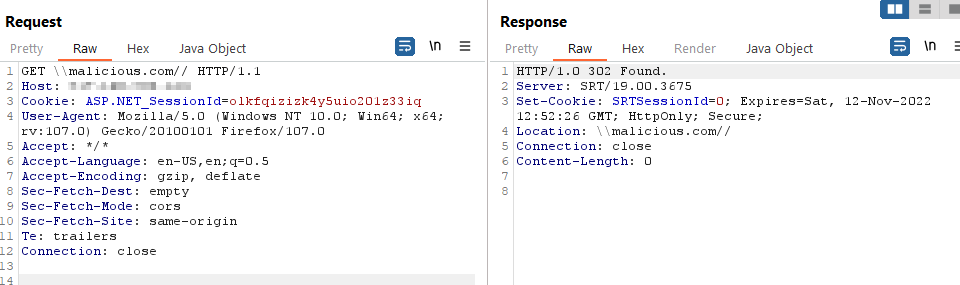
Public disclosure of TitanFTP 19.X Open Redirection vulnerability

WordPress Munk Sites plugin <= 1.0.7 - CSRF to Arbitrary Plugin Installation vulnerability

Educational Proof-of-Concept for the CVE-2022-30190 (Follina) vulnerability.

Proof-of-concept demonstrating a Clickjacking vulnerability on the G1 website, with a malicious iframe overlay and social engineering popup for…

A security vulnerability has been identified in Krayin CRM <=2.1.0 that allows a low-privileged user to escalate privileges by tricking an admin into…

(DOM-based XSS) HTML Injection vulnerability in TOWeb v.12.05 and before allows an attacker to inject HTML/JS code via the _message.html component.

Proof of concept for a blind/persistent XSS vulnerability in Blinger.io helpdesk, demonstrating remote code execution in admin panels via crafted…

Python tool for CVE-2010-1240 research - generates malicious PDFs exploiting Adobe Reader Launch Actions

PoC CVE-2025-49144

Windows File Explorer Zero Click NTLMv2-SSP Hash Disclosure

【Teedy 1.11】Account Takeover via XSS

POC Files for CVE-2019-17497