
skills
 specterops/skills
Reusable offensive security skills and plugins for AI agents, covering reconnaissance, exploitation, C2, payload development, and reporting across…
command-and-controleducationexploitation+9
715
specterops/skillsReusable offensive security skills and plugins for AI agents, covering reconnaissance, exploitation, C2, payload development, and reporting across…
 e-m-e-k-a/moniker-link-lab-setup
Penetration testing lab demonstrating CVE-2024-21413 moniker link exploitation for NTLM credential theft, including attack execution, hash cracking,…
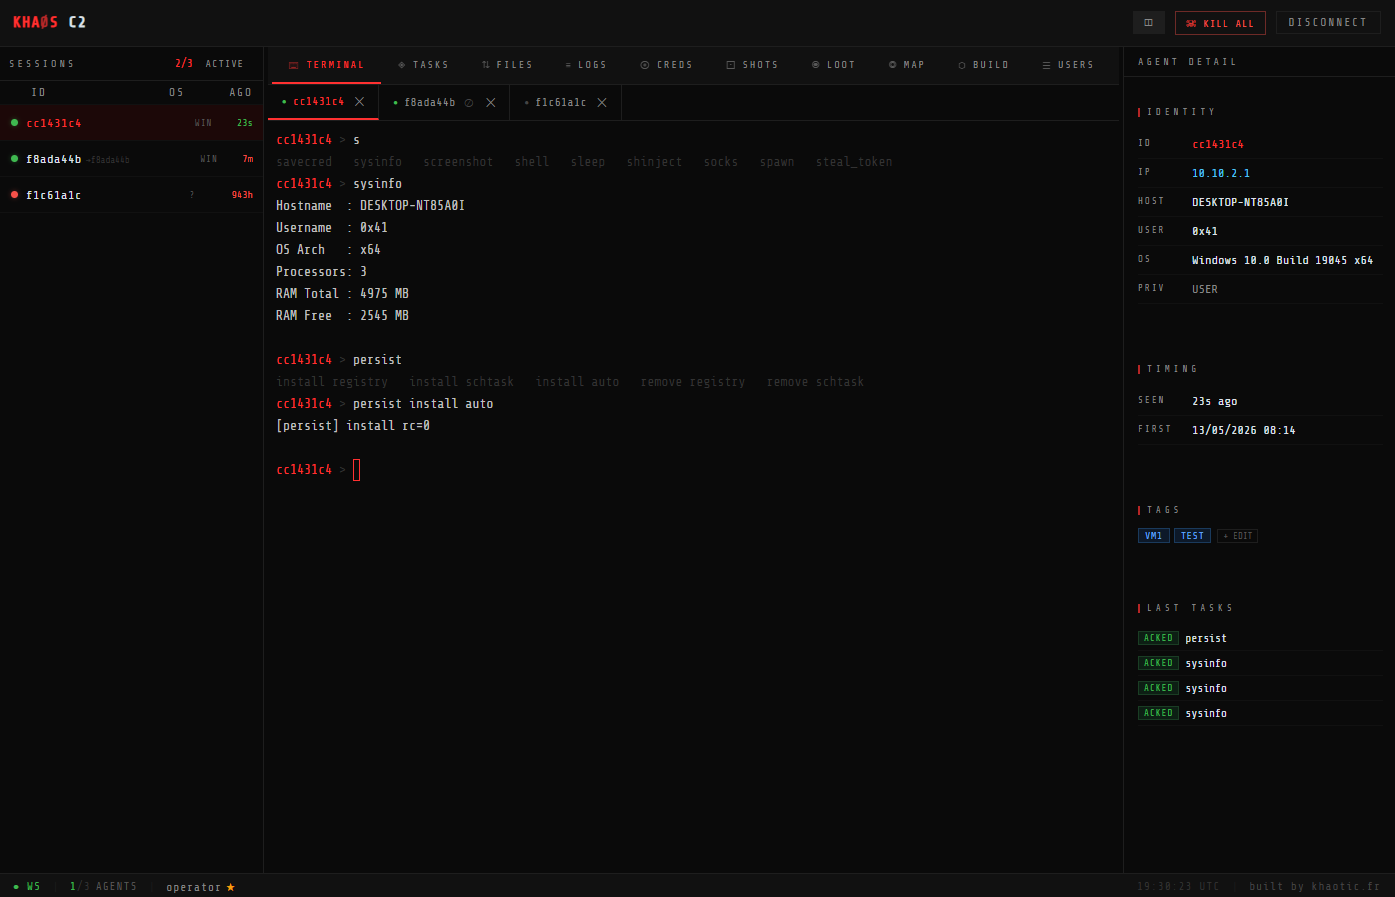 28zaaky/khaos-c2
KHAOS is a modern C2 framework that routes agent traffic through cloud services already trusted by enterprise networks.
 cappricio-securities/cappriciosec-university
A Hacker's E-learning App for Tamil People
 drk1wi/modlishka
Modlishka. Reverse Proxy.
 nephila016/cve-2025-55319-poc
PoC for CVE-2025-55319
 nnatsopoulos/xz-backdoor-research
CVE-2024-3094 XZ Utils backdoor research - attack surface visualiser, system vulnerability checker, and general Linux CVE assessment tool
 pericena/ciclopeclic
Security awareness training tool for authorized phishing simulations and internal IT audits
 trustedsec/social-engineer-toolkit
The Social-Engineer Toolkit (SET) repository from TrustedSec - All new versions of SET will be deployed here.
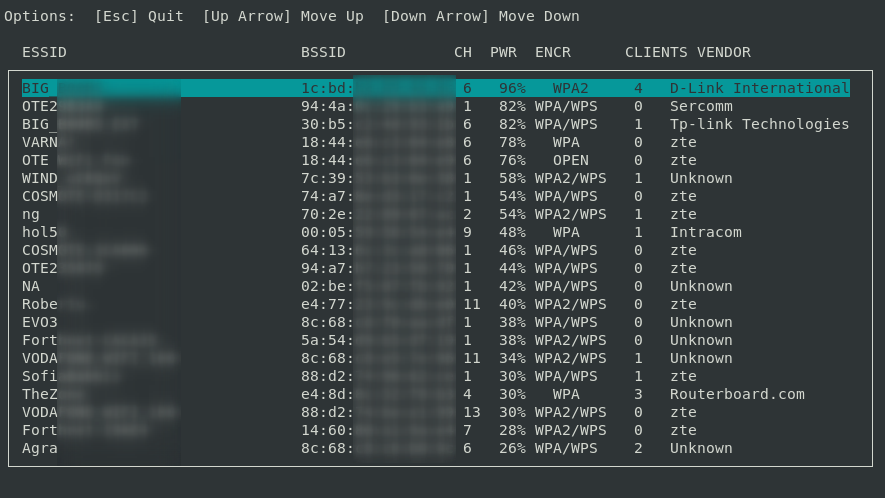 wifiphisher/wifiphisher
Rogue Access Point framework for red team engagements and Wi-Fi security testing. Performs Evil Twin, KARMA, and Known Beacons attacks to achieve…
 corvralabs/evilneko
Automated container orchestration tool for Browser-in-the-Browser (BITB) phishing attacks, enabling red teams to scale multi-target infrastructure…
 jumpseclabs/tokenflare
Serverless AITM Simulation Framework for Entra ID and M365
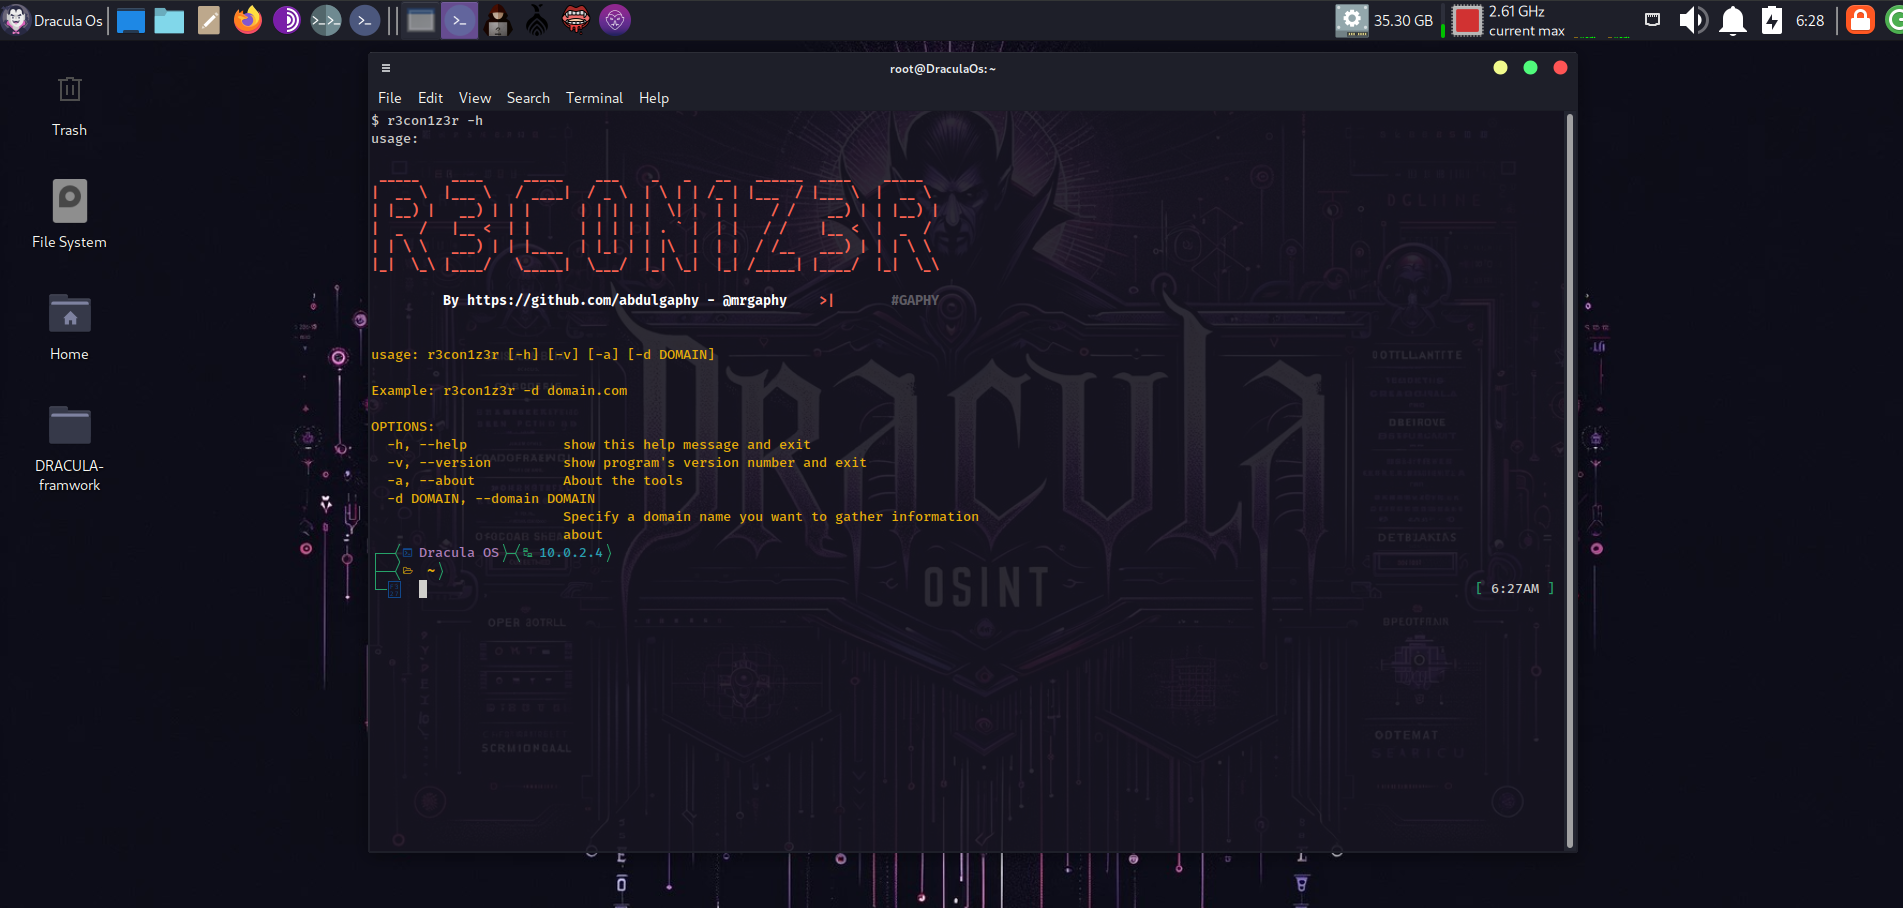 emrekybs/draculaos
Dracula OS is a Linux operating system meticulously designed for OSINT (Open Source Intelligence) and Cyber Intelligence missions.
 aleksamcode/wifi-password-stealer
Simple Windows and Linux keystroke injection tool that exfiltrates stored WiFi data (SSID and password).
 r00t-3xp10it/fakeimageexploiter
Use a Fake image.jpg to exploit targets (hide known file extensions)
 exfil0/weaponizing-cve-2024-4367
CVE-2024-4367 is a critical vulnerability (CVSS 9.8) in PDF.js, allowing arbitrary JavaScript code execution due to insufficient type checks on the…
 d4vinci/pastejacker
Hacking systems with the automation of PasteJacking attacks.
 skyler-ferrante/cve-2024-28085
WallEscape vulnerability in util-linux