
SmuggleMyPayload
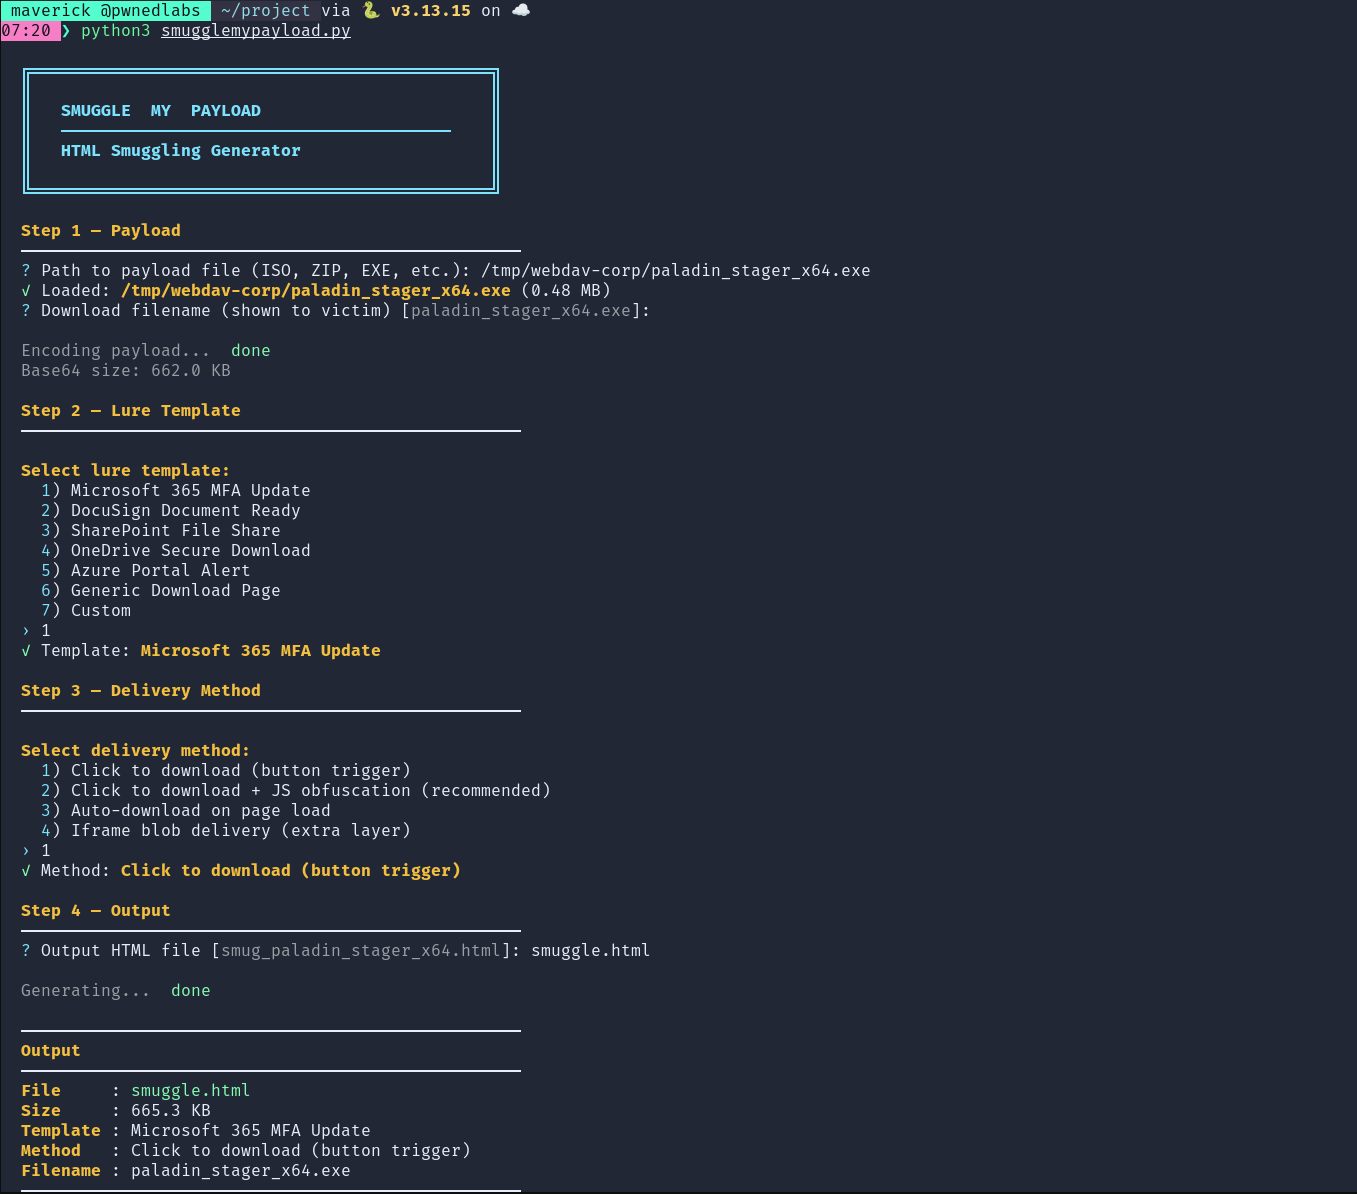
Generates HTML smuggling pages that embed and reconstruct files client-side via JavaScript, with payload encoding, chunking, obfuscation, and…

Generates HTML smuggling pages that embed and reconstruct files client-side via JavaScript, with payload encoding, chunking, obfuscation, and…

This is a Automated Generate Payload for CVE-2019-11932 (WhatsApp Remote Code Execution)

PoC exploit chain for WordPress pre-auth XSS to RCE via DOM clobbering, REST JSONP/SOME, and plugin upload, with Docker lab verification and…

Hide your payload into .jpg file

Lnk crafting and research tools

Remote DLL hijack exploit for Real Player (CVE-2022-32291) using malicious DLLs from WebDAV/SMB shares to achieve code execution.

PoC exploit for CVE-2023-52076 - zip-slip path traversal in Atril/Xreader (MATE/Cinnamon) enabling arbitrary file write and RCE via crafted EPUB.…

Snoopy: A distributed tracking and data interception framework

A malicious OAuth application that can be leveraged for both internal and external phishing attacks targeting Microsoft Azure and Office365 users.

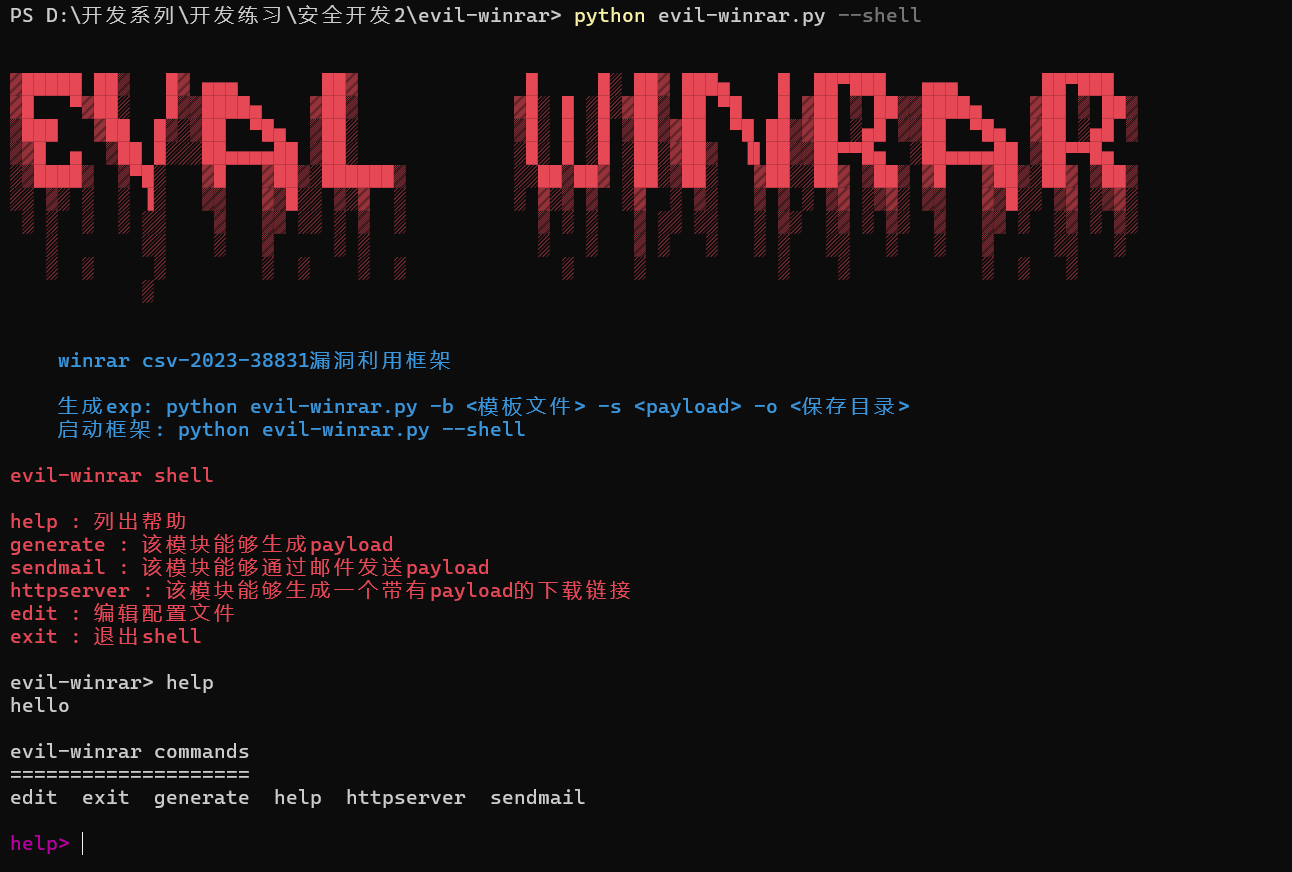
evil-winrar,CVE-2023-38831漏洞利用和社会工程学攻击框架 (evil-winrar, CVE-2023-38831 Vulnerability Exploitation and Social Engineering Attack Framework)

This is a Automated Generate Payload for CVE-2019-11932 (WhatsApp Remote Code Execution)

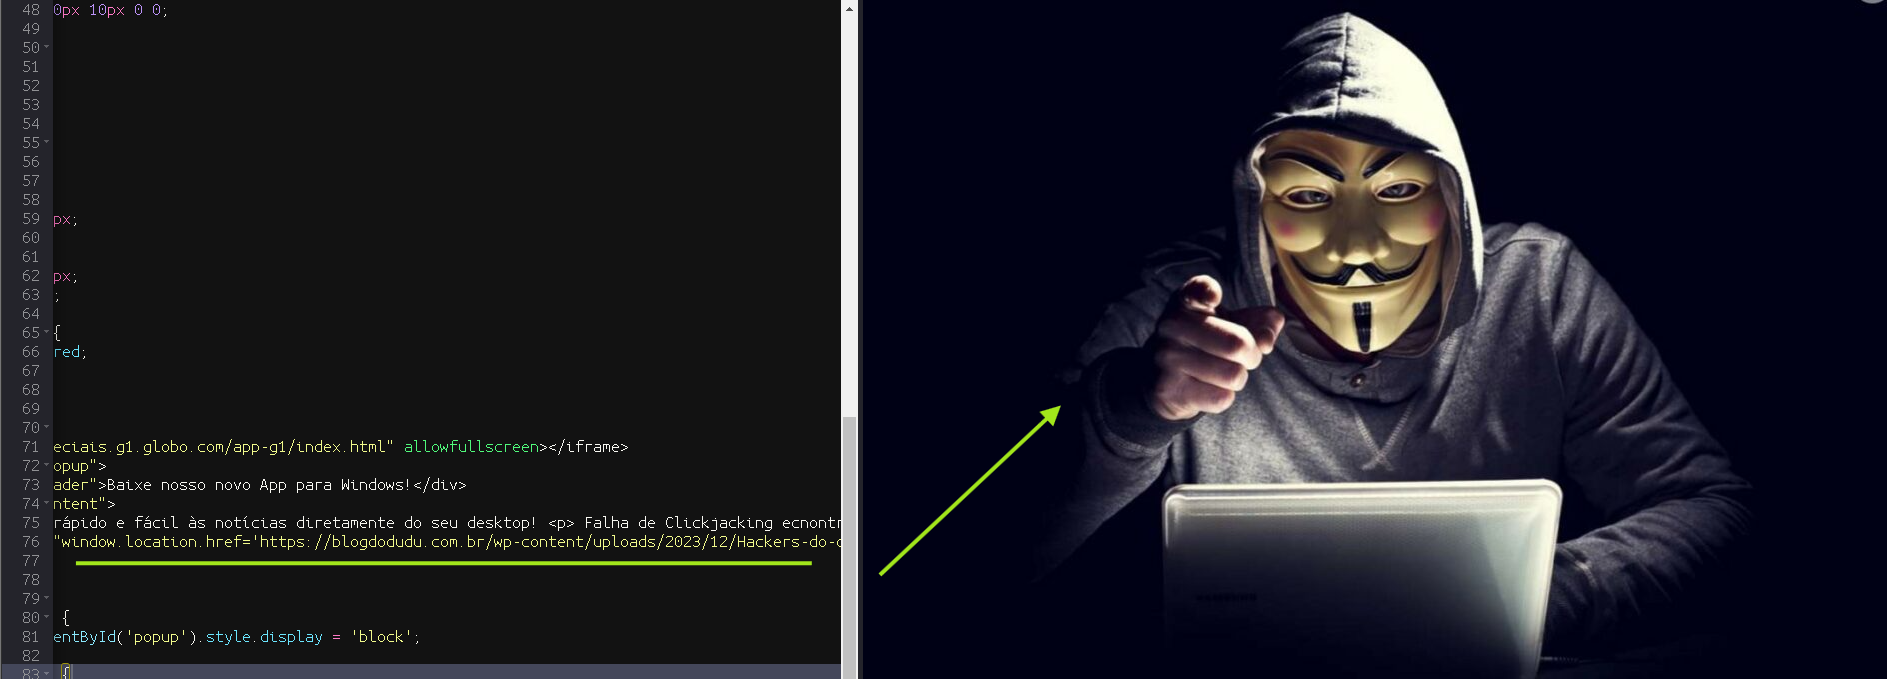
Proof-of-concept demonstrating a Clickjacking vulnerability on the G1 website, with a malicious iframe overlay and social engineering popup for…

A security vulnerability has been identified in Krayin CRM <=2.1.0 that allows a low-privileged user to escalate privileges by tricking an admin into…

CVE-2025-33053 Proof Of Concept (PoC)

Proof-of-concept exploit for CVE-2025-23040 demonstrating credential exfiltration from GitHub Desktop (< 3.4.12) via malicious repository clone URLs,…

an attacker to create and export an address book containing a malicious payload in a field. For example, in the “Other” field of the Instant…

This project contains a Python script that exploits **CVE-2023-38831**, a vulnerability in **WinRAR** versions prior to 6.23. The exploit generates a…