
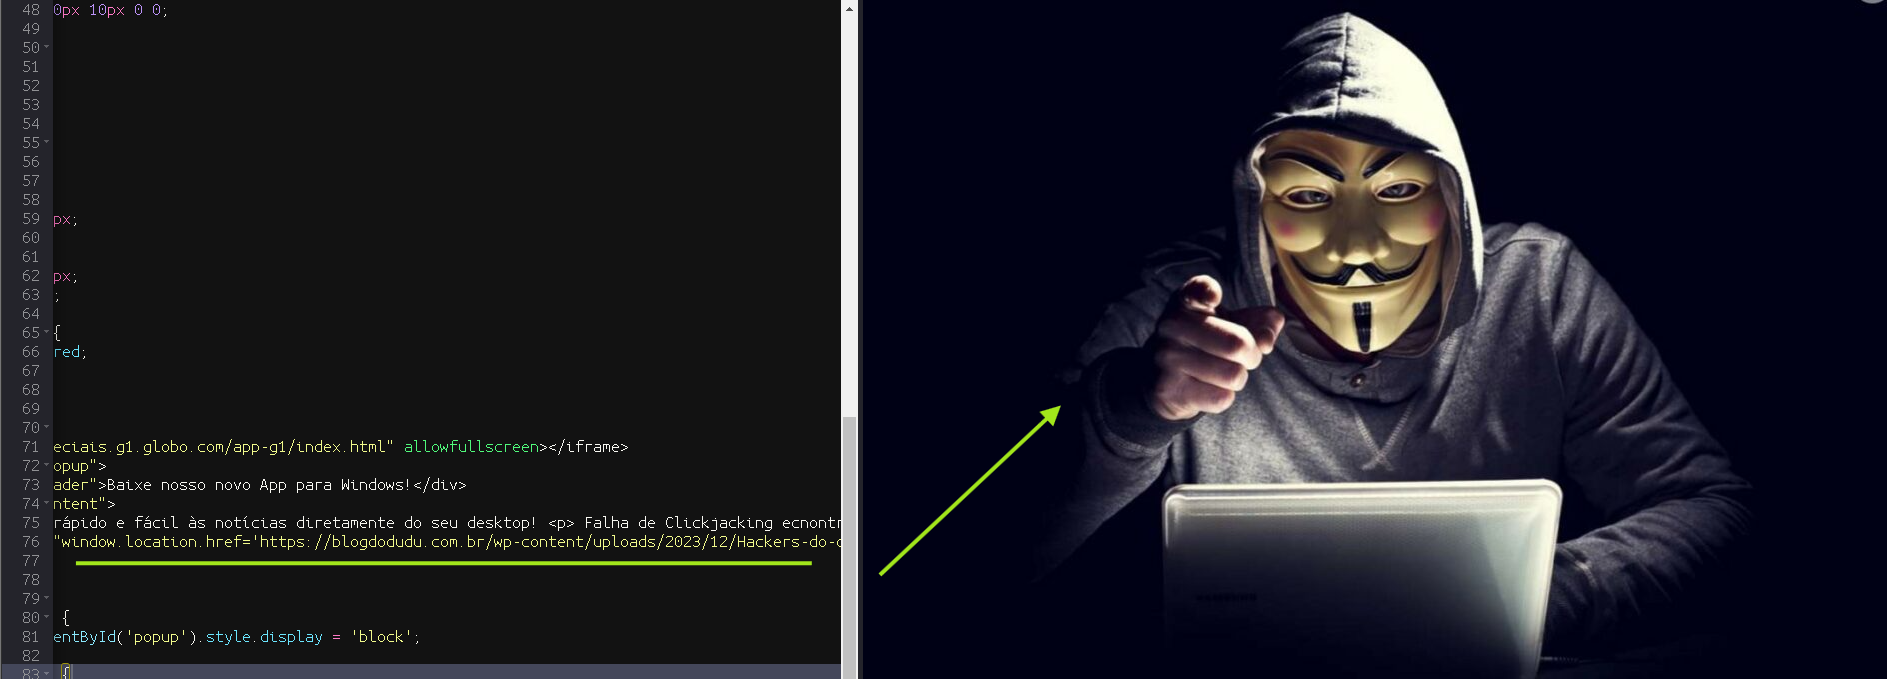
CVE-2023-38873-G1
 k9-modz/cve-2023-38873-g1
Proof-of-concept demonstrating a Clickjacking vulnerability on the G1 website, with a malicious iframe overlay and social engineering popup for…
educationexploitationpapers-research+3
k9-modz/cve-2023-38873-g1Proof-of-concept demonstrating a Clickjacking vulnerability on the G1 website, with a malicious iframe overlay and social engineering popup for…
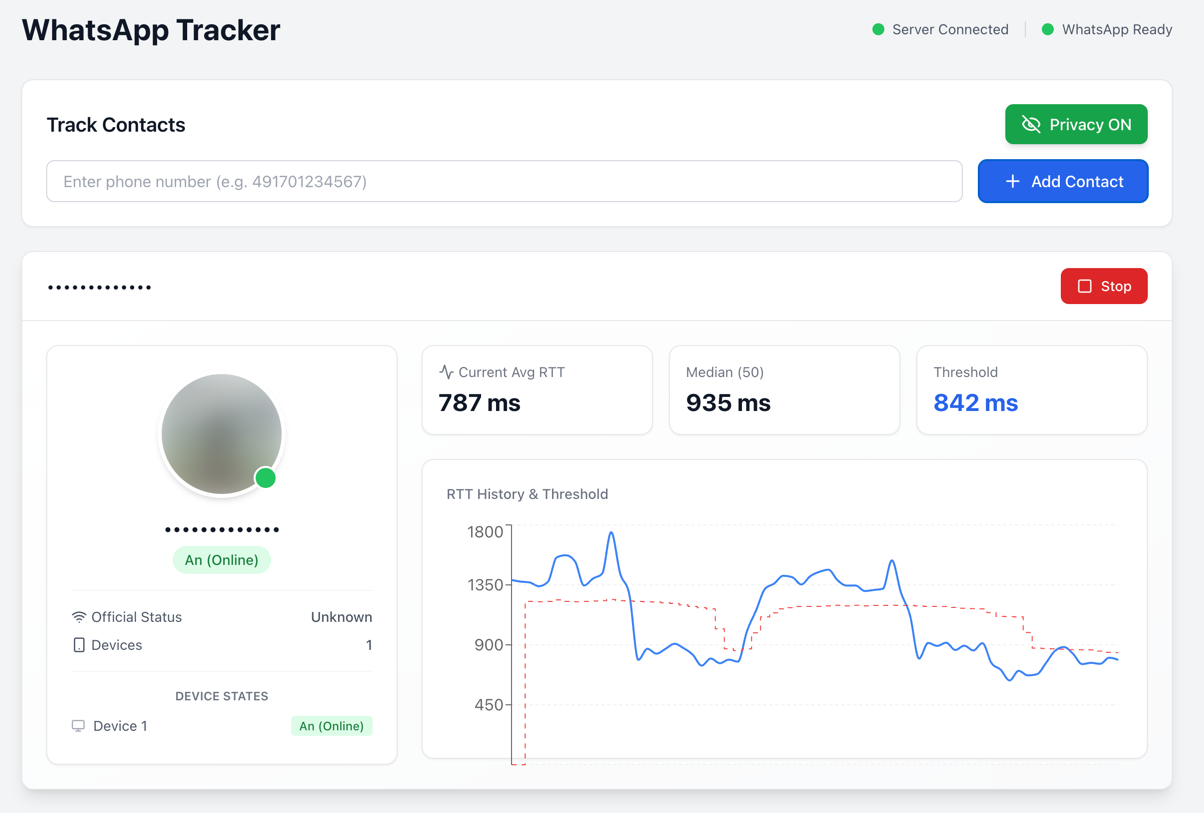 gommzystudio/device-activity-tracker
A phone number can reveal whether a device is active, in standby or offline (and more). This PoC demonstrates how delivery receipts + RTT timing leak…
 skyler-ferrante/cve-2024-28085
WallEscape vulnerability in util-linux
 security-avs/cve-2019-13633
Proof of concept for a blind/persistent XSS vulnerability in Blinger.io helpdesk, demonstrating remote code execution in admin panels via crafted…
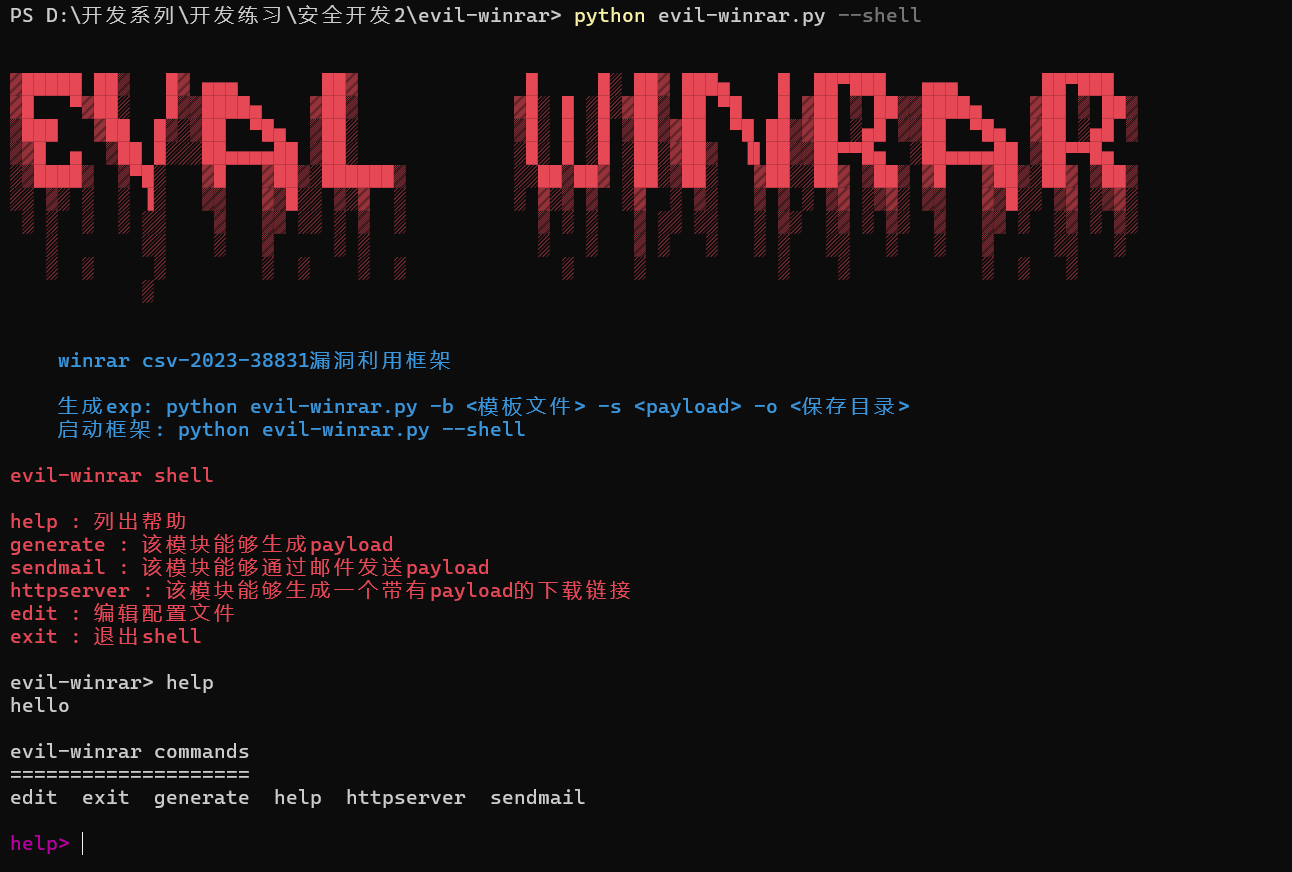 youmulijiang/evil-winrar
evil-winrar,CVE-2023-38831漏洞利用和社会工程学攻击框架 (evil-winrar, CVE-2023-38831 Vulnerability Exploitation and Social Engineering Attack Framework)
 openxp-research/cve-2022-47132
Academy LMS <= 5.10 CSRF
 exfil0/weaponizing-cve-2024-4367
CVE-2024-4367 is a critical vulnerability (CVSS 9.8) in PDF.js, allowing arbitrary JavaScript code execution due to insufficient type checks on the…
 elenichristopoulou/poc-cve-2026-20841
Proof-of-concept exploit for CVE-2026-20841, a Windows Notepad remote code execution vulnerability, using a crafted .md file and social engineering…
 groppoxx/cve-2023-52076-poc
PoC exploit for CVE-2023-52076 - zip-slip path traversal in Atril/Xreader (MATE/Cinnamon) enabling arbitrary file write and RCE via crafted EPUB.…
 12345qwert123456/cve-2010-1240
Python tool for CVE-2010-1240 research - generates malicious PDFs exploiting Adobe Reader Launch Actions
 d0rb/cve-2024-21378
This repository contains an exploit for targeting Microsoft Outlook through Exchange Online, leveraging a vulnerability to execute arbitrary code via…
 abdurahmon3236/cve-2024-6529
Proof-of-concept scripts demonstrating reflected XSS in the Ultimate Classified Listings WordPress plugin and admin cookie theft via crafted payloads…
 mbadanoiu/cve-2021-46366
CVE-2021-46366: Credential Bruteforce Attack via CSRF + Open Redirect in Magnolia CMS
 nnatsopoulos/xz-backdoor-research
CVE-2024-3094 XZ Utils backdoor research - attack surface visualiser, system vulnerability checker, and general Linux CVE assessment tool
 leocottret/cve-2024-30956
(DOM-based XSS) HTML Injection vulnerability in TOWeb v.12.05 and before allows an attacker to inject HTML/JS code via the _message.html component.
 andrewd-cg/cve-2024-52005-poc
Proof-of-Concept for CVE-2024-52005: ANSI escape sequence injection in Git. Demonstrates incorrect 'not_affected' VEX claims in hardened container…
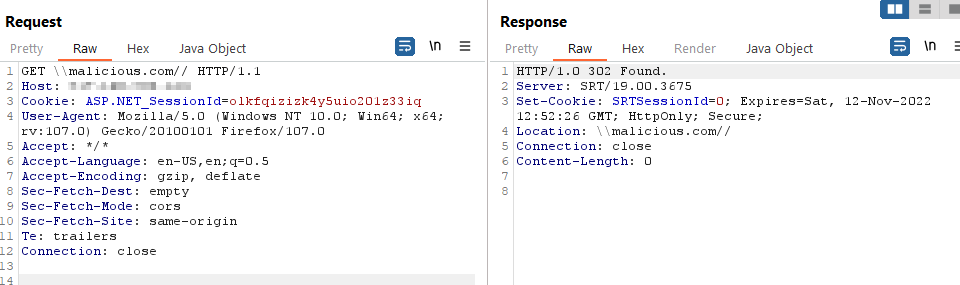 jbalanza/cve-2022-44215
Public disclosure of TitanFTP 19.X Open Redirection vulnerability
 jm-lemmi/cve-2019-17497
POC Files for CVE-2019-17497