
siofra
 cybereason/siofra
Simulates the Windows PE loader to identify DLL hijacking vulnerabilities, generates weaponized DLLs with shellcode payloads, and detects UAC…
binary-analysisbinary-exploitationpayload-generation+4
512
cybereason/siofraSimulates the Windows PE loader to identify DLL hijacking vulnerabilities, generates weaponized DLLs with shellcode payloads, and detects UAC…
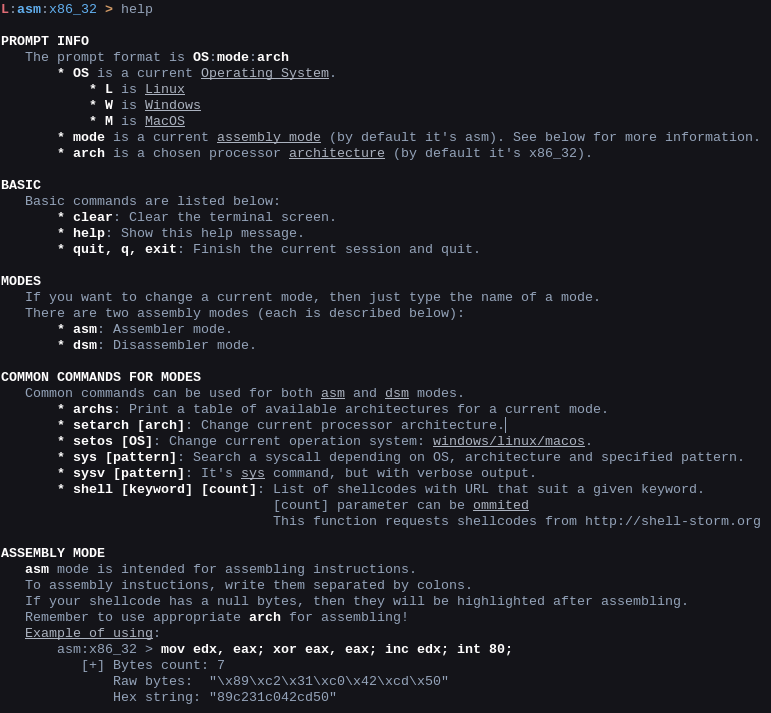 konatabrk/shellen
:cherry_blossom: Interactive shellcoding environment to easily craft shellcodes
 veil-framework/veil
Veil 3.1.X (Check version info in Veil at runtime)
 veil-framework/veil-evasion
Veil Evasion is no longer supported, use Veil 3.0!
 therealdreg/shellex
C-shellcode to hex converter, handy tool for paste & execute shellcodes in IDA PRO, gdb, windbg, radare2, ollydbg, x64dbg, immunity debugger & 010…
 rburrito/payloadgenerator
A wrapper for MSFvenom that allows for easy generation of payloads
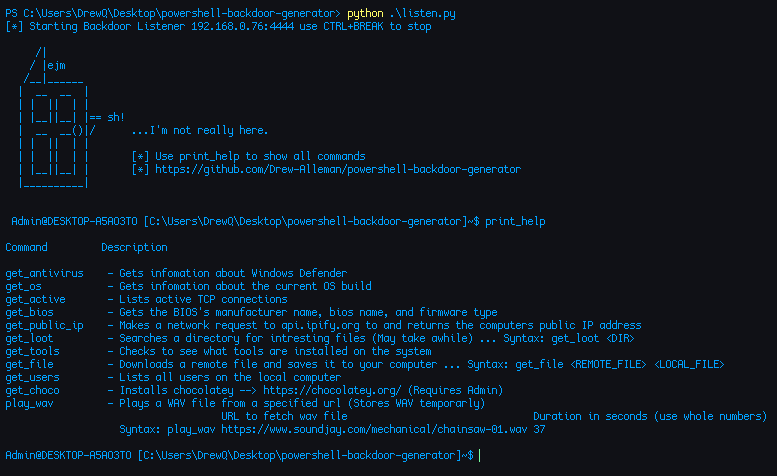 drew-alleman/powershell-backdoor-generator
Reverse backdoor written in PowerShell and obfuscated with Python. It generates payloads for popular hacking devices like Flipper Zero and Hak5 USB…
 klezvirus/syswhispers3
SysWhispers on Steroids - AV/EDR evasion via direct system calls.
 tanc7/exocet-av-evasion
EXOCET - AV-evading, undetectable, payload delivery tool
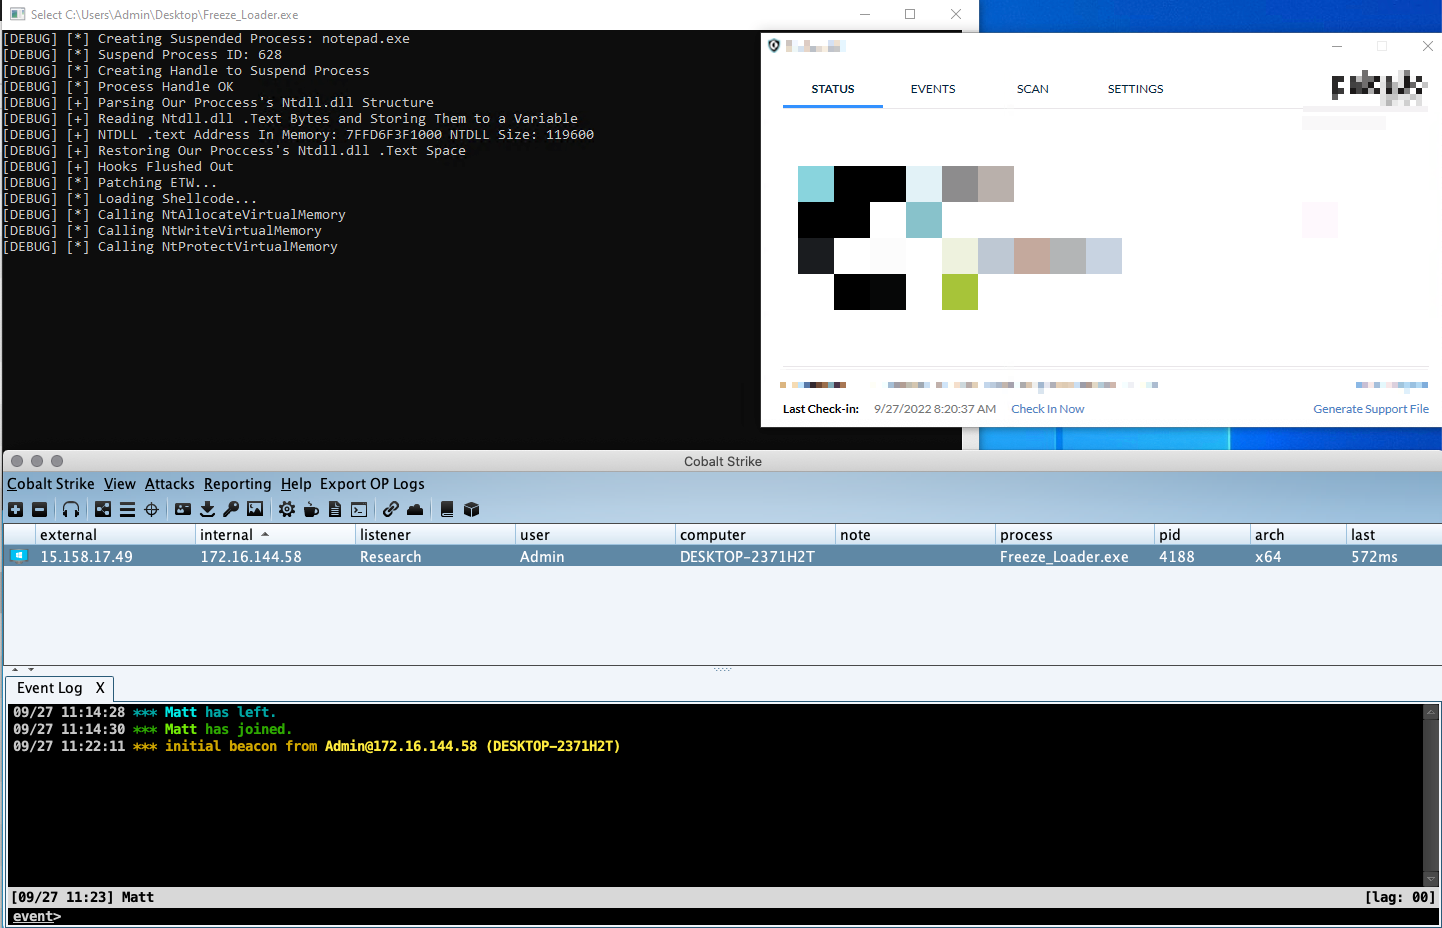 optiv/freeze
Freeze is a payload toolkit for bypassing EDRs using suspended processes, direct syscalls, and alternative execution methods
 zerx0r/kage
Kage is Graphical User Interface for Metasploit Meterpreter and Session Handler
 getrektboy724/meterpwrshell
Automated Tool That Generates The Perfect Meterpreter Powershell Payload
 iamsopotatoe-coder/tinyload
Open source Windows x64 PE packer and crypter. Compresses and encrypts executables with a custom virtual machine into a self extracting stub.
 oddcod3/phantom-evasion
Python antivirus evasion tool
 owasp/zsc
OWASP ZSC - Shellcode/Obfuscate Code Generator https://www.secologist.com/
 helviojunior/shellcodetester
An application to test windows and linux shellcodes
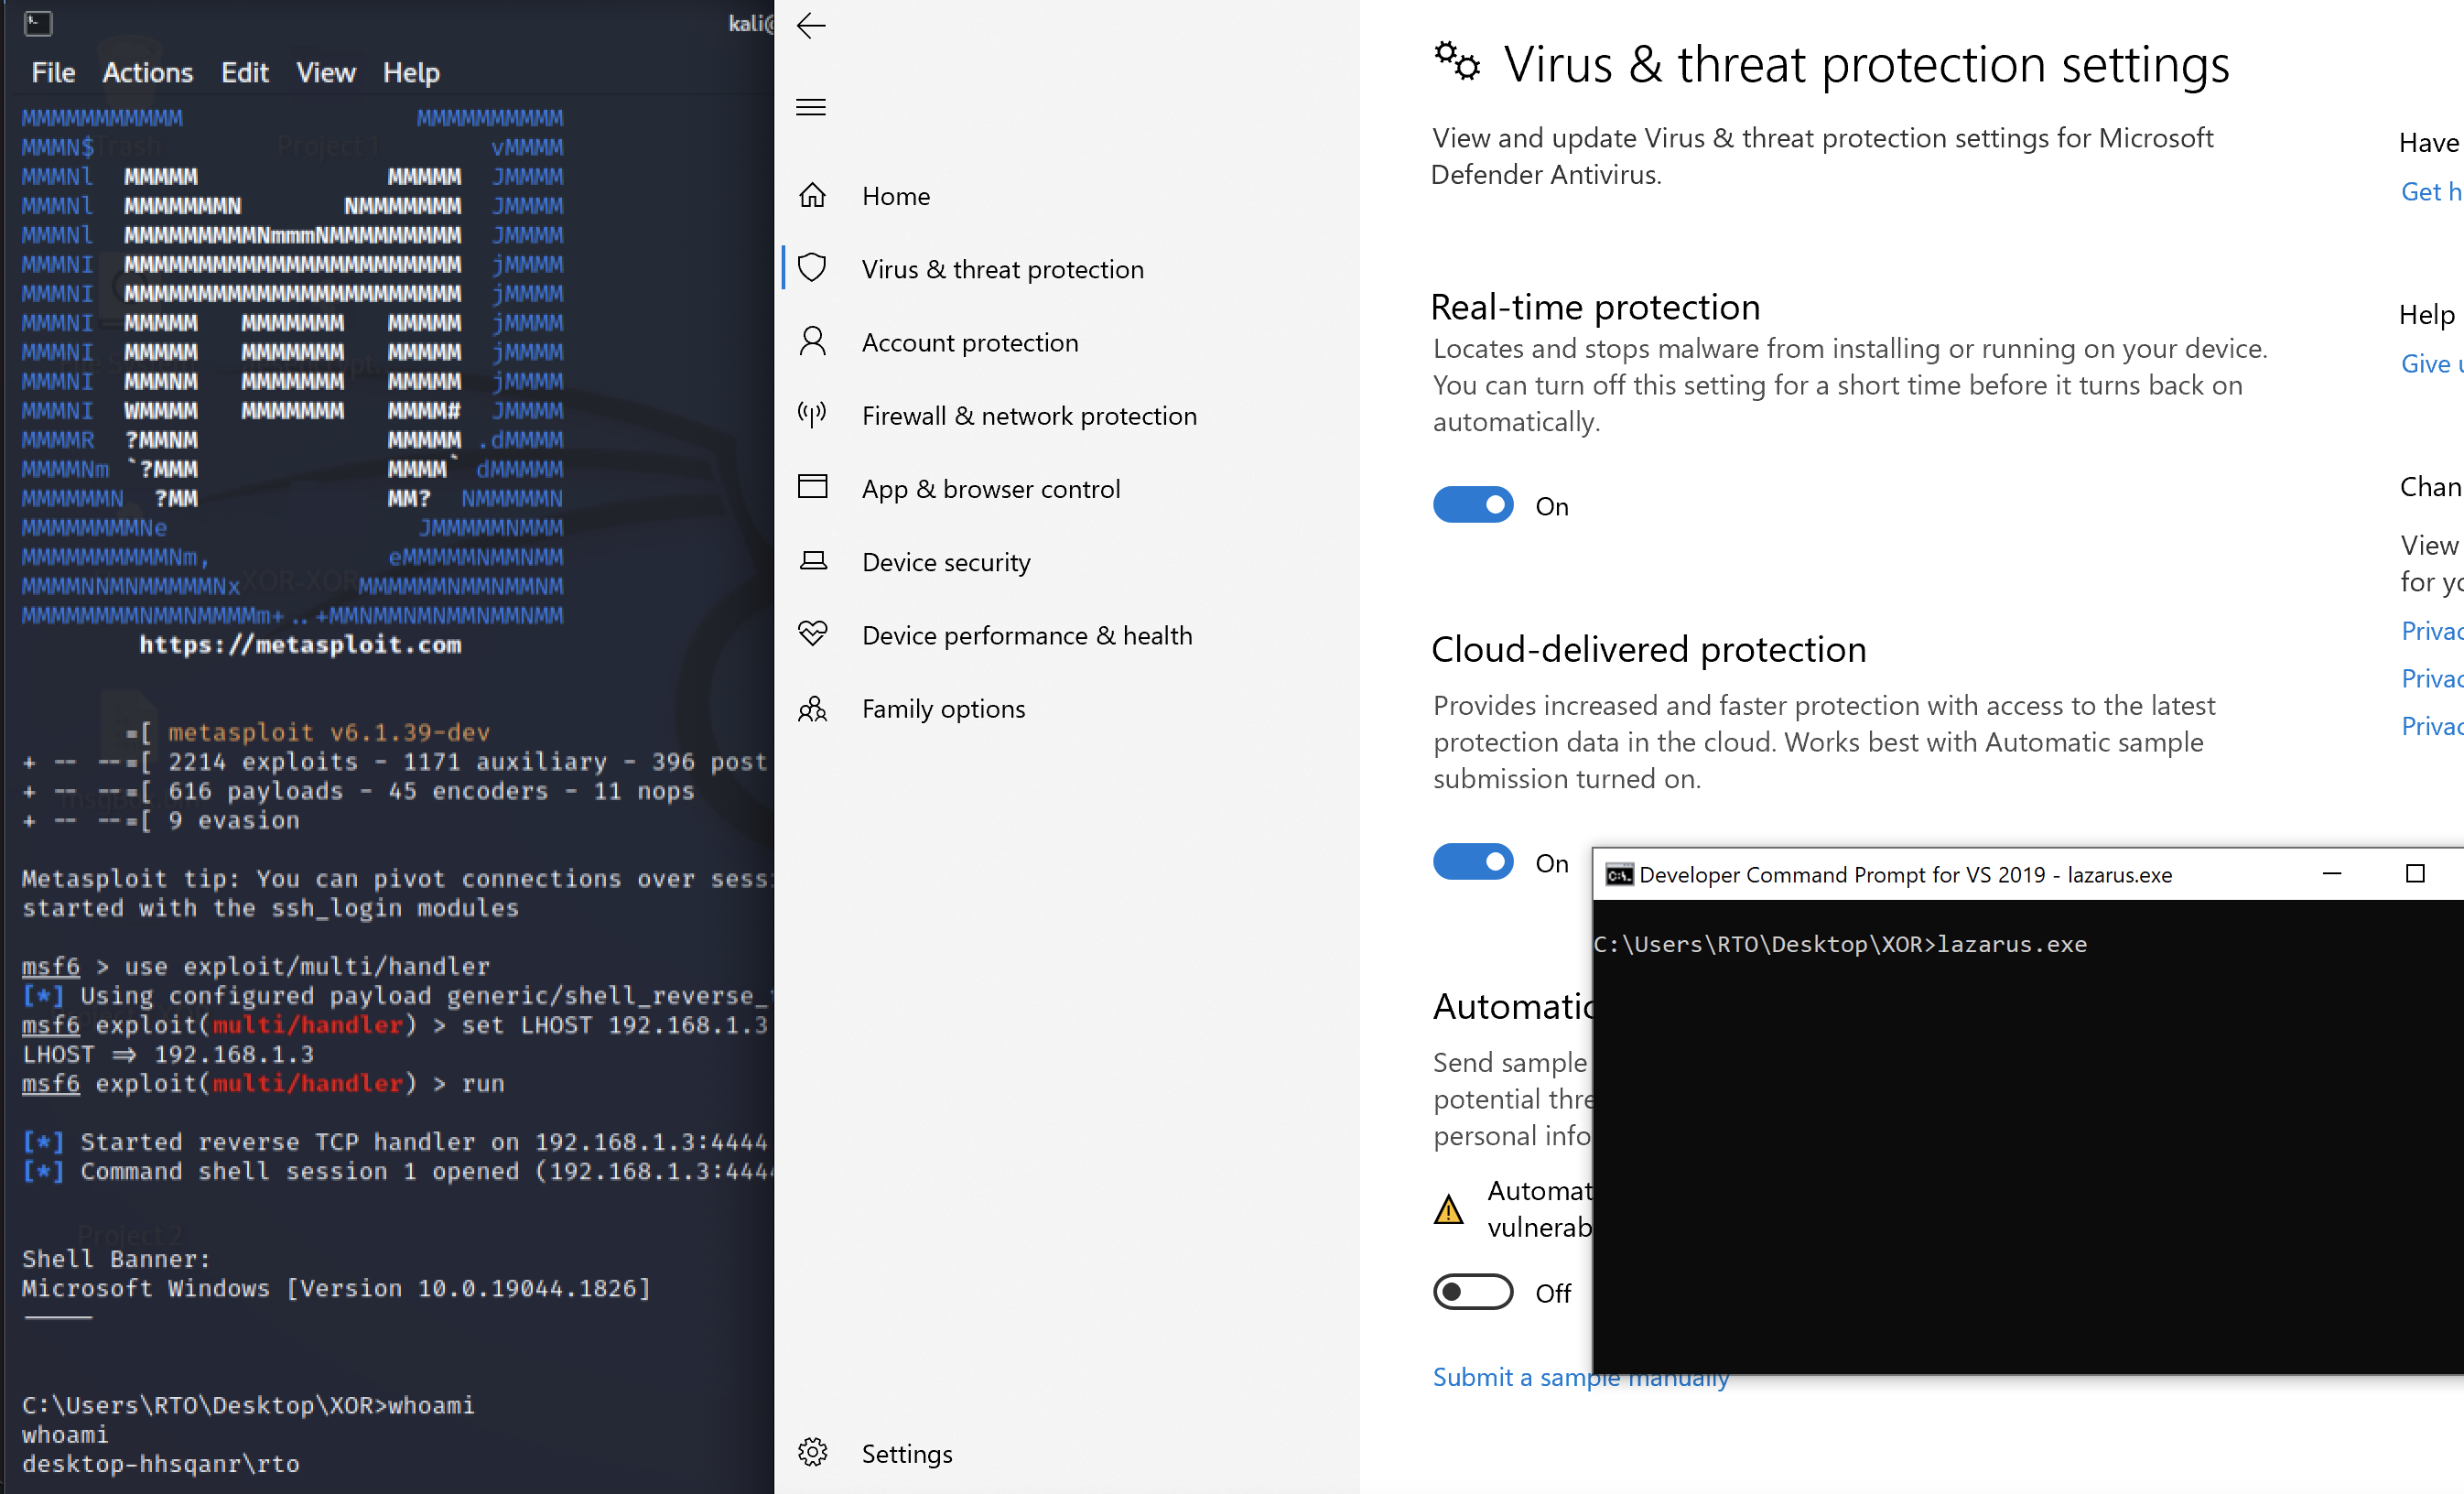 bl4ckm1rror/fud-uuid-shellcode
C++ shellcode injection technique using XOR encryption and UUID string conversion to bypass Windows Defender, with function call obfuscation and…
 spiralbl0ck/bypass-payloadrestrictions.dll-wdeg-rop-mitigation-
C-based PoC to bypass Windows PayloadRestrictions.dll and wdeg ROP mitigation, enabling payload execution and binary exploitation for security…