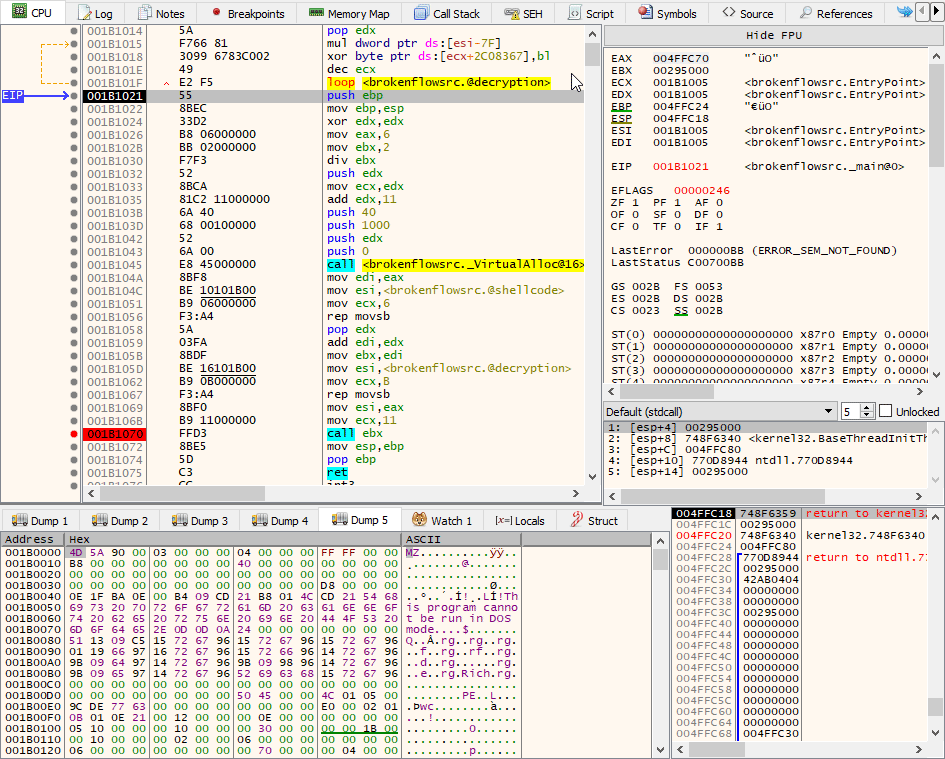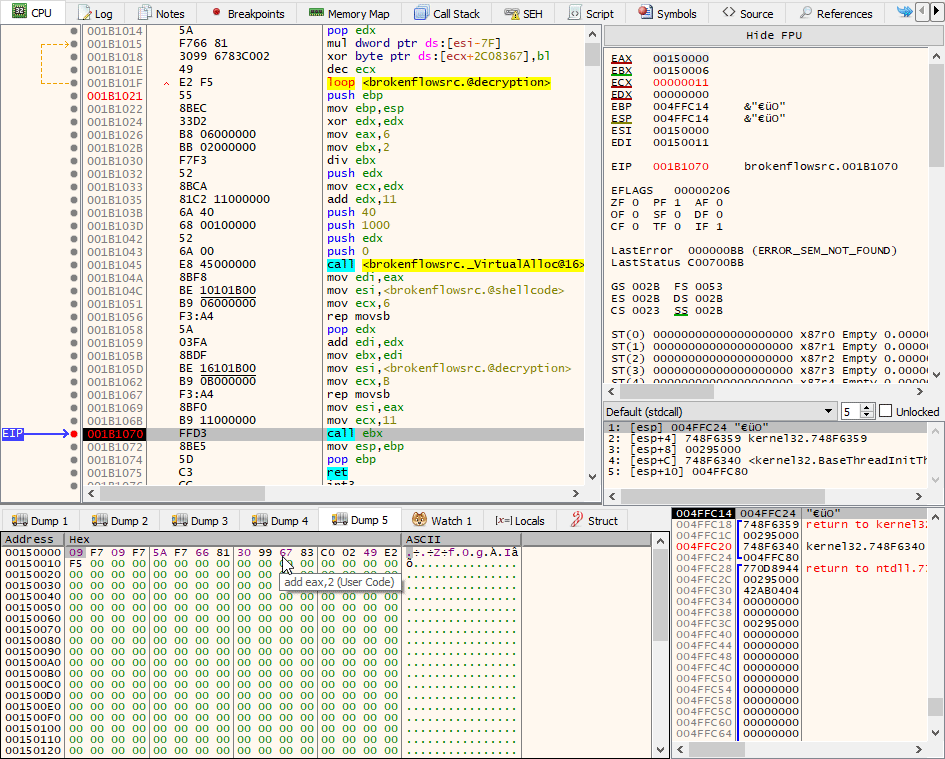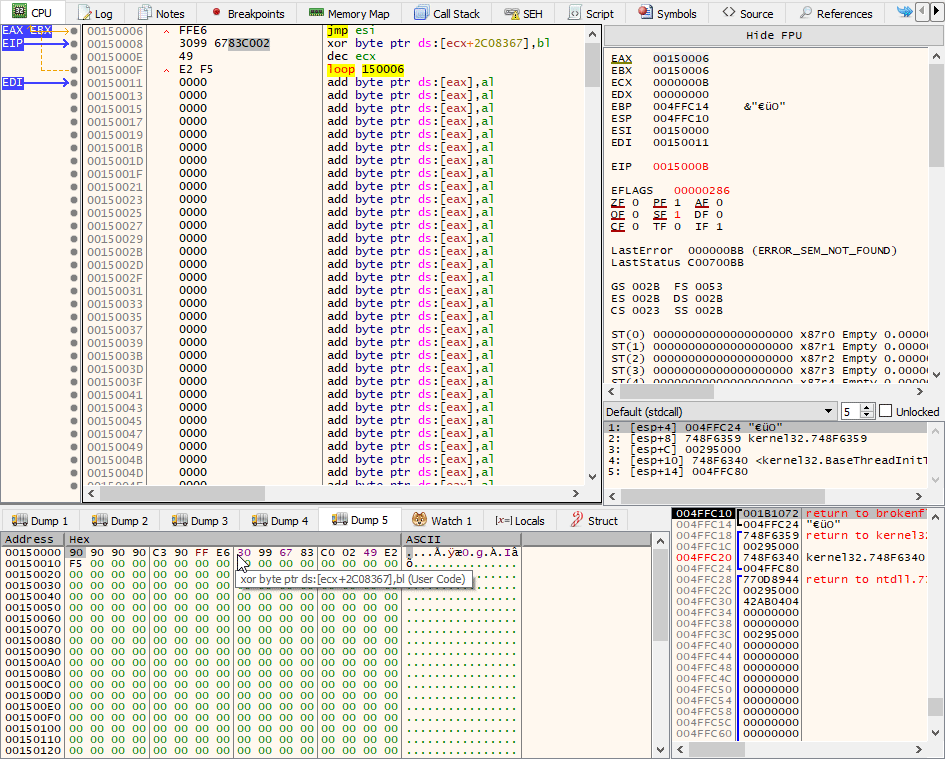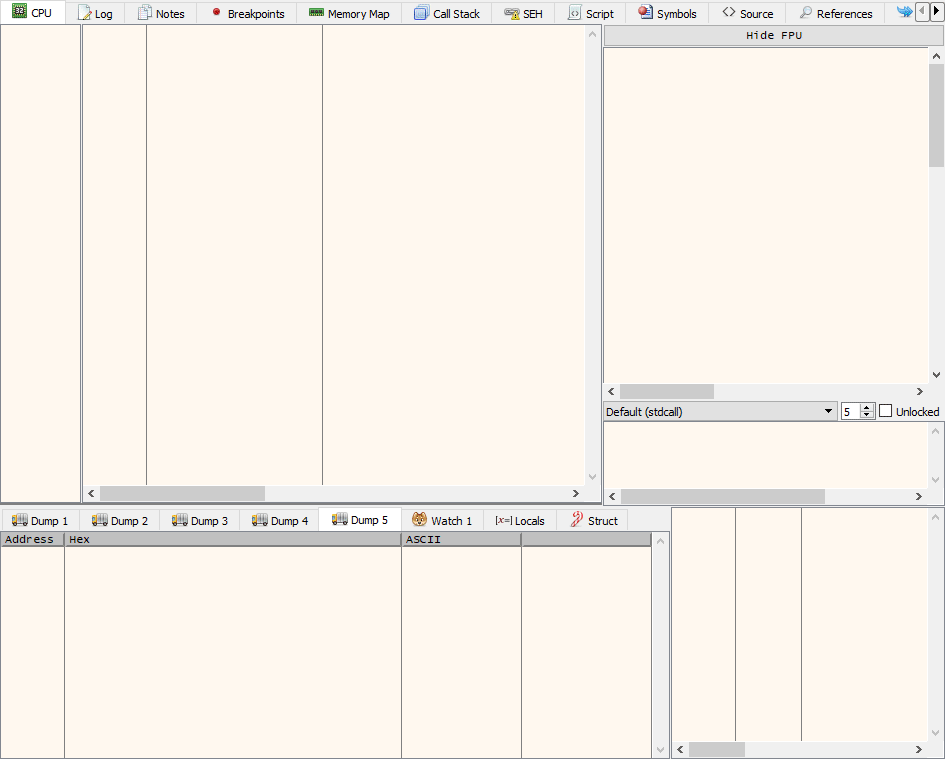
BrokenFlow
 enkomio/brokenflow
A simple PoC to invoke an encrypted shellcode by using an hidden call
binary-exploitationencryption-decryption-toolsexploitation+4
1153 years ago
enkomio/brokenflowA simple PoC to invoke an encrypted shellcode by using an hidden call
 alberties/ghostfuscator
The Python Password-Protected Obfuscator
 sliverarmory/malasada
Linux Shared Library to Shellcode Loader
 seanheelan/anamnesis-release
Evaluation framework for studying LLM agents that automatically generate working exploits from vulnerability reports, bypassing modern security…
 oldboy21/shgenob
Python based tool for generating Shellcode from PIC C
 0xsha/cve-2026-6307
Google Chrome CVE-2026-6307 PoC
 bc-security/empire
Empire is a post-exploitation and adversary emulation framework that is used to aid Red Teams and Penetration Testers.
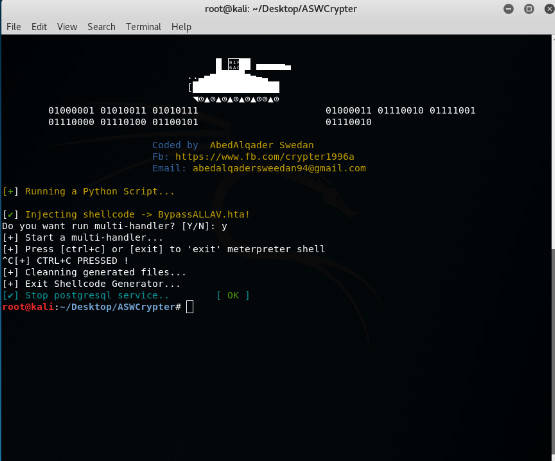 abedalqaderswedan1/aswcrypter
An Bash&Python Script For Generating Payloads that Bypasses All Antivirus so far [FUD]
 kasturixbm5/staged-dll-injection-smb-
Staged DLL injection proof-of-concept built in C using Win32 APIs — developed in an isolated lab environment for red team certification study (CRTO).
 mahmoudimus/static_asm
Header-only C++2x compile-time assembler for x86/x86-64 instruction encoding
 ac8999/cve-2009-3999-hp-power-manager-4.2-build-7-buffer-overflow
Automatic script written in python for CVE-2009-3999
 runik/harmonic
Suite for reverse shell handling geared toward working within the native shell
 egebalci/egesploit
EGESPLOIT is a golang library for malware development
 octetsplicer/lazypariah
A tool for generating reverse shell payloads on the fly.
 m4sc3r4n0/astroid
ASTROID v 1.2 bypass most A.V softwares
 watchtowrlabs/watchtowr-vs-citrix-netscaler-preauth-rce-cve-2026-8452
CVE-2026-8452 PreAuth RCE