
POC-CVE-2026-0300-exploit
 sam00/poc-cve-2026-0300-exploit
Palo Alto - CVE-2026-0300 exploit
binary-exploitationexploitationnetwork-security+6
sam00/poc-cve-2026-0300-exploitPalo Alto - CVE-2026-0300 exploit
 flabbergastedbd/cve-2019-11707
https://bugs.chromium.org/p/project-zero/issues/detail?id=1820
 drac0nids/cve-2017-8570
## 在kali中自动化生成cve-2017-8570的恶意ppsx文件和配置msf监听
 hackthem/openstamanager_rce_exploit-cve-2026-38751-
OpenSTAManager RCE Exploit (CVE-2026-38751)
 stuub/cve-2025-3969-exploit
CVE-2025-3969: Exploit PoC (OS CMD injection, Web Shell, Interactive Shell)
 paulsery/cve-2021-30632
m-y-mo: https://github.com/github/securitylab/tree/main/SecurityExploits/Chrome/v8/CVE-2021-30632
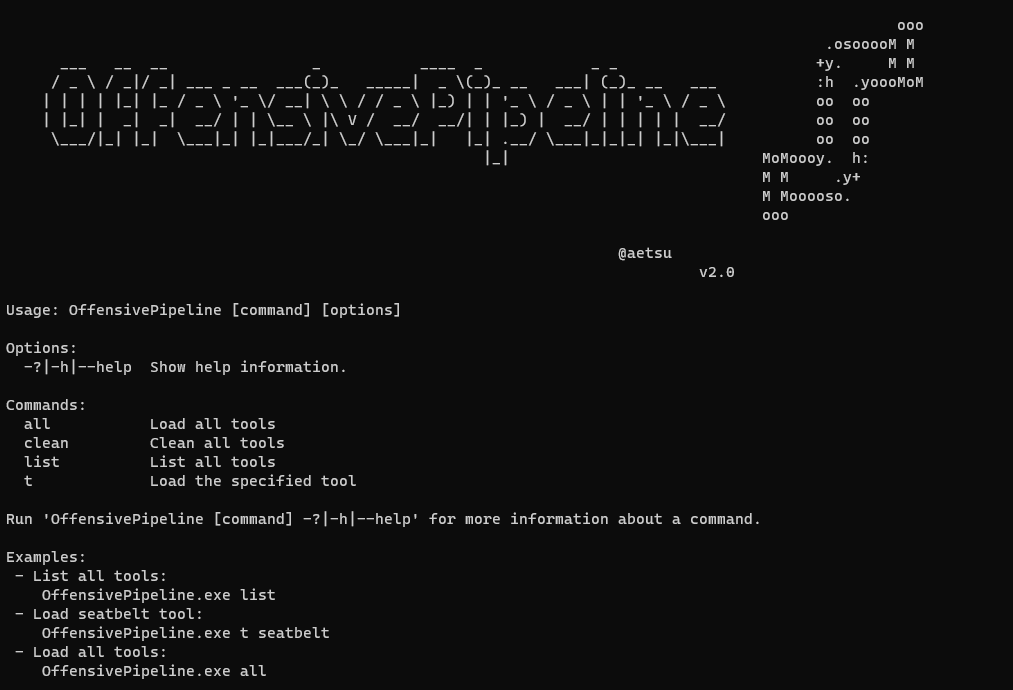 aetsu/offensivepipeline
OfensivePipeline allows you to download and build C# tools, applying certain modifications in order to improve their evasion for Red Team exercises.
 pwn1sher/frostbyte
Combines AppDomain Manager injection with shellcode embedding in signed binaries to evade EDR/AV detection for red team payloads.
 runik/harmonic
Suite for reverse shell handling geared toward working within the native shell
 m4sc3r4n0/astroid
ASTROID v 1.2 bypass most A.V softwares
 s0lst1c3/dropengine
DropEngine provides a malleable framework for creating shellcode runners, allowing operators to choose from a selection of components and combine…
 machine1337/fudshell
An efficent Script To Generate FUD Persistent Reverse Shell For Red Teaming. Don't Upload Generated Stub On Virustotal
 licitrasimone/crystalsliver
Crystal Palace Evasion kit for Sliver
 connormcgarr/littlecorporal
LittleCorporal: A C# Automated Maldoc Generator
 ohjeongwook/shellcodeemulator
Shellcode emulator written with Unicorn Framework With Process Dump Emulation Environment
 souhardya/zerodoor
A script written lazily for generating cross-platform backdoors on the go :)
 techryptic/pokemon-shellcode-loader
Tired of looking at hex all day and popping '\x41's? Rather look at Lugia/Charmander? I have the solution for you.
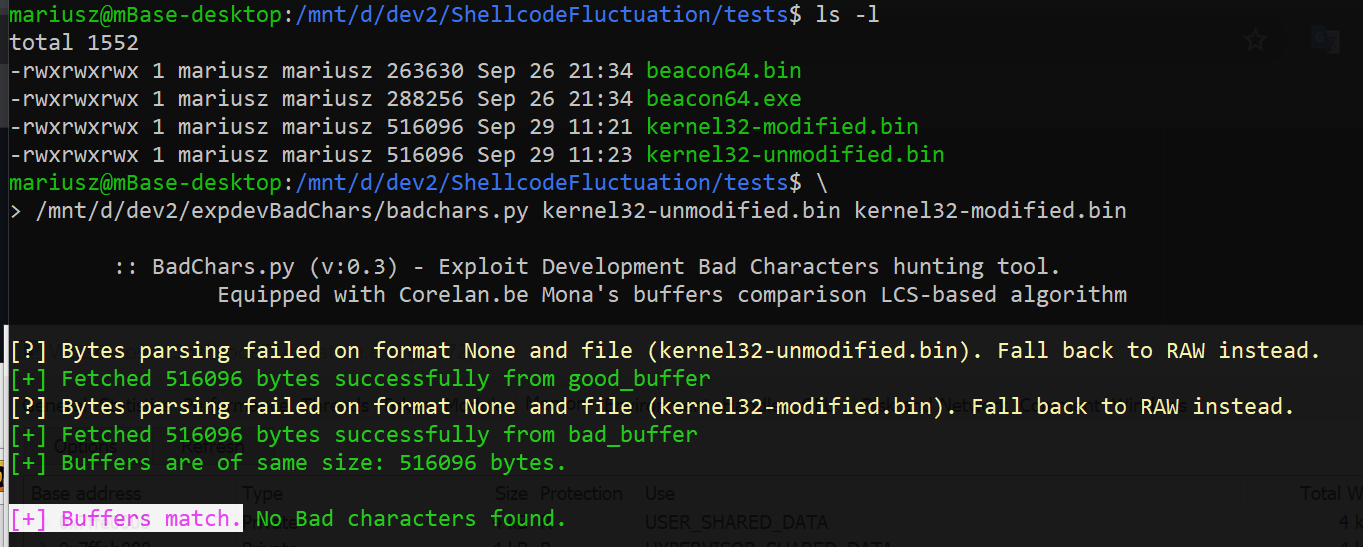 mgeeky/shellcodefluctuation
An advanced in-memory evasion technique fluctuating shellcode's memory protection between RW/NoAccess & RX and then encrypting/decrypting its contents