
SILVERPICK
 winterknife/silverpick
Windows User-Mode Shellcode Development Framework (WUMSDF)
exploitationpayload-developmentred-teaming+2
159
winterknife/silverpickWindows User-Mode Shellcode Development Framework (WUMSDF)
 dis0rder0x00/dbgnexum
Shellcode injection using the Windows Debugging API

 watchtowrlabs/watchtowr-vs-citrix-netscaler-preauth-rce-cve-2026-8452
CVE-2026-8452 PreAuth RCE
 mracumen/cve-2021-40444
Microsoft-Office-Word-MSHTML-Remote-Code-Execution-Exploit
 andrewtrube/cve-2014-7205
Bassmaster Plugin NodeJS RCE
 thewover/donut
Generates x86, x64, or AMD64+x86 position-independent shellcode that loads .NET Assemblies, PE files, and other Windows payloads from memory and runs…
 hasherezade/pe_to_shellcode
Converts PE into a shellcode
 omerya/invisi-shell
Hide your Powershell script in plain sight. Bypass all Powershell security features
 med0x2e/executeassembly
Load/Inject .NET assemblies by; reusing the host (spawnto) process loaded CLR AppDomainManager, Stomping Loader/.NET assembly PE DOS headers,…
 cryptolok/aslray
Linux ELF x32/x64 ASLR DEP/NX bypass exploit with stack-spraying
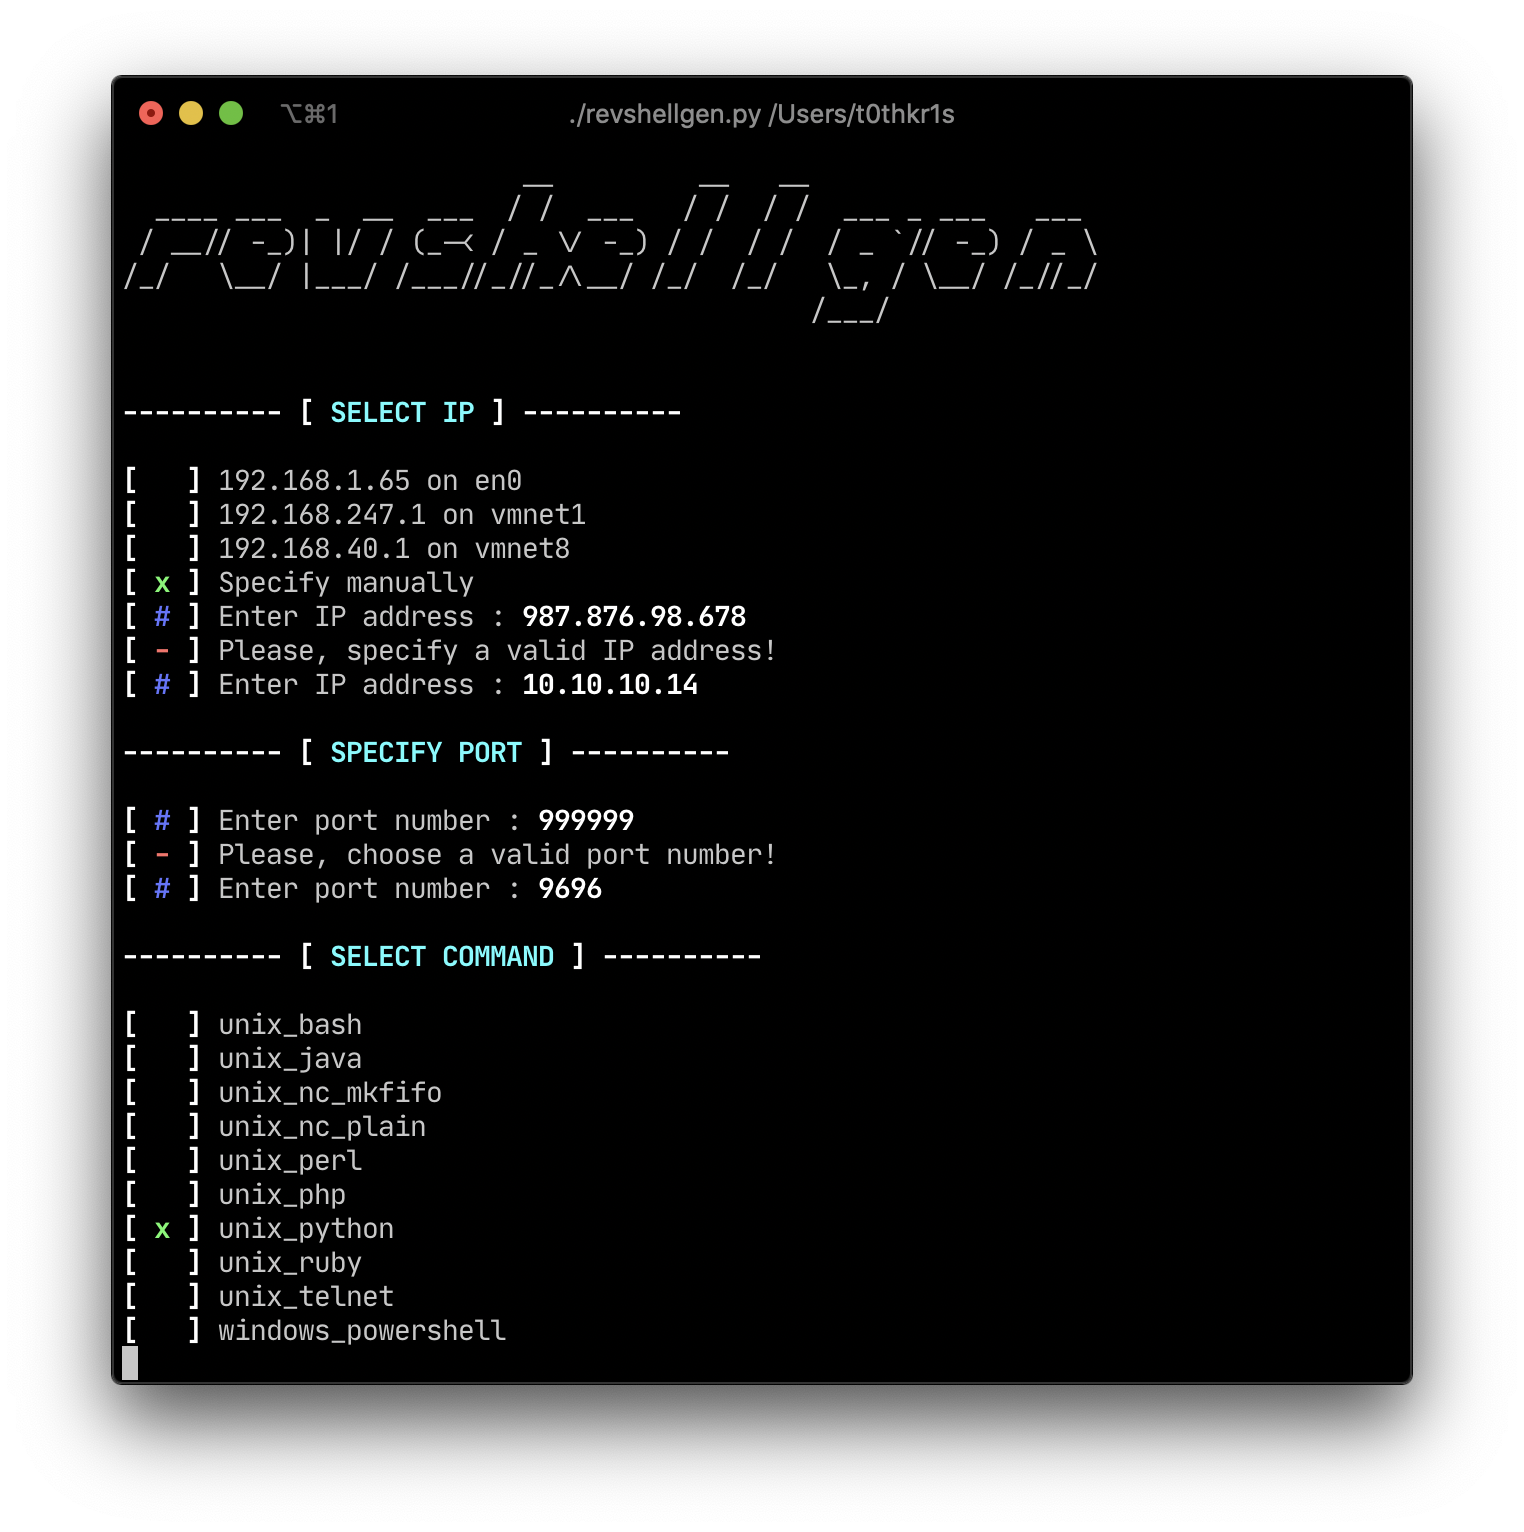 t0thkr1s/revshellgen
Reverse shell generator written in Python 3.
 hatriot/shellme
simple shellcode generator
 hacksysteam/cve-2022-28672
Foxit PDF Reader Remote Code Execution Exploit
 elweth-sec/cve-2023-2255
CVE-2023-2255 Libre Office
 pimps/cve-2019-2725
WebLogic Insecure Deserialization - CVE-2019-2725 payload builder & exploit
 umpolungfish/byvalver
takes shellcode bad-bytes and banishes them, returning cleaned shellcode with preserved functionalities
