
CVE-2009-3999-HP-Power-Manager-4.2-Build-7-Buffer-Overflow
 ac8999/cve-2009-3999-hp-power-manager-4.2-build-7-buffer-overflow
Automatic script written in python for CVE-2009-3999
binary-exploitationeducationexploitation+6
ac8999/cve-2009-3999-hp-power-manager-4.2-build-7-buffer-overflowAutomatic script written in python for CVE-2009-3999
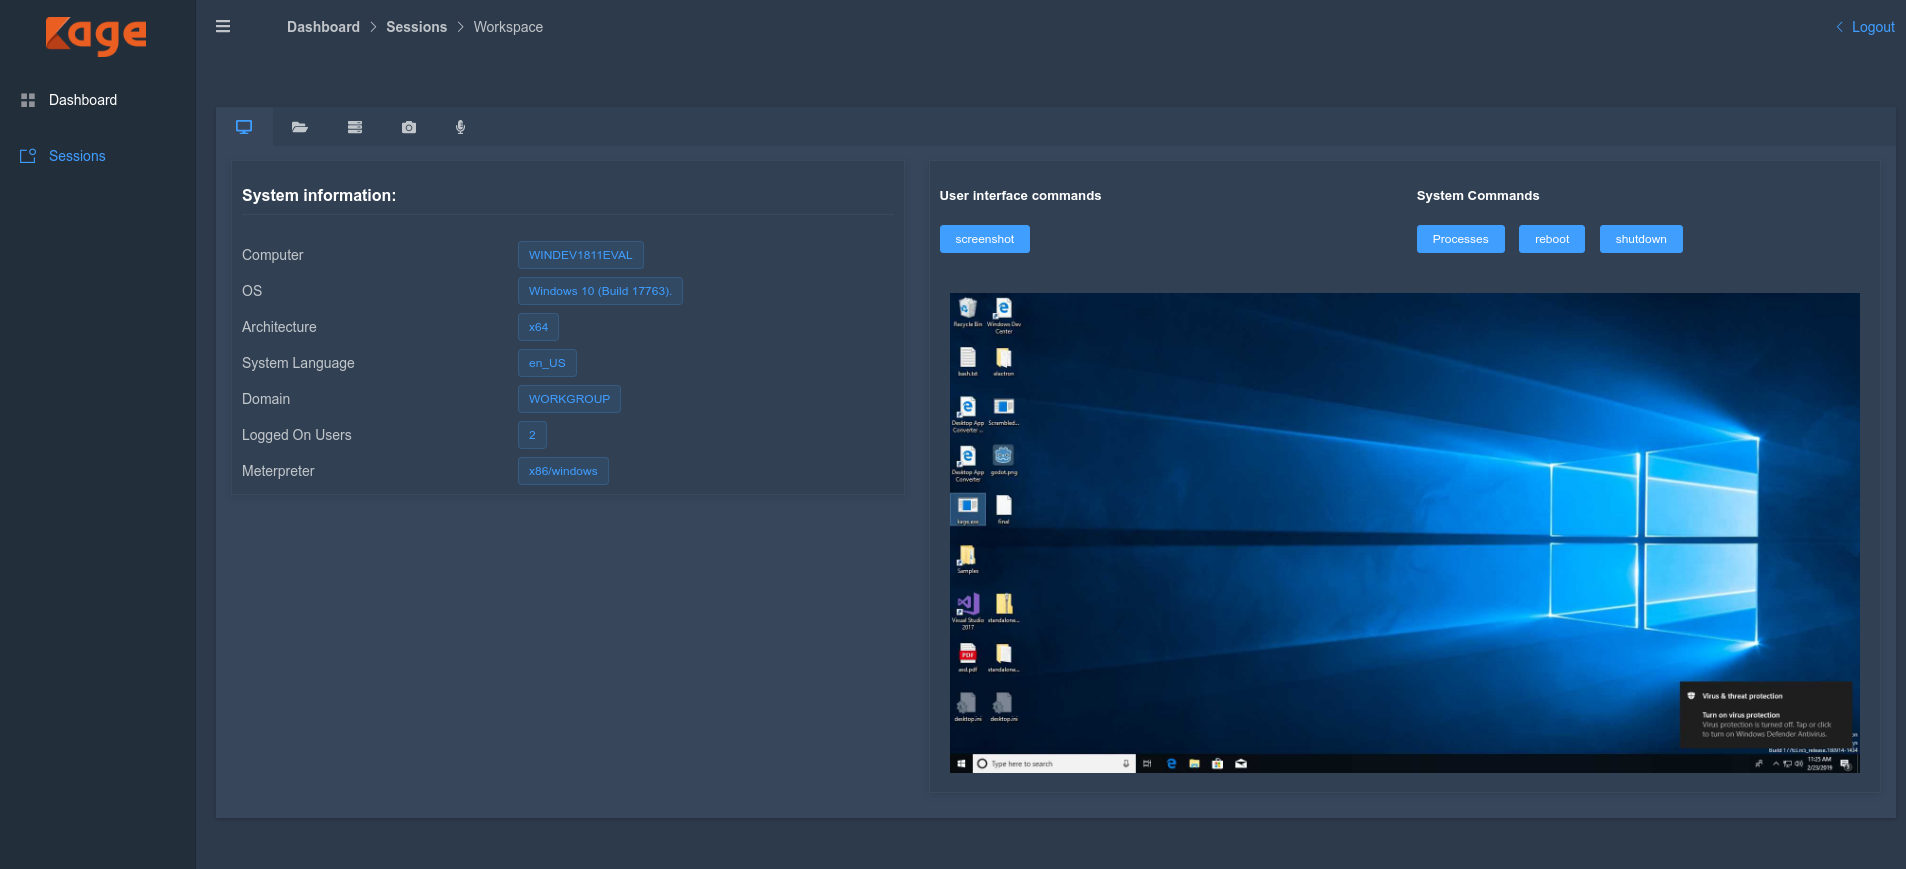 zerx0r/kage
Kage is Graphical User Interface for Metasploit Meterpreter and Session Handler
 bishopfox/sliver
Adversary Emulation Framework
 ne0nd0g/merlin
Merlin is a cross-platform post-exploitation HTTP/2 Command & Control server and agent written in golang.

 monoxgas/srdi
Shellcode implementation of Reflective DLL Injection. Convert DLLs to position independent shellcode
 klezvirus/syswhispers3
SysWhispers on Steroids - AV/EDR evasion via direct system calls.
 nytrorst/shellcodecompiler
Shellcode Compiler
 mgeeky/shellcodefluctuation
An advanced in-memory evasion technique fluctuating shellcode's memory protection between RW/NoAccess & RX and then encrypting/decrypting its contents

 vlad902/hacking-team-windows-kernel-lpe
Previously-0day exploit from the Hacking Team leak, written by Eugene Ching/Qavar.
 senzee1984/micr0_shell
micr0shell is a Python script that dynamically generates Windows X64 PIC Null-Free reverse shell shellcode.
 iamsopotatoe-coder/tinyload
Open source Windows x64 PE packer and crypter. Compresses and encrypts executables with a custom virtual machine into a self extracting stub.
 winterknife/silverpick
Windows User-Mode Shellcode Development Framework (WUMSDF)
 dis0rder0x00/dbgnexum
Shellcode injection using the Windows Debugging API
 watchtowrlabs/watchtowr-vs-citrix-netscaler-preauth-rce-cve-2026-8452
CVE-2026-8452 PreAuth RCE
