
put2win
 devploit/put2win
Script to automate PUT HTTP method exploitation to get shell
exploitationpenetration-testingshellcode-generation+1
devploit/put2winScript to automate PUT HTTP method exploitation to get shell
 licitrasimone/crystalsliver
Crystal Palace Evasion kit for Sliver
 rad9800/pmd
Practical Windows malware development course: API hashing, DLL sideloading, shellcode execution, PE manipulation, payload hosting, and delivery labs.
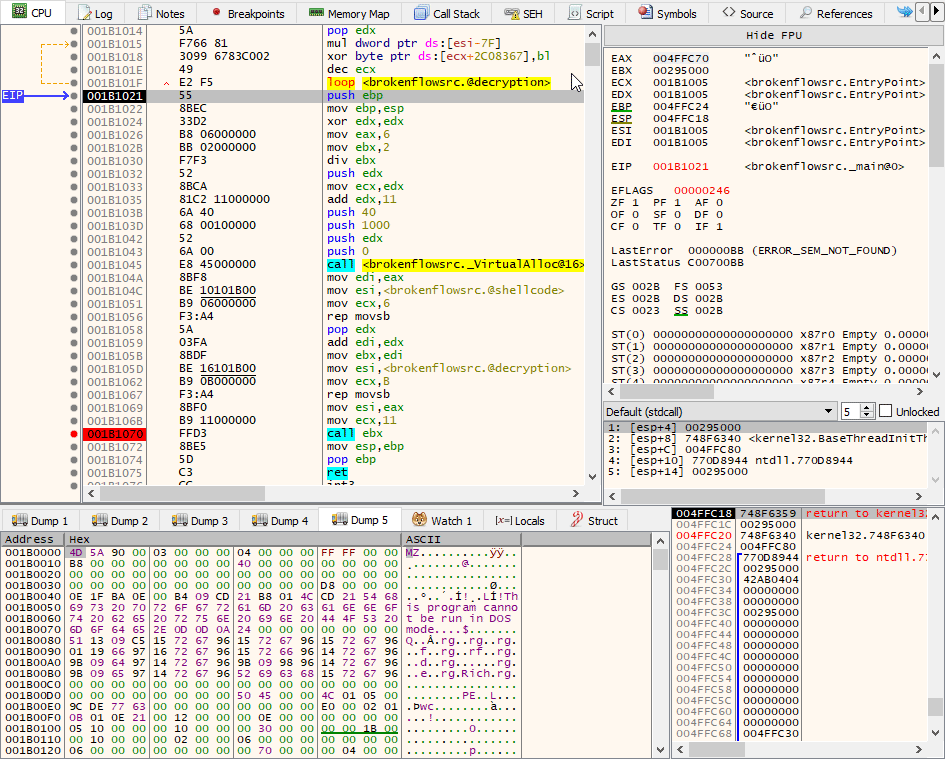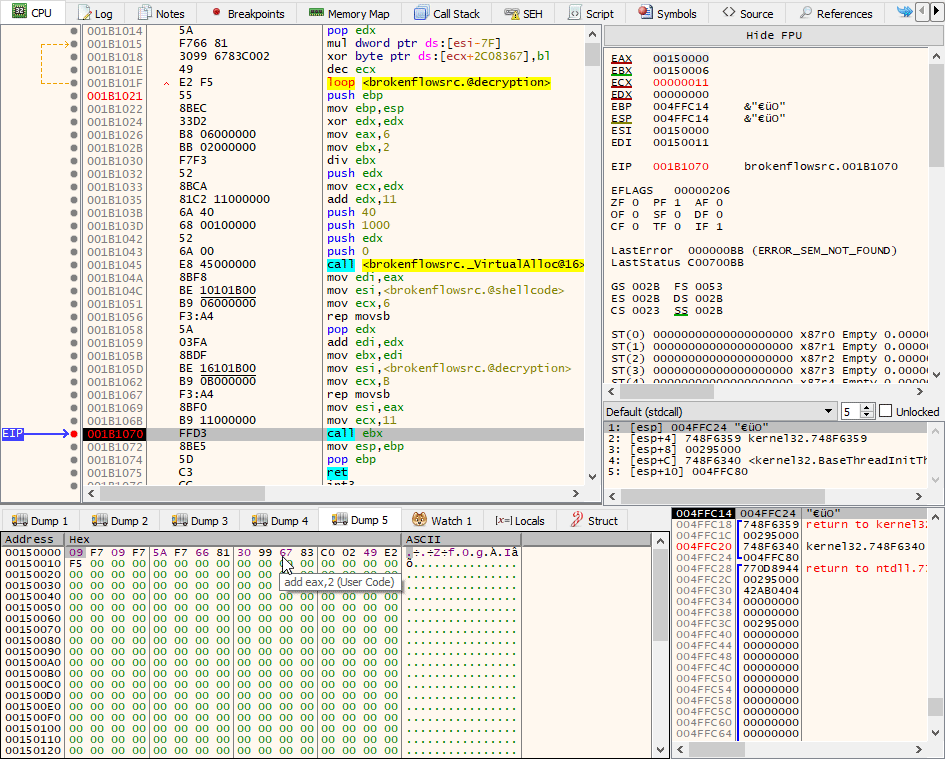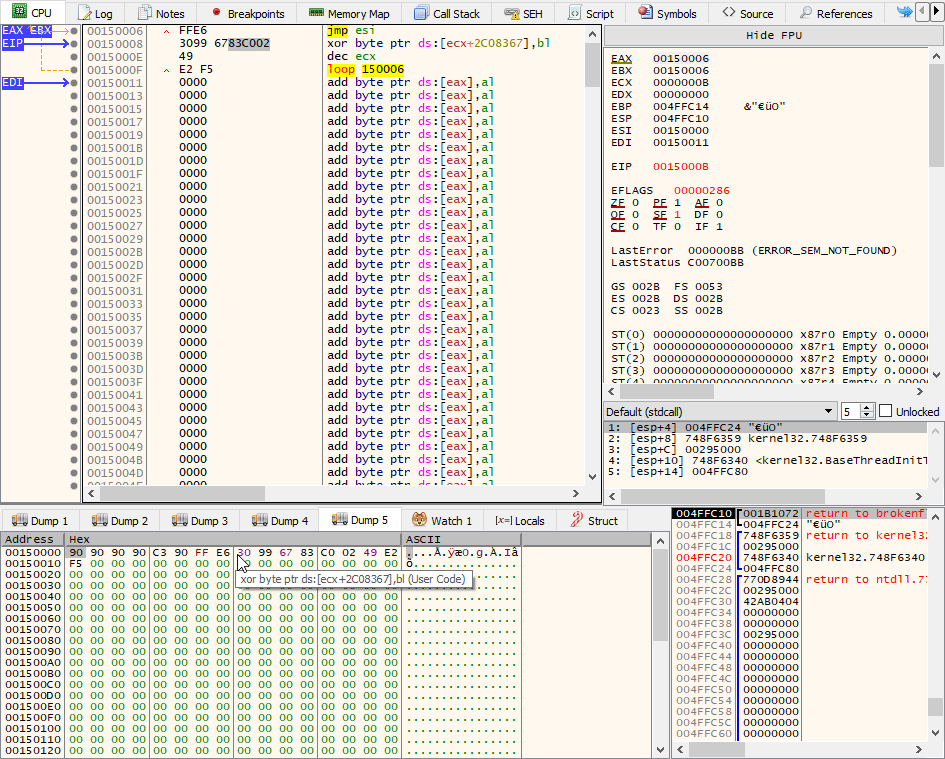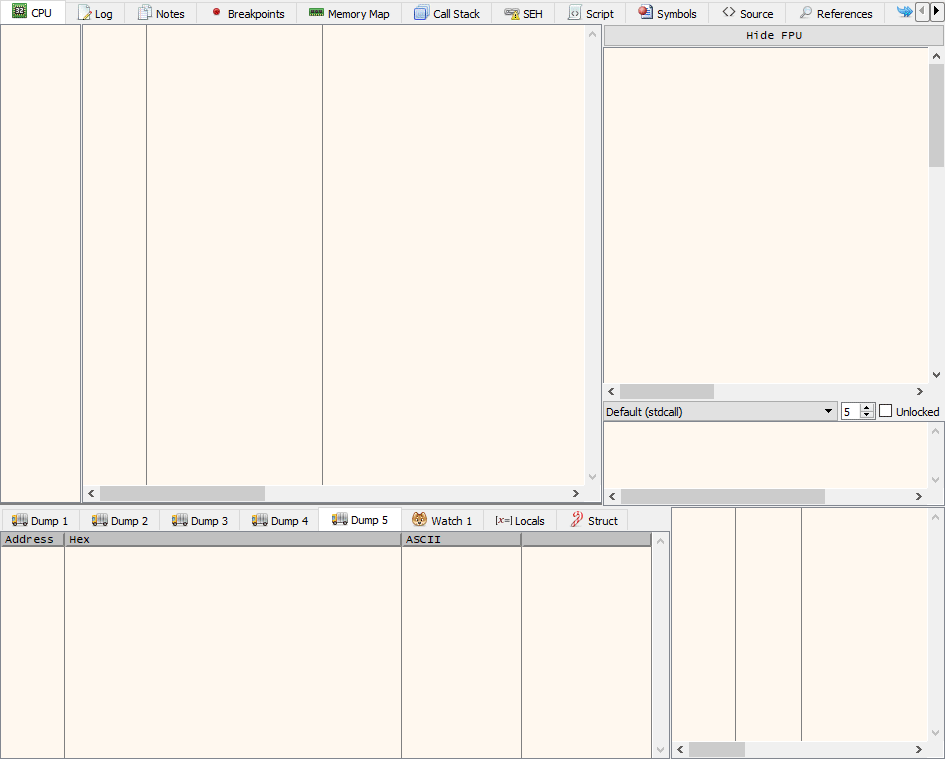 enkomio/brokenflow
A simple PoC to invoke an encrypted shellcode by using an hidden call
 watchtowrlabs/watchtowr-vs-citrix-netscaler-preauth-rce-cve-2026-8452
CVE-2026-8452 PreAuth RCE
 techryptic/pokemon-shellcode-loader
Tired of looking at hex all day and popping '\x41's? Rather look at Lugia/Charmander? I have the solution for you.
 chaelsoo/hollow
A shellcode loader generator with support for multiple injection techniques, built for red team engagements.
 praetorian-inc/wasmforge
WasmForge — compile Go and C# programs to single-binary, WASM-sandboxed native executables with polymorphic output.
 0xsha/cve-2026-6307
Google Chrome CVE-2026-6307 PoC
 g13net/lockjaw
Modular Windows C2 framework with a Rust teamserver, Zig implant, indirect syscalls, AMSI bypass, reflective/PoolParty injection, in-memory BOF…
 elweth-sec/cve-2023-2255
CVE-2023-2255 Libre Office
 pimps/cve-2019-2725
WebLogic Insecure Deserialization - CVE-2019-2725 payload builder & exploit
 saerxcit/libtp_gadget
Crystal Palace library for proxying Nt API calls via the Threadpool. Updated for call gadgets.
 l-urk/cve-2024-6387
Proof of concept python script for regreSSHion exploit.