
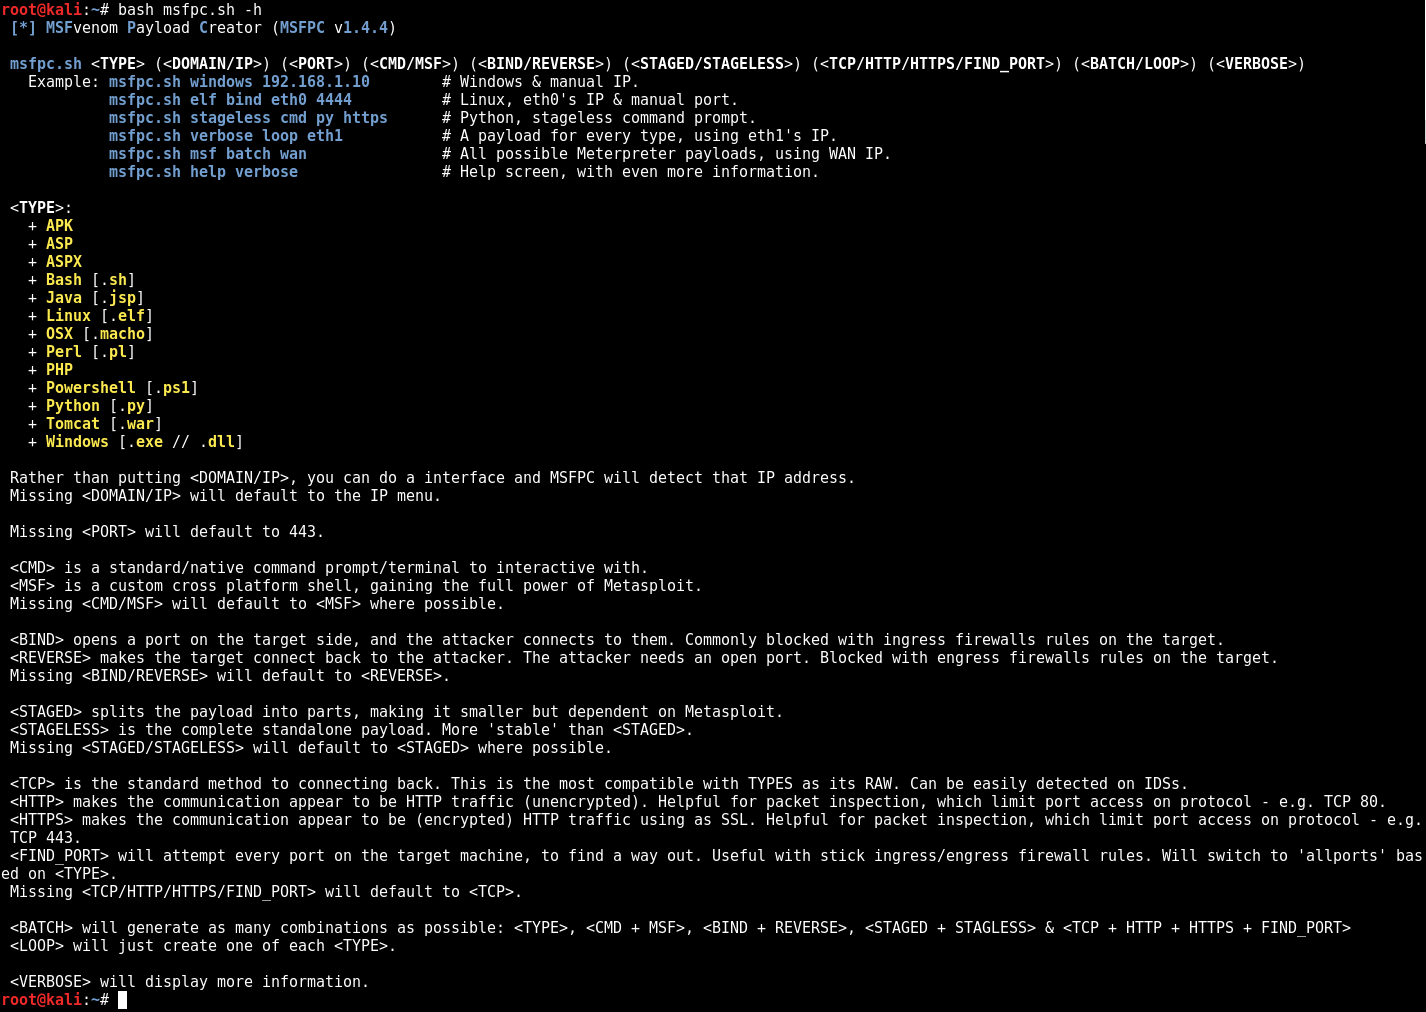
msfpc
 g0tmi1k/msfpc
MSFvenom Payload Creator (MSFPC)
command-and-controlexploit-frameworkspayload-development+5
g0tmi1k/msfpcMSFvenom Payload Creator (MSFPC)
 rvn0xsy/cooolis-ms
Cooolis-ms是一个包含了Metasploit Payload Loader、Cobalt Strike External C2 Loader、Reflective DLL injection的代码执行工具,它的定位在于能够在静态查杀上规避一些我们将要执行且含有特征的代码,帮助红队人员更方便快…
 petitoto/chromium-exploit-dev
Toolkit to weaponize Chromium vulnerabilities into reliable, cross-platform, full-chain exploits

 licitrasimone/crystalsliver
Crystal Palace Evasion kit for Sliver
 bishopfox/joro
A collaborative web exploitation framework.
 egebalci/hercules
HERCULES is a special payload generator that can bypass antivirus softwares.
 bhassani/eternalbluec
EternalBlue suite remade in C/C++ which includes: MS17-010 Exploit, EternalBlue vulnerability detector, DoublePulsar detector and DoublePulsar…
 carsonshaffer/cve-2020-7384
Bash exploit script for CVE-2020-7384, a remote code execution vulnerability in Apache NiFi, with improved usability and quality-of-life enhancements.
 y0naldez/cve-2024-28397-js2py-rce
Generates JavaScript payloads to exploit CVE-2024-28397 Js2Py sandbox escape, enabling remote command execution and reverse shells via Python…
 nudttan91/webmin-cve-2022-0824-enhanced-exploit
Python exploit for Webmin CVE-2022-0824 with dual-mode support: direct command execution and reverse shell. Features multiple payload types,…
 johnjohnsp1/cve-2014-4113
PowerShell-based exploit for CVE-2014-4113 targeting x64 Windows systems with remote payload download and execution.
 boydhacks/dameflare
Python 3 exploit for CVE-2019-3980. Unauthenticated RCE as SYSTEM via SolarWinds Dameware MRC smart card authentication bypass.
 hacksysteam/cve-2022-28672
Foxit PDF Reader Remote Code Execution Exploit
 tremwil/ds3-nrssr-rce
Documentation and proof of concept code for CVE-2022-24125 and CVE-2022-24126.
 stuub/cve-2025-3969-exploit
CVE-2025-3969: Exploit PoC (OS CMD injection, Web Shell, Interactive Shell)
 ne0nd0g/merlin
Merlin is a cross-platform post-exploitation HTTP/2 Command & Control server and agent written in golang.
 bc-security/empire
Empire is a post-exploitation and adversary emulation framework that is used to aid Red Teams and Penetration Testers.