

Pokemon-Shellcode-Loader
 techryptic/pokemon-shellcode-loader
Tired of looking at hex all day and popping '\x41's? Rather look at Lugia/Charmander? I have the solution for you.
adversarial-attackpayload-developmentpayload-generation+3
126
techryptic/pokemon-shellcode-loaderTired of looking at hex all day and popping '\x41's? Rather look at Lugia/Charmander? I have the solution for you.
 saerxcit/libtp_gadget
Crystal Palace library for proxying Nt API calls via the Threadpool. Updated for call gadgets.
 l-urk/cve-2024-6387
Proof of concept python script for regreSSHion exploit.
 justin-p/psforgot2keyxchange
PoC for Forgot2kEyXCHANGE (CVE-2020-0688) written in PowerShell
 voidsecsoftwares/voidsec-proxy
Multi-module offensive security toolkit for SOCKS5 proxy chaining, port scanning, DNS enumeration, hash cracking, reverse shell generation,…
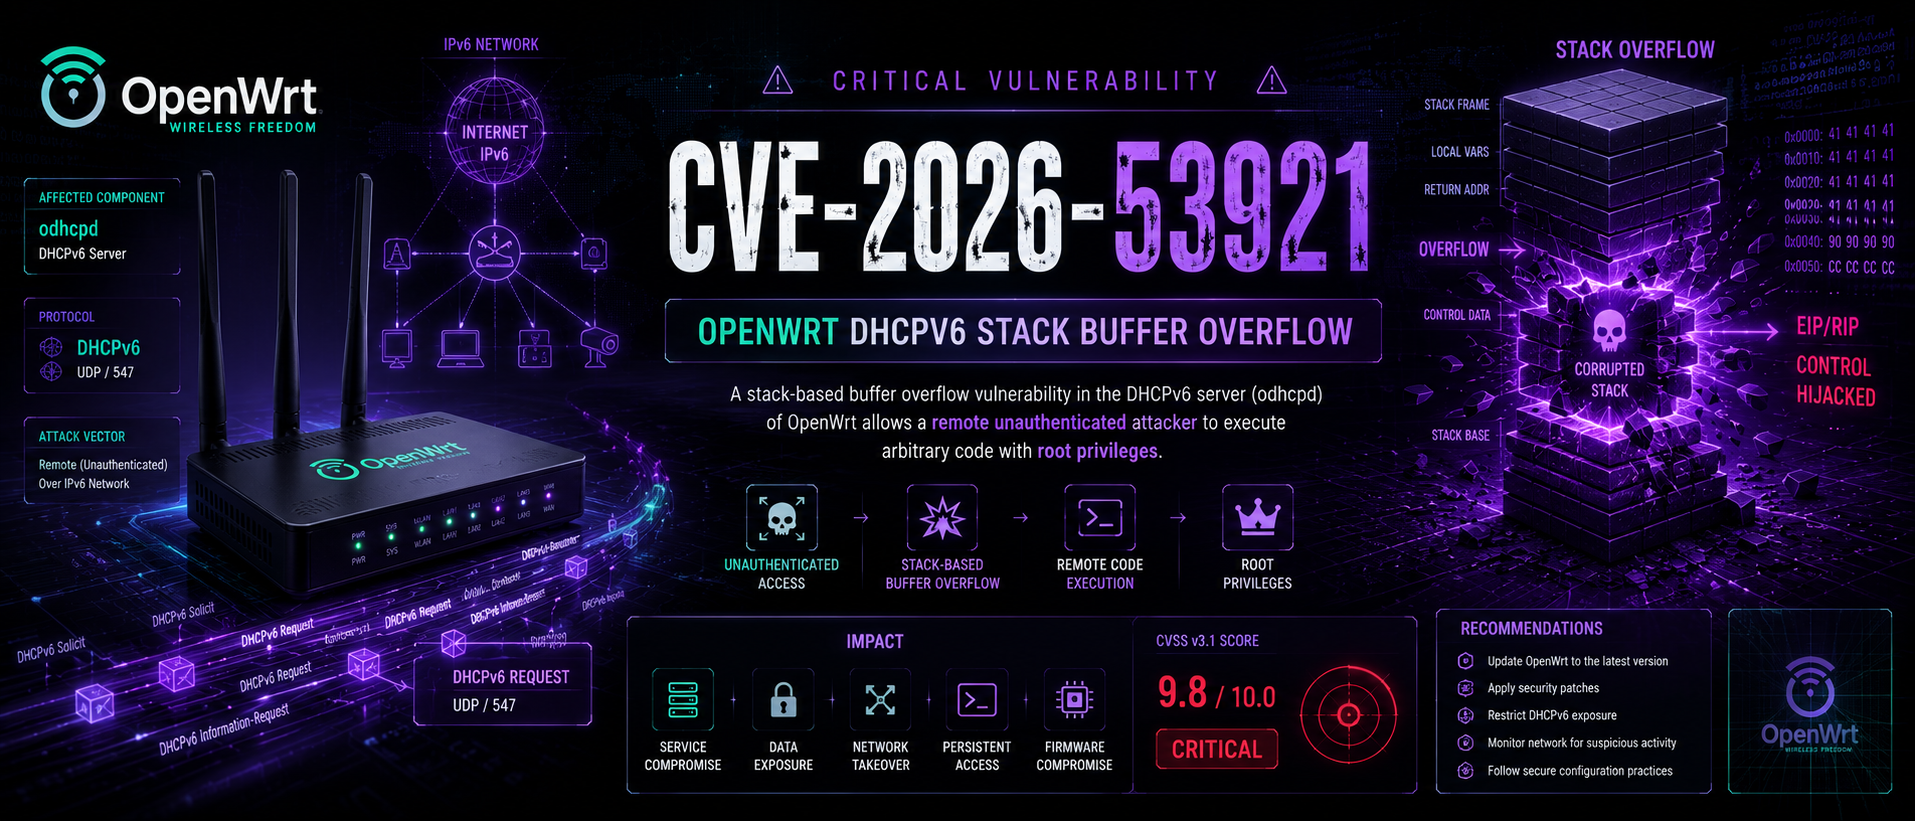 tc4dy/cve-2026-53921-poc-exploit
CVE-2026-53921 – odhcpd Stack Overflow (CVSS 9.8) 🛡️ Vuln detailed and comprehensive Write-Up and Verifier & Multi-exploit for OpenWrt DHCPv6 RCE.…
 johnjohnsp1/cve-2014-4113
PowerShell-based exploit for CVE-2014-4113 targeting x64 Windows systems with remote payload download and execution.
 boydhacks/dameflare
Python 3 exploit for CVE-2019-3980. Unauthenticated RCE as SYSTEM via SolarWinds Dameware MRC smart card authentication bypass.
 stuub/cve-2025-3969-exploit
CVE-2025-3969: Exploit PoC (OS CMD injection, Web Shell, Interactive Shell)
 spiralbl0ck/bypass-payloadrestrictions.dll-wdeg-rop-mitigation-
C-based PoC to bypass Windows PayloadRestrictions.dll and wdeg ROP mitigation, enabling payload execution and binary exploitation for security…
 orangepirate/cve-2018-9948-9958-exp
a exp for cve-2018-9948/9958 , current shellcode called win-calc
 nudttan91/webmin-cve-2022-0824-enhanced-exploit
Python exploit for Webmin CVE-2022-0824 with dual-mode support: direct command execution and reverse shell. Features multiple payload types,…
 runik/harmonic
Suite for reverse shell handling geared toward working within the native shell
 kal1gh0st/cve-2021-40444_cab_archives
Custom CAB template generator for CVE-2021-40444, crafting malicious cabinet archives to exploit Windows MSHTML remote code execution via crafted…
 tiagob0b/cve-2021-40444
Malicious DOCX generator exploiting CVE-2021-40444 (Microsoft Office Word RCE) with CAB-based DLL side-loading and CAB-less RAR/WSF attack chains for…
 carsonshaffer/cve-2020-7384
Bash exploit script for CVE-2020-7384, a remote code execution vulnerability in Apache NiFi, with improved usability and quality-of-life enhancements.
 damariion/cve-2015-8522.rce
Exploit for CVE-2015-8522 targeting Tivoli FastBack Server with stack-based buffer overflow, ASLR/DEP bypass, and automated reverse-shell…
 bishopfox/sliver
Adversary Emulation Framework