CVE-2025-3969-Exploit
 stuub/cve-2025-3969-exploit
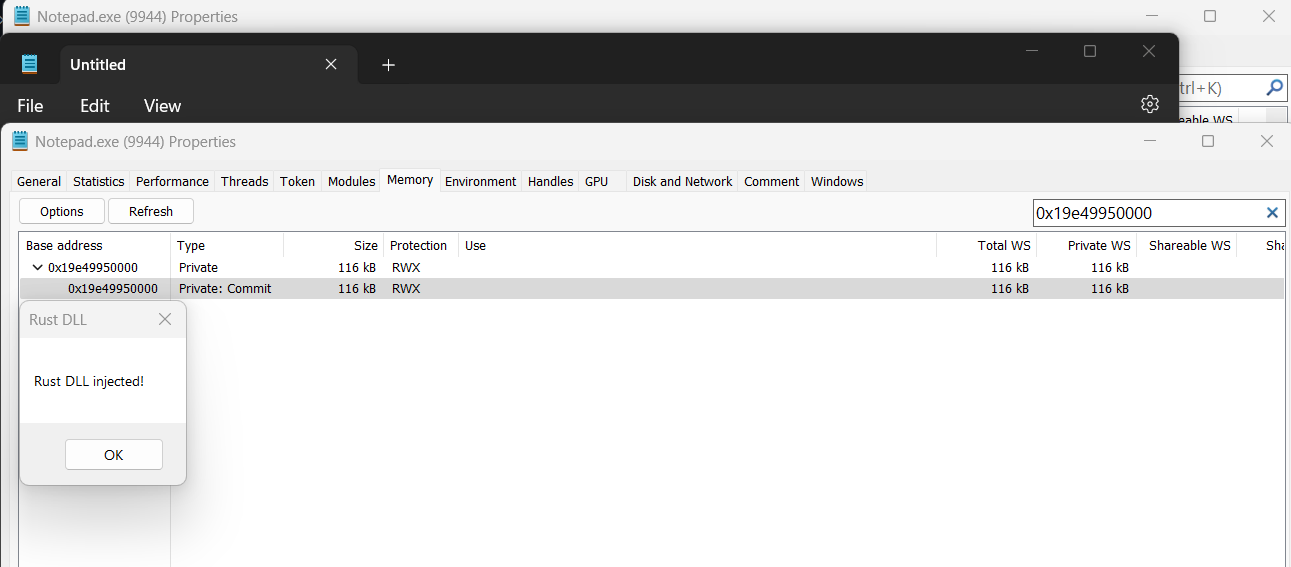
CVE-2025-3969: Exploit PoC (OS CMD injection, Web Shell, Interactive Shell)
command-and-controlexploitationpayload-generation+3
2
stuub/cve-2025-3969-exploitCVE-2025-3969: Exploit PoC (OS CMD injection, Web Shell, Interactive Shell)
 y0naldez/cve-2024-28397-js2py-rce
Generates JavaScript payloads to exploit CVE-2024-28397 Js2Py sandbox escape, enabling remote command execution and reverse shells via Python…
 nudttan91/webmin-cve-2022-0824-enhanced-exploit
Python exploit for Webmin CVE-2022-0824 with dual-mode support: direct command execution and reverse shell. Features multiple payload types,…
 runik/harmonic
Suite for reverse shell handling geared toward working within the native shell
 zerx0r/kage
Kage is Graphical User Interface for Metasploit Meterpreter and Session Handler
 egebalci/egesploit
EGESPLOIT is a golang library for malware development
 veil-framework/veil
Veil 3.1.X (Check version info in Veil at runtime)
 veil-framework/veil-evasion
Veil Evasion is no longer supported, use Veil 3.0!
 octetsplicer/lazypariah
A tool for generating reverse shell payloads on the fly.
 getrektboy724/meterpwrshell
Automated Tool That Generates The Perfect Meterpreter Powershell Payload