
shellcodetester
 helviojunior/shellcodetester
An application to test windows and linux shellcodes
binary-analysisexploitationpayload-development+2
helviojunior/shellcodetesterAn application to test windows and linux shellcodes
 techryptic/pokemon-shellcode-loader
Tired of looking at hex all day and popping '\x41's? Rather look at Lugia/Charmander? I have the solution for you.
 umpolungfish/byvalver
takes shellcode bad-bytes and banishes them, returning cleaned shellcode with preserved functionalities
 bishopfox/cve-2021-35211
Python exploit for Serv-U SSH vulnerability (CVE-2021-35211) with multiple payload modes: stage, exec, and download-execute, enabling shellcode…
 kira2040k/avbypass
golang script for bypass AV and work only in windows platform
 voidsecsoftwares/voidsec-proxy
Multi-module offensive security toolkit for SOCKS5 proxy chaining, port scanning, DNS enumeration, hash cracking, reverse shell generation,…
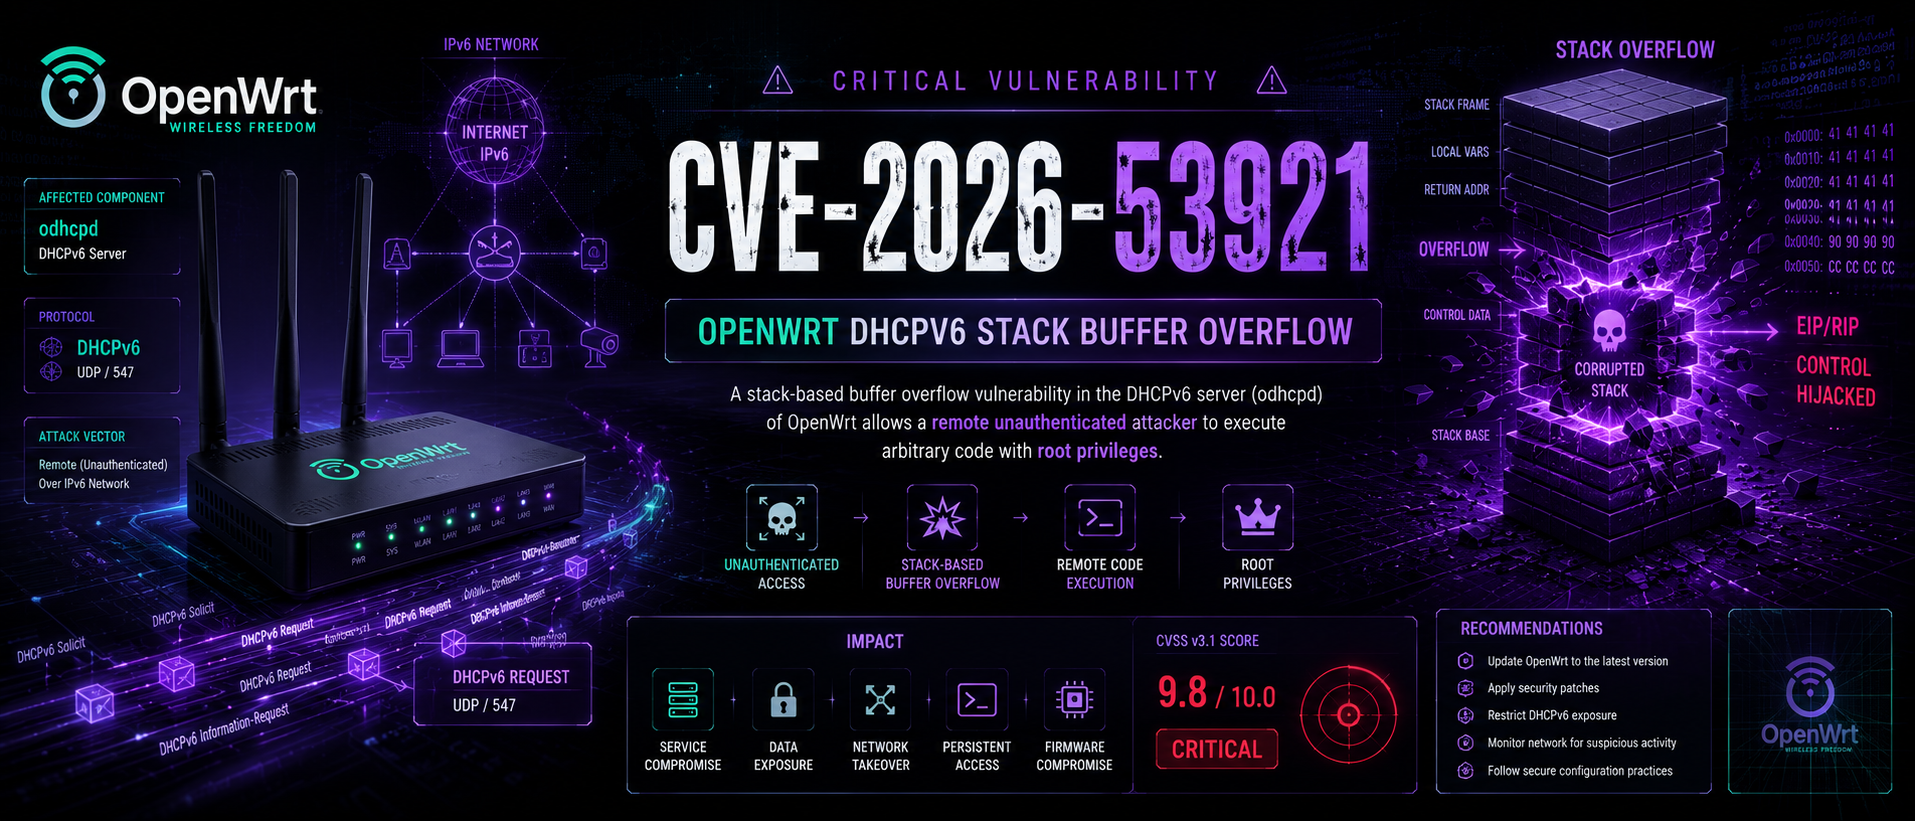 tc4dy/cve-2026-53921-poc-exploit
CVE-2026-53921 – odhcpd Stack Overflow (CVSS 9.8) 🛡️ Vuln detailed and comprehensive Write-Up and Verifier & Multi-exploit for OpenWrt DHCPv6 RCE.…
 johnjohnsp1/cve-2014-4113
PowerShell-based exploit for CVE-2014-4113 targeting x64 Windows systems with remote payload download and execution.
 cerberusmrxi/krayincrm-rce-exploit-cve-2026-38526
CVE-2026-38526 exploit for Krayin CRM v2.2.x - Authenticated RCE via TinyMCE file upload bypass. Features interactive shell, multi-type payloads,…
 y0naldez/cve-2024-28397-js2py-rce
Generates JavaScript payloads to exploit CVE-2024-28397 Js2Py sandbox escape, enabling remote command execution and reverse shells via Python…
 spiralbl0ck/bypass-payloadrestrictions.dll-wdeg-rop-mitigation-
C-based PoC to bypass Windows PayloadRestrictions.dll and wdeg ROP mitigation, enabling payload execution and binary exploitation for security…
 blueisbeautiful/cve-2018-19323
An exploitation framework for CVE-2018-19323 - GIGABYTE GDrv privilege escalation vulnerability with multi-architecture support and framework…
 nudttan91/webmin-cve-2022-0824-enhanced-exploit
Python exploit for Webmin CVE-2022-0824 with dual-mode support: direct command execution and reverse shell. Features multiple payload types,…
 tiagob0b/cve-2021-40444
Malicious DOCX generator exploiting CVE-2021-40444 (Microsoft Office Word RCE) with CAB-based DLL side-loading and CAB-less RAR/WSF attack chains for…
 carsonshaffer/cve-2020-7384
Bash exploit script for CVE-2020-7384, a remote code execution vulnerability in Apache NiFi, with improved usability and quality-of-life enhancements.
 damariion/cve-2015-8522.rce
Exploit for CVE-2015-8522 targeting Tivoli FastBack Server with stack-based buffer overflow, ASLR/DEP bypass, and automated reverse-shell…
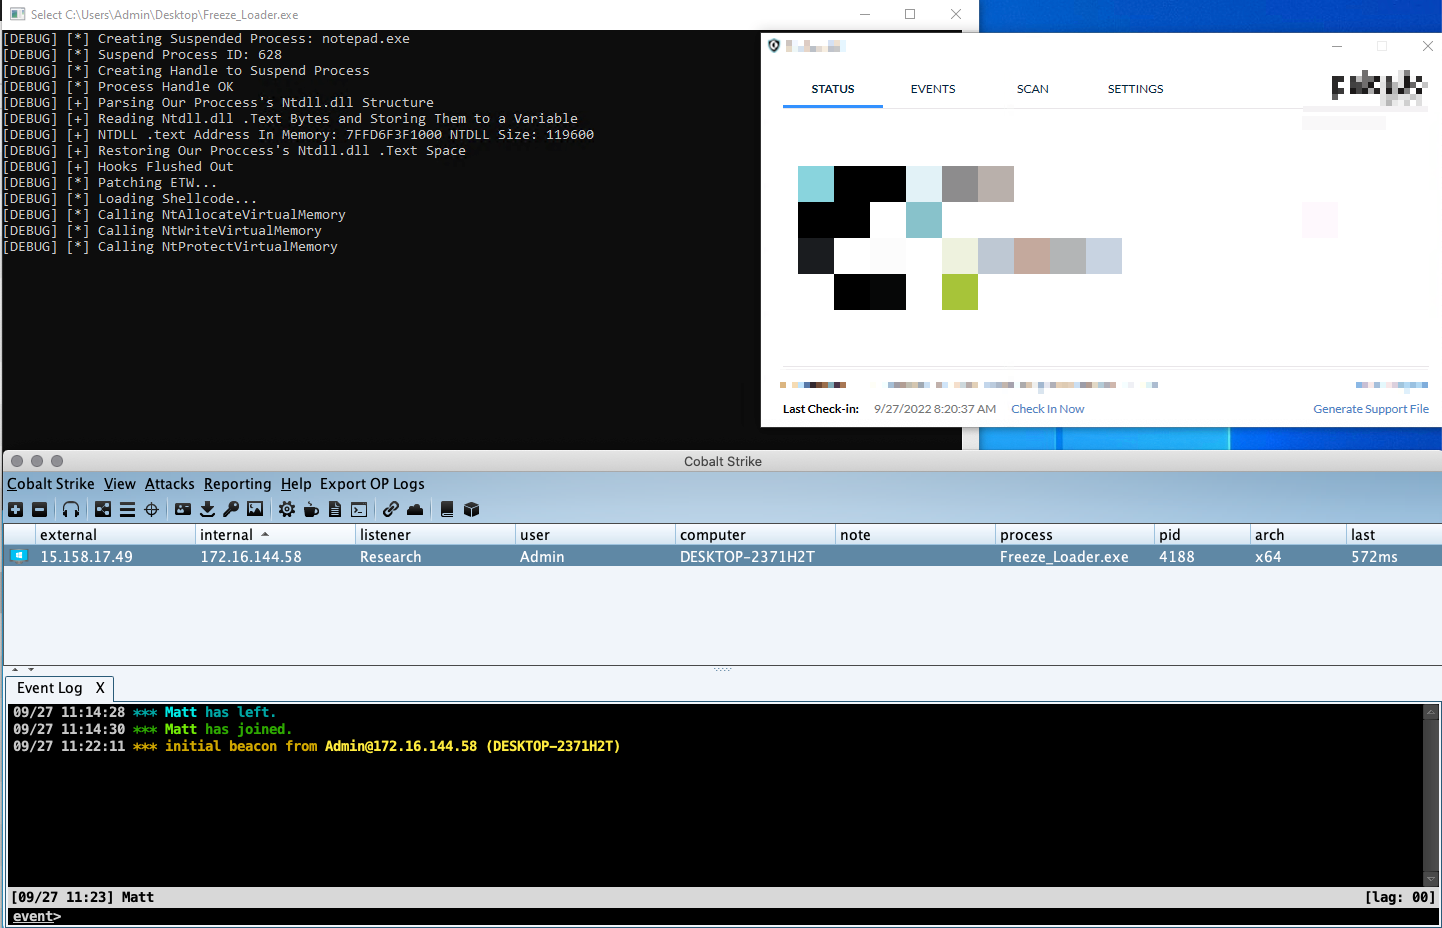 optiv/freeze
Freeze is a payload toolkit for bypassing EDRs using suspended processes, direct syscalls, and alternative execution methods
 zerx0r/kage
Kage is Graphical User Interface for Metasploit Meterpreter and Session Handler