
Archived
EGESPLOIT
 egebalci/egesploit
EGESPLOIT is a golang library for malware development
command-and-controlinformation-gatheringmalware-analysis+5
339
 optiv/freeze
Freeze is a payload toolkit for bypassing EDRs using suspended processes, direct syscalls, and alternative execution methods
 bishopfox/sliver
Adversary Emulation Framework
 iamsopotatoe-coder/tinyload
Open source Windows x64 PE packer and crypter. Compresses and encrypts executables with a custom virtual machine into a self extracting stub.

 g13net/lockjaw
Modular Windows C2 framework with a Rust teamserver, Zig implant, indirect syscalls, AMSI bypass, reflective/PoolParty injection, in-memory BOF…
 darthton/blackbone
Windows memory hacking library
 bc-security/empire
Empire is a post-exploitation and adversary emulation framework that is used to aid Red Teams and Penetration Testers.
 nccgroup/winpayloads
Undetectable Windows Payload Generation
 rvn0xsy/cooolis-ms
Cooolis-ms是一个包含了Metasploit Payload Loader、Cobalt Strike External C2 Loader、Reflective DLL injection的代码执行工具,它的定位在于能够在静态查杀上规避一些我们将要执行且含有特征的代码,帮助红队人员更方便快…
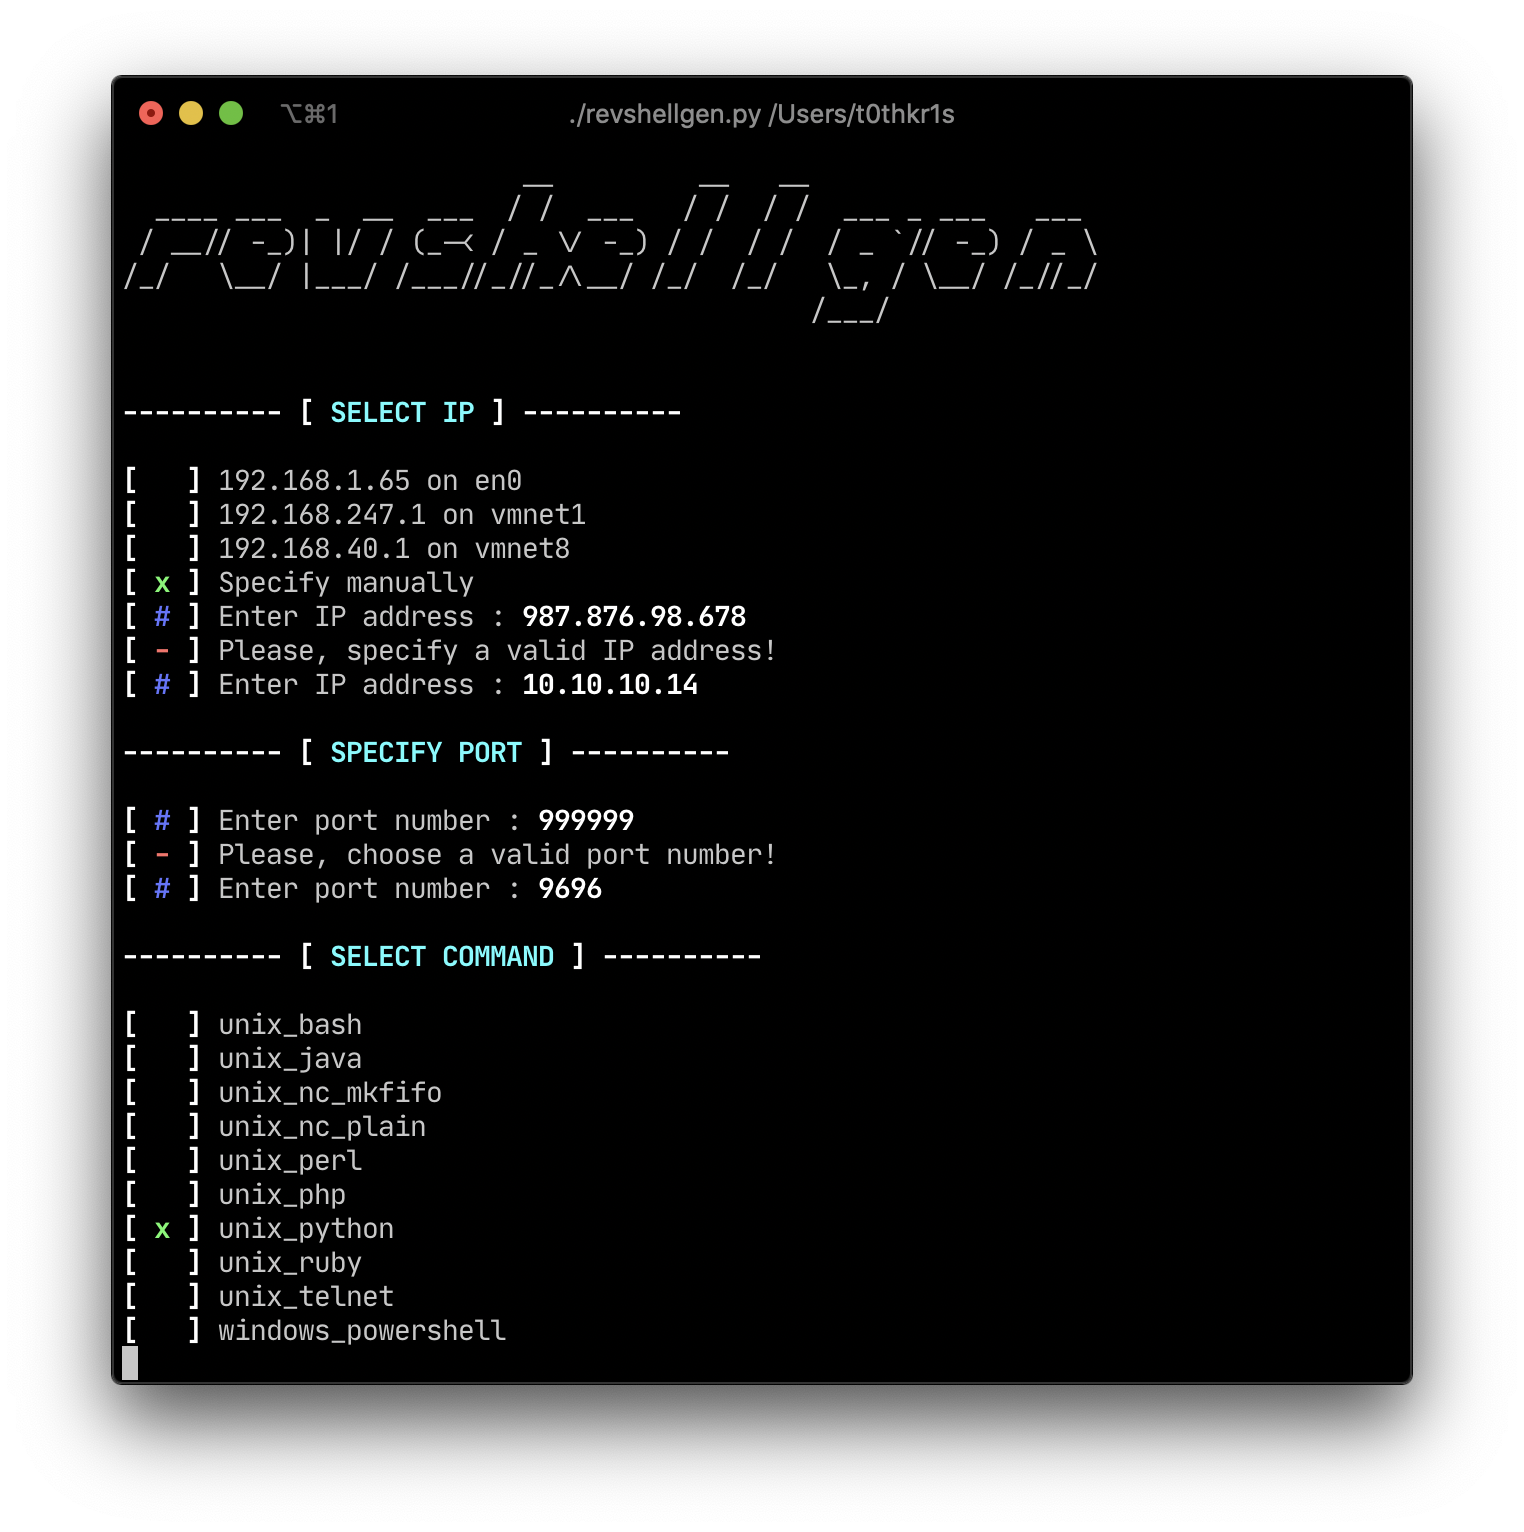 t0thkr1s/revshellgen
Reverse shell generator written in Python 3.
 n00py/hwacha
Deploy payloads to *Nix systems en masse
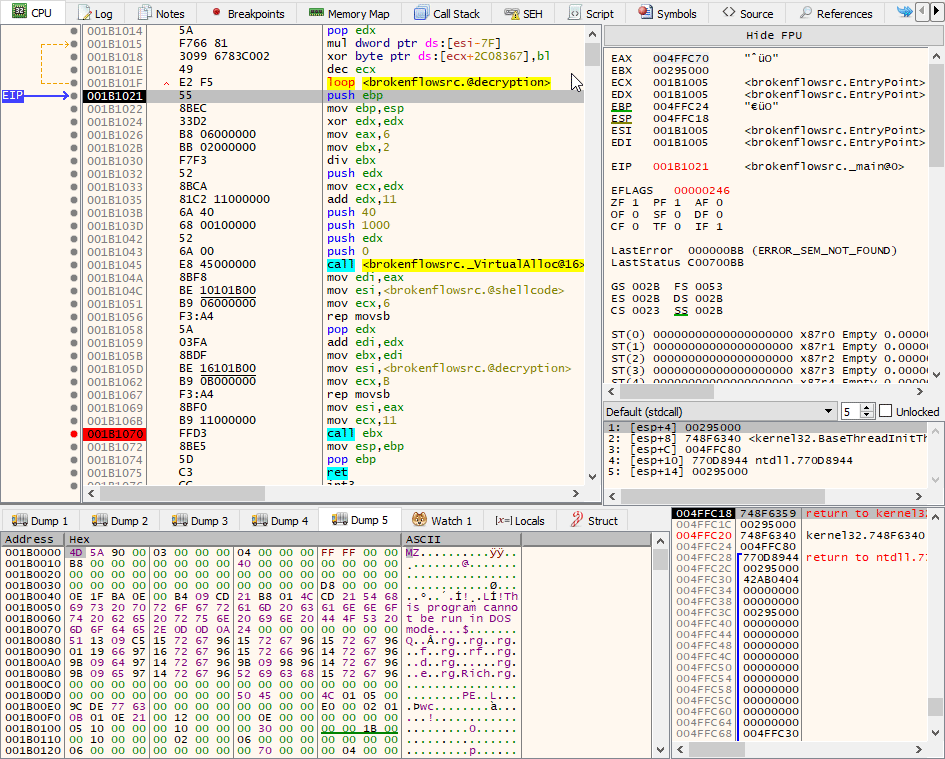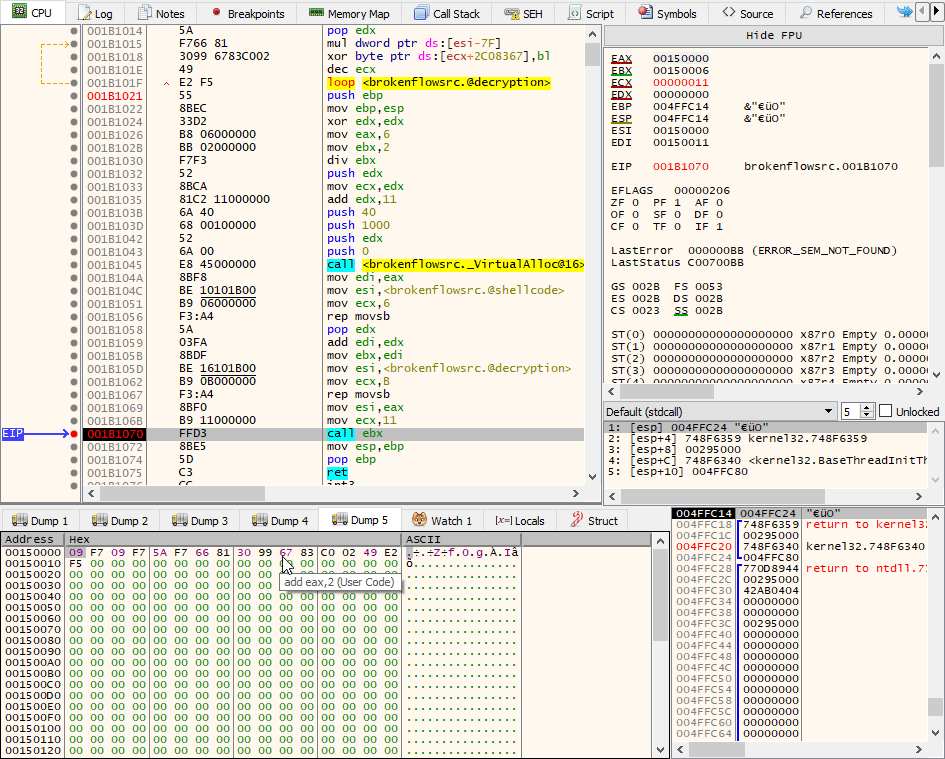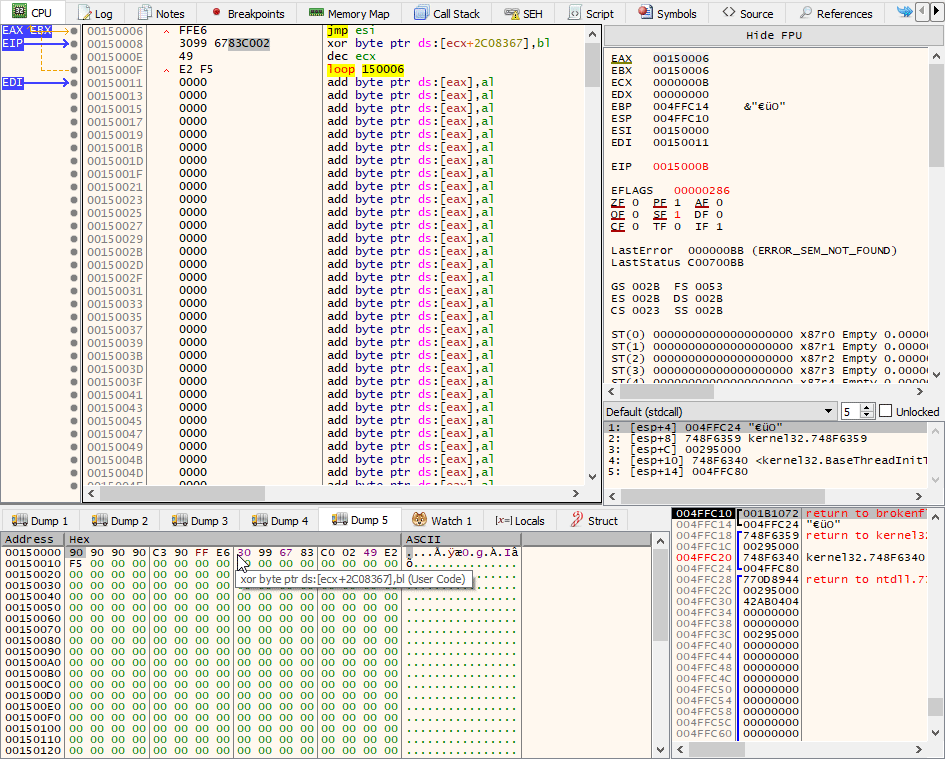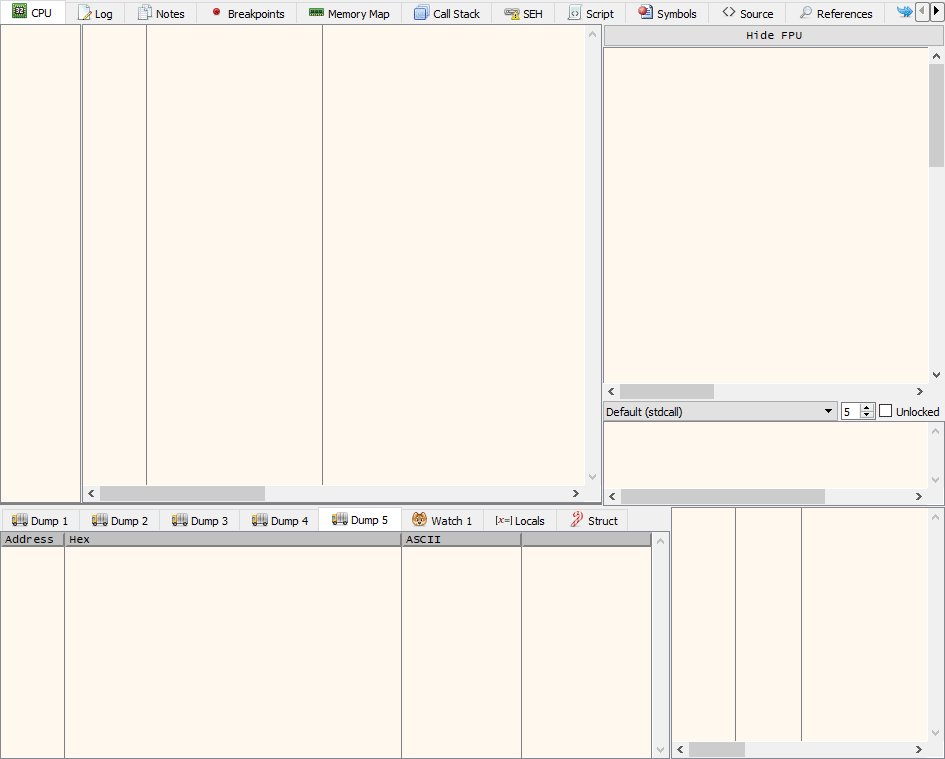 enkomio/brokenflow
A simple PoC to invoke an encrypted shellcode by using an hidden call
 praetorian-inc/wasmforge
WasmForge — compile Go and C# programs to single-binary, WASM-sandboxed native executables with polymorphic output.

 hackthem/openstamanager_rce_exploit-cve-2026-38751-
OpenSTAManager RCE Exploit (CVE-2026-38751)
 getrektboy724/meterpwrshell
Automated Tool That Generates The Perfect Meterpreter Powershell Payload
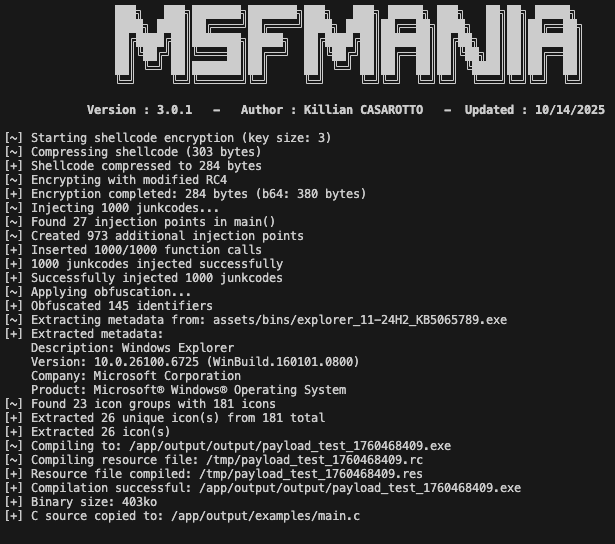 lepotekil/msfmania
Python AV Evasion Tools