powershell-backdoor-generator

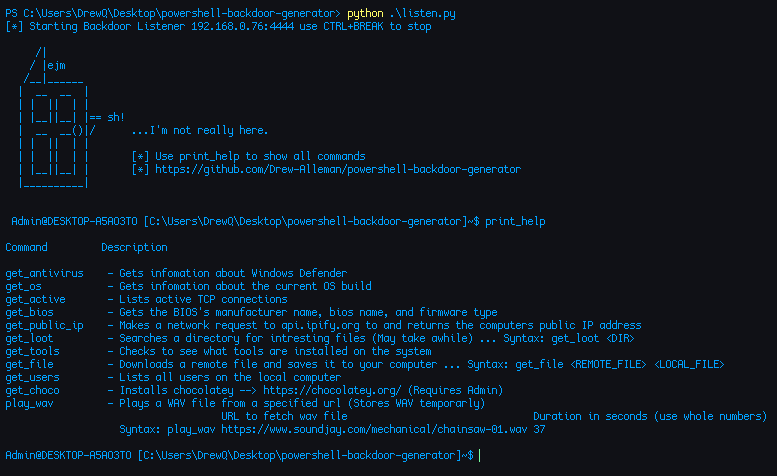
Reverse backdoor written in PowerShell and obfuscated with Python. It generates payloads for popular hacking devices like Flipper Zero and Hak5 USB…

Reverse backdoor written in PowerShell and obfuscated with Python. It generates payloads for popular hacking devices like Flipper Zero and Hak5 USB…

Patching ROP-encoded shellcodes into PEs

Deploy payloads to *Nix systems en masse

ASTROID v 1.2 bypass most A.V softwares


A wrapper for MSFvenom that allows for easy generation of payloads

CVE-2026-38526 exploit for Krayin CRM v2.2.x - Authenticated RCE via TinyMCE file upload bypass. Features interactive shell, multi-type payloads,…

Kage is Graphical User Interface for Metasploit Meterpreter and Session Handler

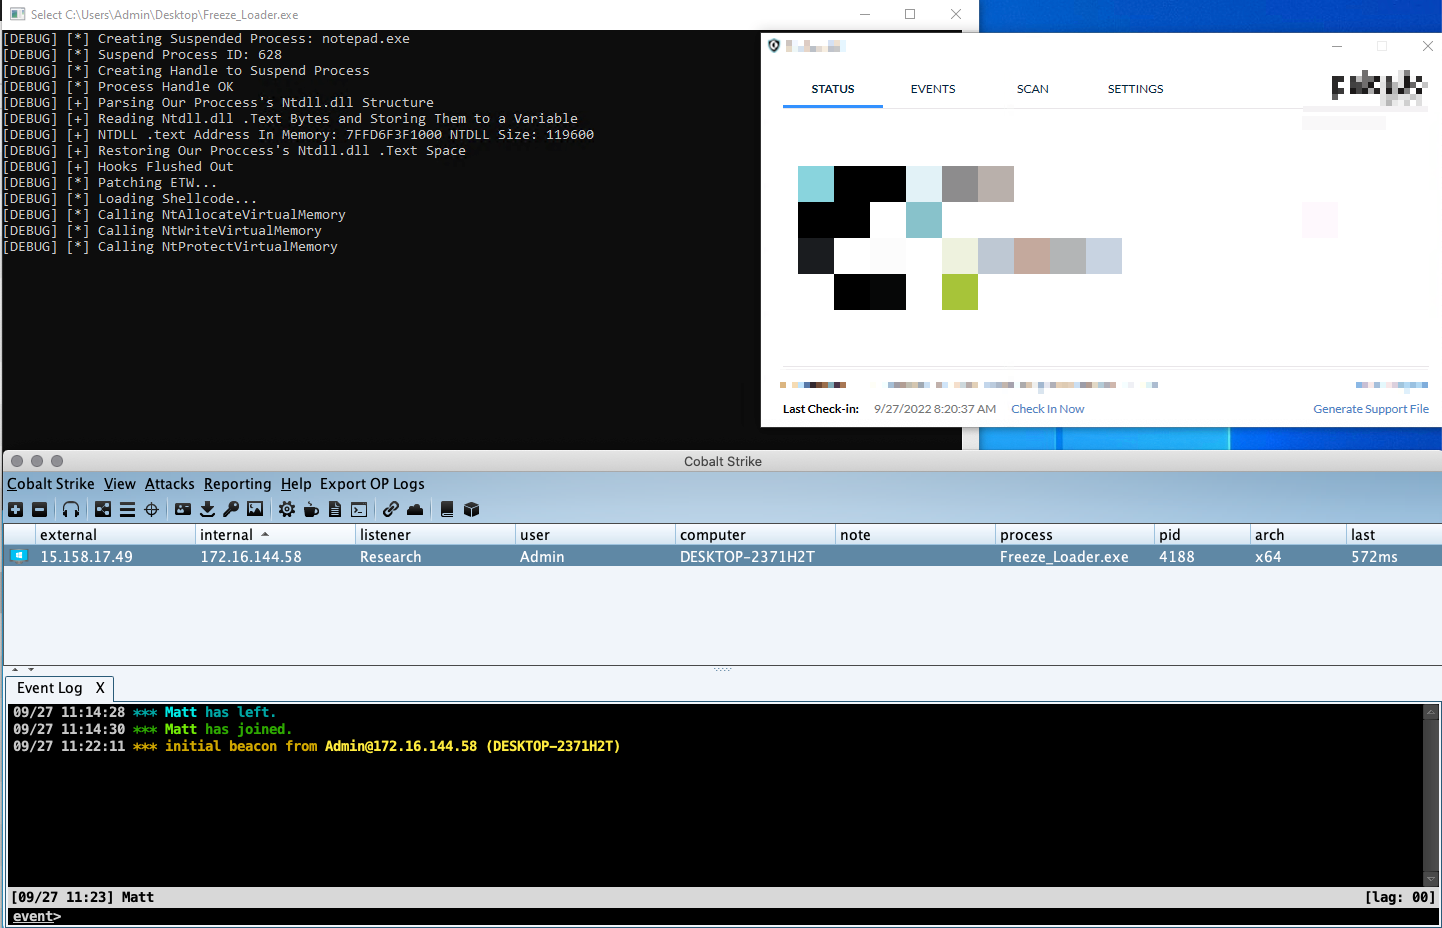
Freeze is a payload toolkit for bypassing EDRs using suspended processes, direct syscalls, and alternative execution methods

Veil 3.1.X (Check version info in Veil at runtime)

Veil Evasion is no longer supported, use Veil 3.0!

Multi-architecture assembler framework that converts assembly source into machine code for Arm, x86, MIPS, PowerPC, RISC-V, and more, with a…

.NET, PE, & Raw Shellcode Packer/Loader Written in Nim

OWASP ZSC - Shellcode/Obfuscate Code Generator https://www.secologist.com/

C# Reflective loader for unmanaged binaries.

The program is designed to obfuscate the shellcode.

Open source Windows x64 PE packer and crypter. Compresses and encrypts executables with a custom virtual machine into a self extracting stub.

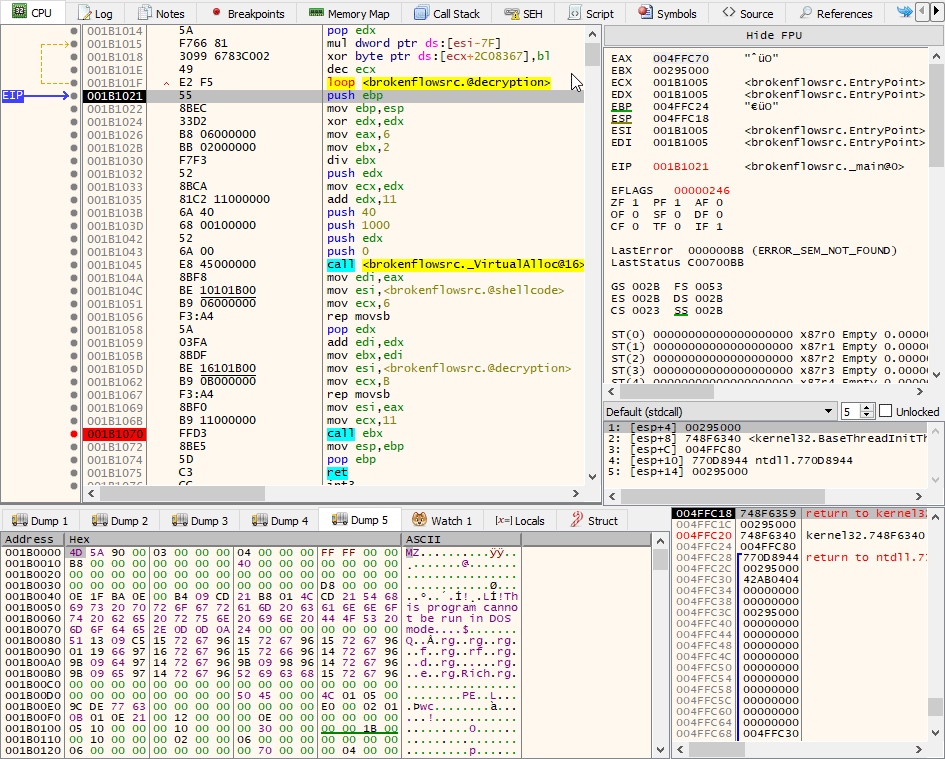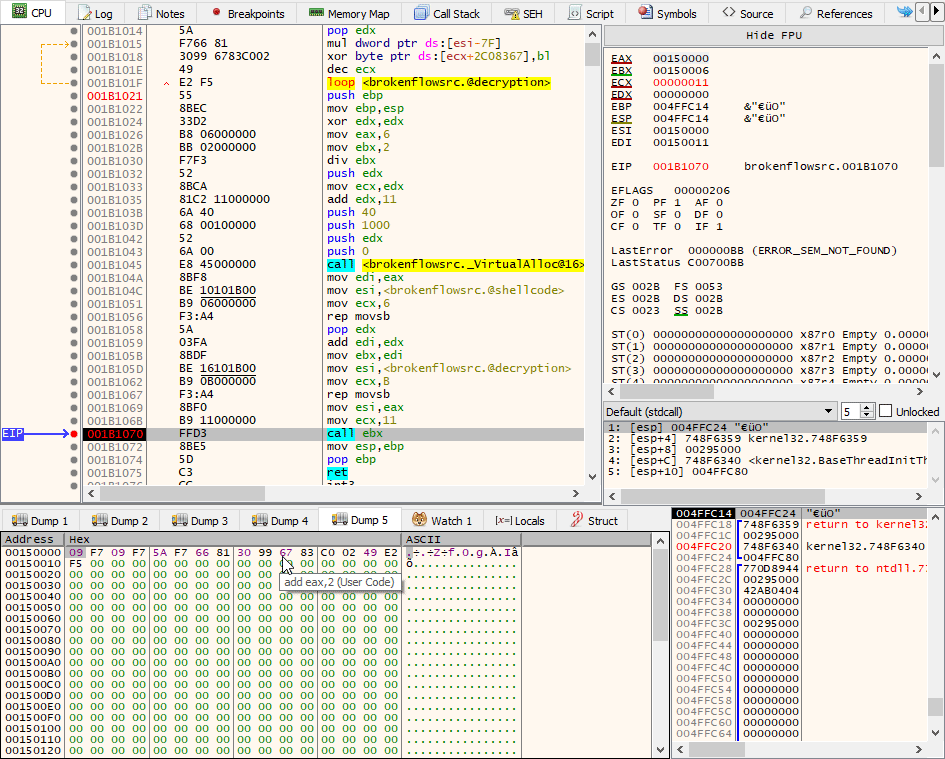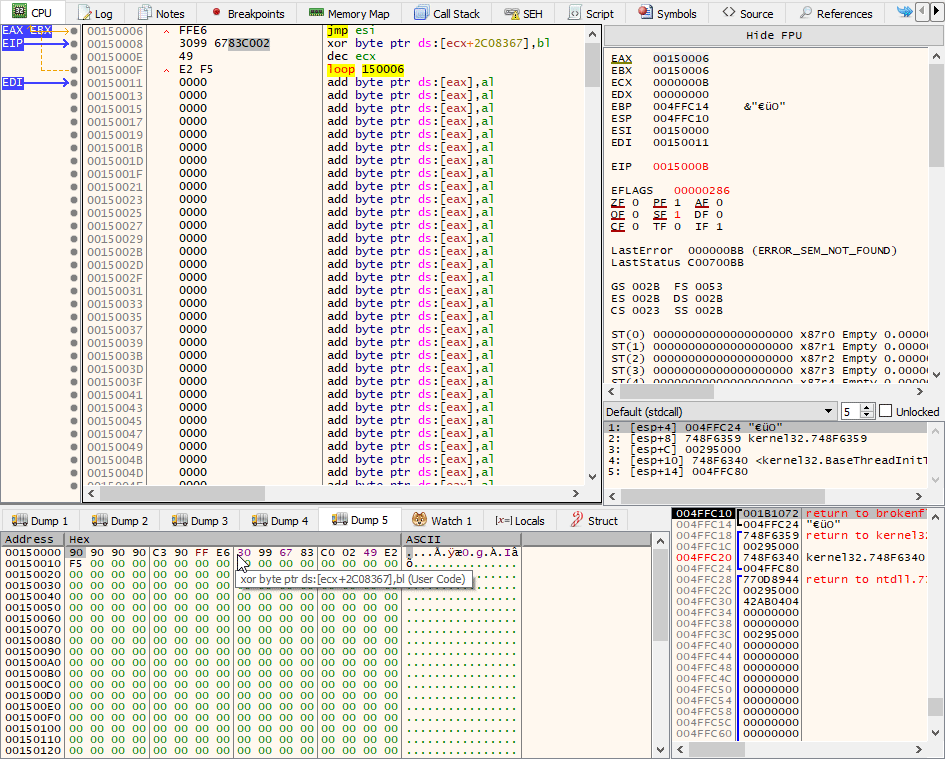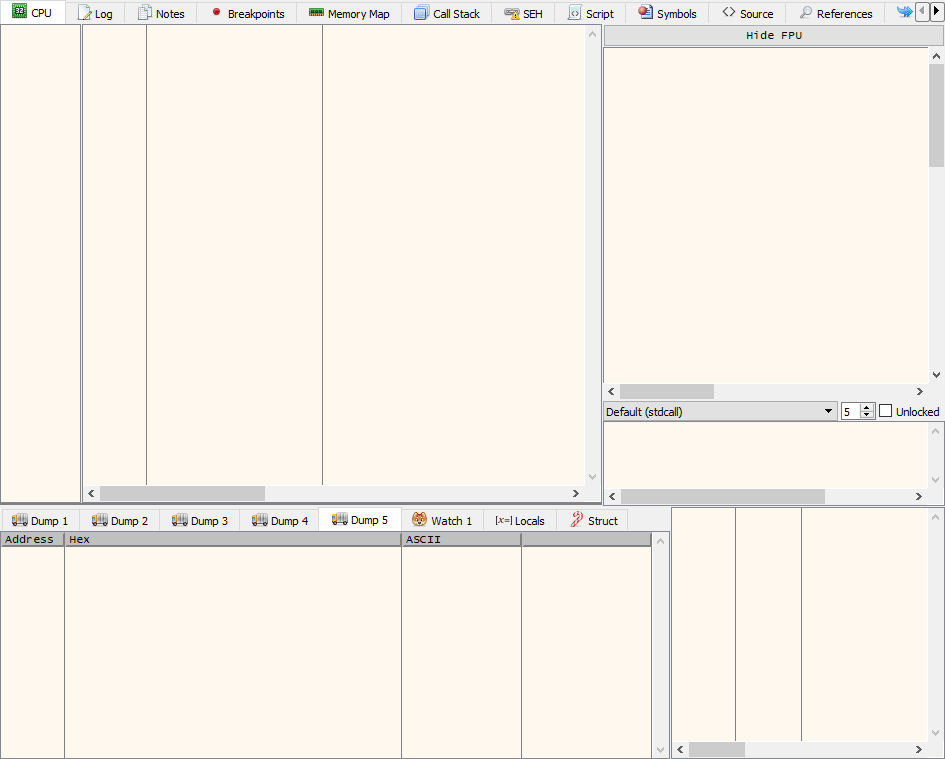
A simple PoC to invoke an encrypted shellcode by using an hidden call