
shellex
 therealdreg/shellex
C-shellcode to hex converter, handy tool for paste & execute shellcodes in IDA PRO, gdb, windbg, radare2, ollydbg, x64dbg, immunity debugger & 010…
binary-analysisdebuggersexploitation+5
113
therealdreg/shellexC-shellcode to hex converter, handy tool for paste & execute shellcodes in IDA PRO, gdb, windbg, radare2, ollydbg, x64dbg, immunity debugger & 010…
 oddcod3/phantom-evasion
Python antivirus evasion tool
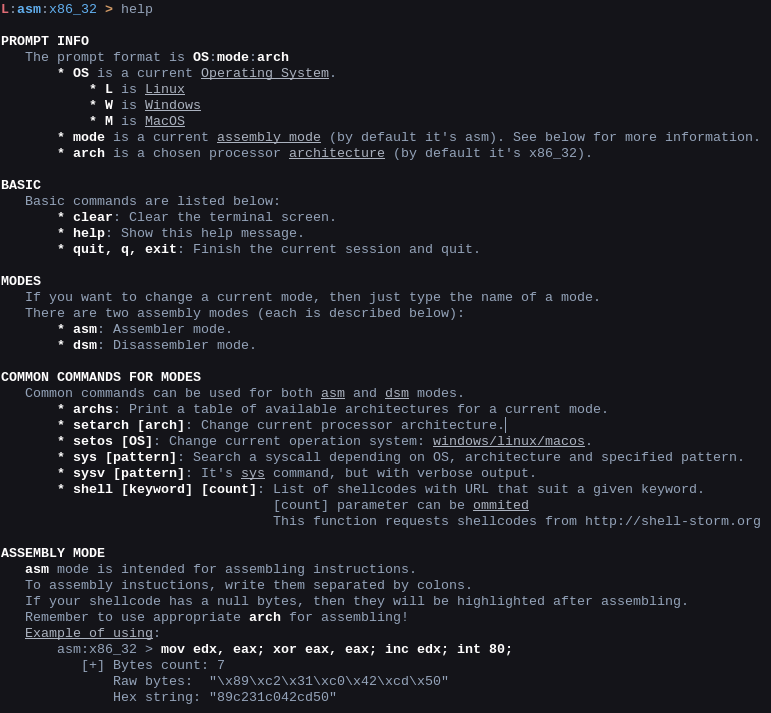 konatabrk/shellen
:cherry_blossom: Interactive shellcoding environment to easily craft shellcodes
 3xpl01tc0d3r/obfuscator
The program is designed to obfuscate the shellcode.
 ohjeongwook/shellcodeemulator
Shellcode emulator written with Unicorn Framework With Process Dump Emulation Environment
 paulsery/cve-2021-30632
m-y-mo: https://github.com/github/securitylab/tree/main/SecurityExploits/Chrome/v8/CVE-2021-30632
 nettitude/runpe
C# Reflective loader for unmanaged binaries.
 techryptic/pokemon-shellcode-loader
Tired of looking at hex all day and popping '\x41's? Rather look at Lugia/Charmander? I have the solution for you.
 dis0rder0x00/dbgnexum
Shellcode injection using the Windows Debugging API
 octetsplicer/lazypariah
A tool for generating reverse shell payloads on the fly.
 zerx0r/kage
Kage is Graphical User Interface for Metasploit Meterpreter and Session Handler
 0dayctf/reverse-shell-generator
Hosted Reverse Shell generator with a ton of functionality. -- (Great for CTFs)
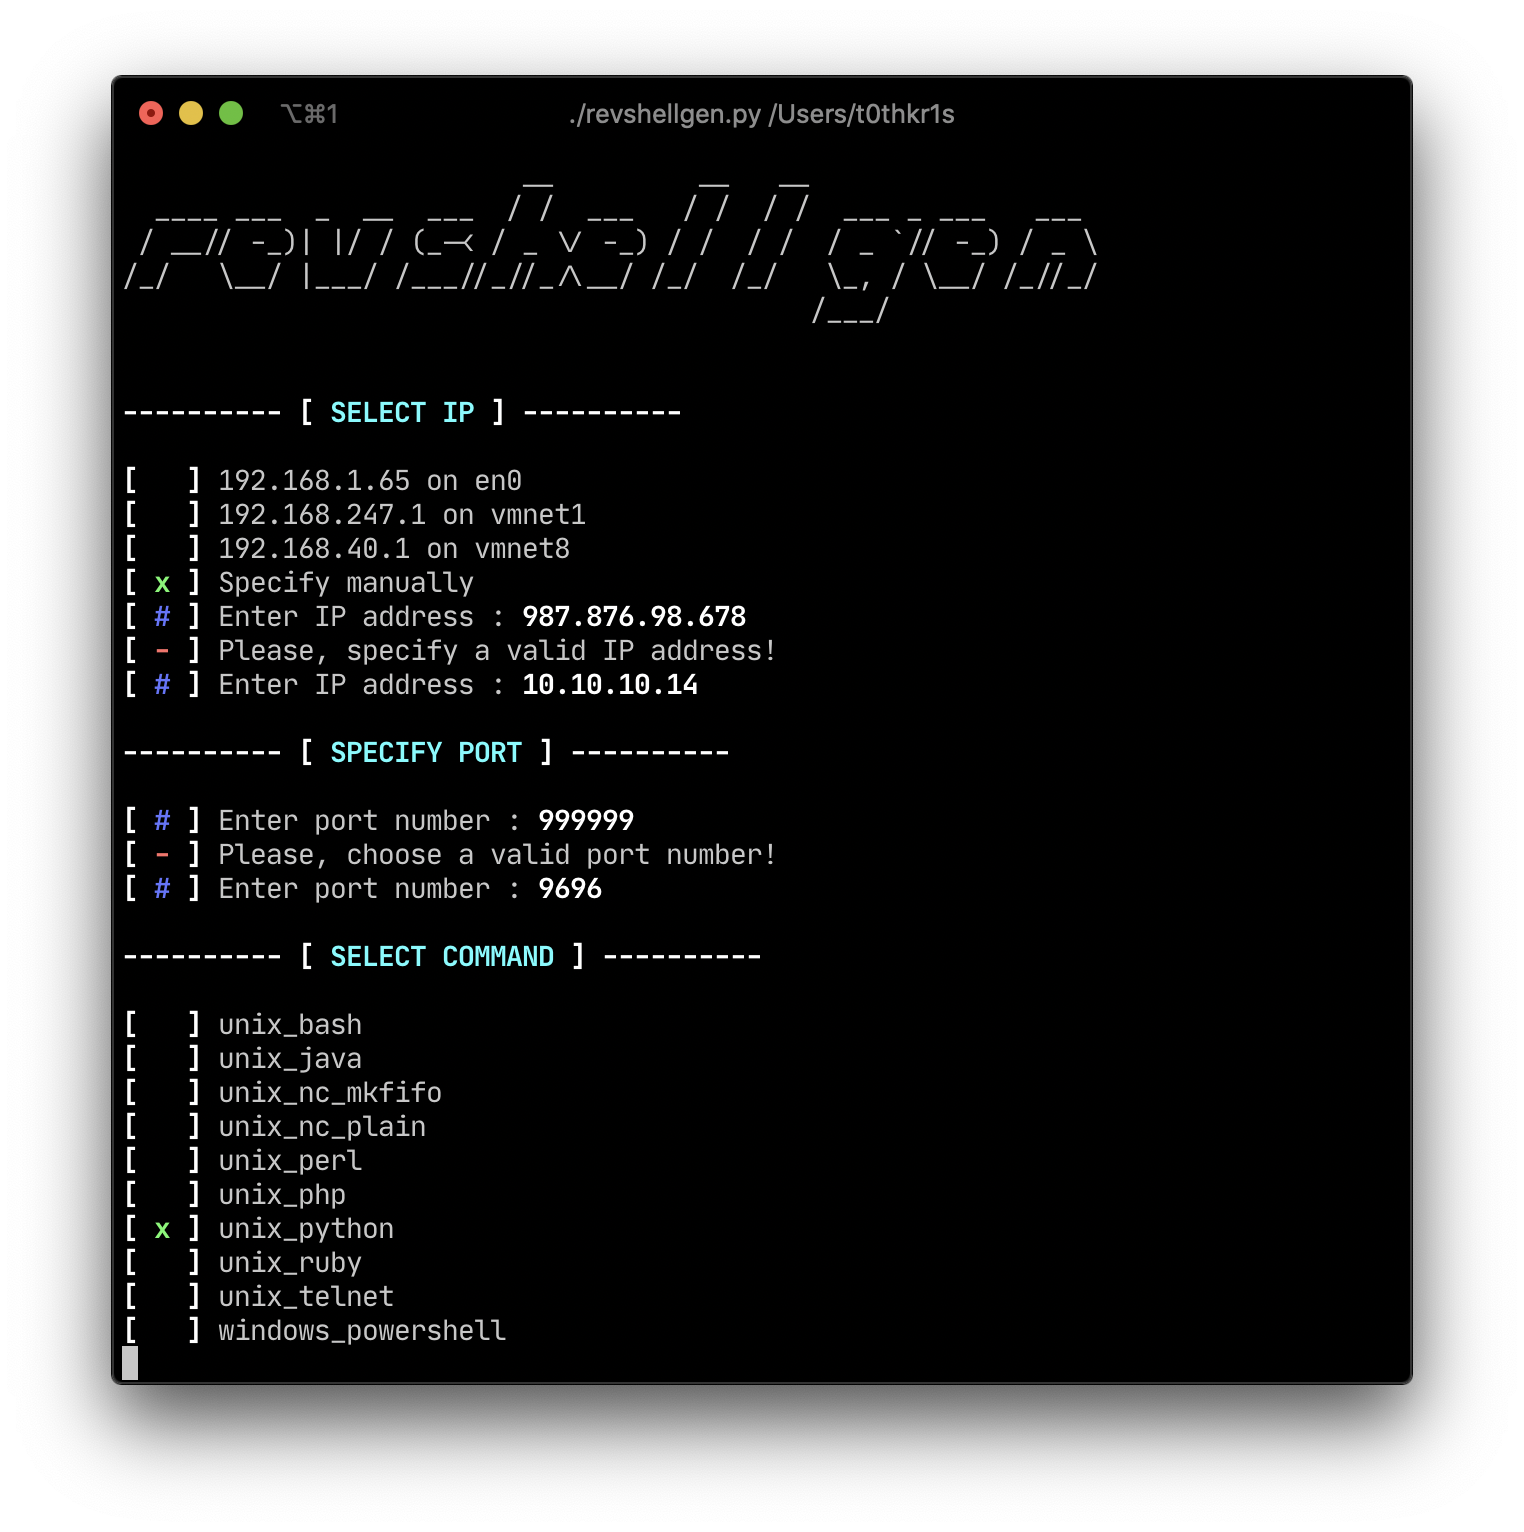 t0thkr1s/revshellgen
Reverse shell generator written in Python 3.
 sam00/poc-cve-2026-0300-exploit
Palo Alto - CVE-2026-0300 exploit
 orangepirate/cve-2018-9948-9958-exp
a exp for cve-2018-9948/9958 , current shellcode called win-calc
 rizinorg/rizin
UNIX-like reverse engineering framework and command-line toolset.
 ne0nd0g/merlin
Merlin is a cross-platform post-exploitation HTTP/2 Command & Control server and agent written in golang.
 tremwil/ds3-nrssr-rce
Documentation and proof of concept code for CVE-2022-24125 and CVE-2022-24126.