

Empire
 bc-security/empire
Empire is a post-exploitation and adversary emulation framework that is used to aid Red Teams and Penetration Testers.
adversarial-attackcommand-and-controldata-exfiltration+16
5.3k
bc-security/empireEmpire is a post-exploitation and adversary emulation framework that is used to aid Red Teams and Penetration Testers.
 nhas/reverse_ssh
SSH-based reverse shell management tool with native SCP/SFTP support, multiple transport protocols, Windows DLL generation, and fileless execution…

 watchtowrlabs/watchtowr-vs-citrix-netscaler-preauth-rce-cve-2026-8452
CVE-2026-8452 PreAuth RCE
 winterknife/silverpick
Windows User-Mode Shellcode Development Framework (WUMSDF)
 chaelsoo/hollow
A shellcode loader generator with support for multiple injection techniques, built for red team engagements.
 kasturixbm5/staged-dll-injection-smb-
Staged DLL injection proof-of-concept built in C using Win32 APIs — developed in an isolated lab environment for red team certification study (CRTO).
 seanheelan/anamnesis-release
Evaluation framework for studying LLM agents that automatically generate working exploits from vulnerability reports, bypassing modern security…
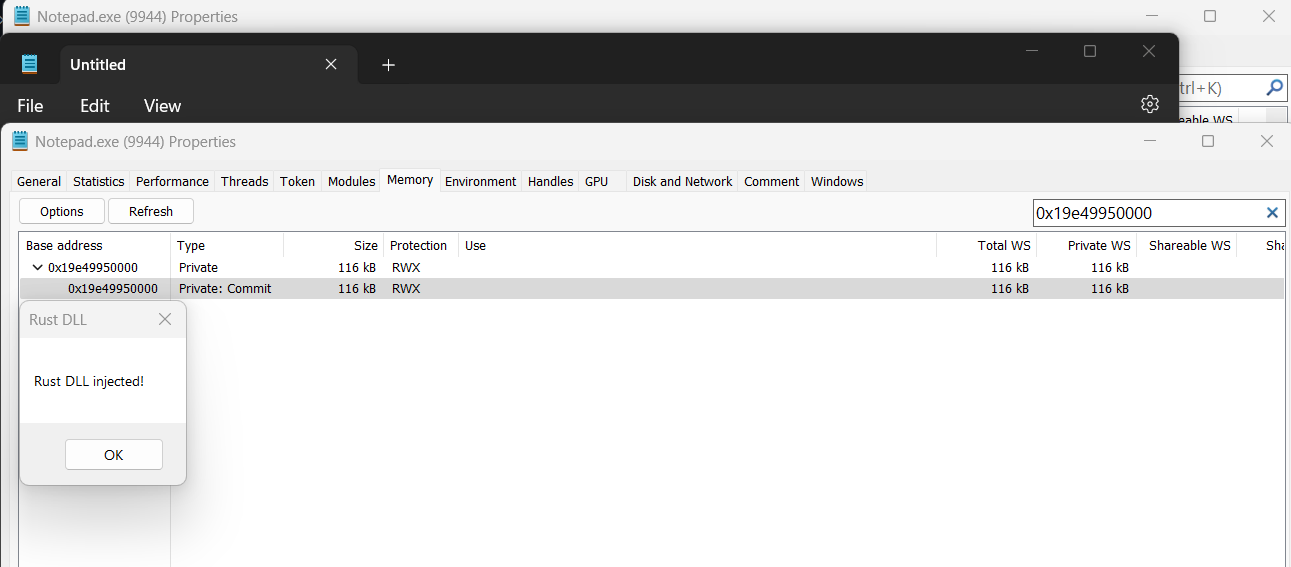 memn0ps/venom-rs
Rusty Injection - Shellcode Reflective DLL Injection (sRDI) in Rust (Codename: Venom)
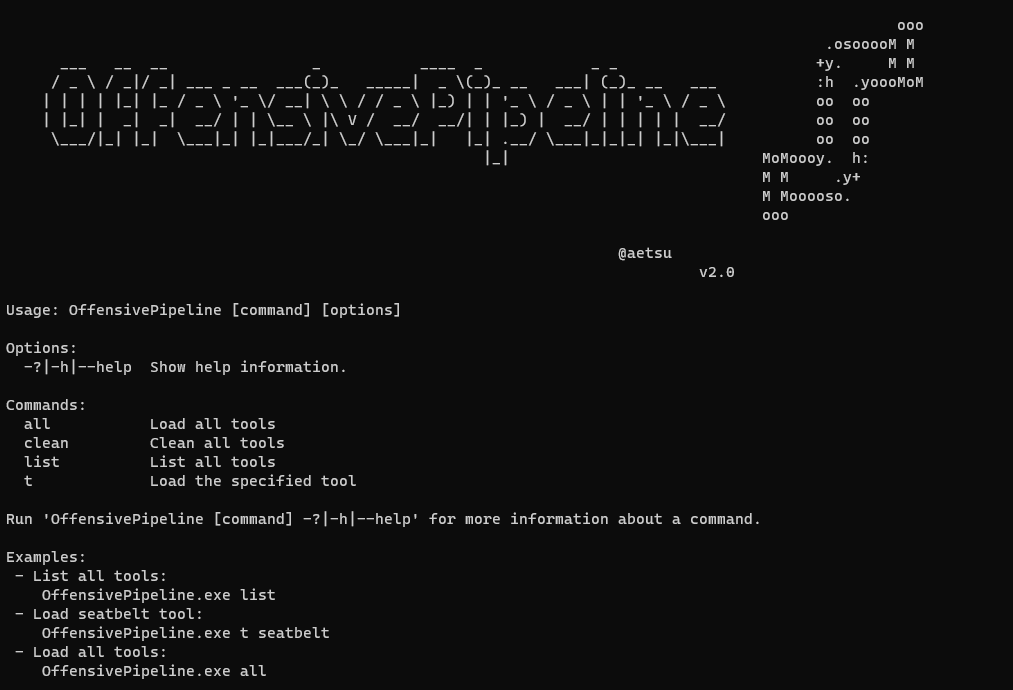 aetsu/offensivepipeline
OfensivePipeline allows you to download and build C# tools, applying certain modifications in order to improve their evasion for Red Team exercises.
 machine1337/fudshell
An efficent Script To Generate FUD Persistent Reverse Shell For Red Teaming. Don't Upload Generated Stub On Virustotal
 pwn1sher/frostbyte
Combines AppDomain Manager injection with shellcode embedding in signed binaries to evade EDR/AV detection for red team payloads.