
ThreadlessInject
 ccob/threadlessinject
Threadless Process Injection using remote function hooking.
adversarial-attackpayload-developmentpayload-generation+4
824
ccob/threadlessinjectThreadless Process Injection using remote function hooking.
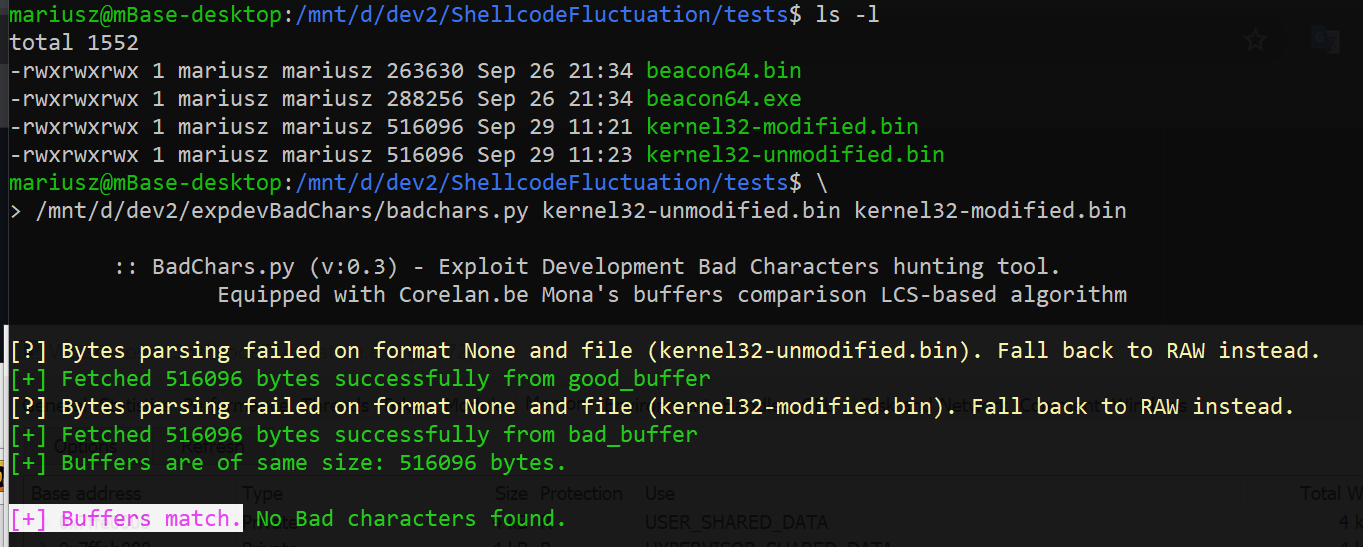 mgeeky/shellcodefluctuation
An advanced in-memory evasion technique fluctuating shellcode's memory protection between RW/NoAccess & RX and then encrypting/decrypting its contents
 techryptic/pokemon-shellcode-loader
Tired of looking at hex all day and popping '\x41's? Rather look at Lugia/Charmander? I have the solution for you.
 deepinstinct/dirty-vanity
A POC for the new injection technique, abusing windows fork API to evade EDRs. https://www.blackhat.com/eu-22/briefings/schedule/index.html#dirty-vani…

 touhidshaikh/bin2shell
bin2shell is very small utils for extract shell code from the binary file
 nccgroup/metasploitavevasion
Metasploit AV Evasion Tool
 hvictor/shellcode-x64
Shellcodes for Windows >= 11 x64
 hatriot/shellme
simple shellcode generator
 flangvik/sharpproxylogon
C# POC for CVE-2021-26855 aka ProxyLogon, supports the classically semi-interactive web shell as well as shellcode injection
 dis0rder0x00/dbgnexum
Shellcode injection using the Windows Debugging API
 sliverarmory/malasada
Linux Shared Library to Shellcode Loader
 0xrootpls/fritter
Polymorphic shellcode generator for in-memory execution of EXE, DLL, .NET, VBScript, and JScript with per-output and per-build randomization for…
 souhardya/zerodoor
A script written lazily for generating cross-platform backdoors on the go :)
 blacknbunny/mcreator
Encoded Reverse Shell Generator With Techniques To Bypass AV's
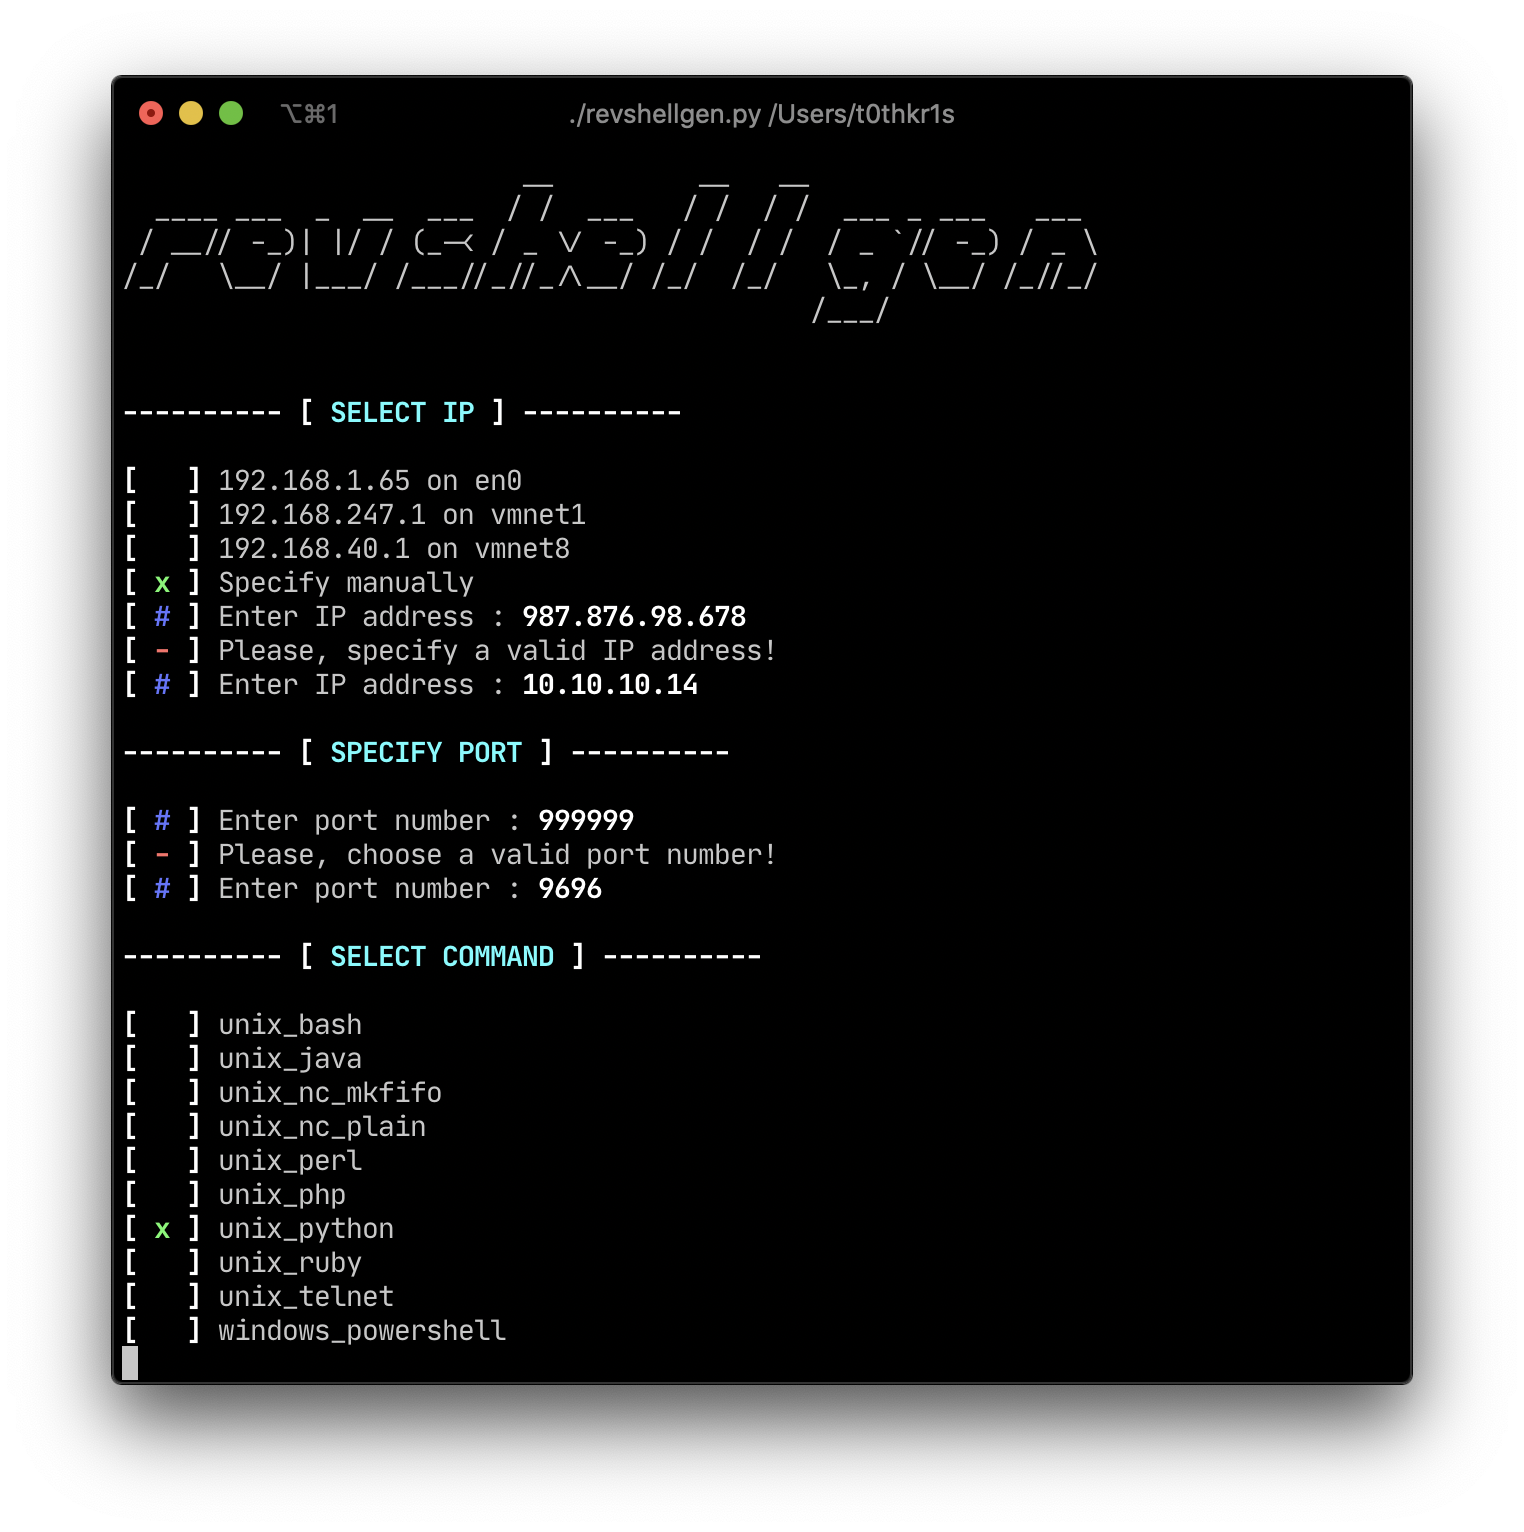 t0thkr1s/revshellgen
Reverse shell generator written in Python 3.
 kira2040k/avbypass
golang script for bypass AV and work only in windows platform
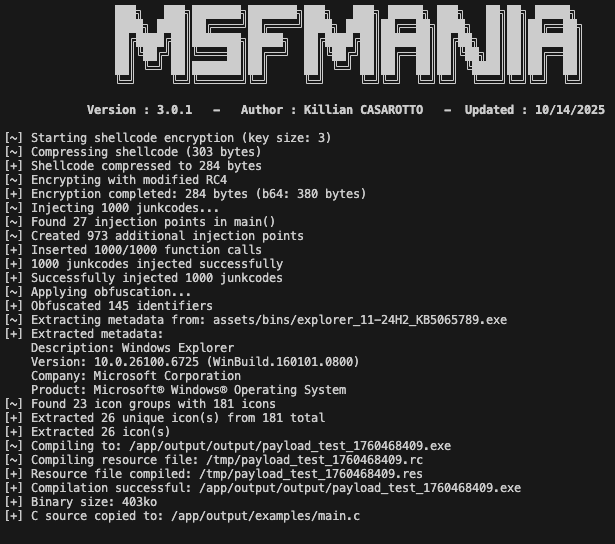 lepotekil/msfmania
Python AV Evasion Tools