

ThreadlessInject
 ccob/threadlessinject
Threadless Process Injection using remote function hooking.
adversarial-attackpayload-developmentpayload-generation+4
823
ccob/threadlessinjectThreadless Process Injection using remote function hooking.
 mgeeky/shellcodefluctuation
An advanced in-memory evasion technique fluctuating shellcode's memory protection between RW/NoAccess & RX and then encrypting/decrypting its contents
 rizinorg/rizin
UNIX-like reverse engineering framework and command-line toolset.
 keystone-engine/keystone
Multi-architecture assembler framework that converts assembly source into machine code for Arm, x86, MIPS, PowerPC, RISC-V, and more, with a…
 techryptic/pokemon-shellcode-loader
Tired of looking at hex all day and popping '\x41's? Rather look at Lugia/Charmander? I have the solution for you.
 cybereason/siofra
Simulates the Windows PE loader to identify DLL hijacking vulnerabilities, generates weaponized DLLs with shellcode payloads, and detects UAC…
 winterknife/silverpick
Windows User-Mode Shellcode Development Framework (WUMSDF)

 touhidshaikh/bin2shell
bin2shell is very small utils for extract shell code from the binary file
 vlad902/hacking-team-windows-kernel-lpe
Previously-0day exploit from the Hacking Team leak, written by Eugene Ching/Qavar.
 hvictor/shellcode-x64
Shellcodes for Windows >= 11 x64
 hatriot/shellme
simple shellcode generator
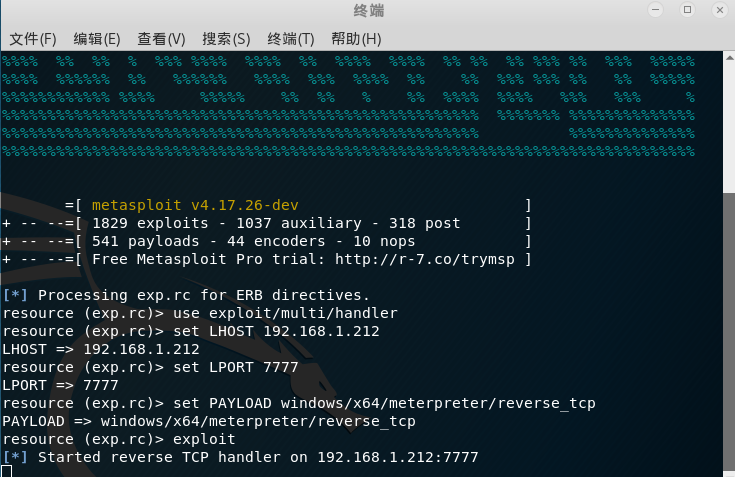 drac0nids/cve-2017-8570
## 在kali中自动化生成cve-2017-8570的恶意ppsx文件和配置msf监听
 yaldobaoth/cve-2015-1578-poc-metasploit
This is a proof-of-concept Metasploit module exploit for CVE-2015-1578, a buffer overflow vulnerability in Achat 0.150 beta7 on Windows. Exploitation…
 tremwil/ds3-nrssr-rce
Documentation and proof of concept code for CVE-2022-24125 and CVE-2022-24126.
 nudttan91/webmin-cve-2022-0824-enhanced-exploit
Python exploit for Webmin CVE-2022-0824 with dual-mode support: direct command execution and reverse shell. Features multiple payload types,…
 y0naldez/cve-2024-28397-js2py-rce
Generates JavaScript payloads to exploit CVE-2024-28397 Js2Py sandbox escape, enabling remote command execution and reverse shells via Python…
 mracumen/cve-2021-40444
Microsoft-Office-Word-MSHTML-Remote-Code-Execution-Exploit