

sliver
 bishopfox/sliver
Adversary Emulation Framework
adversarial-attackcommand-and-controldata-exfiltration+16
bishopfox/sliverAdversary Emulation Framework
 iamsopotatoe-coder/tinyload
Open source Windows x64 PE packer and crypter. Compresses and encrypts executables with a custom virtual machine into a self extracting stub.
 bc-security/empire
Empire is a post-exploitation and adversary emulation framework that is used to aid Red Teams and Penetration Testers.
 zznop/sploit
Go package that aids in binary analysis and exploitation
 chaelsoo/hollow
A shellcode loader generator with support for multiple injection techniques, built for red team engagements.
 monoxgas/srdi
Shellcode implementation of Reflective DLL Injection. Convert DLLs to position independent shellcode
 darthton/blackbone
Windows memory hacking library
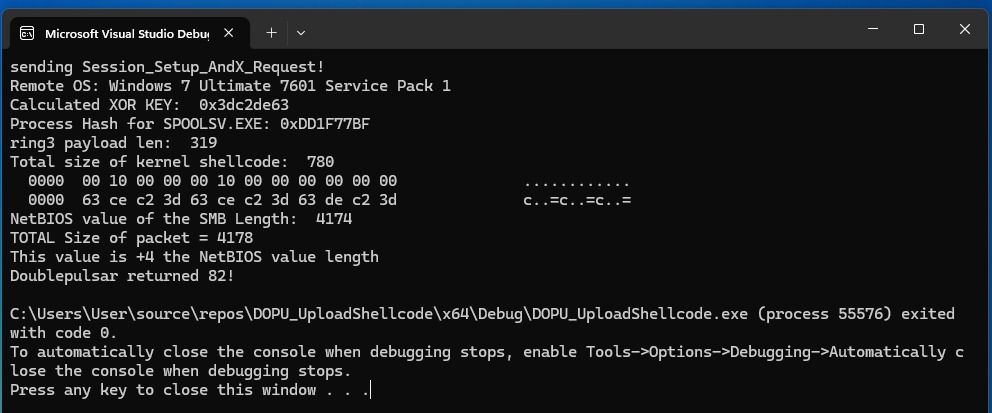 bhassani/eternalbluec
EternalBlue suite remade in C/C++ which includes: MS17-010 Exploit, EternalBlue vulnerability detector, DoublePulsar detector and DoublePulsar…
 rapid7/metasploit-framework
Open-source exploitation framework with modular payload, encoder, and auxiliary system for penetration testing, vulnerability validation, and…
 keystone-engine/keystone
Multi-architecture assembler framework that converts assembly source into machine code for Arm, x86, MIPS, PowerPC, RISC-V, and more, with a…
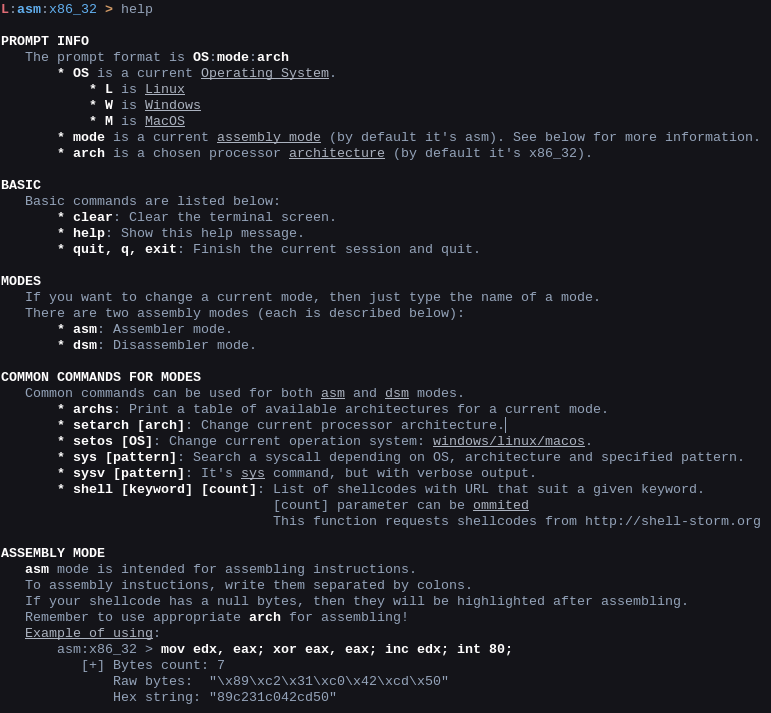 konatabrk/shellen
:cherry_blossom: Interactive shellcoding environment to easily craft shellcodes
 ohjeongwook/shellcodeemulator
Shellcode emulator written with Unicorn Framework With Process Dump Emulation Environment
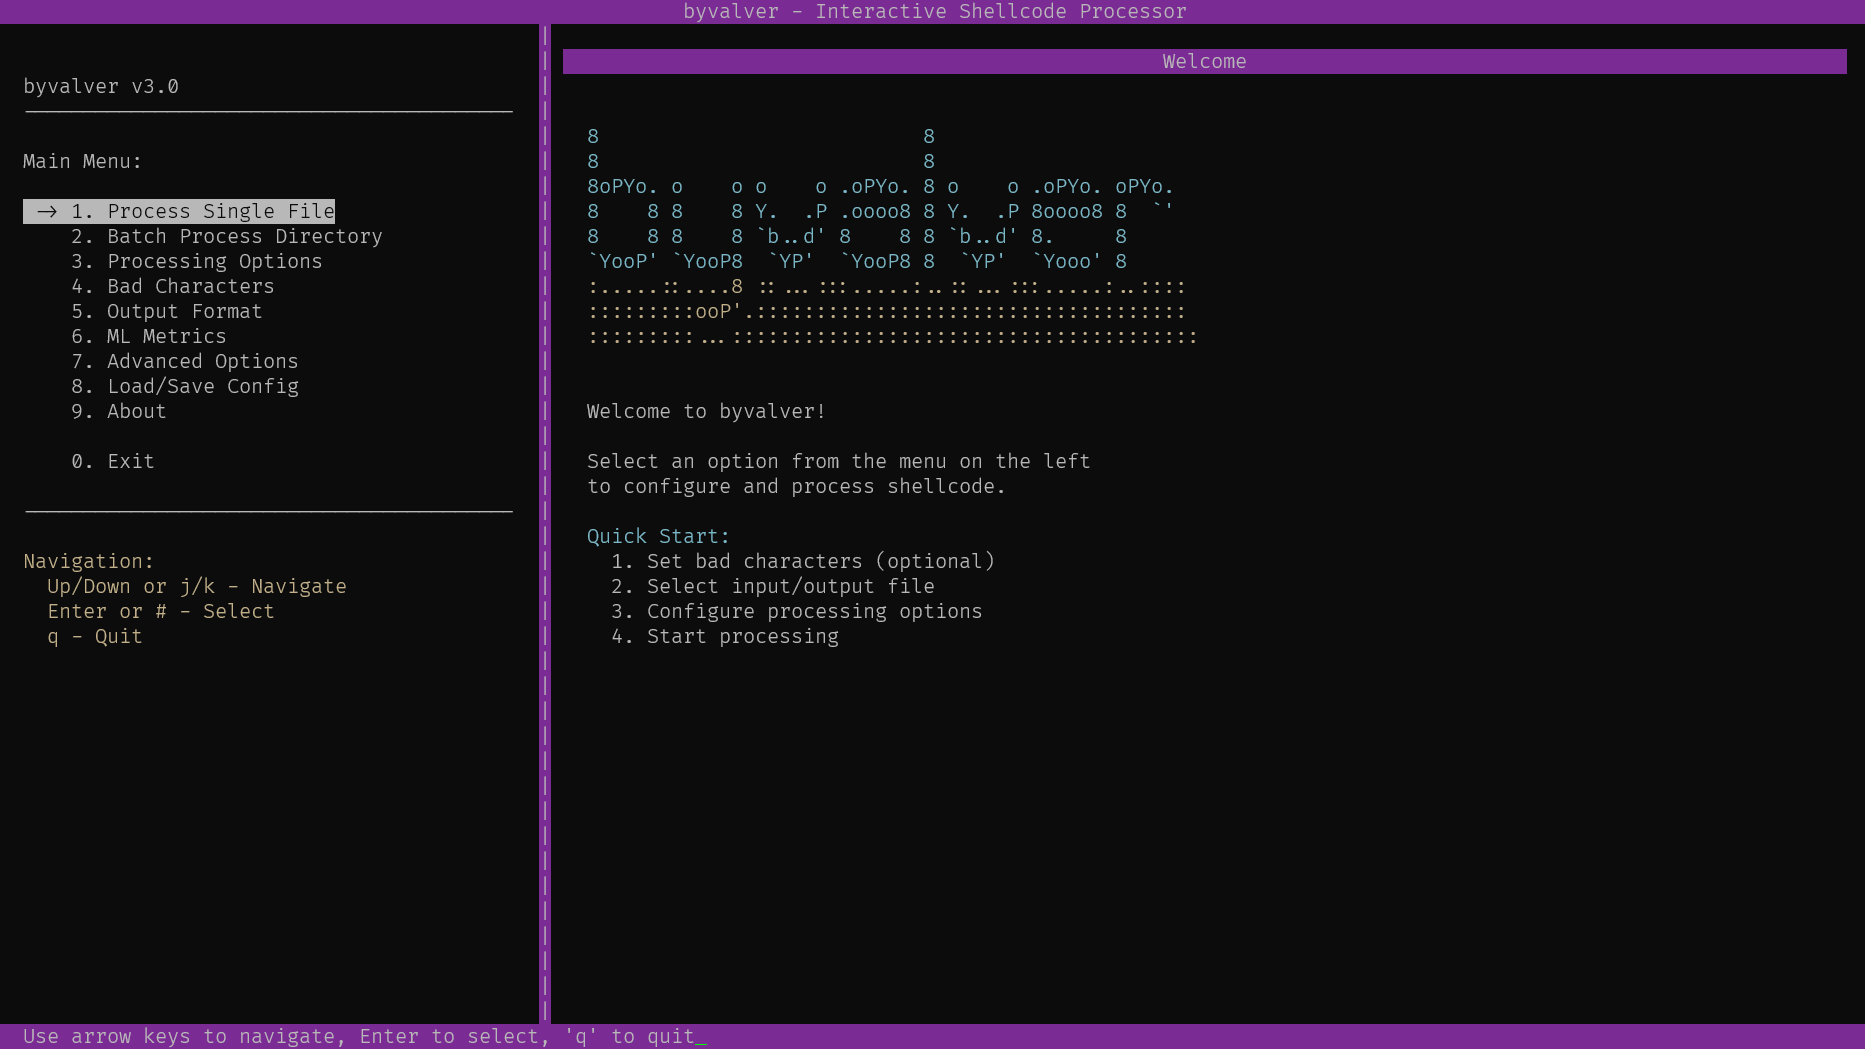 umpolungfish/byvalver
takes shellcode bad-bytes and banishes them, returning cleaned shellcode with preserved functionalities
 capt-meelo/lazzzy
Shellcode loader demonstrating multiple execution techniques including direct syscalls, IAT evasion, encrypted payloads, PPID spoofing, and code…
 0xrootpls/fritter
Polymorphic shellcode generator for in-memory execution of EXE, DLL, .NET, VBScript, and JScript with per-output and per-build randomization for…
 techryptic/pokemon-shellcode-loader
Tired of looking at hex all day and popping '\x41's? Rather look at Lugia/Charmander? I have the solution for you.