PichichiH0ll0wer
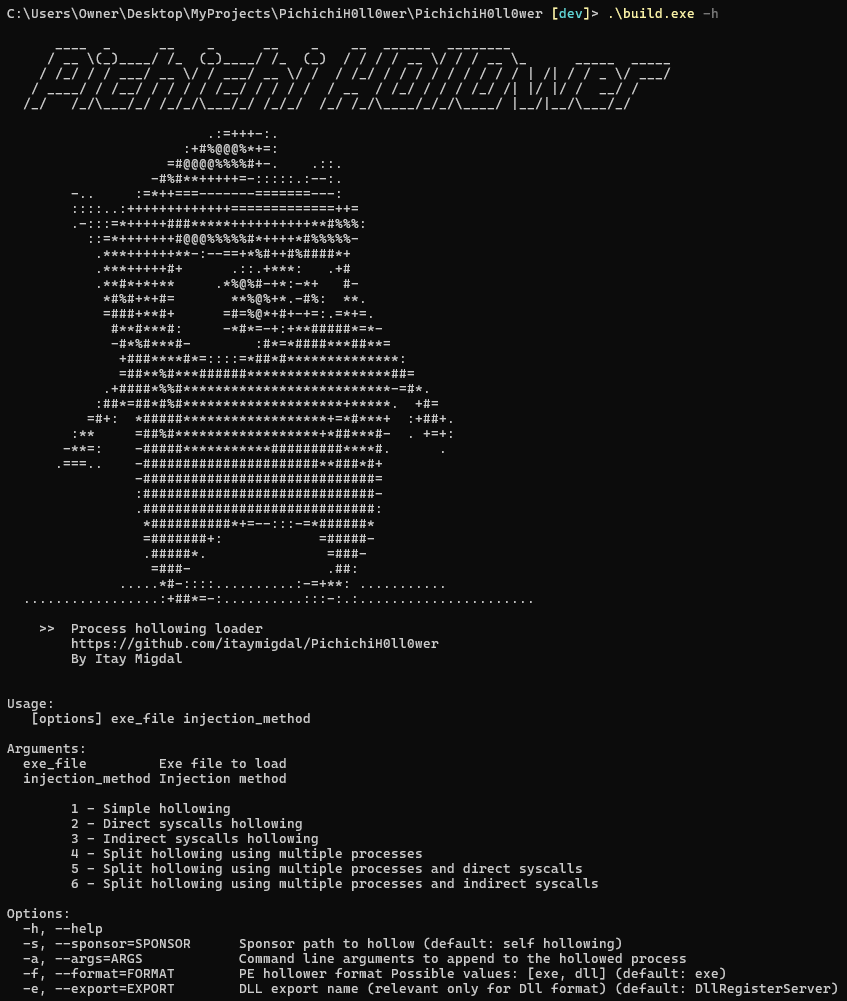
 itaymigdal/pichichih0ll0wer
Nim-based process hollowing loader for PE executables with configurable injection methods, direct/indirect syscalls, anti-debug, payload encryption,…
binary-exploitationexploitationpayload-generation+3
64
itaymigdal/pichichih0ll0werNim-based process hollowing loader for PE executables with configurable injection methods, direct/indirect syscalls, anti-debug, payload encryption,…
 themalwareguardian/cve-2025-5548
Buffer overflow in FreeFloat FTP Server 1.0 illustrating how a single unsafe handler can generate multiple CVE entries across different commands.
 ntdallas/bof_runpe
BOF to run PE in Cobalt Strike Beacon without console creation
 esskumar/phantomevasion
Python-based antivirus evasion tool generating undetectable executables from msfvenom payloads with advanced techniques like junkcode injection,…