
pinky
 davidtavarez/pinky
pinky - The PHP mini RAT (Remote Administration Tool)
command-and-controlencryption-decryption-toolspayload-generation+6
768 years ago
davidtavarez/pinkypinky - The PHP mini RAT (Remote Administration Tool)
 nxploited/cve-2025-32206
WordPress Processing Projects Plugin <= 1.0.2 is vulnerable to Arbitrary File Upload
 liangyueliangyue/spring-core-rce
Python-based exploit for CVE-2022-22965 (Spring4Shell) with vulnerability detection and webshell injection (Behinder/Godzilla) into Spring web…
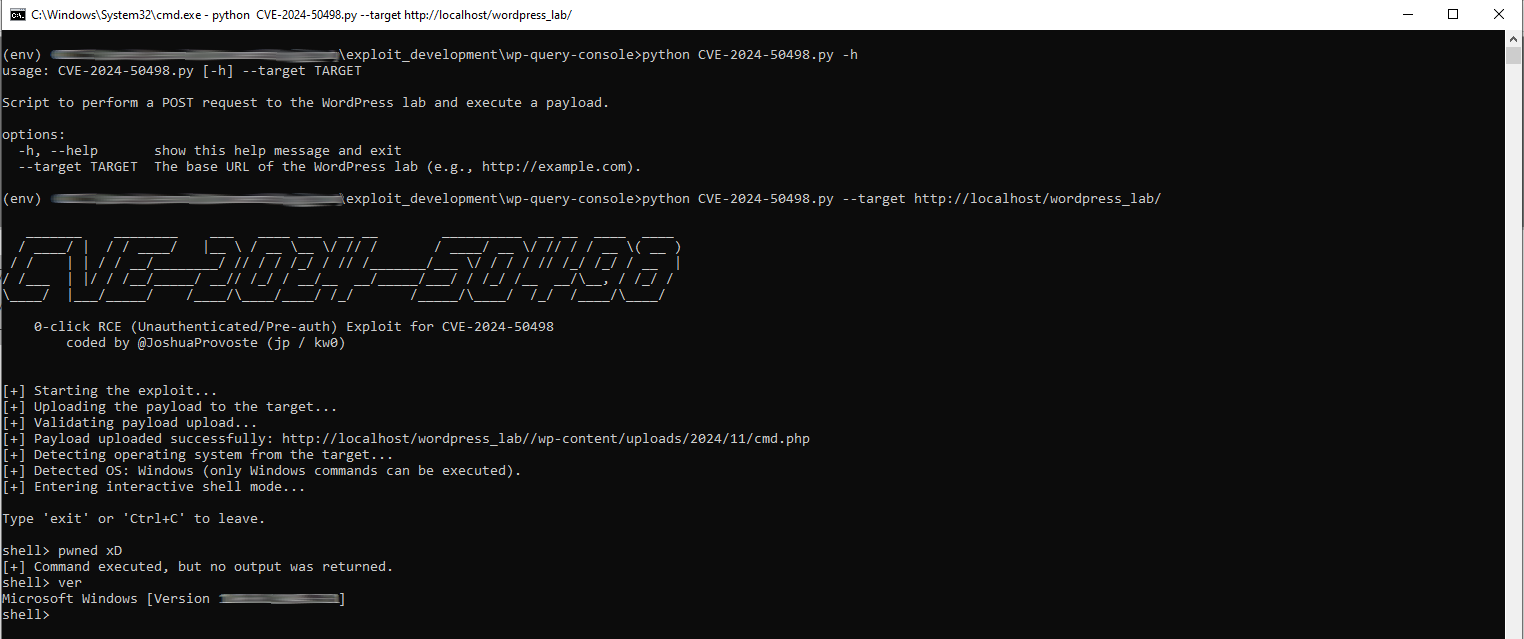 joshuaprovoste/0-click-rce-exploit-for-cve-2024-50498
Unauthenticated 0-click RCE exploit for CVE-2024-50498. Exploits a code injection vulnerability in the LUBUS WP Query Console plugin to execute…
 nxploited/cve-2024-56249
WordPress WPMasterToolKit plugin <= 1.13.1 - Arbitrary File Upload vulnerability
 themalwareguardian/cve-2002-1120
Classic stack-based buffer overflow in Savant Web Server 3.1 demonstrating early-2000s remote memory corruption through a crafted HTTP request.
 themalwareguardian/cve-2025-34096
SEH-based buffer overflow in Easy File Sharing Web Server 7.2, reachable through the password recovery endpoint.
 engranaabubakar/cve-2023-46818
Proof-of-concept exploit for authenticated PHP code injection in ISPConfig <= 3.2.11, enabling remote code execution via unsanitized language file…
 secforce/cve-2018-8941
D-Link DSL-3782 Code Execution (Proof of Concept)
 lukechilds/reverse-shell
On-demand reverse shell service that auto-detects target environment and executes appropriate payload for remote access during penetration tests.
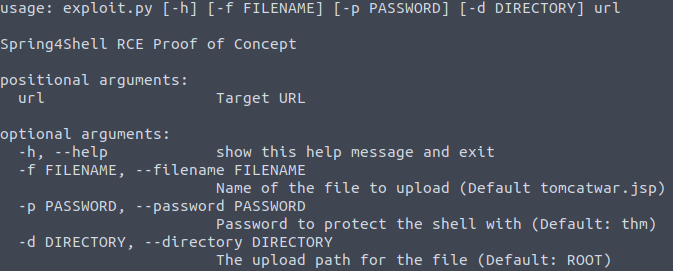 lucaspdiniz/cve-2022-22965
Spring4Shell Vulnerability RCE - CVE-2022-22965
 rapid7/metasploit-framework
Open-source exploitation framework with modular payload, encoder, and auxiliary system for penetration testing, vulnerability validation, and…
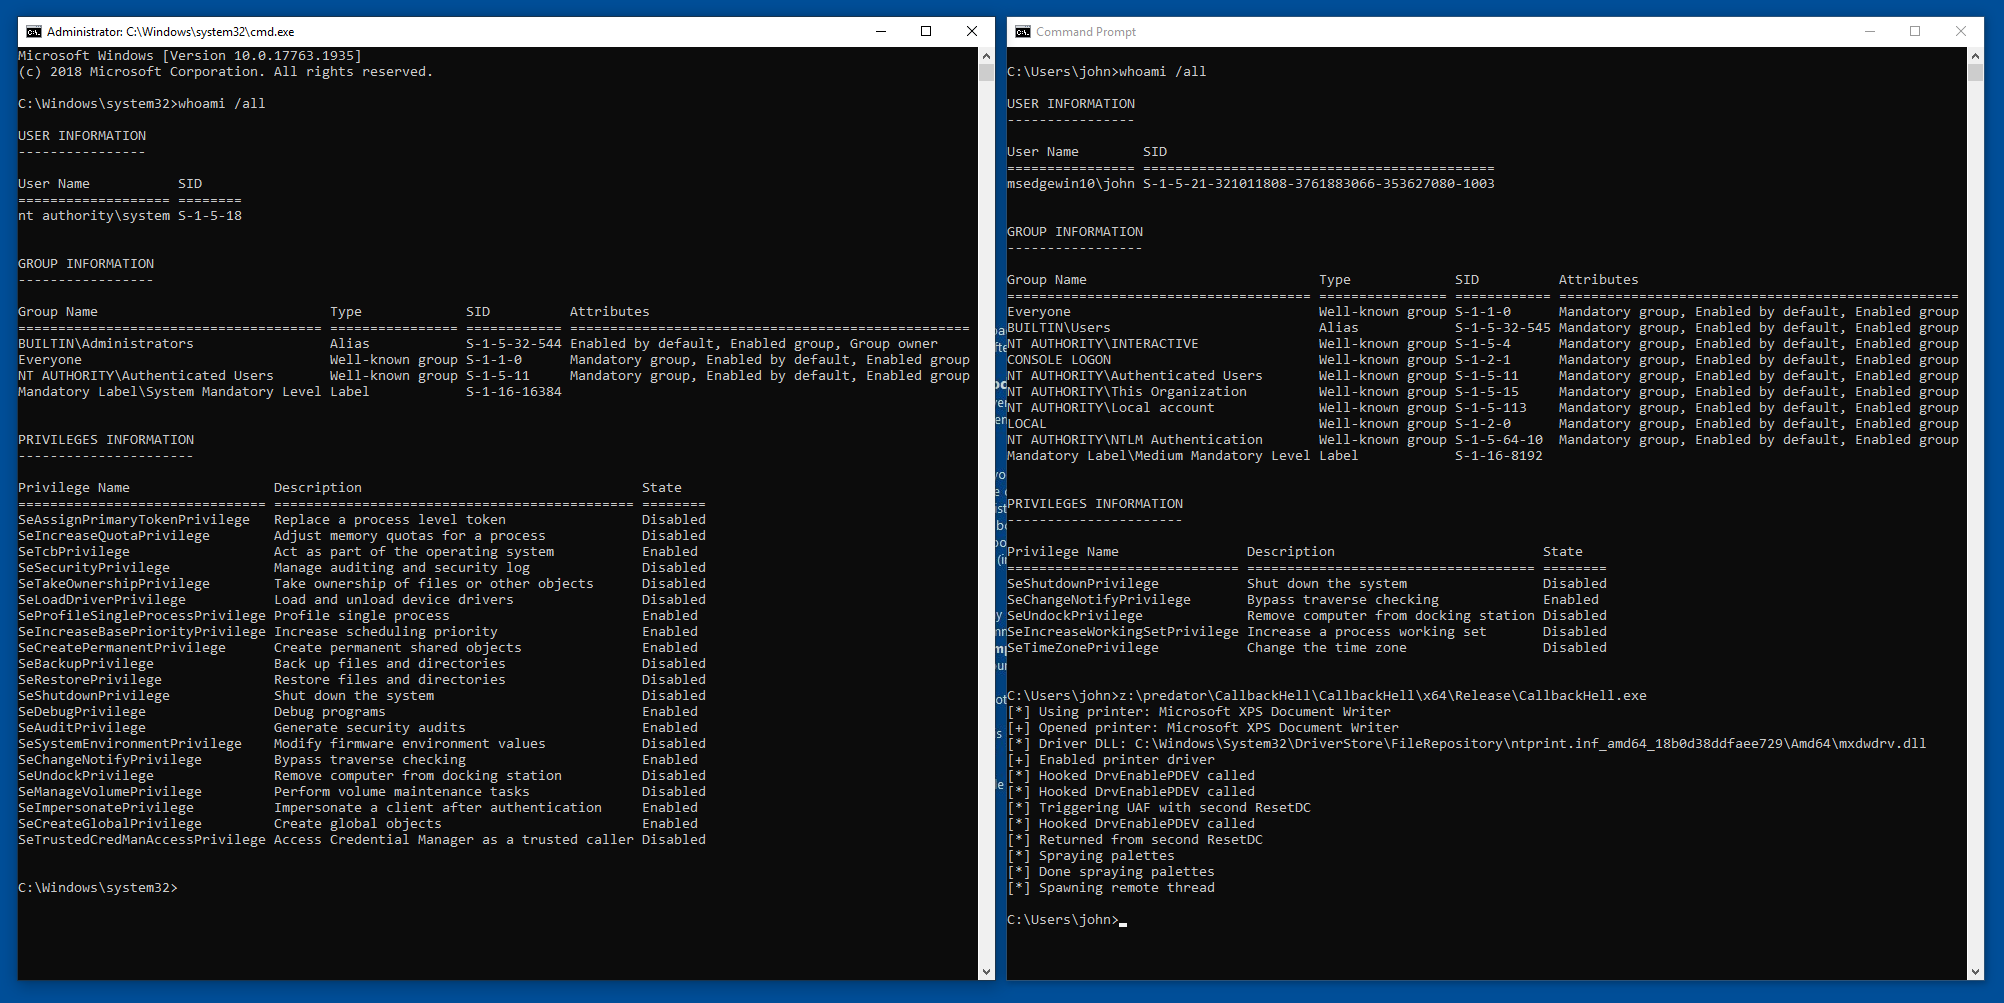 ly4k/callbackhell
Exploit for CVE-2021-40449 - Win32k Elevation of Privilege Vulnerability (LPE)
 noperator/cve-2019-18935
RCE exploit for a .NET JSON deserialization vulnerability in Telerik UI for ASP.NET AJAX.
 polo35/cve-2020-0022
CVE-2020-0022 vulnerability exploitation on Bouygues BBox Miami (Android TV 8.0 - ARM32 Cortex A9)
 rai2en/cve-2023-50564_pluck-v4.7.18_poc
A Proof of Concept for CVE-2023-50564 vulnerability in Pluck CMS version 4.7.18
 w01fh4cker/cve-2020-0688-gui
GUI Exploit Tool for CVE-2020-0688(Microsoft Exchange default MachineKeySection deserialize vulnerability)
 chainmanner/gzdoom-arbitrary-code-execution-via-zscript-poc
Proof of concept for CVE-2024-54756, a vulnerability I found in GZDoom's ZScript scripting engine.