
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
252 results
ZSC preview

ZSC

GitHubowasp/zsc

OWASP ZSC - Shellcode/Obfuscate Code Generator https://www.secologist.com/
encryption-decryption-toolsexploit-frameworkspayload-generation+5
6532 years ago
CVE-2026-31431-Linux-Copy-Fail preview

CVE-2026-31431-Linux-Copy-Fail

GitHubdullpurple-sloop726/cve-2026-31431-linux-copy-fail

Exploit CVE-2026-31431 on Linux using a Rust implementation to achieve local privilege escalation via an arbitrary page cache write primitive.
binary-exploitationeducationexploitation+4
32 days ago
artifacts-kit preview

artifacts-kit

GitHubforrest-orr/artifacts-kit

Pseudo-malicious usermode memory artifact generator kit designed to easily mimic the footprints left by real malware on an infected Windows OS.
exploitationforensicsmalware-analysis+5
2282 years ago
patching preview

patching

GitHubgaasedelen/patching

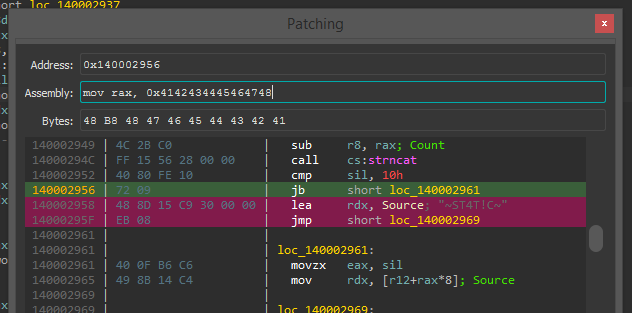
An Interactive Binary Patching Plugin for IDA Pro

binary-analysisbinary-exploitationdebuggers+8
1.3k1 year ago
InflativeLoading preview

InflativeLoading

GitHubsenzee1984/inflativeloading

Dynamically convert an unmanaged EXE or DLL file to PIC shellcode by prepending a shellcode stub.
binary-exploitationexploitationmalware-analysis+3
3252 years ago
VectoredOverloading preview

VectoredOverloading

GitHubcheckpointsw/vectoredoverloading

Local PE injection technique using hardware breakpoints and vectored exception handling to manipulate DLL loading and execute arbitrary payloads, as…
binary-exploitationexploitationmalware-analysis+6
1269 months ago
js-driveby-download-CVE-2006-4777 preview

js-driveby-download-CVE-2006-4777

GitHubmario1234/js-driveby-download-cve-2006-4777

malware del lado del cliente de explotacion de vulnerabilidad de internet explorer 6.0 SP1 en windows xp SP2. No requiere de consentimiento por parte…

exploitationmalware-analysispayload-generation+2
8 years ago
themida-unmutate preview

themida-unmutate

GitHubergrelet/themida-unmutate

Static deobfuscator for Themida, WinLicense and Code Virtualizer 3.x's mutation-based obfuscation.

binary-analysisbinary-exploitationmalware-analysis+3
3952 years ago
Lucky-Spark preview

Lucky-Spark

GitHubschich/lucky-spark

A stealthy stager designed for shellcode payloads staged with http/https like Sliver, or on github raw.
binary-analysiscommand-and-controlexploitation+6
632 months ago
shellcodetester preview

shellcodetester

GitHubhelviojunior/shellcodetester

An application to test windows and linux shellcodes
binary-analysisexploitationpayload-development+2
951 year ago
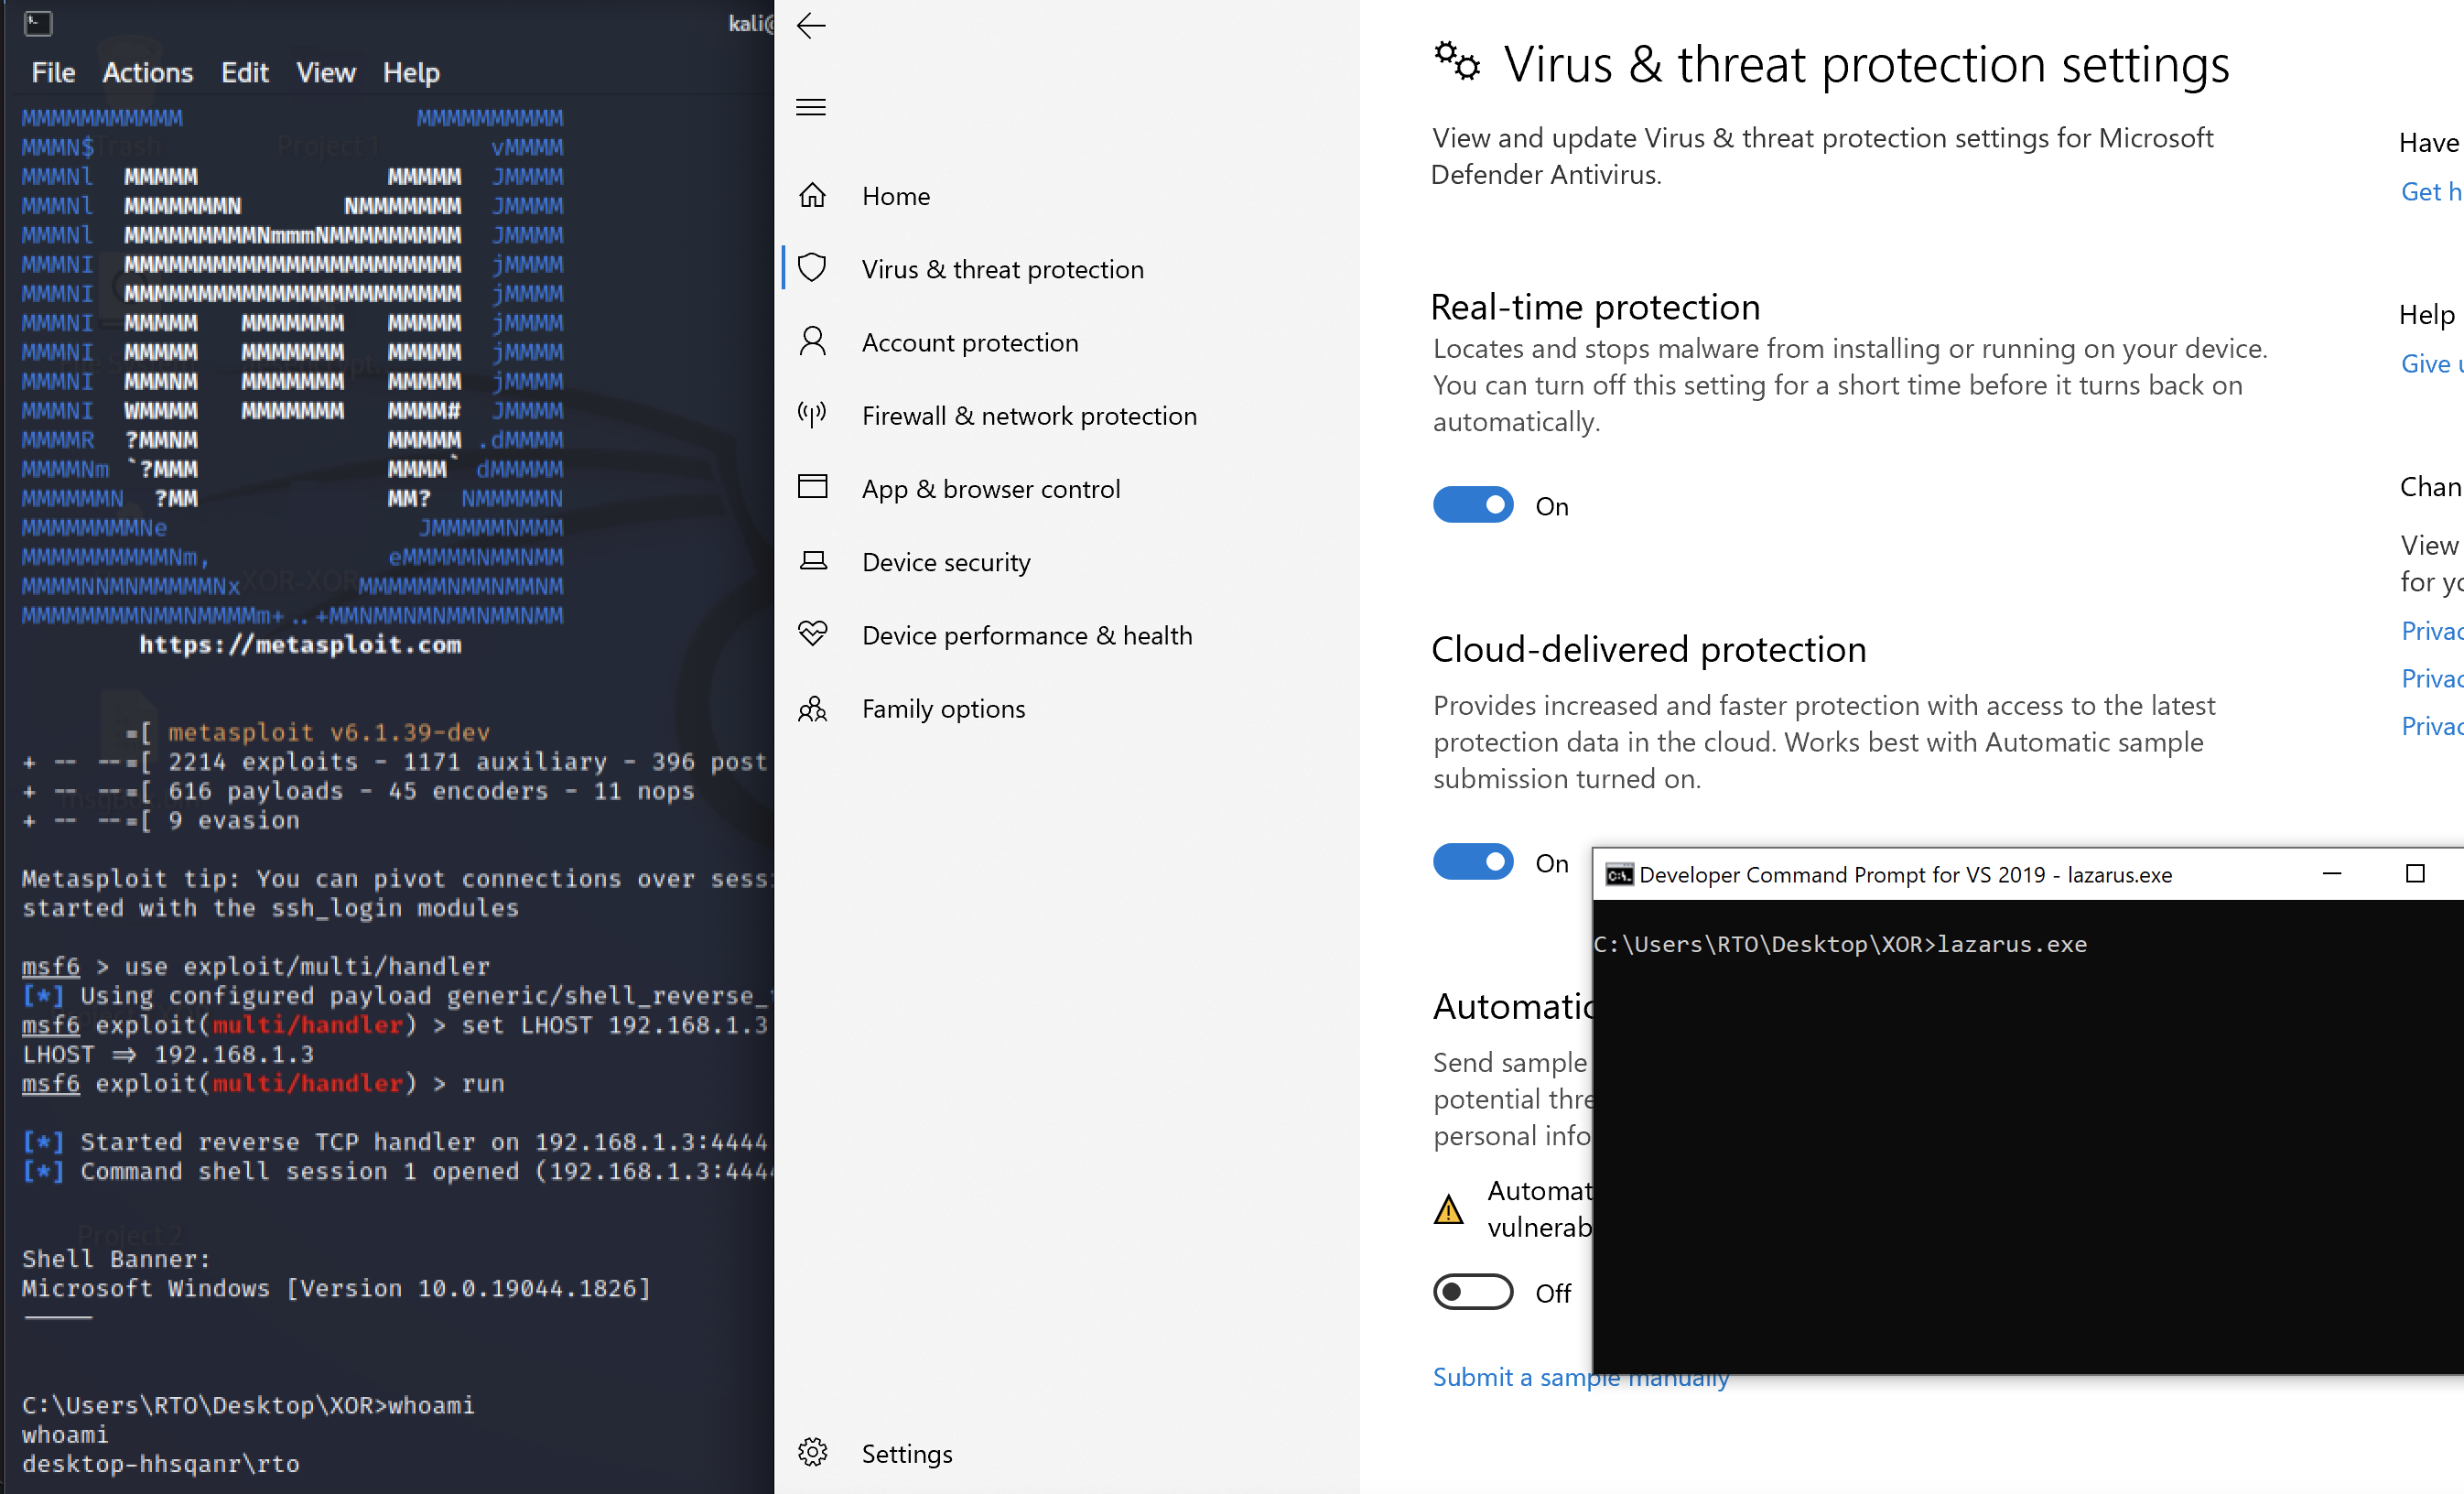
FUD-UUID-Shellcode preview

FUD-UUID-Shellcode

GitHubbl4ckm1rror/fud-uuid-shellcode

C++ shellcode injection technique using XOR encryption and UUID string conversion to bypass Windows Defender, with function call obfuscation and…

binary-exploitationdefensive-toolsexploitation+6
3343 years ago
Windows-X64-RAT preview

Windows-X64-RAT

GitHubmaorbuskila/windows-x64-rat

Remote Access Trojan (RAT) for Windows x64 using a combination of vulnerability CVE-2023-38831 (WinRAR < 6.23 vulnerability) and Shellcode…

binary-exploitationcommand-and-controleducation+5
22 years ago
Dirty-Vanity preview

Dirty-Vanity

GitHubdeepinstinct/dirty-vanity

A POC for the new injection technique, abusing windows fork API to evade EDRs. https://www.blackhat.com/eu-22/briefings/schedule/index.html#dirty-vani…
adversarial-attackexploitationpayload-development+4
6743 years ago
CVE-2025-2783 preview

CVE-2025-2783

GitHubeliangonzi00/cve-2025-2783

Full-chain RCE exploit for CVE-2025-2783, a Chromium Ipcz sandbox escape vulnerability. Implements thread hijacking, V8 hooks, and shellcode…

binary-exploitationexploitationpayload-development+5
3 months ago
cve-2022-3218 preview

cve-2022-3218

GitHubmoisestapia/cve-2022-3218

Python exploit for CVE-2022-3218 that generates a reverse TCP payload via msfvenom and delivers it over HTTP to a target Windows host.
command-and-controlexploitationpayload-generation+3
9 months ago
CVE-2015-1578-PoC-Metasploit preview

CVE-2015-1578-PoC-Metasploit

GitHubyaldobaoth/cve-2015-1578-poc-metasploit

This is a proof-of-concept Metasploit module exploit for CVE-2015-1578, a buffer overflow vulnerability in Achat 0.150 beta7 on Windows. Exploitation…

binary-exploitationexploitationexploit-frameworks+6
1 year ago
CVE-2015-1578-PoC preview

CVE-2015-1578-PoC

GitHubyaldobaoth/cve-2015-1578-poc

This is a proof-of-concept exploit for CVE-2015-1578, a buffer overflow vulnerability in Achat 0.150 beta7 on Windows. Exploitation leads to remote…

binary-exploitationeducationexploitation+5
1 year ago
BloodfangC2 preview

BloodfangC2

GitHubzarkones/bloodfangc2

Modern PIC implant for Windows (64 & 32 bit)

adversarial-attackcommand-and-controlpayload-development+4
1031 year ago
Previous12…14Next