

ExecuteAssembly
 med0x2e/executeassembly
Load/Inject .NET assemblies by; reusing the host (spawnto) process loaded CLR AppDomainManager, Stomping Loader/.NET assembly PE DOS headers,…
command-and-controlexploitationids-ips-evasion+8
599
med0x2e/executeassemblyLoad/Inject .NET assemblies by; reusing the host (spawnto) process loaded CLR AppDomainManager, Stomping Loader/.NET assembly PE DOS headers,…
 enelg52/kittystager
KittyStager is a simple stage 0 C2. It is made of a web server to host the shellcode and an implant, called kitten. The purpose of this project is to…
 m4sc3r4n0/astroid
ASTROID v 1.2 bypass most A.V softwares
 rek7/postshell
PostShell - Post Exploitation Bind/Backconnect Shell
 choisg/onedriveupdatersideloading
Payload for DLL sideloading of the OneDriveUpdater.exe, based on the PaloAltoNetwork Unit42's blog post
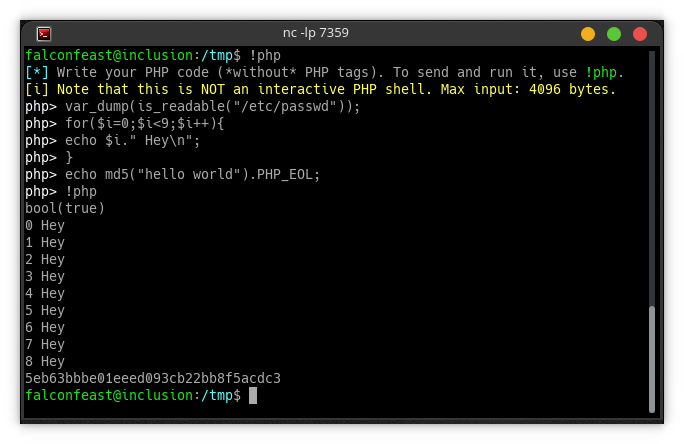 nickguitar/yaps
Yet Another PHP Shell - The most complete PHP reverse shell
 ruoji6/cve-2025-55182-rce-shell
Burp Suite/antsword - Interactive shell (HTTP hijack + POST + AES-256-CBC/BASE64)
 ill-deed/cve-2025-34085-multi-target
Multi-target unauthenticated RCE scanner for CVE-2025-34085 affecting WordPress Simple File List plugin. Uploads, renames, and triggers PHP webshells…
 yukinime/cve-2025-34085
Automated scanner and exploit for CVE-2025-34085, an unauthenticated RCE in the WordPress Simple File List plugin. Supports multi-target scanning,…
 lipeozyy/cve-2017-14980_syncbreeze_10.0.28_bof
Proof-of-concept buffer overflow exploit for Sync Breeze Enterprise v10.0.28 (CVE-2017-14980). Sends crafted HTTP POST payload to overwrite EIP and…
 themalwareguardian/cve-2018-18912
SEH-based buffer overflow in Easy File Sharing Web Server 7.2 demonstrating how an authenticated HTTP POST parameter can corrupt the exception…
 moisestapia/cve-2022-3218
Python exploit for CVE-2022-3218 that generates a reverse TCP payload via msfvenom and delivers it over HTTP to a target Windows host.
 svchostmm/cve-2024-25600-mass
Mass exploit for CVE-2024-25600, uploading webshells to vulnerable WordPress sites via a list of targets.
 laskdjlaskdj12/cve-2024-35106-poc
Proof-of-concept exploit for CVE-2024-35106, a stack buffer overflow in NEXTU FLETA AX1500 Wi-Fi 6 router. Demonstrates denial-of-service and…
 bc-security/empire
Empire is a post-exploitation and adversary emulation framework that is used to aid Red Teams and Penetration Testers.
 klezvirus/syswhispers3
SysWhispers on Steroids - AV/EDR evasion via direct system calls.
 cobbr/sharpsploit
SharpSploit is a .NET post-exploitation library written in C#
 lukechilds/reverse-shell
On-demand reverse shell service that auto-detects target environment and executes appropriate payload for remote access during penetration tests.