

Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
30 results
Invisi-Shell preview

Invisi-Shell

GitHubomerya/invisi-shell

Hide your Powershell script in plain sight. Bypass all Powershell security features

defensive-toolsexploitationids-ips-evasion+9
1.3k7 years ago
DEFCON-31-Syscalls-Workshop preview

DEFCON-31-Syscalls-Workshop

GitHubvirtualalllocex/defcon-31-syscalls-workshop

Contains all the material from the DEF CON 31 workshop "(In)direct Syscalls: A Journey from High to Low".

educationlabs-practicepayload-development+2
7891 year ago
sharem preview

sharem

GitHubbw3ll/sharem

SHAREM is a shellcode analysis framework, capable of emulating more than 45,000 WinAPIs and virutally all Windows syscalls. It also contains its own…

ai-securitybinary-analysisdebuggers+5
4927 months ago
win-exec-calc-shellcode preview

win-exec-calc-shellcode

GitHubpeterferrie/win-exec-calc-shellcode

A small, null-free Windows shellcode that executes calc.exe (x86/x64, all OS/SPs)

binary-exploitationexploitationpayload-development+3
4502 years ago
monomorph preview

monomorph

GitHubdavidbuchanan314/monomorph

MD5-Monomorphic Shellcode Packer - all payloads have the same MD5 hash

binary-exploitationcryptographyexploitation+5
7924 years ago
ASWCrypter preview

ASWCrypter

GitHubabedalqaderswedan1/aswcrypter

An Bash&Python Script For Generating Payloads that Bypasses All Antivirus so far [FUD]
educationexploit-frameworkspayload-development+4
2908 years ago
ByteCaster preview

ByteCaster

GitHubprint3m/bytecaster

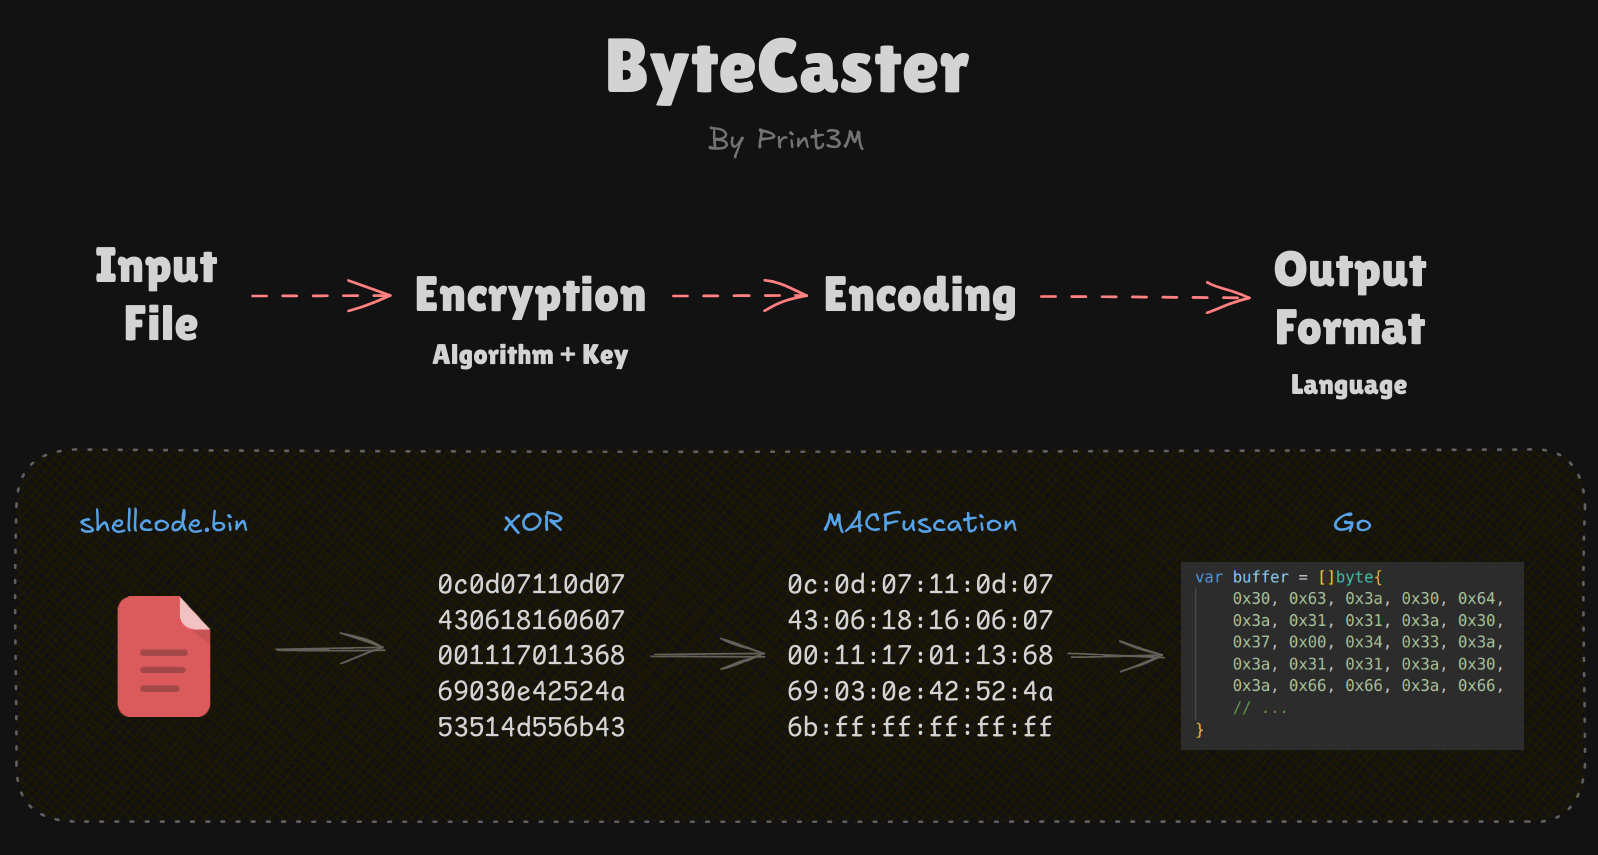
Swiss Army Knife for payload encryption, obfuscation, and conversion to byte arrays – all in a single command (14 output formats supported)! ☢️

encryption-decryption-toolspayload-developmentred-teaming+1
2307 months ago
Pokemon-Shellcode-Loader preview

Pokemon-Shellcode-Loader

GitHubtechryptic/pokemon-shellcode-loader

Tired of looking at hex all day and popping '\x41's? Rather look at Lugia/Charmander? I have the solution for you.
adversarial-attackpayload-developmentpayload-generation+3
1264 years ago
cve-2019-0708_bluekeep_rce preview

cve-2019-0708_bluekeep_rce

GitHubcoolboy4me/cve-2019-0708_bluekeep_rce

it works on xp (all version sp2 sp3)
exploitationpayload-developmentpenetration-testing+3
757 years ago
bst preview
Archived

bst

GitHube3prom/bst

Binary String Toolkit (BST). Quickly and easily convert binary strings for all your exploit development needs. 😎
binary-analysispayload-generationpenetration-testing+3
228 years ago
meterssh preview

meterssh

GitHubtrustedsec/meterssh

MeterSSH is a way to take shellcode, inject it into memory then tunnel whatever port you want to over SSH to mask any type of communications as a…

command-and-controlexploitationpayload-development+4
5309 years ago
sliver preview

sliver

GitHubbishopfox/sliver

Adversary Emulation Framework

adversarial-attackcommand-and-controldata-exfiltration+16
12.1k5 days ago
Blackbone preview

Blackbone

GitHubdarthton/blackbone

Windows memory hacking library

binary-analysisdebuggersdynamic-analysis-sandboxing+9
5.5k4 years ago
merlin preview

merlin

GitHubne0nd0g/merlin

Merlin is a cross-platform post-exploitation HTTP/2 Command & Control server and agent written in golang.

command-and-controldata-exfiltrationexploit-frameworks+10
5.6k4 days ago
BokuLoader preview

BokuLoader

GitHubboku7/bokuloader

A proof-of-concept Cobalt Strike Reflective Loader which aims to recreate, integrate, and enhance Cobalt Strike's evasion features!

binary-analysisexploit-frameworkspayload-development+3
1.4k2 years ago
reverse_ssh preview

reverse_ssh

GitHubnhas/reverse_ssh

SSH-based reverse shell management tool with native SCP/SFTP support, multiple transport protocols, Windows DLL generation, and fileless execution…
shellcodeshellcode-generation
1.5k1 month ago
Obfusk8 preview

Obfusk8

GitHubx86byte/obfusk8

Obfusk8: lightweight Obfuscation library based on C++17 / Header Only for windows binaries
cryptographyexploit-frameworkspayload-development+4
8323 months ago
Shellcode-Injection-Techniques preview

Shellcode-Injection-Techniques

GitHubplackyhacker/shellcode-injection-techniques

C# implementations of shellcode injection techniques including classic injection, thread hijacking, process hollowing, and atom bombing, using…

exploitationpost-exploitationred-teaming+1
4674 years ago
Previous12Next