CVE-2023-41425-RCE-WonderCMS-4.3.2

Automates creation and hosting of a JavaScript XSS payload to install a malicious theme module, triggering a reverse shell via Remote Code Execution…

Automates creation and hosting of a JavaScript XSS payload to install a malicious theme module, triggering a reverse shell via Remote Code Execution…

Icecast Header Overwrite buffer overflow RCE < 2.0.1 (Win32)

Threadless Module Stomping In Rust with some features (In memory of those murdered in the Nova party massacre)

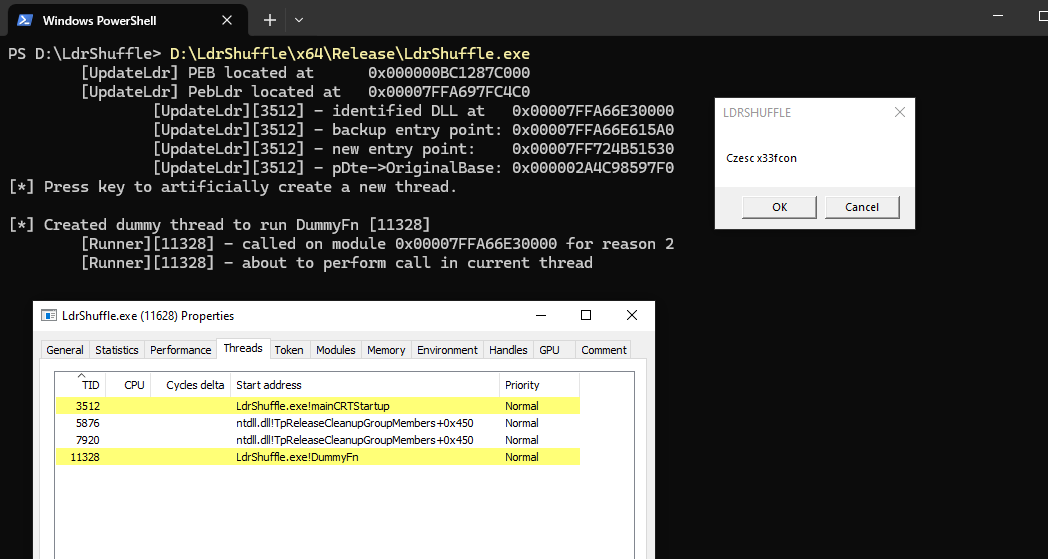
Code execution/injection technique using DLL PEB module structure manipulation

Adaptix C2 agent using Crystal Palace PIC linker and PICO module system

Cobalt Strike UDRL that performs advanced module stomping using VEH to intercept calls, unmap modules during sleep, and remap fresh modules to evade…

This is a proof-of-concept Metasploit module exploit for CVE-2015-1578, a buffer overflow vulnerability in Achat 0.150 beta7 on Windows. Exploitation…

Hide your Powershell script in plain sight. Bypass all Powershell security features

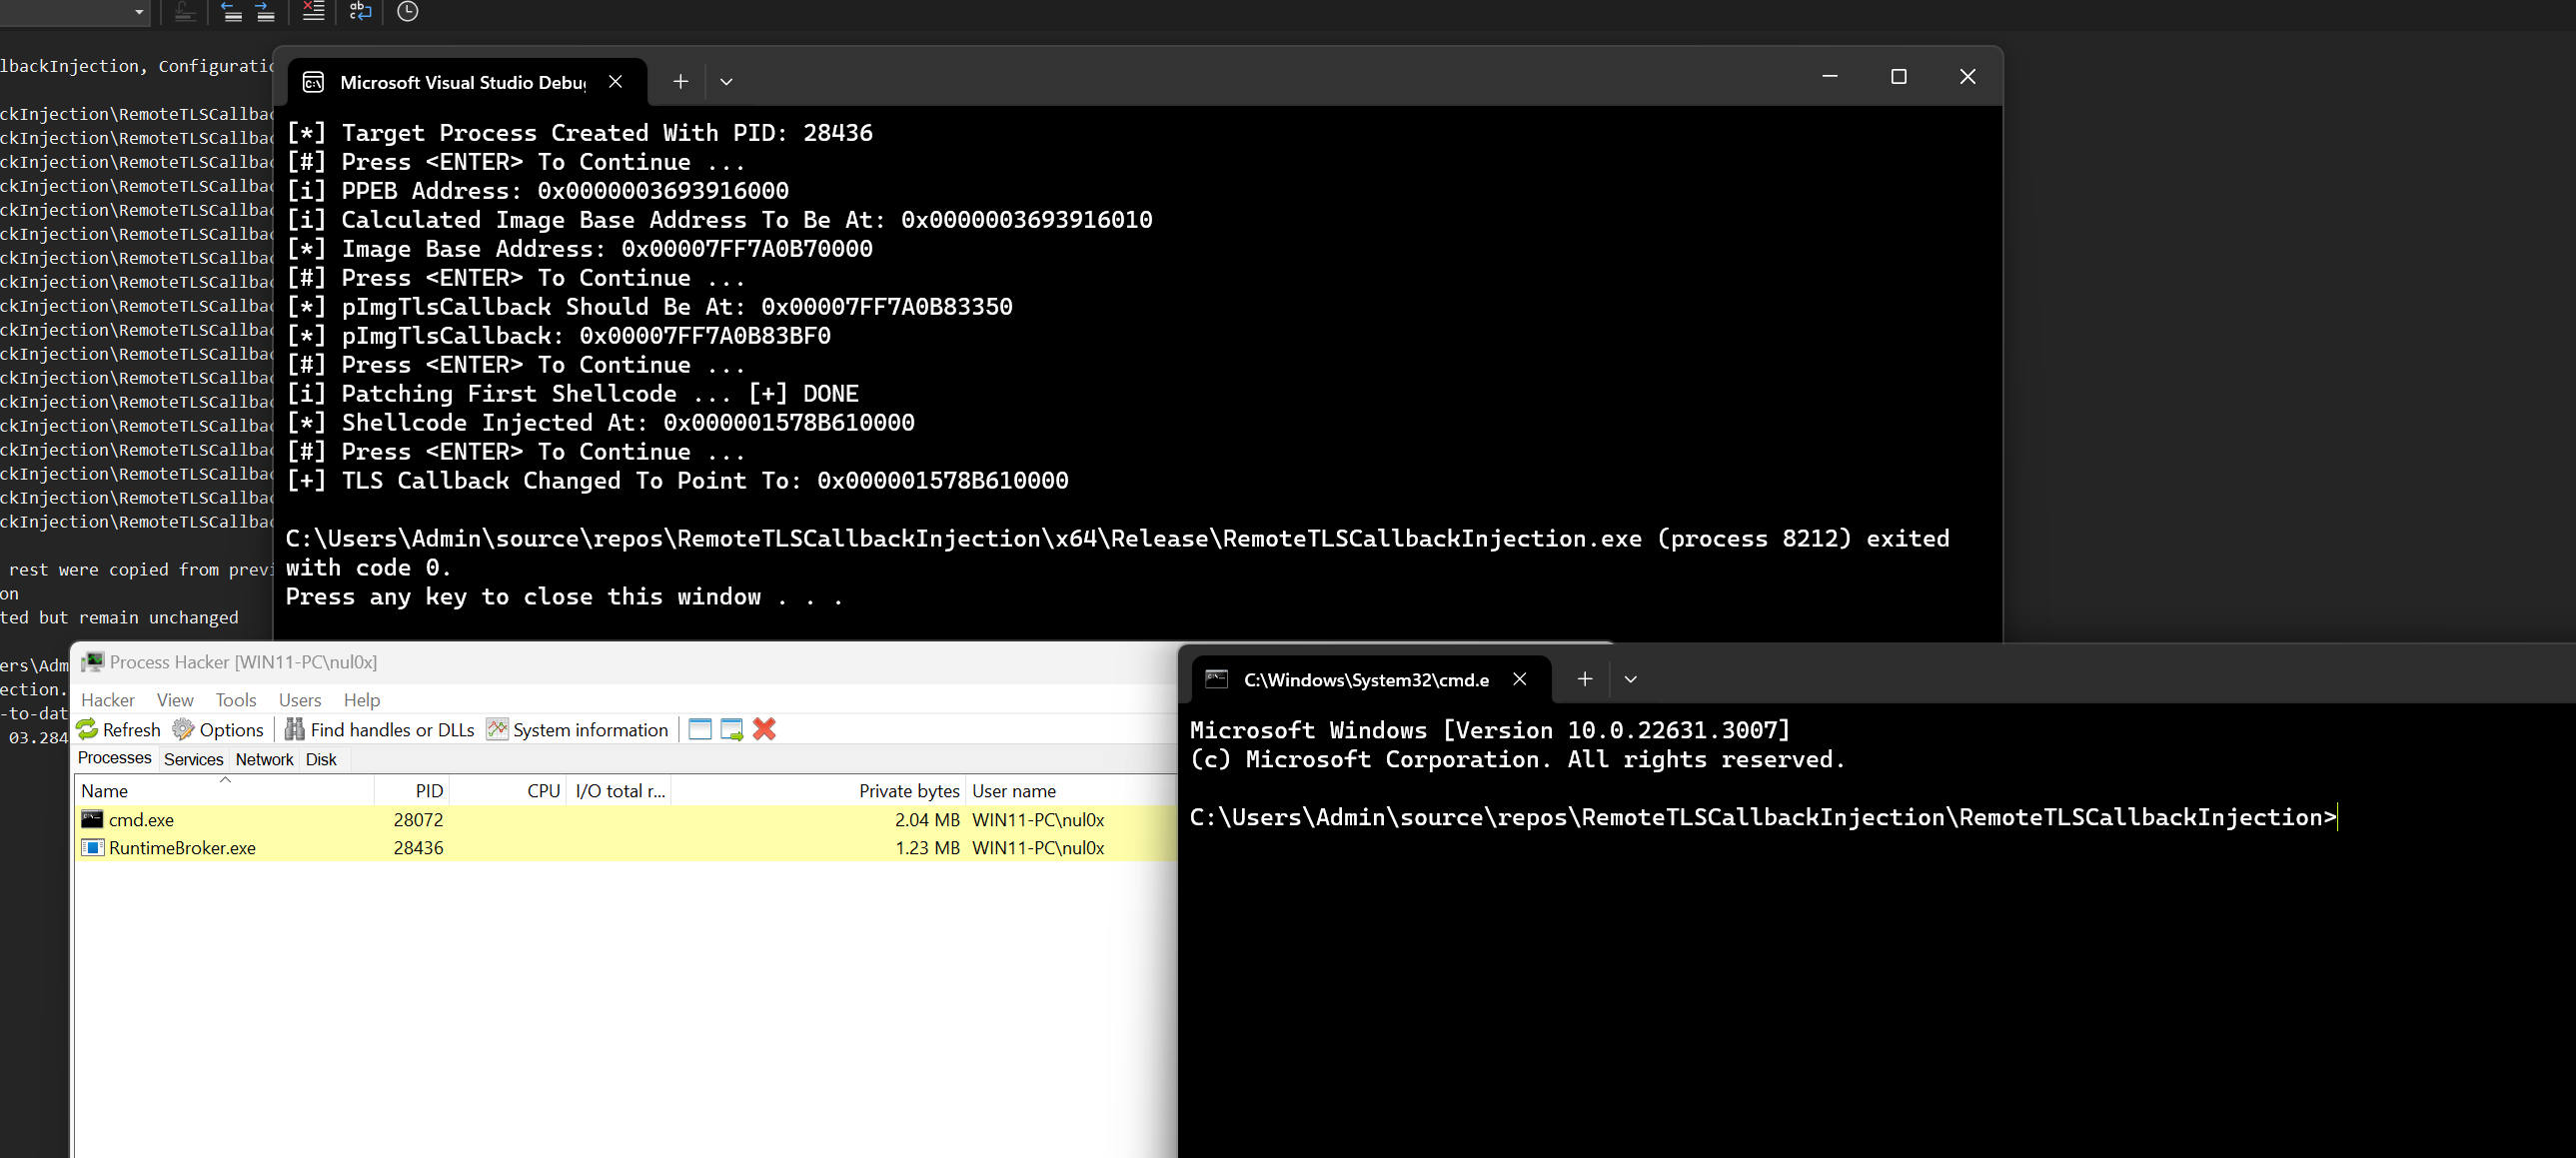
Utilizing TLS callbacks to execute a payload without spawning any threads in a remote process

BOF to run PE in Cobalt Strike Beacon without console creation