


 zardus/ctf-tools
Some setup scripts for security research tools.
 ashemery/exploitation-course
Offensive Software Exploitation Course
 byt3bl33d3r/offensivedlr
Toolbox containing research notes & PoC code for weaponizing .NET's DLR
 sunblaze-ucb/exploitgym
ExploitGym is a large-scale, realistic benchmark built from real-world vulnerabilities designed to evaluate AI agents' ability to develop exploits.
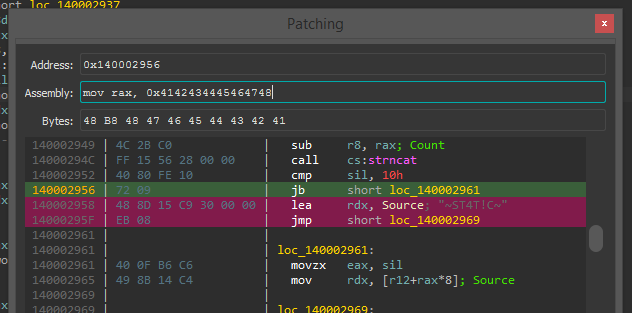 gaasedelen/patching
An Interactive Binary Patching Plugin for IDA Pro
 bw3ll/sharem
SHAREM is a shellcode analysis framework, capable of emulating more than 45,000 WinAPIs and virutally all Windows syscalls. It also contains its own…
 seanheelan/anamnesis-release
Evaluation framework for studying LLM agents that automatically generate working exploits from vulnerability reports, bypassing modern security…
 zznop/sploit
Go package that aids in binary analysis and exploitation
 zcutlip/bowcaster
Python-based exploit development framework with payloads, encoders, and connect-back servers, focused on MIPS CPU architecture but designed for…
 arthastang/router-exploit-shovel
Automated Application Generation for Stack Overflow Types on Wireless Routers
 d4rkcat/stackflow
Universal stack-based buffer overfow exploitation tool
 flopz-project/flopz
Pure Python assembler toolkit for creating shellcode, dynamically patching binaries, and instrumenting firmware images for debugging and fuzzing on…
 fkshield/cve-2025-5548
End-to-end exploitation lab for CVE-2025-5548 (FreeFloat FTP Server stack buffer overflow). Includes static analysis with IDA/Ghidra, binary fuzzing,…

 blackjuker2/cve-2019-0232
Apache Tomcat CGI Servlet RCE (Windows)
 sudoand3rs0n/cve-2025-5548
Educational repository documenting the analysis and exploitation of CVE-2025-5548 (FreeFloat FTP Server buffer overflow). Includes a reusable…