Skip to content
KitploitKITPLOIT
ToolsBlog
Submit
ToolsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

··Feeds·Contact·Privacy·© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
128 results
CVE-2019-0567-MS-Edge preview

CVE-2019-0567-MS-Edge

GitHubnatteesetobol/cve-2019-0567-ms-edge

My proof of concept for CVE-2019 Microsoft-Edge

binary-exploitationeducationexploitation+4
2 years ago
Empire preview

Empire

GitHubbc-security/empire

Empire is a post-exploitation and adversary emulation framework that is used to aid Red Teams and Penetration Testers.

adversarial-attackcommand-and-controldata-exfiltration+16
5.3k12 days ago
donut preview

donut

GitHubthewover/donut

Generates x86, x64, or AMD64+x86 position-independent shellcode that loads .NET Assemblies, PE files, and other Windows payloads from memory and runs…

exploitationids-ips-evasionmemory-forensics+7
4.7k1 year ago
Villain preview

Villain

GitHubt3l3machus/villain

Villain is a high level stage 0/1 C2 framework that can handle multiple reverse TCP & HoaxShell-based shells, enhance their functionality with…

command-and-controlexploit-frameworkspayload-generation+4
4.5k1 year ago
r77-rootkit preview

r77-rootkit

GitHubbytecode77/r77-rootkit

Fileless ring 3 rootkit with installer and persistence that hides processes, files, network connections, etc.
command-and-controldefensive-toolsids-ips-evasion+6
2.2k2 months ago
reverse-shell preview

reverse-shell

GitHublukechilds/reverse-shell

On-demand reverse shell service that auto-detects target environment and executes appropriate payload for remote access during penetration tests.

command-and-controlexploitationpenetration-testing+3
2.1k7 months ago
twittor preview

twittor

GitHubpaulsec/twittor

A fully featured backdoor that uses Twitter as a C&C server

command-and-controlexploitationpayload-development+4
81111 years ago
Shoggoth preview

Shoggoth

GitHubfrkngksl/shoggoth

Polymorphic encryptor that transforms shellcode, PE, and COFF files into obfuscated, position-independent payloads with RC4 and random block cipher…
binary-analysisexploit-frameworkspayload-generation+2
8105 months ago
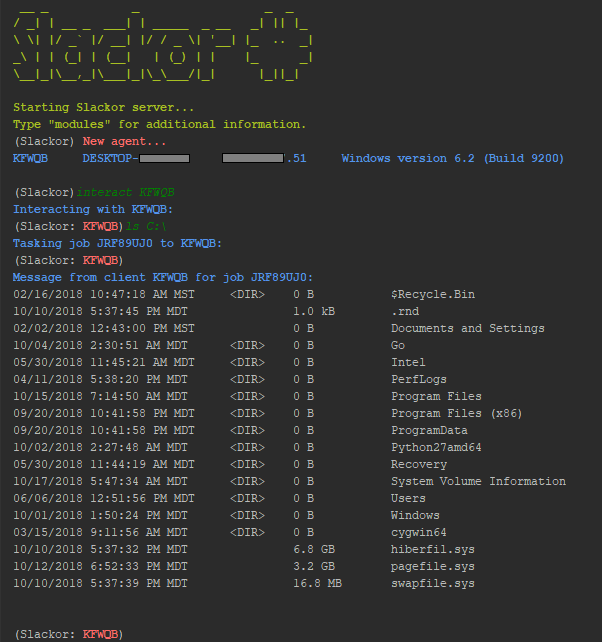
Slackor preview

Slackor

GitHubcoalfire-research/slackor

A Golang implant that uses Slack as a command and control server

command-and-controllateral-movementpassword-attacks+8
4606 years ago
OffensiveCpp preview

OffensiveCpp

GitHublsecqt/offensivecpp

This repo contains C/C++ snippets that can be handy in specific offensive scenarios.
adversarial-attackcurated-resourcesexploitation+6
7741 year ago
Voidgate preview

Voidgate

GitHubvxcrypt0r/voidgate

A technique that can be used to bypass AV/EDR memory scanners. This can be used to hide well-known and detected shellcodes (such as msfvenom) by…
adversarial-attackdebuggersids-ips-evasion+3
5982 years ago
canisrufus preview

canisrufus

GitHubmaldevel/canisrufus

A stealthy Python based Windows backdoor that uses Github as a command and control server
command-and-controlpayload-generationpost-exploitation+2
2659 years ago
gmailc2 preview

gmailc2

GitHubmachine1337/gmailc2

A Fully Undetectable C2 Server That Communicates Via Google SMTP to evade Antivirus Protections and Network Traffic Restrictions

command-and-controleducationpayload-generation+4
4891 year ago
win-exec-calc-shellcode preview

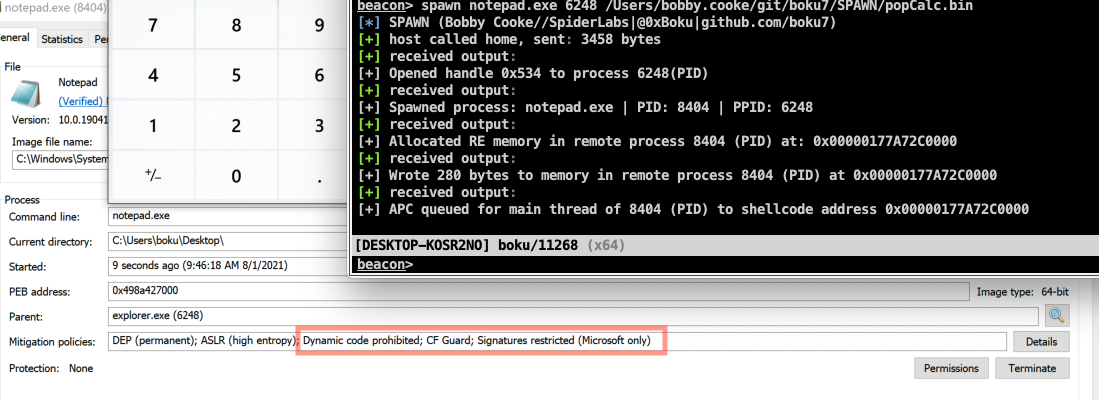
win-exec-calc-shellcode

GitHubpeterferrie/win-exec-calc-shellcode

A small, null-free Windows shellcode that executes calc.exe (x86/x64, all OS/SPs)
binary-exploitationexploitationpayload-development+3
4512 years ago
spawn preview

spawn

GitHubboku7/spawn

Cobalt Strike BOF that spawns a sacrificial process, injects it with shellcode, and executes payload. Built to evade EDR/UserLand hooks by spawning…

command-and-controlexploitationpayload-development+5
4643 years ago
DllNotificationInjection preview

DllNotificationInjection

GitHubdec0ne/dllnotificationinjection

A POC of a new “threadless” process injection technique that works by utilizing the concept of DLL Notification Callbacks in local and remote…
exploitationred-teamingshellcode
4673 years ago
ropium preview

ropium

GitHubboyan-milanov/ropium

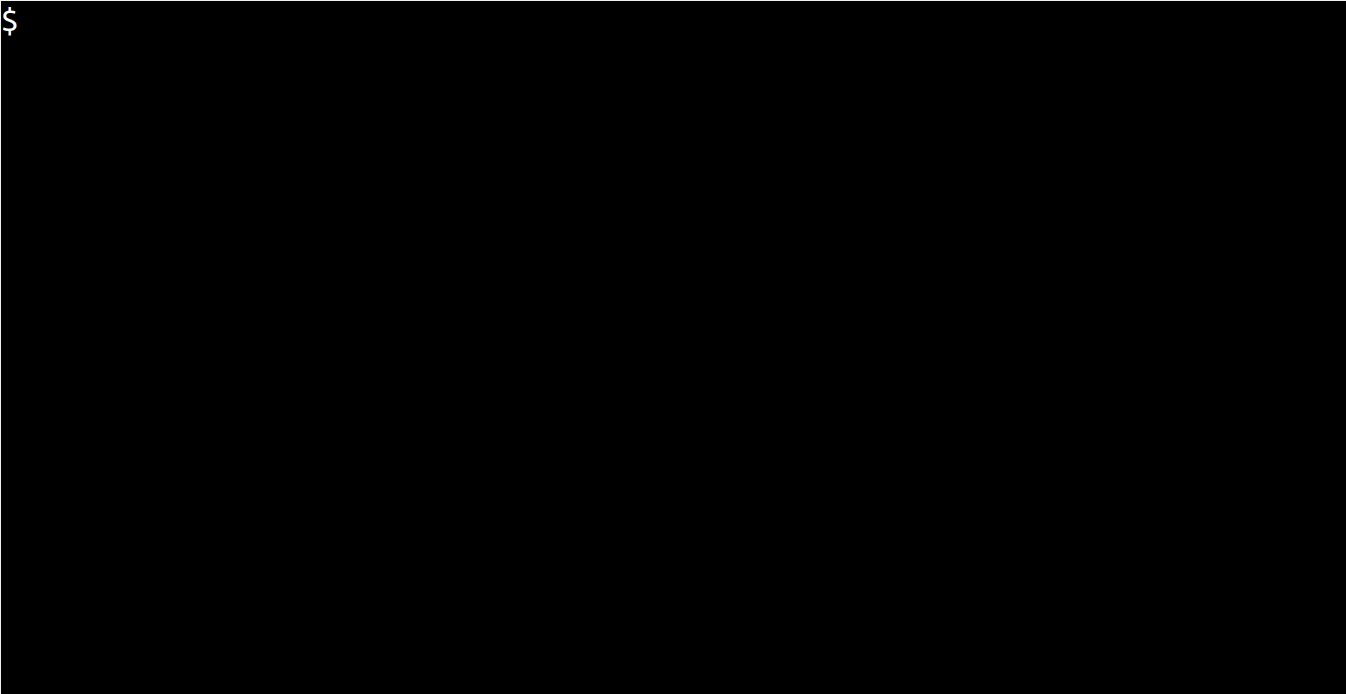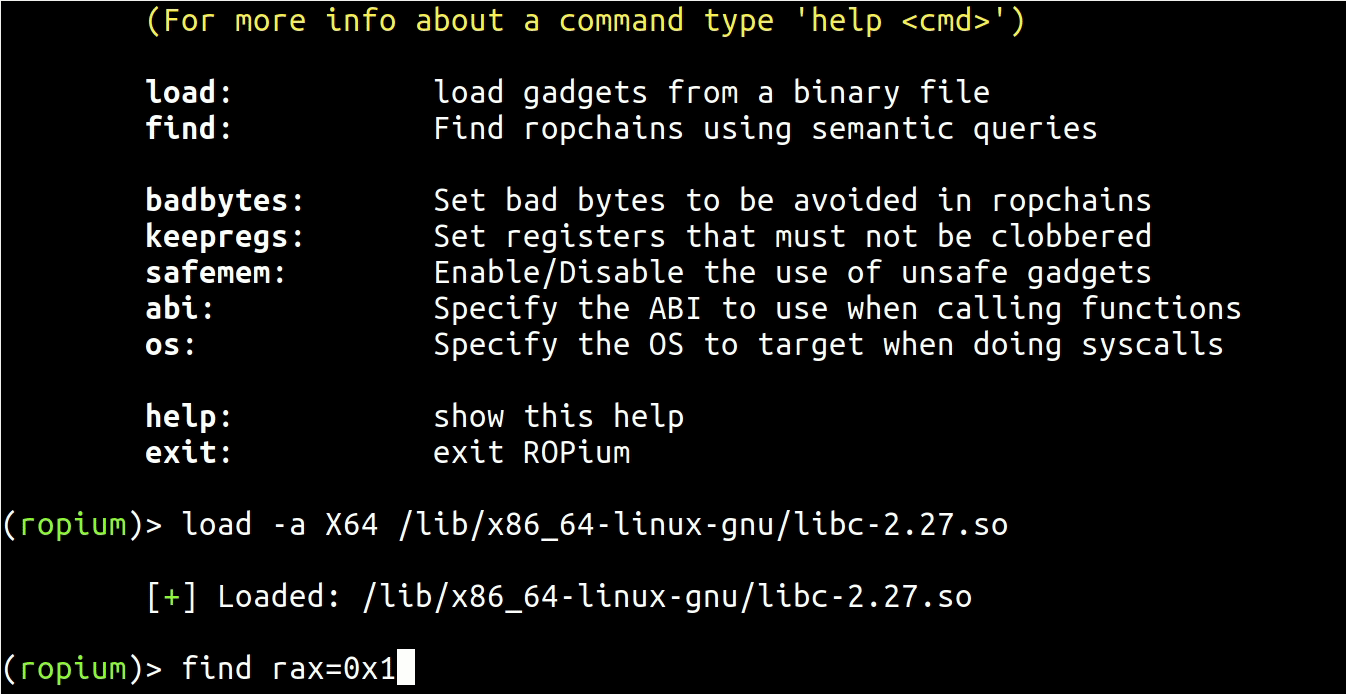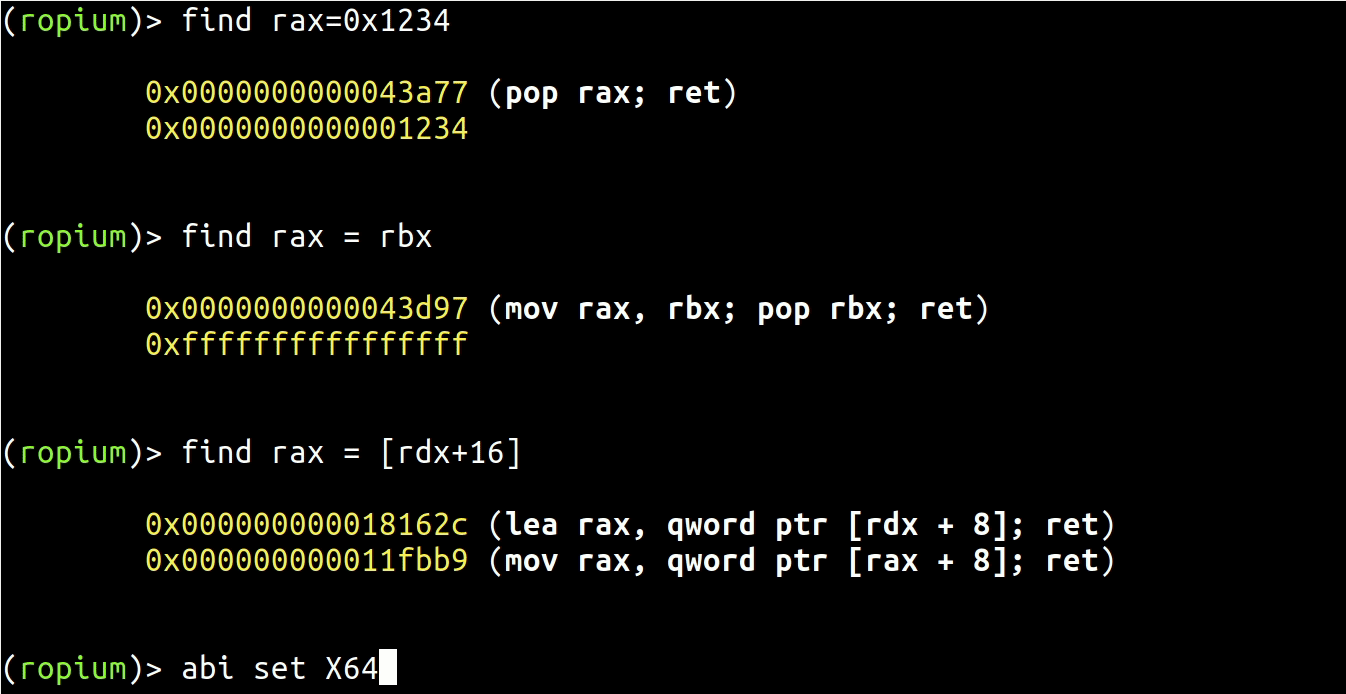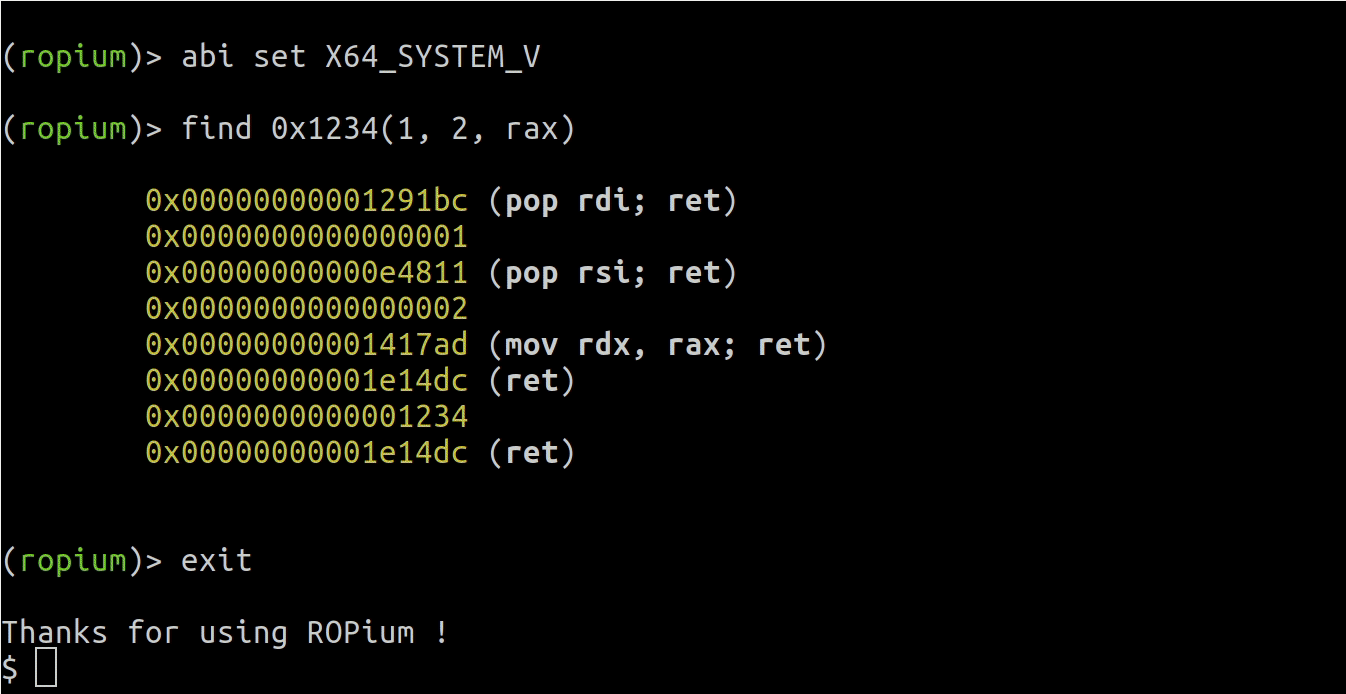
Automated ROP chain builder that extracts and analyzes gadgets from binaries using semantic queries, supporting X86/X64 architectures with a Python…
binary-exploitationexploit-frameworkspayload-development+2
4024 years ago
gdog preview

gdog

GitHubmaldevel/gdog

A fully featured Windows backdoor that uses Gmail as a C&C server

command-and-controlpayload-generationpost-exploitation+2
5089 years ago
Previous12…8Next