
CVE-2010-5301
 lem0nsec/cve-2010-5301
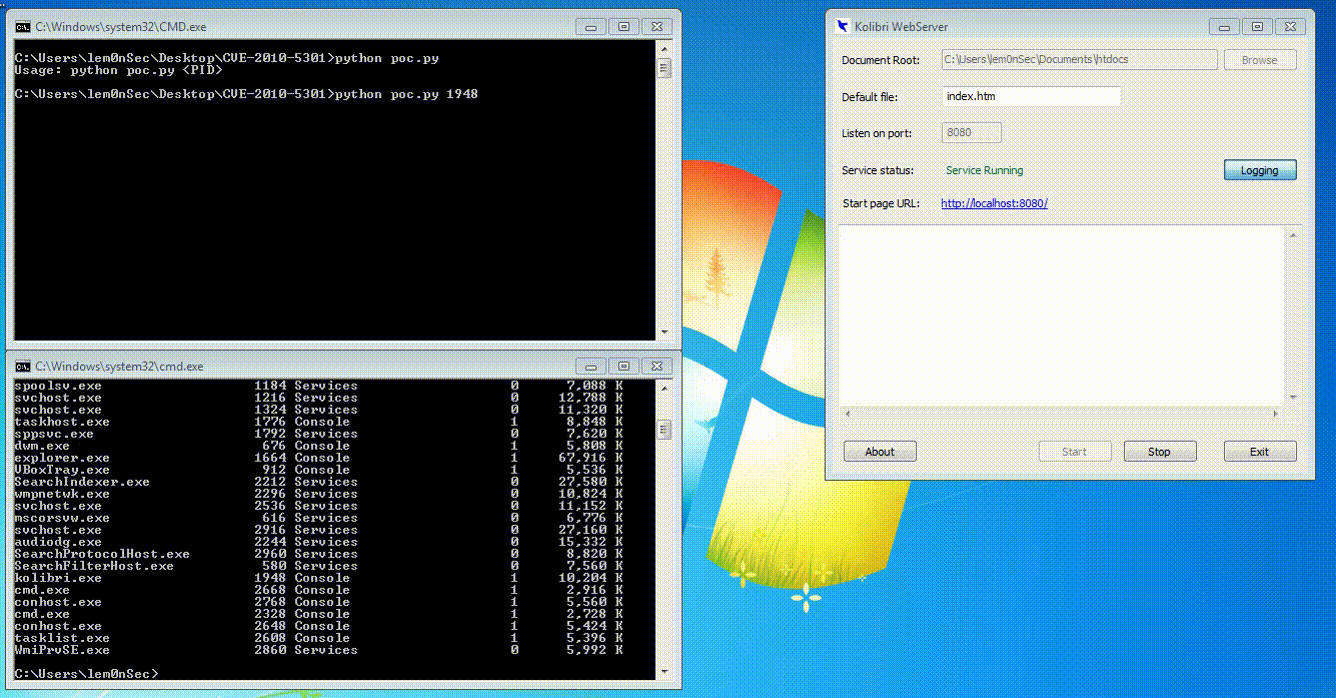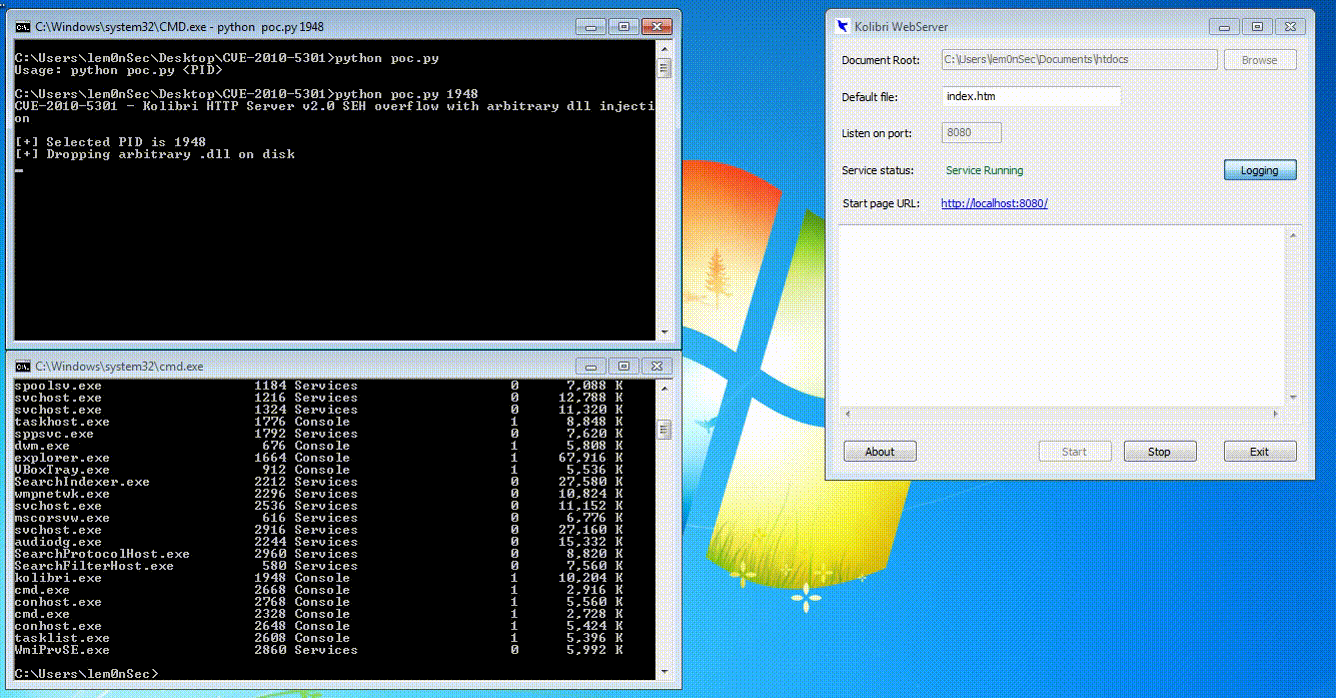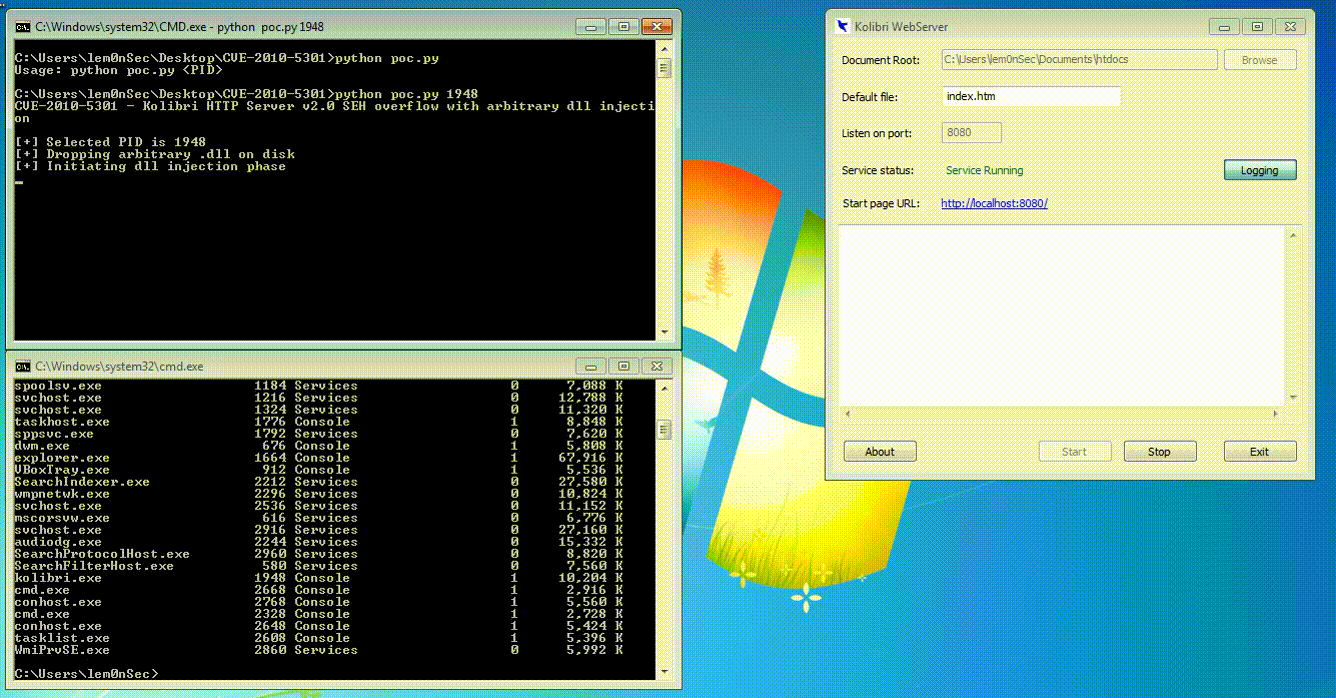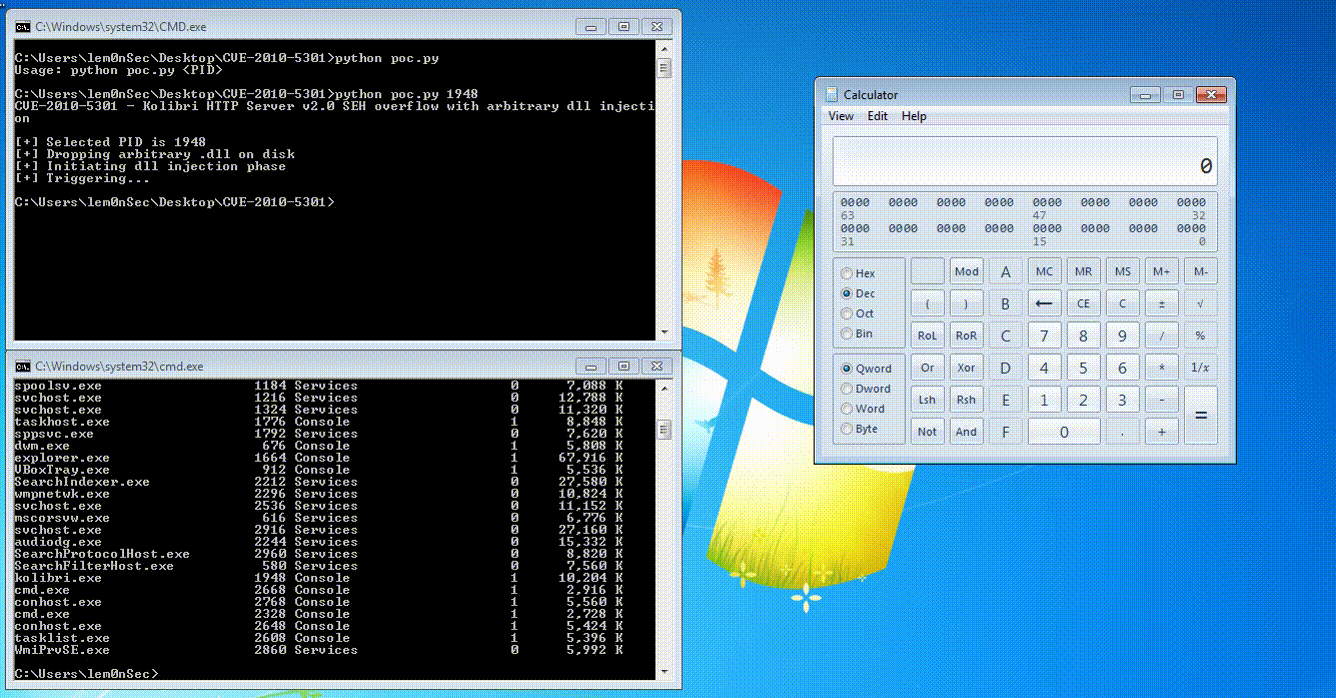
A proof of concept of an SEH overflow with arbitrary dll injection
binary-exploitationexploitationpayload-development+3
2
lem0nsec/cve-2010-5301A proof of concept of an SEH overflow with arbitrary dll injection
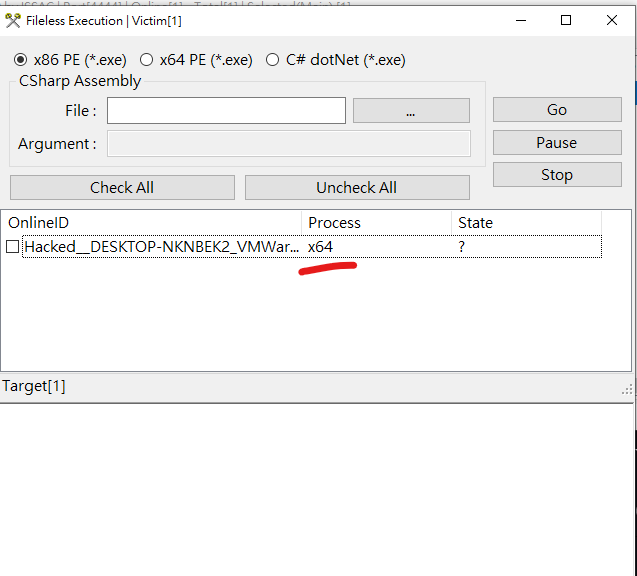 iss4cf0ng/duplexspycs
An open-source, C#-based remote administration tool (RAT), enabling complete control of a remote Windows machine, designed for legitimate remote…
 lukechilds/reverse-shell
On-demand reverse shell service that auto-detects target environment and executes appropriate payload for remote access during penetration tests.
 epotseluevskaya/aspx_webshell_coffloader
ASPX web shell with COFF loader for executing Beacon Object Files (BOFs) on target servers via a semi-interactive Python client, designed for…
 b3mb4m/shellsploit-framework
Framework for generating shellcode and exploit payloads, designed for penetration testing and security research to automate payload creation and…
 hussienmisbah/exploits
Repository containing exploit scripts for various CVEs, targeting web applications, binaries, and network services, suitable for penetration testing…
 rastating/wordpress-exploit-framework
A Ruby framework designed to aid in the penetration testing of WordPress systems.
 rapid7/metasploit-framework
Open-source exploitation framework with modular payload, encoder, and auxiliary system for penetration testing, vulnerability validation, and…
 bc-security/empire
Empire is a post-exploitation and adversary emulation framework that is used to aid Red Teams and Penetration Testers.
 ekultek/graffiti
A tool to generate obfuscated one liners to aid in penetration testing
 nullsecuritynet/tools
Curated collection of security tools, exploits, proof-of-concept code, shellcodes, and scripts for penetration testing and educational offensive…
 jasperla/cve-2017-9101
Authenticated remote code execution exploit for PlaySMS 1.4 via CSV phonebook upload. Provides single-command and interactive shell modes for…
 encrypter15/cve-2025-50165-x64-exploit
Generates weaponized JPEG files exploiting CVE-2025-50165 (Windows Graphics RCE) with custom x64 shellcode, heap spray, ROP chain, and AV/EDR evasion…
 nu11secur1ty/shellupload
PHP-based web shell uploader for penetration testing, enabling file upload and remote command execution on vulnerable web servers.
 schn1tzelme1ster/cve-2025-6002
Python exploit for CVE-2025-6002 targeting authenticated arbitrary file upload in VirtueMart < 4.4.10. Logs in, uploads a PHP webshell, and triggers…
 kaleth4/cve-2025-60751
Technical analysis and professional exploit for CVE-2025-60751, a stack-based buffer overflow in GeographicLib. Includes a pwntools-based Ret2Libc…
 kaleth4/cve-2024-6387
Exploit and scanner for CVE-2024-6387 (regreSSHion) in OpenSSH. Includes detection, RCE exploitation, and shellcode generation for authorized…
 dahalsamir/cve-2011-2523-exploit
Python exploit for vsFTPd 2.3.4 backdoor (CVE-2011-2523) that triggers a hidden shell on port 6200 via a crafted username, enabling remote command…